

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
37 results
blindxss-lite preview

blindxss-lite

GitHubyuyudhn/blindxss-lite

A lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask
command-and-controldata-exfiltrationinformation-gathering+7
39 days ago
CVE-2026-84388-POC preview

CVE-2026-84388-POC

GitHubshadowforge-cyber/cve-2026-84388-poc

Improper Restriction of Rendered UI Layers or Frames (CWE-1021)

data-exfiltrationexploitationpayload-development+3
1 month ago
StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis preview

StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis

GitHubkaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…
command-and-controldata-exfiltrationdigital-forensics+7
31 month ago
Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis preview

Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis

GitHubkaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis

In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…
binary-analysiscommand-and-controldata-exfiltration+4
121 month ago
CVE-2026-39047 preview

CVE-2026-39047

GitHubazhariramadhan/cve-2026-39047

Printer exploitation framework for security testing via raw port 9100, featuring PCL payload delivery, DoS bombing, C2 QR codes, phishing QR codes,…
data-exfiltrationexploitationnetwork-security+4
7 months ago
CVE-2026-41653 preview

CVE-2026-41653

GitHubastaruf/cve-2026-41653

Proof-of-concept exploit for CVE-2026-41653, a stored XSS in BentoPDF that enables silent file exfiltration and WASM supply-chain hijacking.
data-exfiltrationexploitationpayload-development+2
6 months ago
AcrStealer-Custom-Protocol-Credential-Theft-Payload-Extraction-Analysis preview

AcrStealer-Custom-Protocol-Credential-Theft-Payload-Extraction-Analysis

GitHubkaandemir993/acrstealer-custom-protocol-credential-theft-payload-extraction-analysis

Reverse engineering analysis of AcrStealer, a sophisticated info-stealer that uses custom protocols, browser credential theft, and payload…

binary-analysiscommand-and-controldata-exfiltration+2
42 months ago
Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis preview

Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis

GitHubkaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis

Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…
binary-analysiscommand-and-controldata-exfiltration+6
62 months ago
slot2 preview

slot2

GitHubcenobyte-vincit/slot2

UEFI GRUB2 bootkit that installs a pre-boot networked implant via NVRAM boot option, chainloads a UKI, executes a dracut payload, and kexecs the…

cloud-securitycommand-and-controldata-exfiltration+5
2 months ago
RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis preview

RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis

GitHubkaandemir993/redline-stealer-c2-defender-bypass-payload-analysis

"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…
command-and-controldata-exfiltrationmalware-analysis+4
12 months ago
Agent-Tesla-APC-Injection-Token-Manipulation-Registry-Persistence-Analysis preview

Agent-Tesla-APC-Injection-Token-Manipulation-Registry-Persistence-Analysis

GitHubkaandemir993/agent-tesla-apc-injection-token-manipulation-registry-persistence-analysis

"Reverse engineering analysis of Agent Tesla, a .NET-based info-stealer that uses APC injection, token manipulation, and registry persistence.…
binary-analysisdata-exfiltrationeducation+4
32 months ago
dark-doh preview

dark-doh

GitHubdarksh3llru/dark-doh

Covert file-transfer tool using DNS-over-HTTPS: encodes payload chunks in TXT records, applies XOR obfuscation, and can execute shellcode for…
command-and-controldata-exfiltrationred-teaming
202 years ago
CVE-2025-55182-Advanced-React-Server-Components-RCE-Exploit preview

CVE-2025-55182-Advanced-React-Server-Components-RCE-Exploit

GitHubcerberusmrxi/cve-2025-55182-advanced-react-server-components-rce-exploit

Advanced React Server Components RCE scanner for CVE-2025-55182. Features: multi-stage fingerprinting, vulnerability verification, DNS exfiltration,…
data-exfiltrationexploitationpayload-development+6
12 months ago
EmbedPayloadInPng preview

EmbedPayloadInPng

GitHubmaldev-academy/embedpayloadinpng

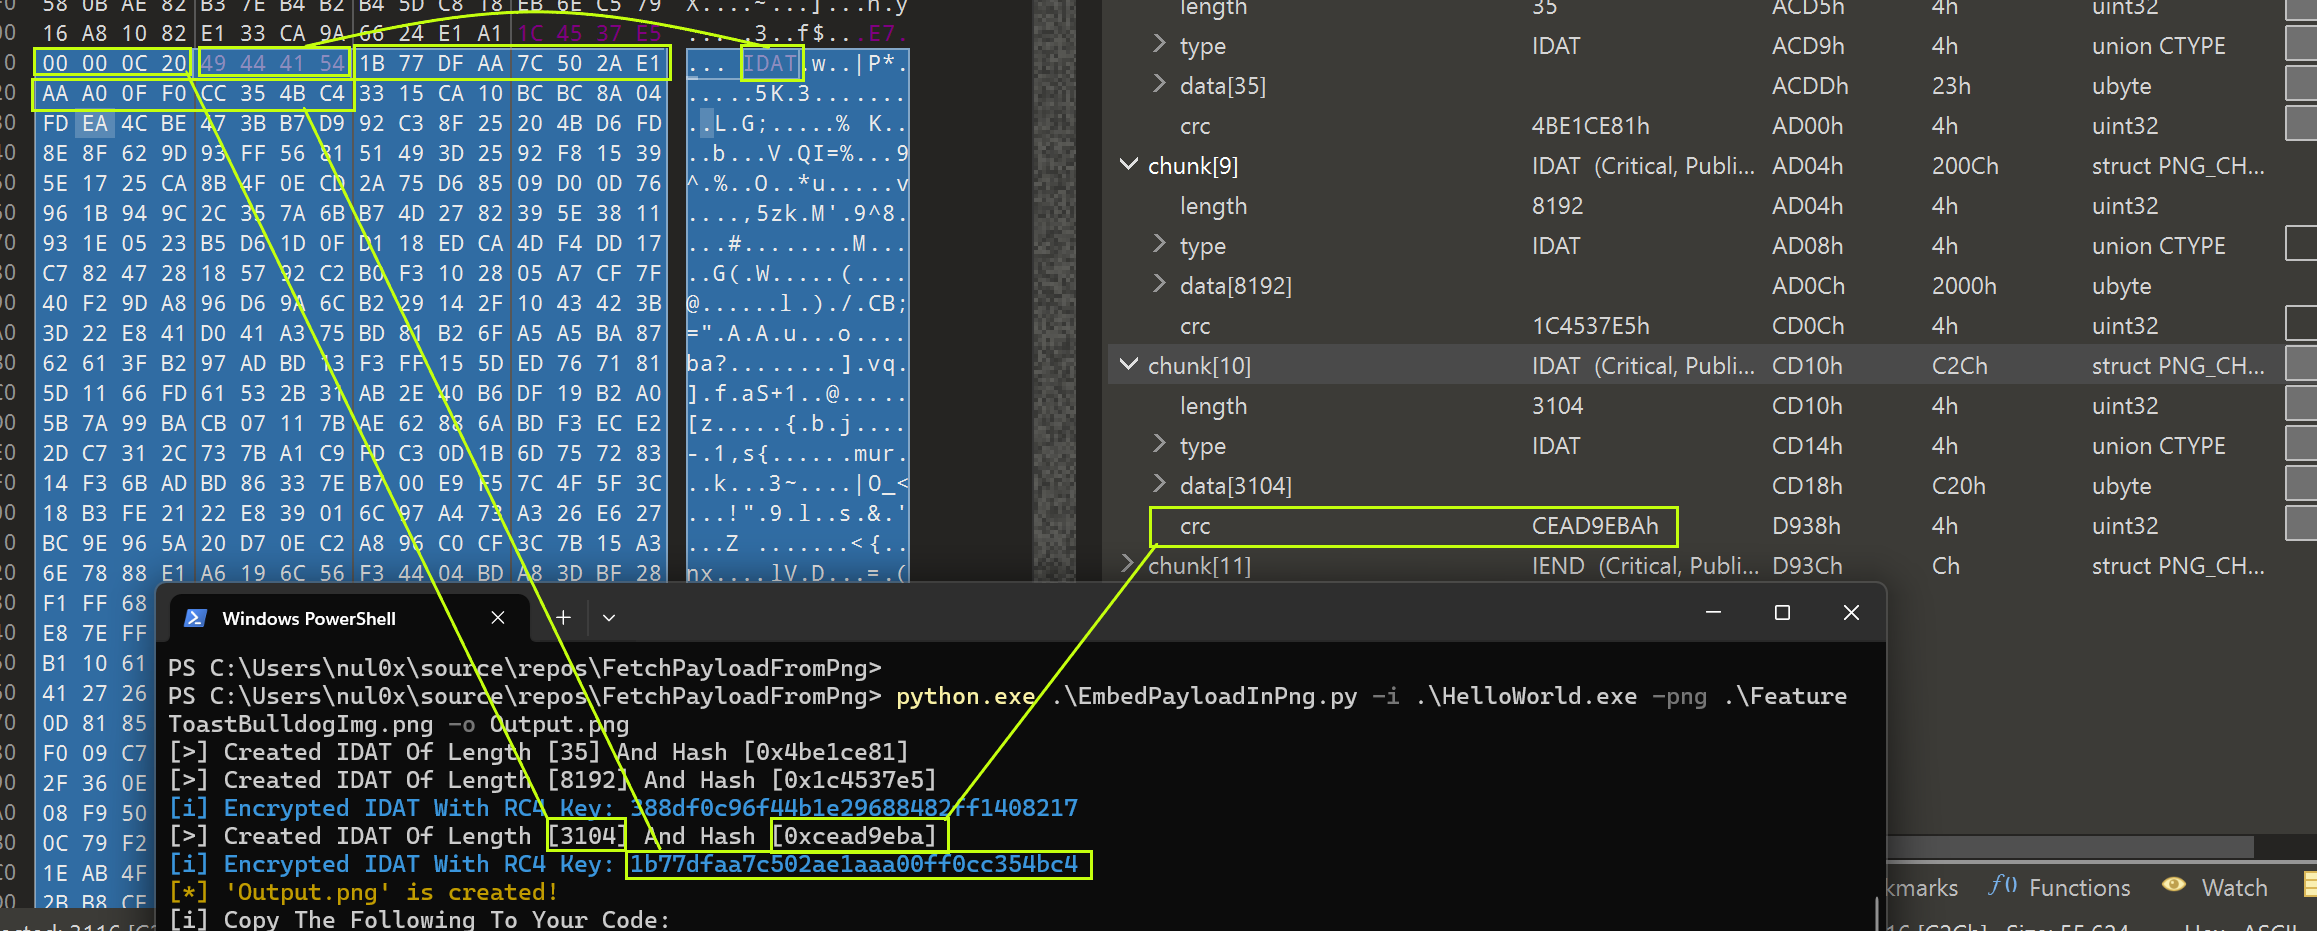
Embed a payload inside a PNG file
cryptographydata-exfiltrationids-ips-evasion+2
3722 years ago
Sleipnir preview

Sleipnir

GitHubnccgroup/sleipnir

Tiny payload for transfer via LOKI - Provides high speed Virtual Channel two way file transfer capabilities
data-exfiltrationpayload-developmentpenetration-testing+1
2711 years ago
CVE-2026-22804 preview

CVE-2026-22804

GitHubthemehackers/cve-2026-22804

This repository contains a Proof of Concept (PoC) exploit for the Stored Cross-Site Scripting (XSS) vulnerability in Termix, which can lead to Local…
data-exfiltrationexploitationpayload-development+2
29 months ago
Grassmarlin-CVE-2026-6807-XXE-POC preview

Grassmarlin-CVE-2026-6807-XXE-POC

GitHubsectestannaquinn/grassmarlin-cve-2026-6807-xxe-poc

Reverse Engineered based on CISA disclosure of new CVE
data-exfiltrationexploitationpayload-development+3
26 months ago
cve-2023-0669-simulation preview

cve-2023-0669-simulation

GitHubzakaria-laouani/cve-2023-0669-simulation

Simulation environment for CVE-2023-0669 with Docker-based attacker, vulnerable server, and listener containers. Demonstrates deserialization exploit…

command-and-controldata-exfiltrationexploitation+3
10 months ago
Previous123Next