CVE-2018-12633-TPLink-Auth-Bypass

A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).

A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).

KeySweeper is a stealthy Arduino-based device, camouflaged as a functioning USB wall charger, that wirelessly and passively sniffs, decrypts, logs…

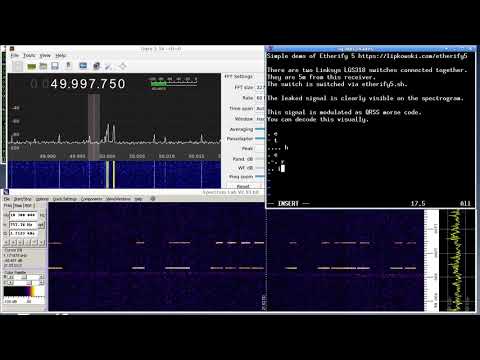
Etherify - bringing the ether back to ethernet

KERUI K259 5MP Wi-Fi (Tuya Smart Security Camera) contains a code execution vulnerability

Documentation of CVE-2025-51643: physical SPI flash extraction on Meitrack T366G-L GPS tracker enabling firmware dump, plaintext credential…

Proof-of-concept exploit for command injection vulnerability in Zyxel NAS devices. Demonstrates arbitrary command execution via crafted HTTP…