

yara-rules
 inquest/yara-rules
Collection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.
curated-resourcesdefensive-toolsincident-response+5
389
inquest/yara-rulesCollection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.
 embee-research/yara-detection-rules
Yara Rules for Modern Malware
 inquest/yara-rules-vt
Collection of YARA rules designed for usage through VirusTotal.com.
 ahmetpayaslioglu/yararules
Curated collection of YARA detection rules for identifying and classifying malware, supporting threat hunting and detection workflows.
 rivitna/malware
Curated YARA rules and detection programs for identifying ransomware families, providing signature-based indicators for malware triage, threat…
 strangerealintel/orion
A YARA rules repository continuously updated for monitoring the old and new threats from articles, incidents responses ...
 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
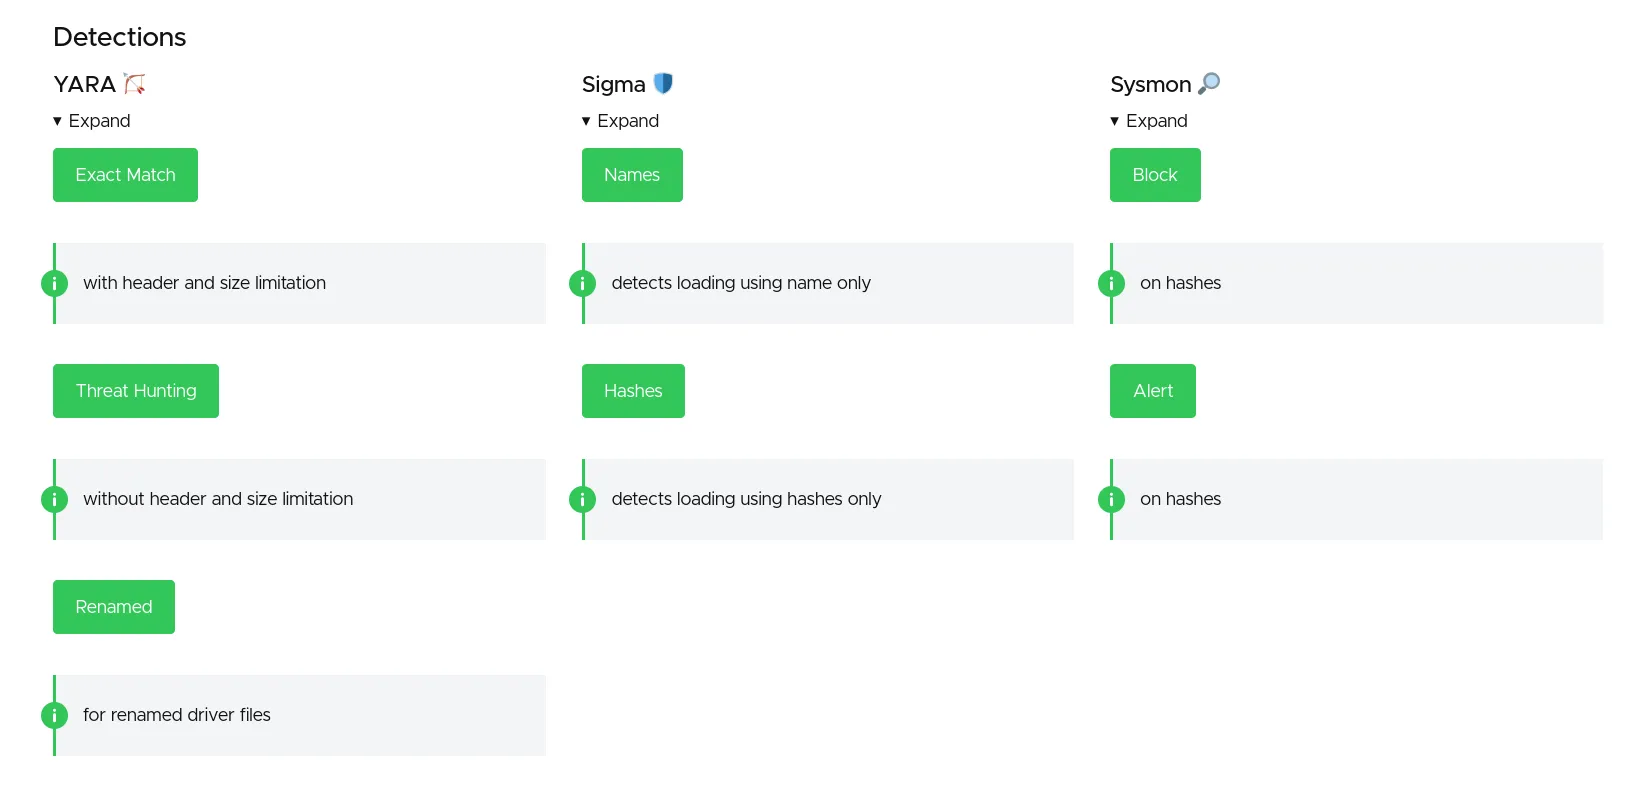 magicsword-io/loldrivers
Curated database of vulnerable and malicious Windows drivers with YARA, Sigma, ClamAV, and Sysmon detection rules for proactive threat hunting and…
 vasyapokemon/cve-2026-31431
Research and detection toolkit for Linux kernel LPE CVE-2026-31431, including exploit analysis, YARA rules, auditd/Falco detection, patching guide,…
 100daysofyara/2024
Rules shared by the community from 100 Days of YARA 2024
 100daysofyara/2026
Rules shared by the community from 100 Days of YARA 2026
 100daysofyara/2023
Rules Shared by the Community from 100 Days of YARA 2023
 shellcromancer/daysofyara-2023
Rules Shared by the Community from 100 Days of YARA 2023 -
 techwithorgito/cve-2025-55182-researching-process
Defensive research repository for CVE-2025-55182 (Pre-Auth RCE in React Server Components/Next.js). Includes technical analysis, detection rules…
 mandiant/heyserial
Programmatically create hunting rules for deserialization exploitation with multiple keywords, gadget chains, object types, encodings, and rule types
 arpsyndicate/vedas-signatures
VEDAS-Driven Autonomous Generation + Community Contributions of Suricata & Nuclei Rules for over 15k CVEs
 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)