
CSPBypass
 renniepak/cspbypass
CSPBypass.com, a tool designed to help ethical hackers bypass restrictive Content Security Policies (CSP) and exploit XSS (Cross-Site Scripting)…
configuration-auditingcurated-resourcesmisconfiguration+4
709
renniepak/cspbypassCSPBypass.com, a tool designed to help ethical hackers bypass restrictive Content Security Policies (CSP) and exploit XSS (Cross-Site Scripting)…
 projectdiscovery/nuclei-templates
Community curated list of templates for the nuclei engine to find security vulnerabilities.
 d0n601/pentest-cheat-sheet
There are many cheat sheets out there, but this is mine.
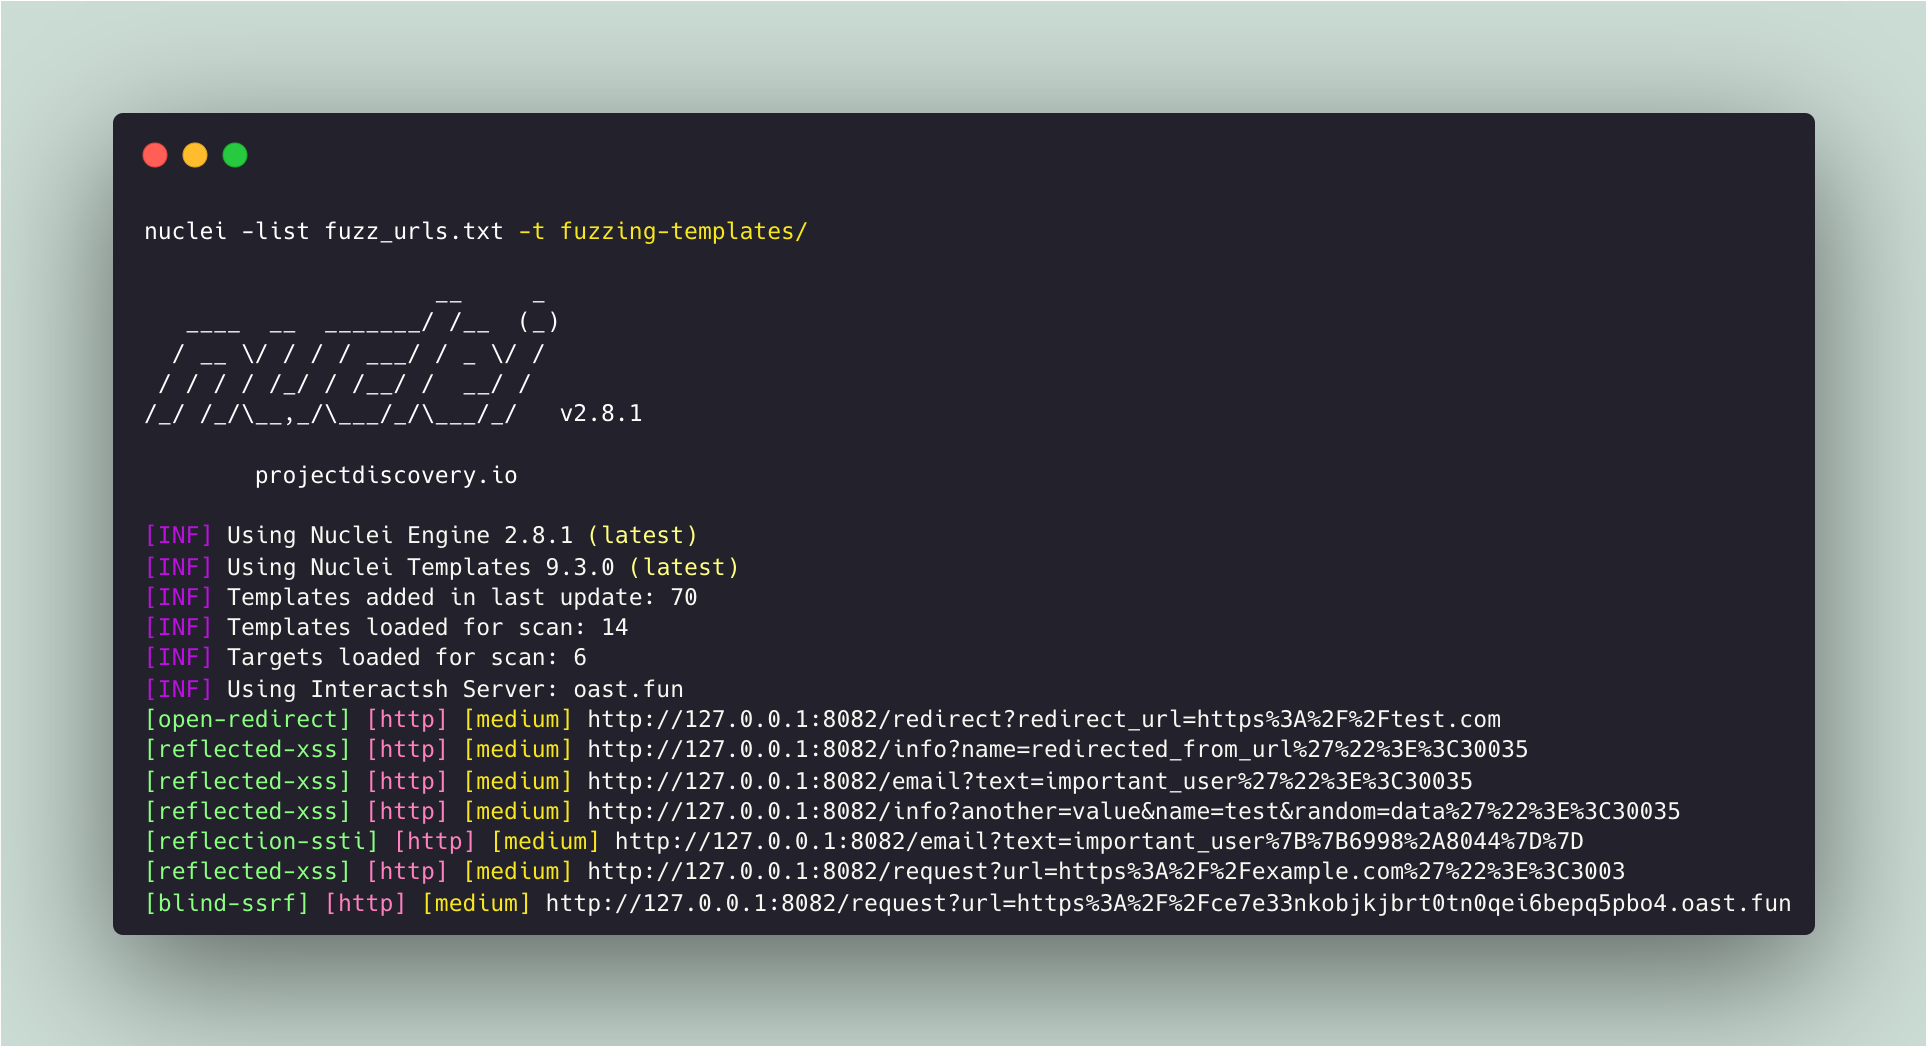 projectdiscovery/fuzzing-templates
Community curated list of nuclei templates for finding "unknown" security vulnerabilities.
 stealthcopter/wordpress-hacking
A collection of useful resources for hacking WordPress and it's plugins and themes
 ignitetechnologies/burpsuite-for-pentester
This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…
 harsh-bothra/securityexplained
SecurityExplained is a new series after the previous learning challenge series #Learn365. The aim of #SecurityExplained series is to create…
 cure53/xsschallengewiki
Community-maintained wiki cataloging XSS challenges and solutions, providing curated hands-on exercises for learning cross-site scripting…
 leox48/cve-2026-1769-writeup
Public write-up and disclosure timeline for CVE-2026-1769 (Stored XSS in Xerox CentreWare Web)
 codermohammed1/cve-2025-63848
CVE disclosure for stored cross-site scripting (XSS) in SWISH Prolog up to v2.2.0, enabling arbitrary code execution and account takeover via crafted…
 snorlyd/https-nj.gov---cve-2019-8331
Vulnearability Report of the New Jersey official site
 lylemi/learn-web-hacking
Structured study notes covering web hacking fundamentals, common vulnerabilities, penetration testing techniques, and defensive security, with…
 lukasz-rybak/cve-2026-1434
CVE-2026-1434 - Omega-PSIR is vulnerable to Reflected XSS via the lang parameter. An attacker can craft a...
 center-for-threat-informed-defense/adversary_emulation_library
An open library of adversary emulation plans designed to empower organizations to test their defenses based on real-world TTPs.
 4rdr/proofs
Collection of CVE findings, proof-of-concept references, and vulnerability research notes, including ExploitDB entries and credited security…
 reddelexc/hackerone-reports
Curated collection of top HackerOne bug bounty reports organized by vulnerability type and program, with scripts to fetch, deduplicate, and rank…
