
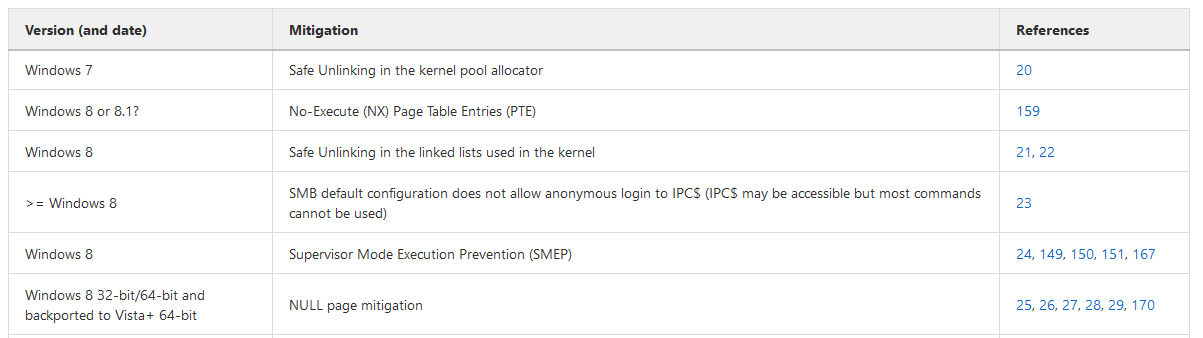
 nccgroup/exploit_mitigations
Knowledge base of exploit mitigations available across numerous operating systems, architectures and applications and versions.
 alvin-tosh/malware-exhibit
🚀🚀 This is a 🎇🔥 REAL WORLD🔥 🎇 Malware Collection I have Compiled & analysed by researchers🔥 to understand more about Malware threats😈,…
 hackinglz/extracteddefender
Collection of extracted Microsoft Defender data for security research purposes
 p0dalirius/windows-coerced-authentication-methods
A list of methods to coerce a windows machine to authenticate to an attacker-controlled machine through a Remote Procedure Call (RPC) with various…
 persistence-info/persistence-info.github.io
Curated reference of Windows persistence mechanisms across registry, scheduled tasks, services, and more, designed to improve protection and…
 sailay1996/awesome_windows_logical_bugs
collect for learning cases
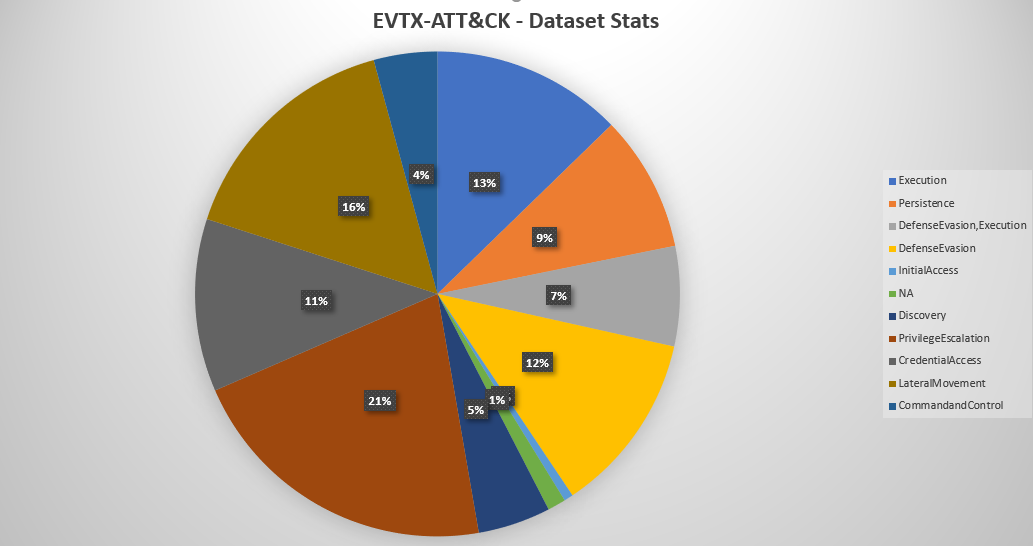 sbousseaden/evtx-attack-samples
Curated collection of Windows EVTX attack samples mapped to MITRE ATT&CK techniques, designed for testing detection scripts, DFIR training, and…
 thel1nus/cve-2004-1561-notes
My notes for CVE-2004-1561 IceCast exploitation
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 an0nud4y/av-edr-lab-environment-setup
AV/EDR Lab environment setup references to help in Malware development
 wattocyber/detection-defense-library
Detection-engineering reference mapping Windows, cloud, container, identity, and ICS attack classes to Sigma rules, trust-boundary models, BYOVD…
 otrf/ossem
Community-driven project for documenting, standardizing, and modeling security event logs to improve detection analytics and data normalization…
 zephrfish/azureattackkit
Collection of Azure Tools to Pull down for Attacking an Environment + quick tips and other useful information
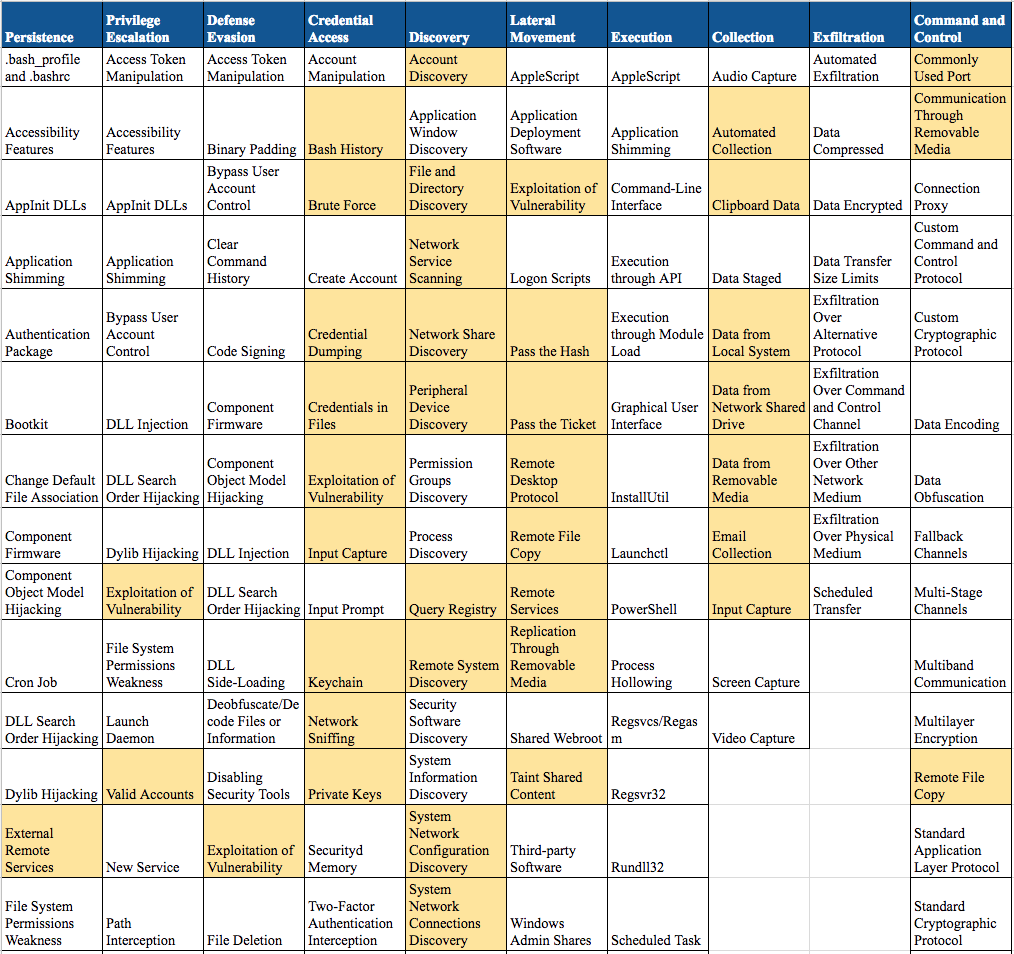 0x4d31/deception-as-detection
Deception based detection techniques mapped to the MITRE’s ATT&CK framework
 gmh5225/cve-2021-42205
ELAN Miniport touchpad Windows driver before 24.21.51.2, as used in PC hardware from multiple manufacturers, allows local users to cause a system…
 frizb/hashcat-cheatsheet
Hashcat reference for OSCP/penetration testing: hash identification, cracking syntax for Linux, Windows, archives, databases, Kerberos tickets, and…
 jonny-jhnson/telemetrysource
Reference mapping Windows telemetry events—Sysmon, Security Auditing, and Threat Intelligence ETW—to underlying API functions, helping defenders…