
user-security-stories
 owasp/user-security-stories
Repo to hold mapping of user-security-stories
curated-resourcesdevsecopseducation+1
1208 years ago
owasp/user-security-storiesRepo to hold mapping of user-security-stories
 kagancapar/cve-2026-54984
CVE-2026-54984 / ZDI-26-543: Windows ICC file parsing out-of-bounds write (CWE-122, CVSS 7.8)
 saykino/cve-2025-56221
Advisory detailing CVE-2025-56221, an authentication rate-limiting flaw in Ascertia SigningHub allowing brute-force attacks, with affected versions…
 saykino/cve-2025-56219
Detailed advisory for CVE-2025-56219, a rate-limiting flaw in Ascertia SigningHub's Add User API, enabling automated user creation and denial of…
 saykino/cve-2025-54321
Documentation of CVE-2025-54321: an email bombing vulnerability in Ascertia SigningHub's reset password function due to missing rate limiting,…
 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
 0x48piraj/incarcero
Incarcero is a tool that creates Virtual Machines (VMs) preconfigured with malware analysis tools and security settings tailored for malware analysis…
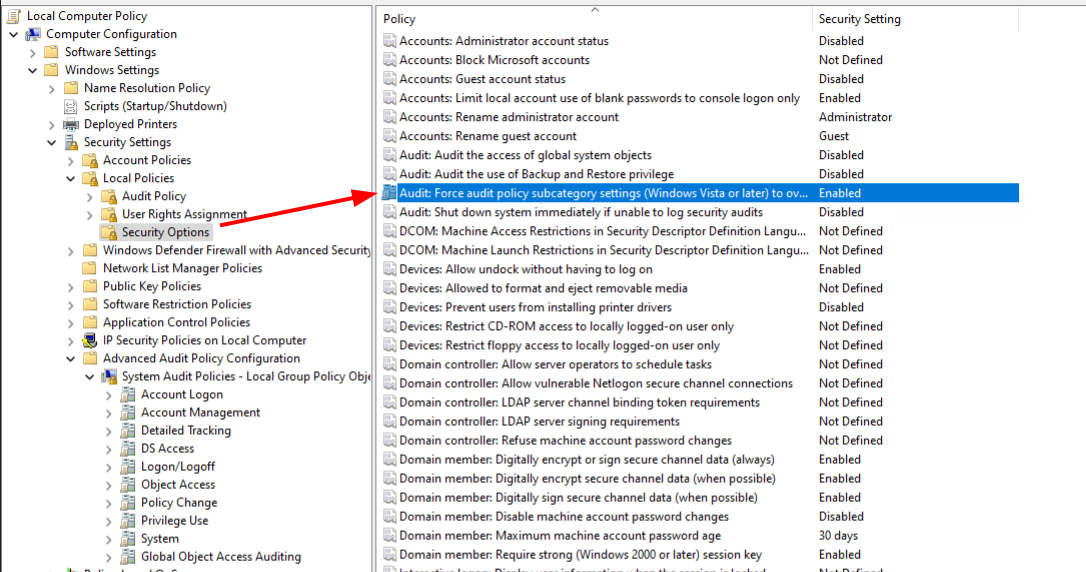 nextronsystems/evtx-baseline
A repository hosting example goodware evtx logs containing sample software installation and basic user interaction
 0xmrma/cve-2026-46558
Plane’s V2 asset subsystem trusted workspace slugs and asset UUIDs without enforcing the right membership checks, which let one authenticated user…
 ristbs/awesome-redteam-cheatsheet
Red Team Cheatsheet in constant expansion.
 soufianetahiri/anxun-isoon
I-SOON/Anxun leak related stuff
 amanyadav78/cve-2026-29861
Advisory and proof-of-concept for CVE-2026-29861, a critical SQL injection in PHP-MYSQL-User-Login-System allowing unauthenticated admin access.
 chaitanyagarware/cve-2026-54519
Public advisory landing page for CVE-2026-54519: missing ownership checks in ai-agent-automation memory APIs enabling cross-user memory read and…
 junz-leo/cve
Public vulnerability reports and CVE write-ups by JunZ-Leo, documenting SQL injection flaws in PHPGurukul COVID19 Testing Management System 1.0.
 archana1122m/cve-disclosures
CVE-2026-3171 and CVE-2026-3170 vulnerability disclosure by Archana M