
Claude-Red
 snailsploit/claude-red
Curated library of 78 offensive security SKILL.md modules that prime Claude with expert red team methodology across web, AD, wireless, cloud, and…
ai-securitycurated-resourceseducation+8
6.8k
snailsploit/claude-redCurated library of 78 offensive security SKILL.md modules that prime Claude with expert red team methodology across web, AD, wireless, cloud, and…
 j3ssie/dynast-bench
A DAST benchmark of intentionally-vulnerable apps with ground-truth answer keys for scoring scanners
 we5ter/scanners-box
The Ultimate Open-Source Security Arsenal for Hackers, Enterprises, and AI Agents——面向极客、企业与 AI 智能体的全域开源网络安全工具矩阵
 owasp/owasp-subtractive-hardening-top-10
The OWASP Subtractive Security Top 10 Project is an initiative to identify, document, and promote the highest-impact opportunities for reducing cyber…
 suominen/ipv6_frag_escape
Tracking IPV6_FRAG_ESCAPE (CVE-2026-53362, CVE-2026-53366), the IPv6 fragmentation container escape
 cr0nx/awesome-linux-attack-forensics-purplelabs
This page is a result of the ongoing hands-on research around advanced Linux attacks, detection and forensics techniques and tools.
 ugurrates/teampcp-supply-chain-attack
CVE-2026-33634 (CVSS 9.4) — The most impactful CI/CD supply chain attack of 2026 so far.
 projectdiscovery/nuclei-templates-labs
Vulnerable environments paired with ready-to-use Nuclei templates for security testing and learning! 🚀
 suominen/itscape
Tracking ITScape (CVE-2026-46316), the KVM/arm64 guest-to-host escape
 alvin-tosh/malware-exhibit
🚀🚀 This is a 🎇🔥 REAL WORLD🔥 🎇 Malware Collection I have Compiled & analysed by researchers🔥 to understand more about Malware threats😈,…
 ishankaru/cve-2026-23111-nftables-lab
Exposure checker and safe disposable-VM lab for CVE-2026-23111 (Linux nf_tables use-after-free local privilege escalation). Defensive: detection,…

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 codykociemba/nolongerevil-thermostat
Breathe fresh life into your bricked Nest, now with 100% less evil!
 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 securewithumer/cve-2026-pocs
A community-curated, verified collection of Proof-of-Concept exploits for CVEs disclosed in 2026.
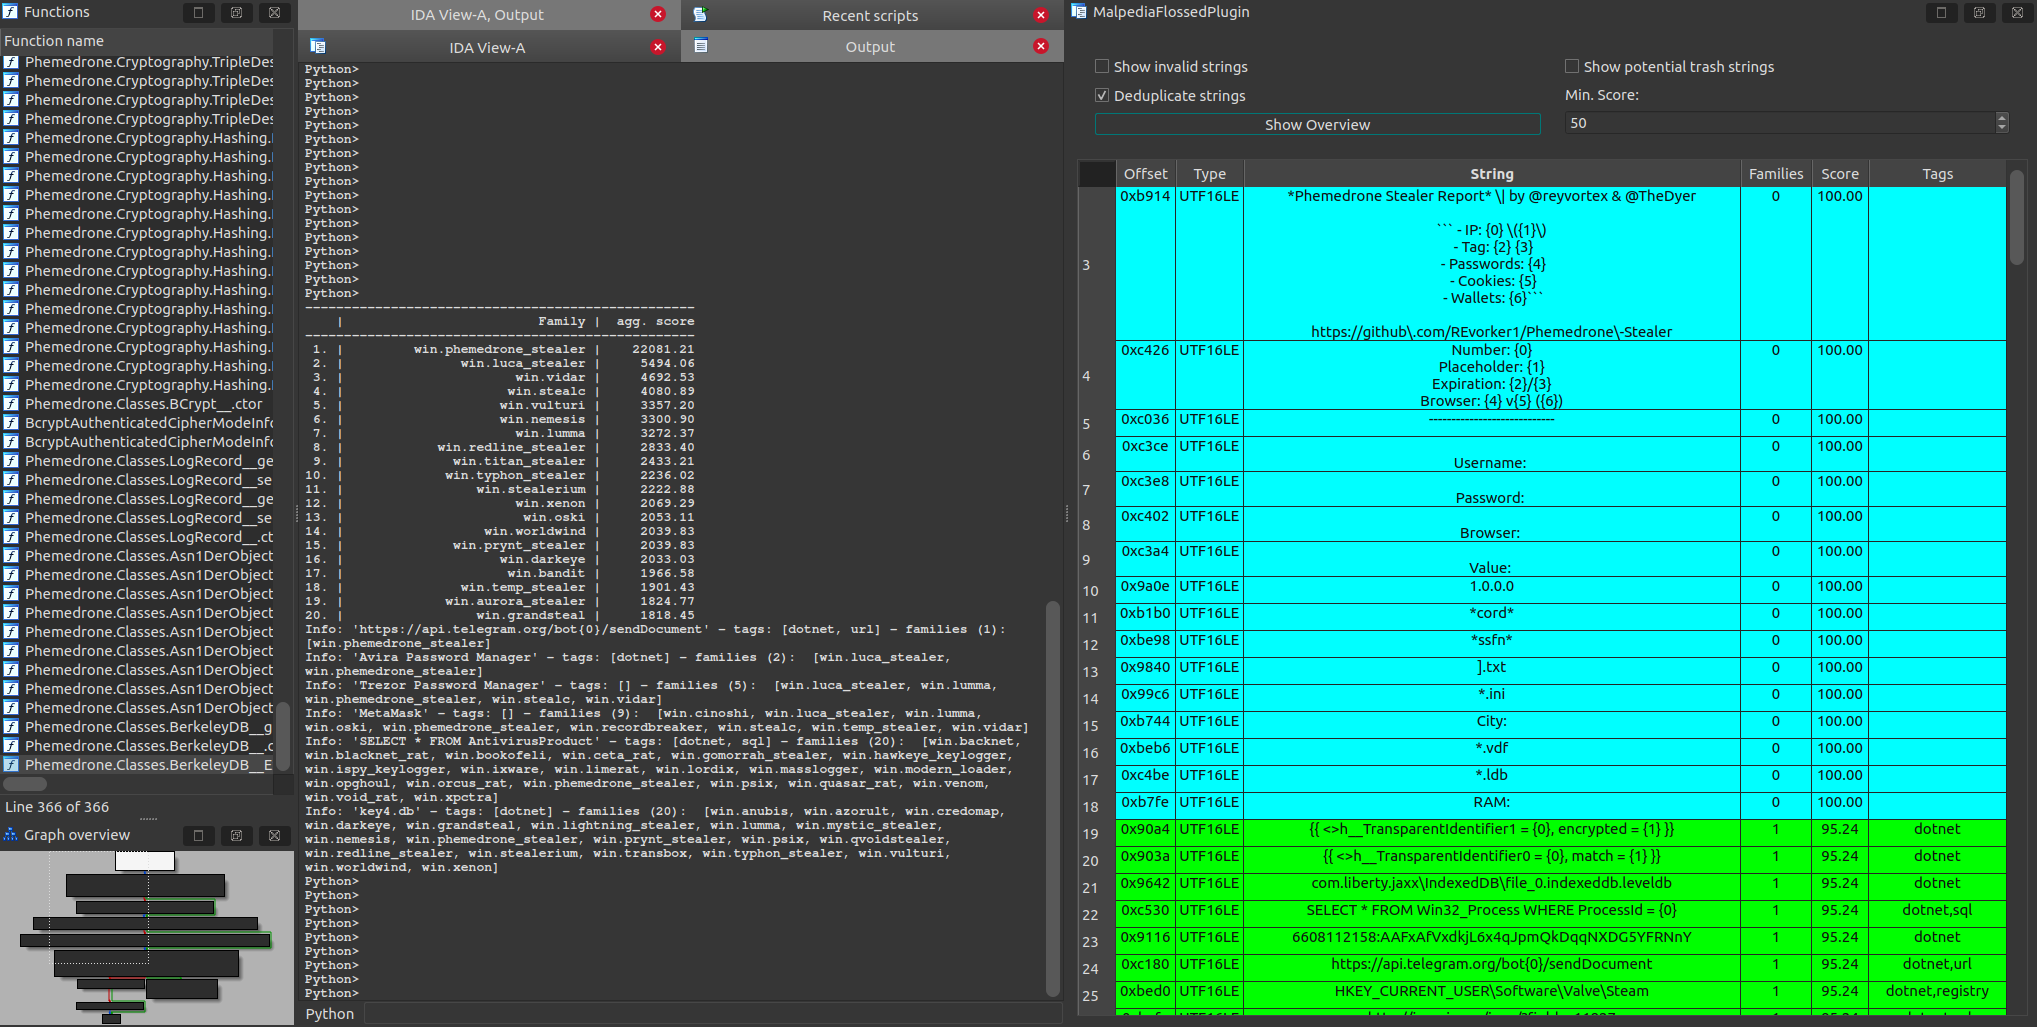 malpedia/malpedia-flossed
FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.
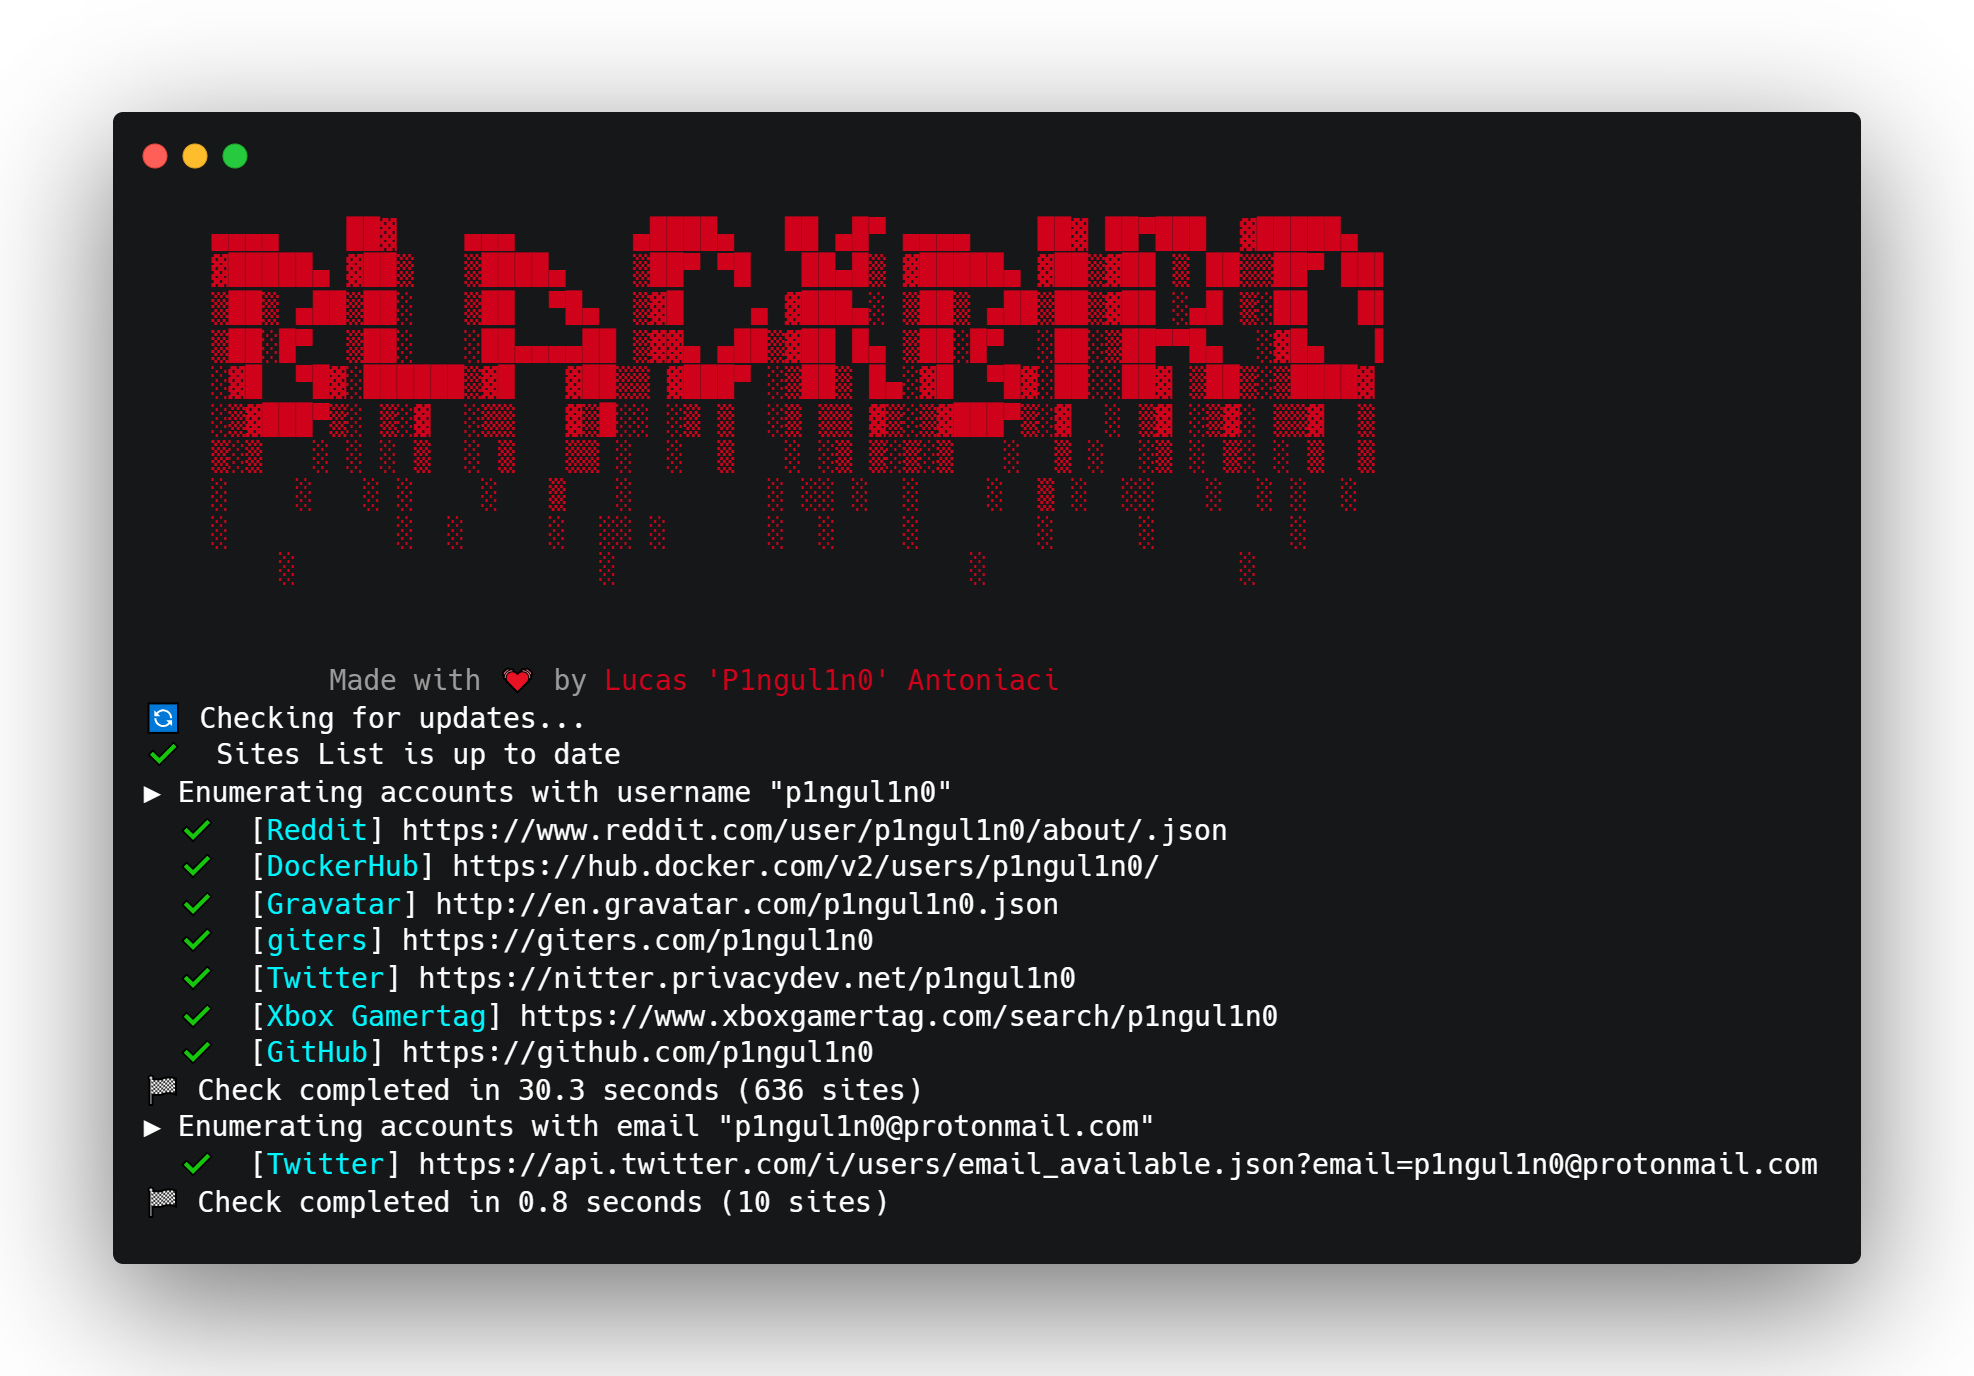 gcabc123/blackbird
An OSINT tool to search for accounts by username in social networks.