
CVE-2006-20001
 r1az4r/cve-2006-20001
A carefully crafted If: request header can cause a memory read, or write of a single zero byte, in a pool (heap) memory location beyond the header…
curated-resourceseducationexploitation+2
r1az4r/cve-2006-20001A carefully crafted If: request header can cause a memory read, or write of a single zero byte, in a pool (heap) memory location beyond the header…
 cisagov/decider
A web application that assists network defenders, analysts, and researchers in the process of mapping adversary behaviors to the MITRE ATT&CK®…
 netbiosx/checklists
Red Teaming & Pentesting checklists for various engagements
 allanlw/svg-cheatsheet
A cheatsheet for exploiting server-side SVG processors.
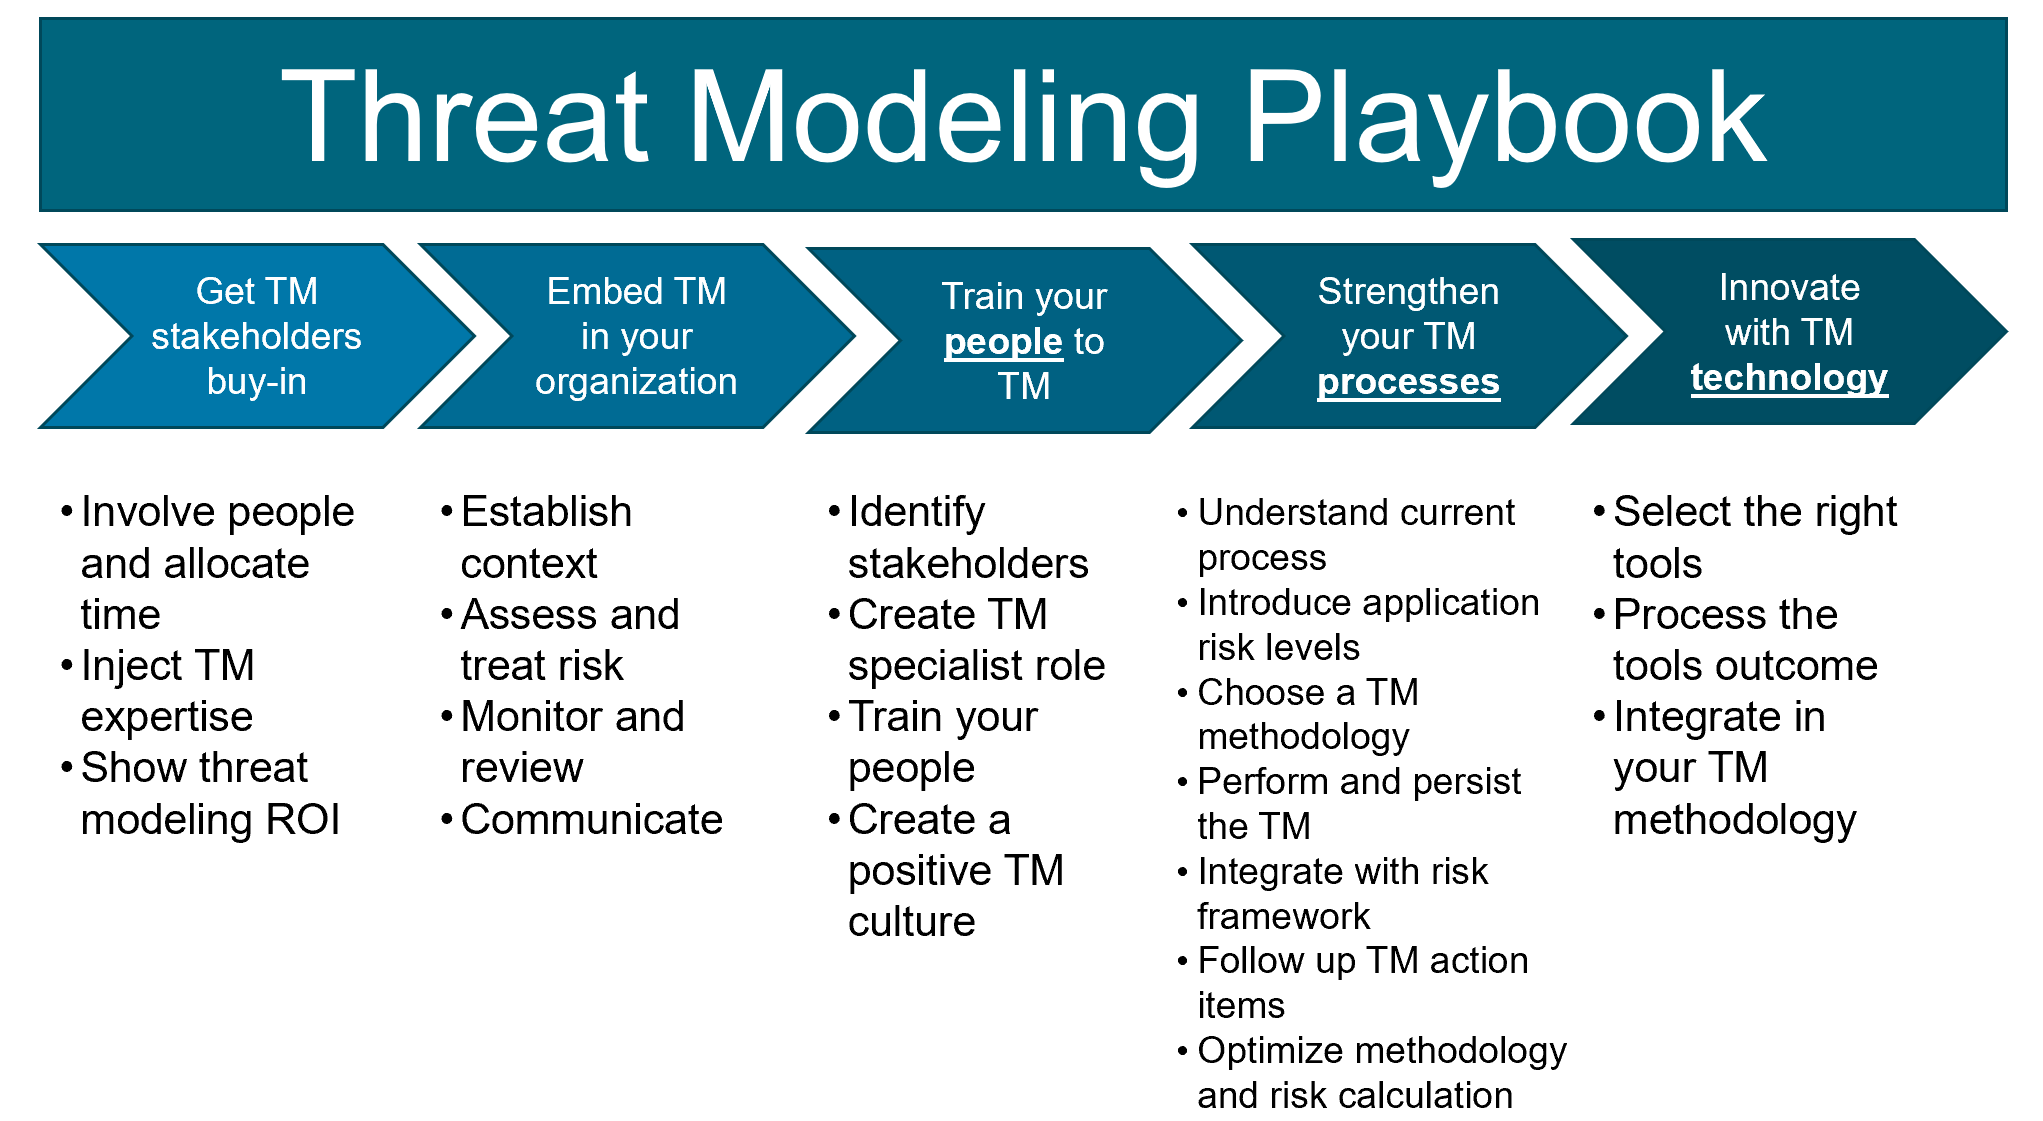 owasp/threat-modeling-playbook
Structured playbook for integrating threat modeling into product security, covering stakeholder buy-in, organizational embedding, training, process…
 oscerd/security-research
Vulnerabilities I've reported to the Apache Software Foundation: 46 CVEs across 15 projects
 harekrishnarai/xz-utils-vuln-checker
Checker for CVE-2024-3094 where malicious code was discovered in the upstream tarballs of xz, starting with version 5.6.0. Through a series of…
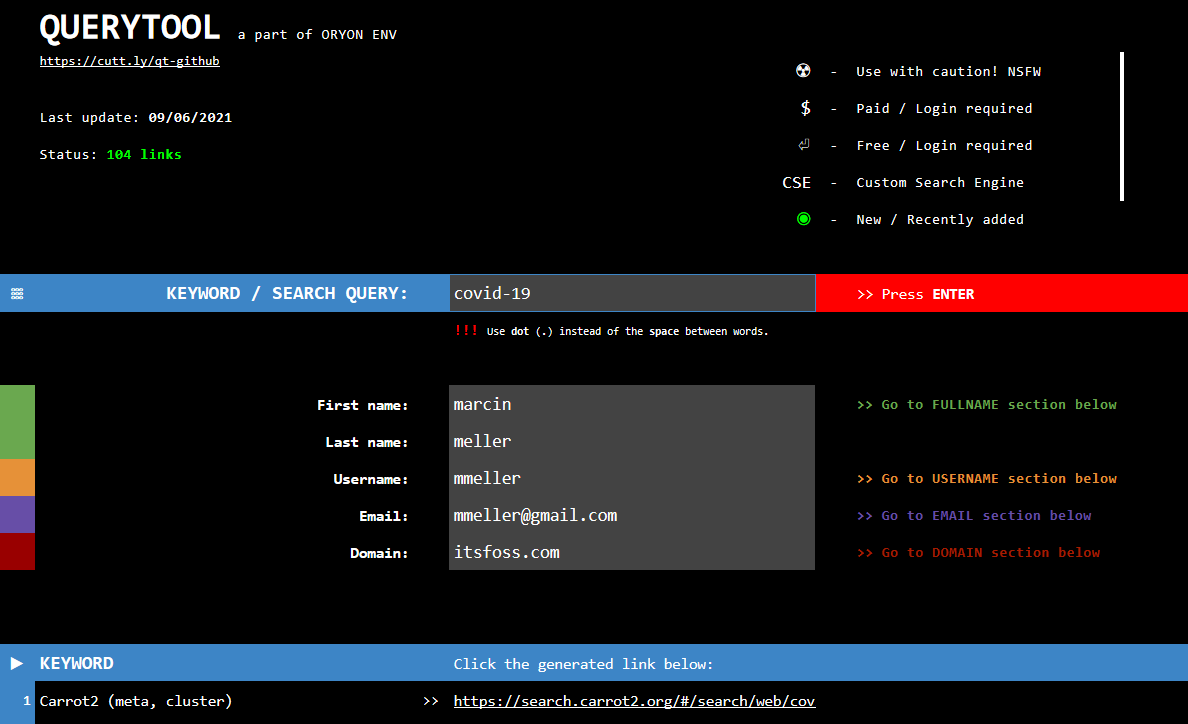 oryon-osint/querytool
Querytool is an OSINT framework based on Google Spreadsheet. With this tool you can perform complex search of terms, people, email addresses, files…
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 owasp/pscf
OWASP framework providing structured security capabilities for software products, derived from regulatory and industry standards analysis to guide…
 matthieu-hackwitharts/win32_offensive_cheatsheet
Win32 and Kernel abusing techniques for pentesters
 7etsuo/windows-api-function-cheatsheets
A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…
 paddycahil/windows-api-function-cheatsheets
A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…
 d3sre/intelligentprocesslifecycle
The Intelligent Process Lifecycle of Active Cyber Defenders
 gmh5225/injection-2
Curated collection of Windows process injection techniques, linking write-ups on Conhost, PROPagate, KernelCallbackTable, KnownDlls poisoning and…