
KingOfBugBountyTips
 kingofbugbounty/kingofbugbountytips
Our main goal is to share tips from some well-known bughunters. Using recon methodology, we are able to find subdomains, apis, and tokens that are…
curated-resourceseducationosint+5
5.6k
kingofbugbounty/kingofbugbountytipsOur main goal is to share tips from some well-known bughunters. Using recon methodology, we are able to find subdomains, apis, and tokens that are…
 sevenolu7/malicious-url-detection-open-source
We collected existing open source code for malicious URL detection
 exploit-garbage/0day-rubbish
Redefining vulnerability disclosure in the AI era. We mass-produce exploitable 0days and disclose them directly, using event-driven pressure to…
 demining/vulnerable-to-debian-openssl-bug-cve-2008-0166
Search for BTC coins on earlier versions of Bitcoin Core with critical vulnerability OpenSSL 0.9.8 CVE-2008-0166
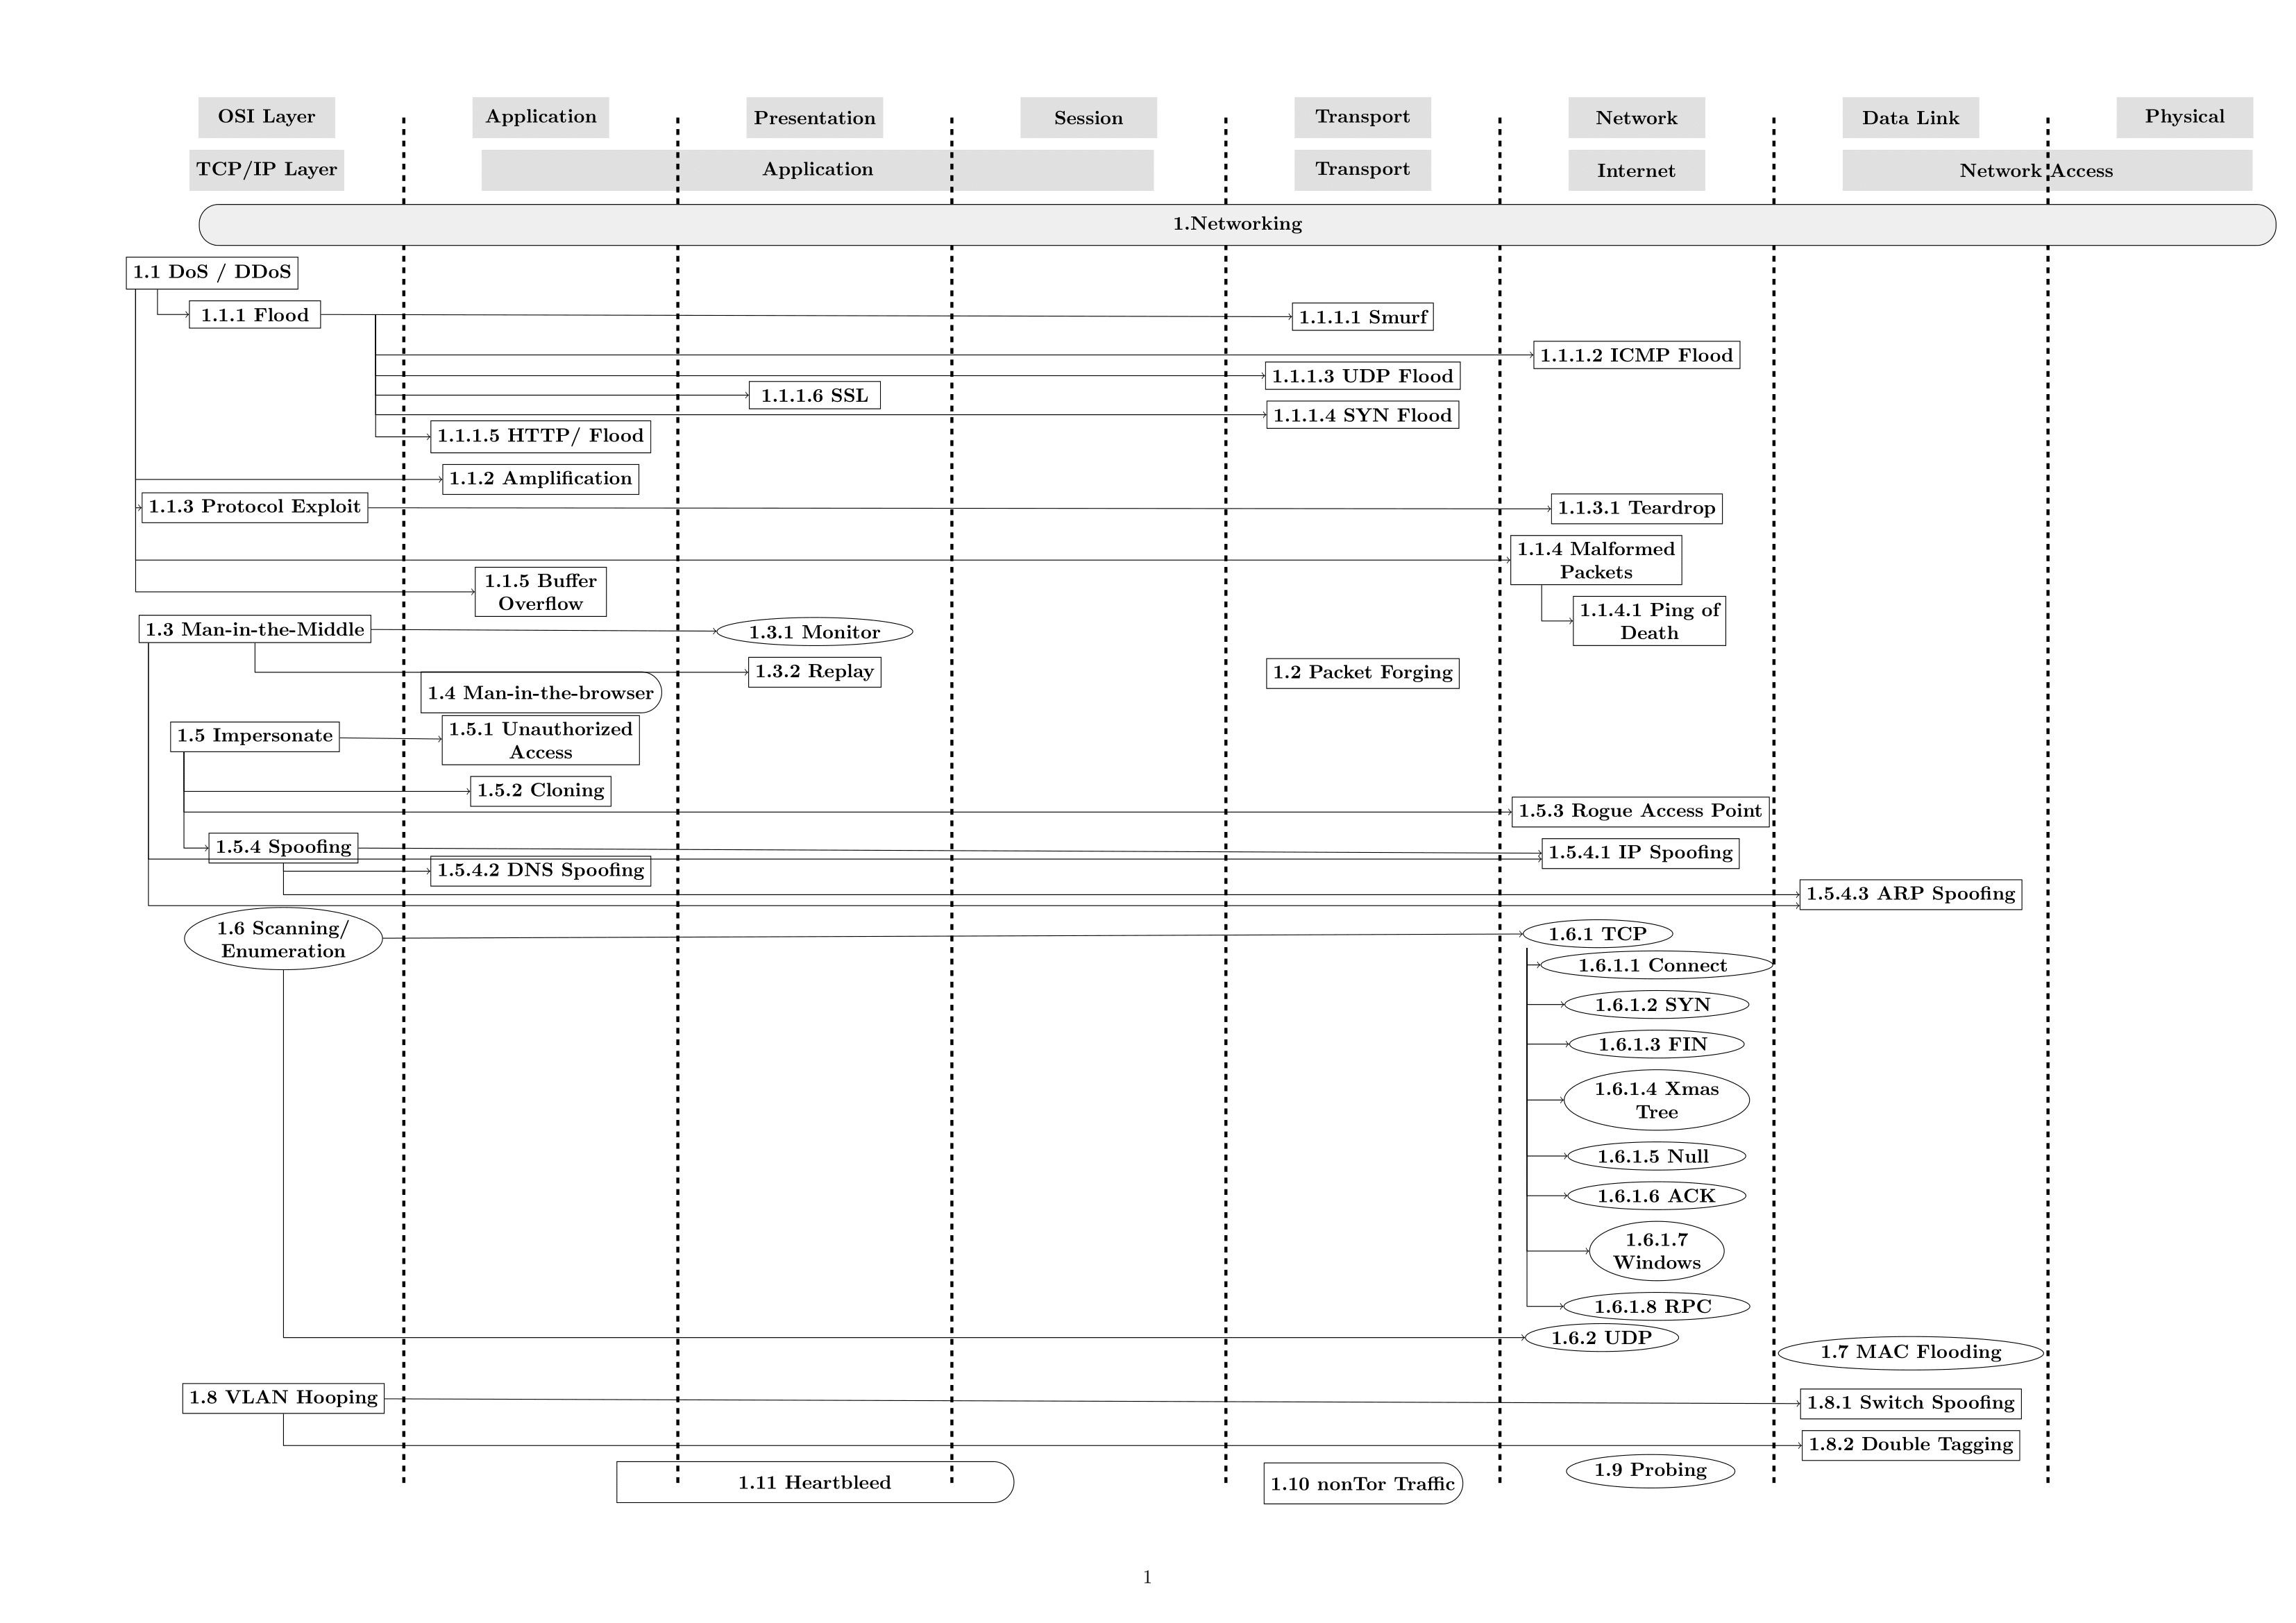 abertaymachinelearninggroup/network-threats-taxonomy
Machine Learning based Intrusion Detection Systems are difficult to evaluate due to a shortage of datasets representing accurately network traffic…
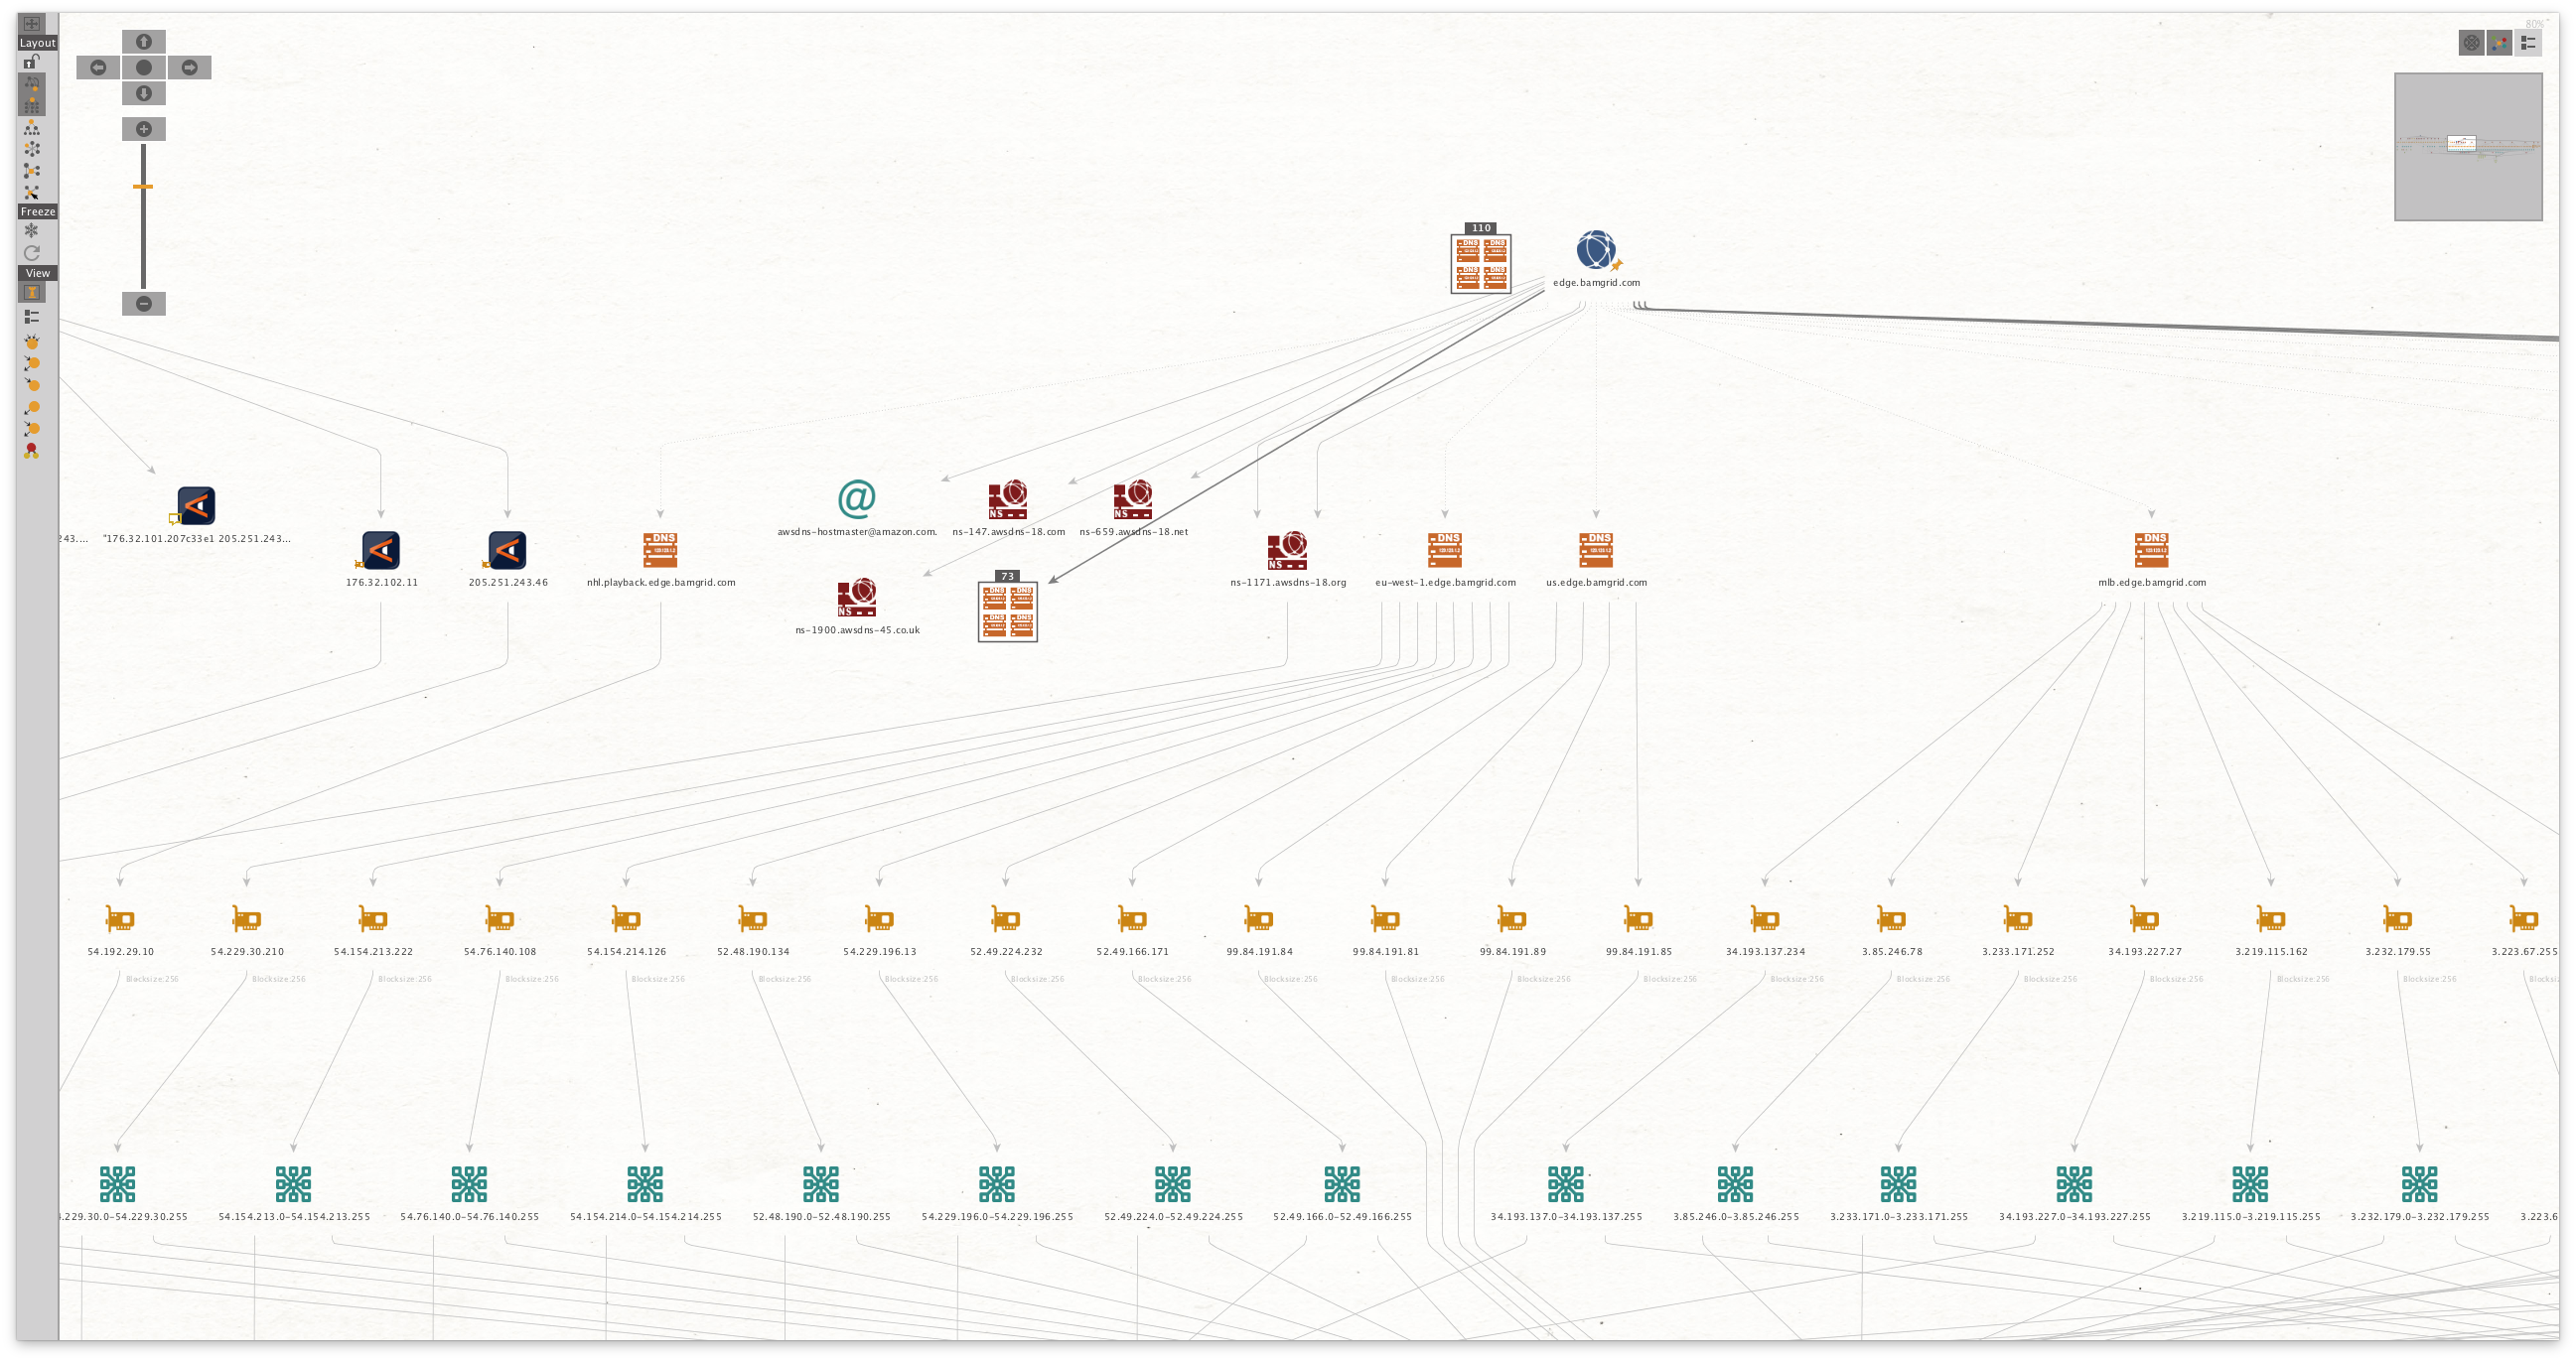 danielcuthbert/trackers
A collection of online trackers, advertising networks, telemetry collectors and general 'we like to watch' lists for you to use to get better control…
 nccgroup/threat-intelligence-alerts
Welcome to the NCC Group Threat Intelligence Alert repo, here you will find the alerts which we have raised to our customers regarding intelligence…
 0xsyr0/log4shell
This repository contains all gathered resources we used during our Incident Reponse on CVE-2021-44228 and CVE-2021-45046 aka Log4Shell.
 bsides-rijeka/meetup-2-curveball
Materials for the second Rijeka secuity meetup. We will be discussing Microsoft cryptoapi vulnerability dubbed CurveBall (CVE-2020-0601)
 papers-we-love/papers-we-love
Papers from the computer science community to read and discuss.
 slowmist/knowledge-base
Curated knowledge base of blockchain security research, audit reports, guides, and translations covering smart contracts, cryptography, and AI…
 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 tmylla/awesome-llm4cybersecurity
Curated systematic literature review of 756+ papers on LLM applications in cybersecurity, covering threat intelligence, vulnerability detection,…
 bushidouk/ransomware-tool-matrix
A resource containing all the tools each ransomware gangs uses
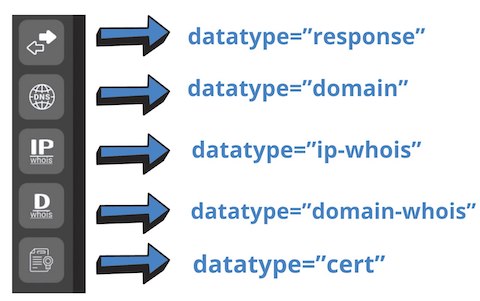 netlas-io/netlas-cookbook
The goal of this guide is very simple - to teach anyone interested in cyber security, regardless of their knowledge level, how to make the most of…
 letsdefend/awesome-soc-analyst
Useful resources for SOC Analyst and SOC Analyst candidates.
 cckuailong/reapoc
OpenSource Poc && Vulnerable-Target Storage Box.
 inquest/yara-rules
Collection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.