
CVE-2025-56218
 saykino/cve-2025-56218
Advisory detailing CVE-2025-56218, an unrestricted file upload vulnerability in Ascertia SigningHub allowing malicious Excel files with phishing…
curated-resourceseducationphishing+2
saykino/cve-2025-56218Advisory detailing CVE-2025-56218, an unrestricted file upload vulnerability in Ascertia SigningHub allowing malicious Excel files with phishing…
 m4now4r/vn_daily_samples
Daily collection of malicious samples originating from Vietnam for malware analysis, threat intelligence, and detection engineering research.
 mbadanoiu/xxe-payloads
Quick access to XXE Payloads
 owasp/owasp-hunting
Curated collection of payloads for ethical security testing and bug bounty hunting, covering common web vulnerabilities and attack vectors.
 gherardofiori/maliciousbrowserextensions
This Repository is created after my own research into malicious browser extensions, by brining the work of many others and news articles into one…
 jstrosch/malware-samples
Malware samples, analysis exercises and other interesting resources.
 otrf/security-datasets
Re-play Security Events
 inquest/yara-rules
Collection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.
 harekrishnarai/xz-utils-vuln-checker
Checker for CVE-2024-3094 where malicious code was discovered in the upstream tarballs of xz, starting with version 5.6.0. Through a series of…
 randomaccess3/detections
Curated repository of detection information and validation guidance for identifying malicious activity in enterprise environments.
 malgamy/yara_rules
Curated signature-rule collection for detecting and classifying malicious files via pattern matching, with CLI instructions for scanning files and…
 hackinglz/extracteddefender
Collection of extracted Microsoft Defender data for security research purposes
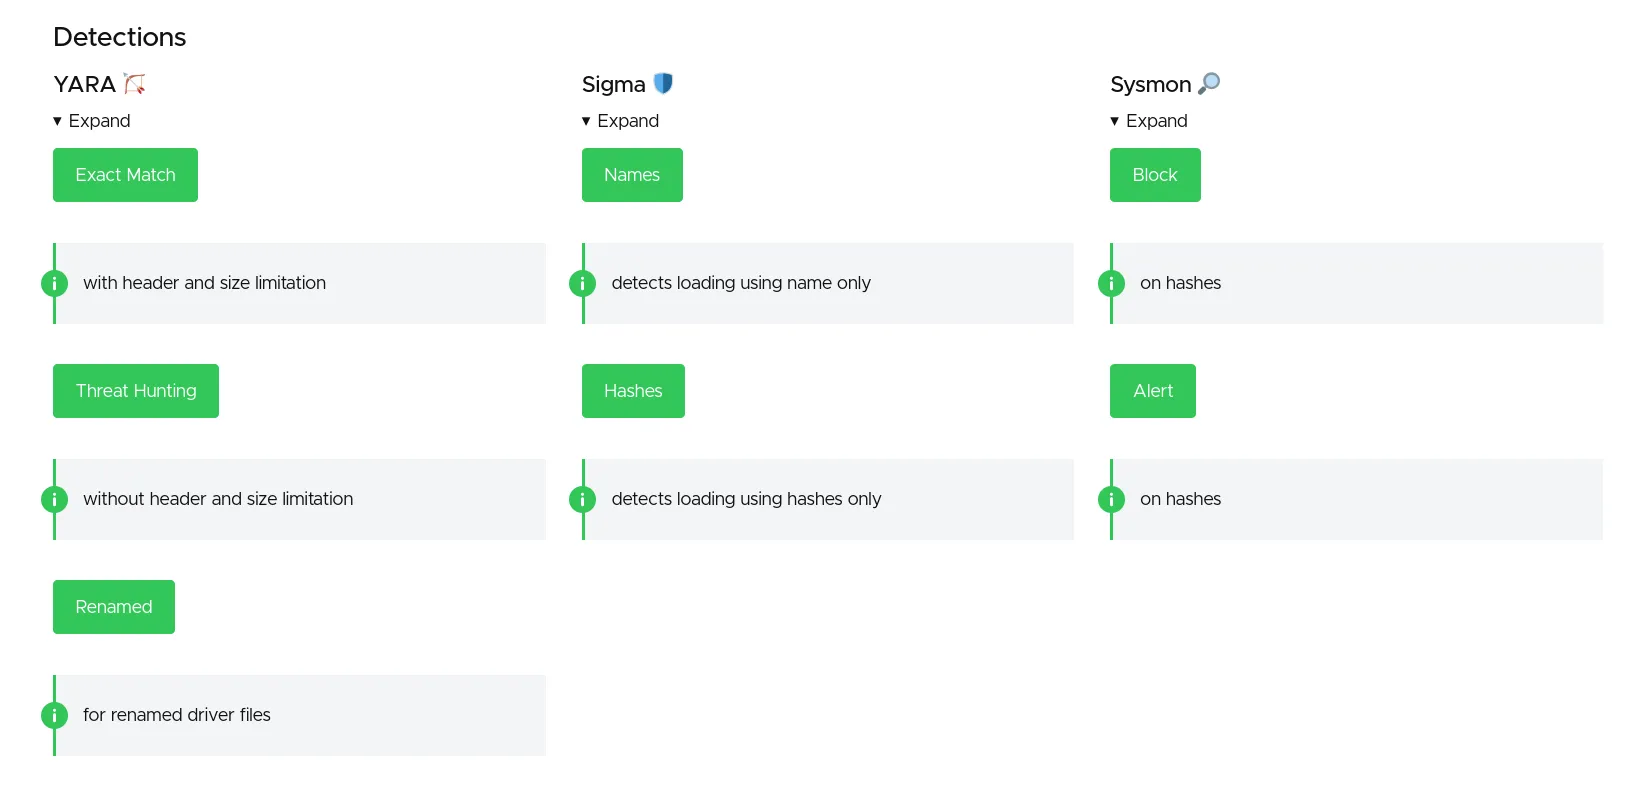 magicsword-io/loldrivers
Curated database of vulnerable and malicious Windows drivers with YARA, Sigma, ClamAV, and Sysmon detection rules for proactive threat hunting and…
 1n3/intruderpayloads
A collection of Burpsuite Intruder payloads, BurpBounty payloads, fuzz lists, malicious file uploads and web pentesting methodologies and checklists.
 sheeki03/tirith
Terminal security for developers and AI agents. Intercepts homograph URLs, pipe-to-shell, ANSI injection, obfuscated payloads, data exfiltration, and…
 toborrm9/malicious_extension_sentry
Malicious Extension Database
 andreassudo/cve-2026-21510-cvss-8.8-important-windows-shell-security-feature-bypass
Detailed analysis of CVE-2026-21510, a Windows Shell security feature bypass allowing silent code execution via malicious links or shortcuts.…
 sevenolu7/malicious-url-detection-open-source
We collected existing open source code for malicious URL detection