
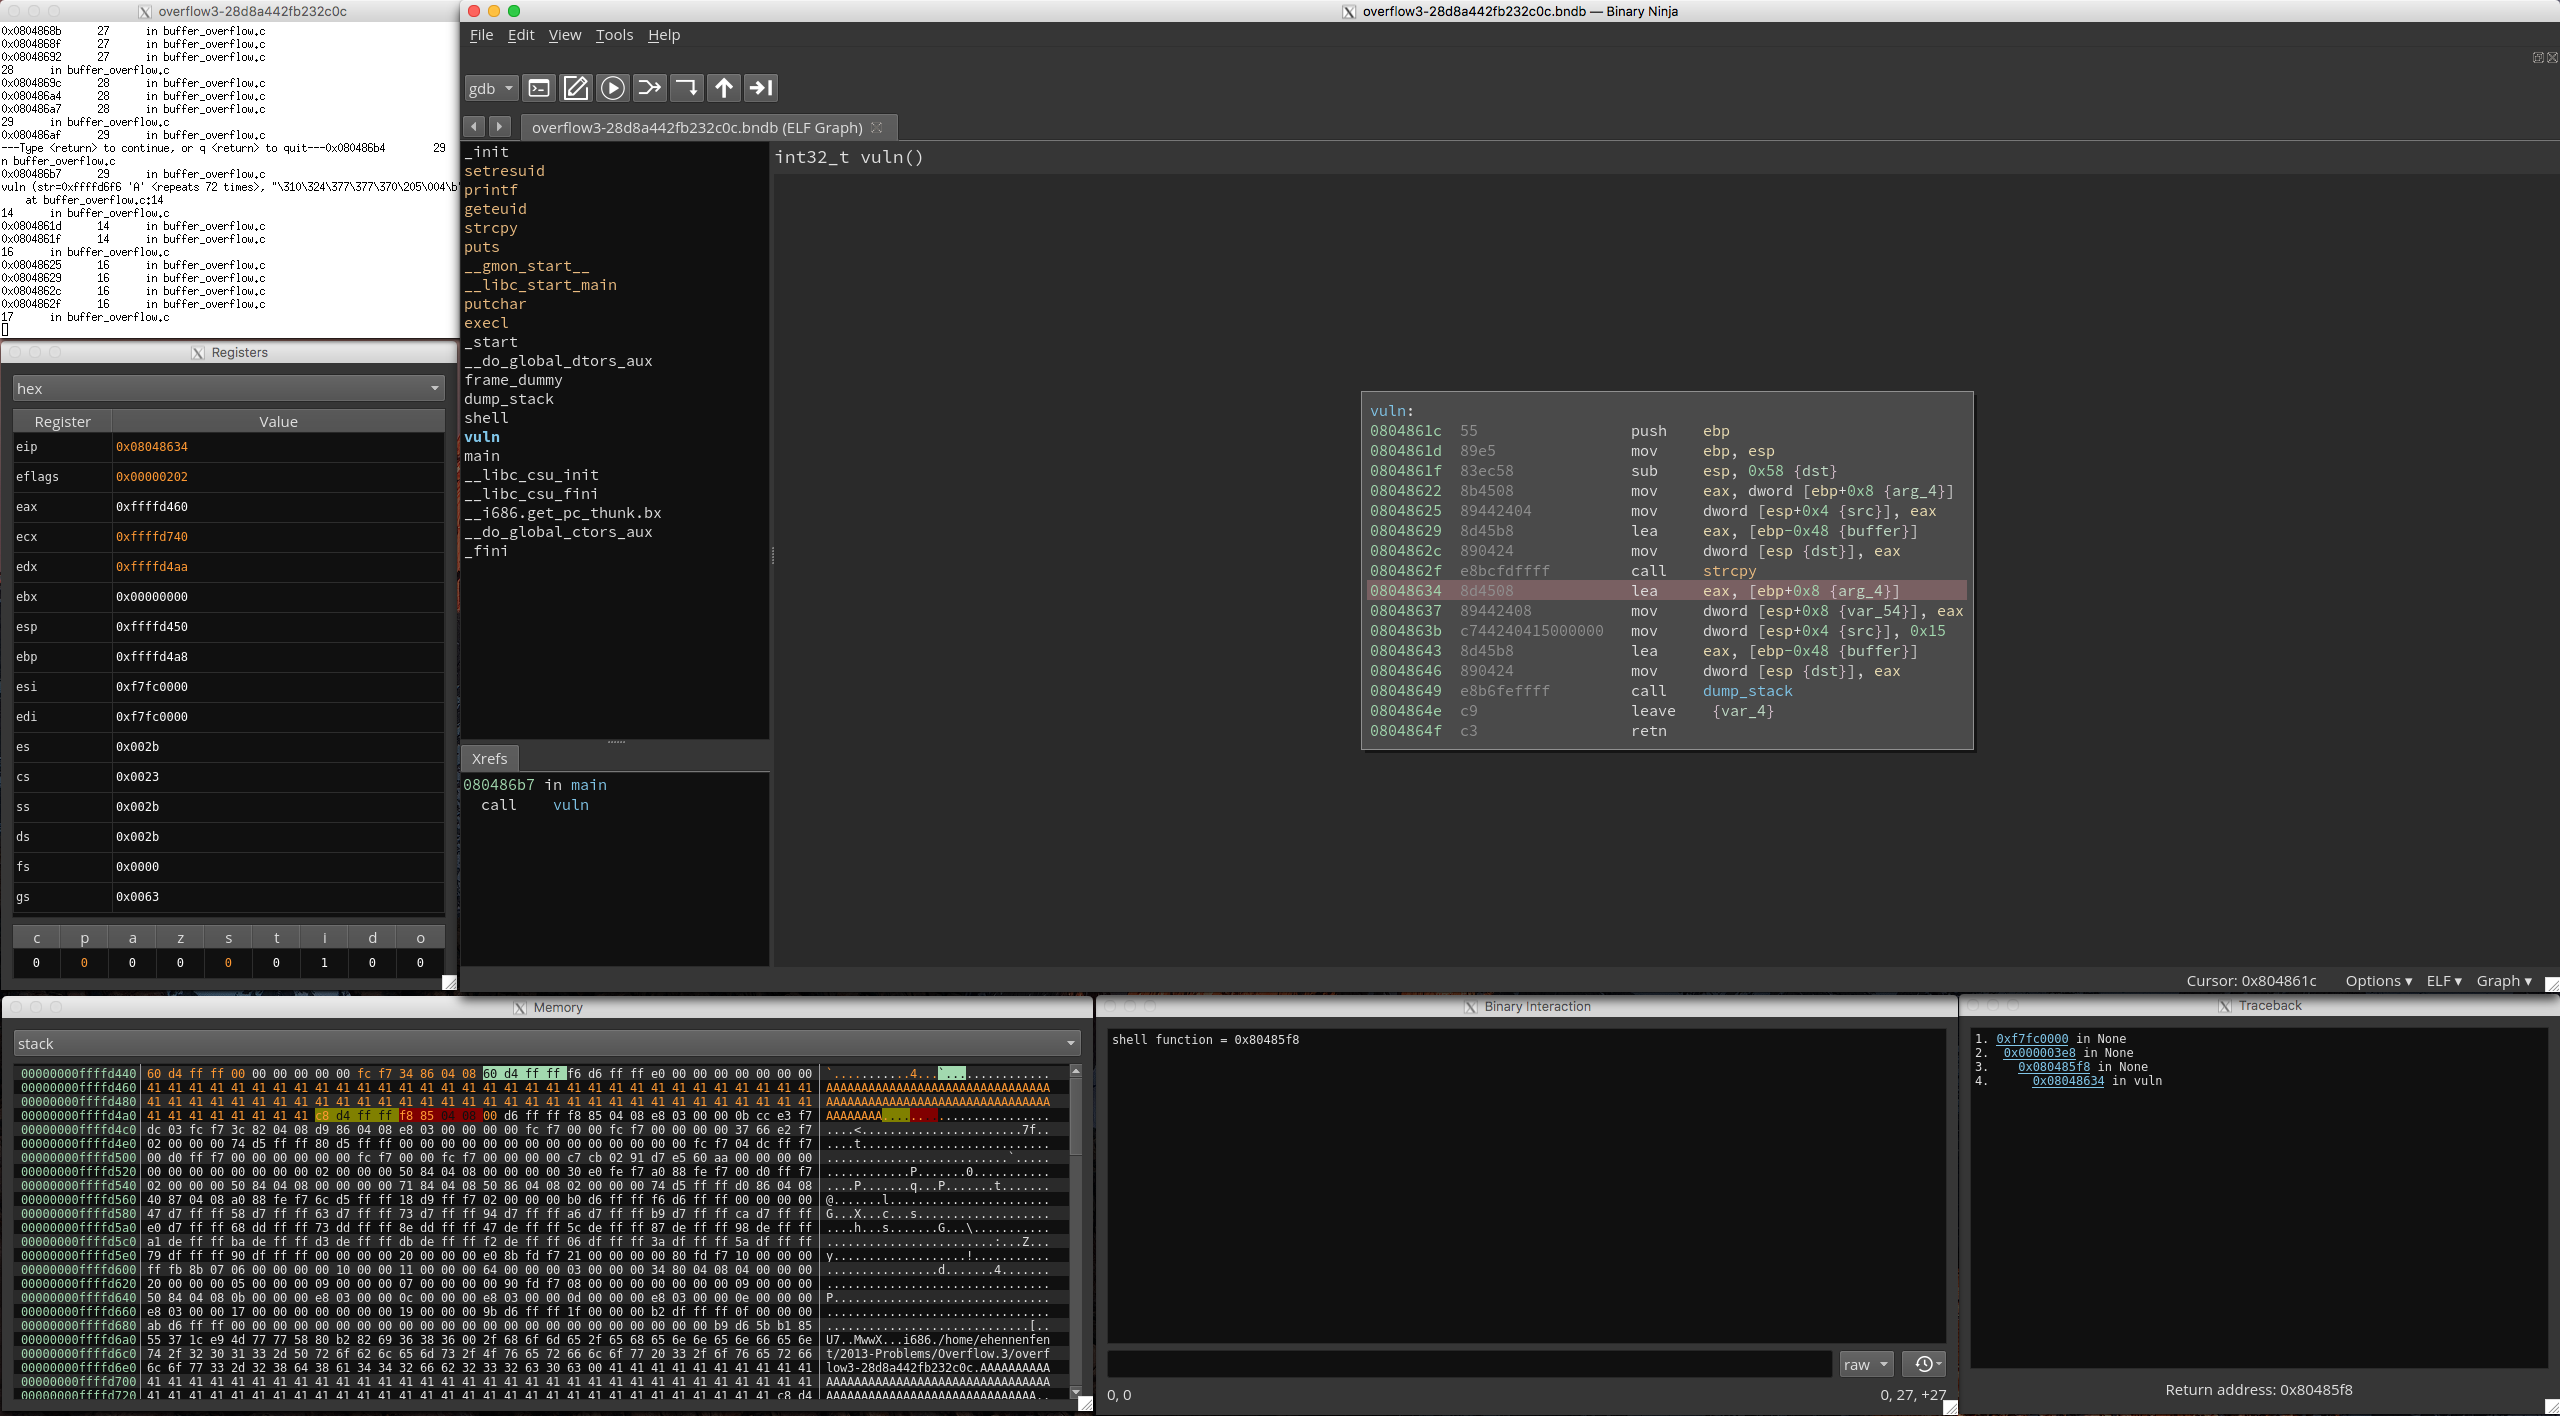
binja_sensei
 nccgroup/binja_sensei
A plugin that provides resources for beginners to learn reverse engineering using Binary Ninja. It automatically installs several other plugins, and…
binary-analysisbinary-exploitationctf+4
26
nccgroup/binja_senseiA plugin that provides resources for beginners to learn reverse engineering using Binary Ninja. It automatically installs several other plugins, and…
 taielab/awesome-hacking-lists
A curated collection of top-tier penetration testing tools and productivity utilities across multiple domains. Join us to explore, contribute, and…
 v33ru/awesome-connected-things-sec
A Curated list of Security Resources for all connected things
 idoka/awesome-canbus
:articulated_lorry: Awesome CAN bus tools, hardware and resources for Cyber Security Researchers, Reverse Engineers, and Automotive Electronics…

 security-prince/resources-for-application-security
Some good resources for getting started with application security
 ronankongala/metasploit-pentest-report
Authorized penetration test against Metasploitable2 and TryHackMe Blue. 3 CVEs exploited (CVE-2011-2523, CVE-2007-2447, CVE-2017-0144), 4 findings…
 sunweb3sec/defihacklabs
Reproduce DeFi hacked incidents using Foundry.
 mr-xn/burpsuite-collections
有关burpsuite的插件(非商店),文章以及使用技巧的收集(此项目不再提供burpsuite破解文件,如需要请在博客mrxn.net下载)---Collection of burpsuite plugins (non-stores), articles and tips for using…
 kingofbugbounty/kingofbugbountytips
Our main goal is to share tips from some well-known bughunters. Using recon methodology, we are able to find subdomains, apis, and tokens that are…
 flangvik/sharpcollection
Nightly builds of common C# offensive tools, fresh from their respective master branches built and released in a CDI fashion using Azure DevOps…
 infosecn1nja/ad-attack-defense
Attack and defend active directory using modern post exploitation adversary tradecraft activity
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 exploit-garbage/0day-rubbish
Redefining vulnerability disclosure in the AI era. We mass-produce exploitable 0days and disclose them directly, using event-driven pressure to…
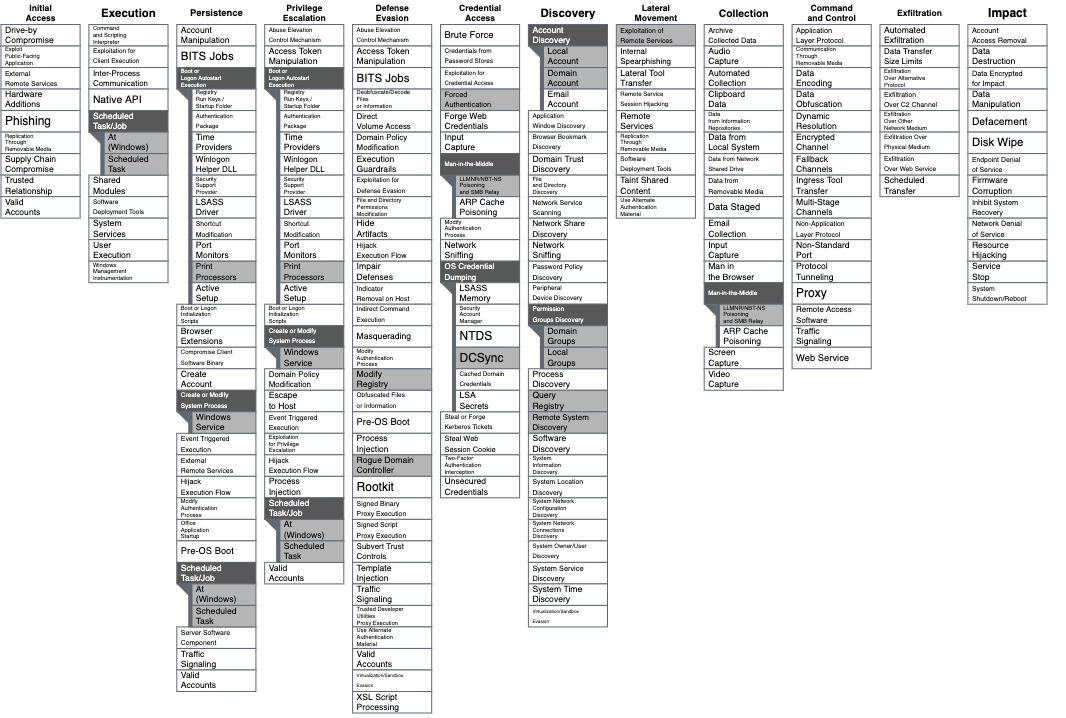 jonny-jhnson/msrpc-to-attack
A repository that maps commonly used attacks using MSRPC protocols to ATT&CK
 corelight/threat-hunting-guide
Structured guide to threat hunting using Zeek logs, aligned with MITRE ATT&CK framework for proactive detection of adversary tactics and techniques.
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 sourcegraph/log4j-cve-code-search-resources
Using code search to help fix/mitigate log4j CVE-2021-44228