Vulnerable-to-Debian-OpenSSL-bug-CVE-2008-0166

Search for BTC coins on earlier versions of Bitcoin Core with critical vulnerability OpenSSL 0.9.8 CVE-2008-0166

Search for BTC coins on earlier versions of Bitcoin Core with critical vulnerability OpenSSL 0.9.8 CVE-2008-0166

Browser-based Merkle tree demo — build a tree, generate inclusion proofs, recompute the root hash by hash, and replay the RFC 6962 second-preimage…

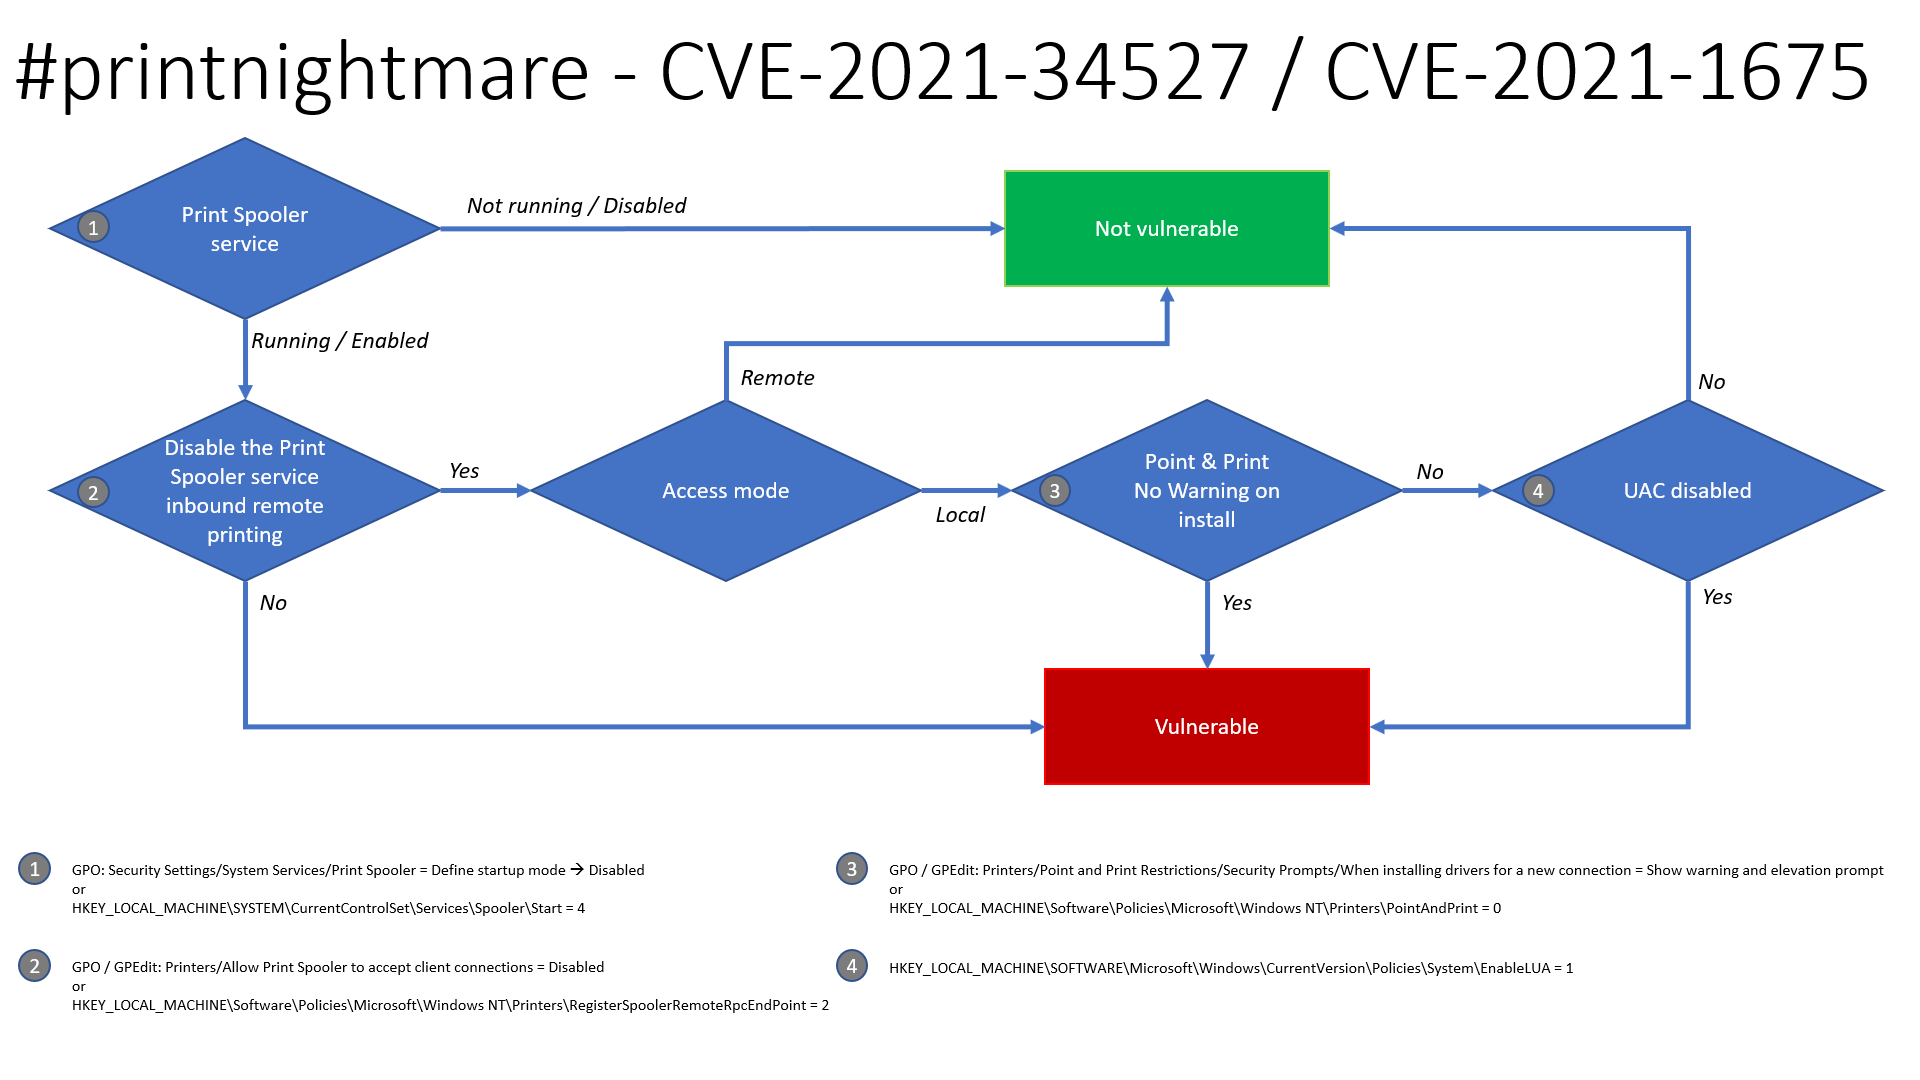
CVE-2021-1675 Detection Info

Collection of Cyber Threat Intelligence sources from the deep and dark web

This repo contains hourly-updated data dumps of bug bounty platform scopes (like Hackerone/Bugcrowd/Intigriti/etc) that are eligible for reports

Curated collection of tools, bookmarks, and guides for open-source intelligence (OSINT) gathering, reconnaissance, and information gathering.

Community curated list of public bug bounty and responsible disclosure programs.

A list of Google Dorks for Bug Bounty, Web Application Security, and Pentesting

A collection of fascinating and bizarre Censys Search Queries

A wordlist of API names for web application assessments

STIX 2.1 collections of the MITRE ATT&CK knowledge base, providing adversary tactics and techniques for enterprise, mobile, and ICS threat…

This Repositories contains list of One Liners with Descriptions and Installation requirements

This repository contains indicators of compromise (IOCs) of our various investigations.

Curated wordlists of API function names, verbs, and nouns for fuzzing web application endpoints with Burp Suite Intruder.

Curated repository of threat actor aliases and naming schemes used by major threat intelligence vendors, enabling cross-vendor search, attribution,…

This is the repository for indicators of compromise (IOCs) and other data for threat intelligence articles posted on the Palo Alto Networks Unit 42…

Extracting OSINT Insights from 15TB of GitHub Event Logs

Structured OSINT dataset of LockBit ransomware-linked identities, including usernames, IDs, join dates, Bitcoin addresses, and media artifacts for…