

PayloadsAllTheThings
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
ctfcurated-resourceseducation+8
80.8k
swisskyrepo/payloadsallthethingsA list of useful payloads and bypass for Web Application Security and Pentest/CTF
 infoslack/awesome-web-hacking
Curated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…
 taksec/google-dorks-bug-bounty
A list of Google Dorks for Bug Bounty, Web Application Security, and Pentesting
 nu11secur1ty/payload-lists
Curated collection of injection payloads for web application security testing, covering SSTI, XXE, XSS, SSRF, SQLi, NoSQLi, LDAP, command injection,…
 h3x0v3rl0rd/xss-payload-list
Curated collection of XSS payload vectors for web application security testing, covering various contexts and bypass techniques.

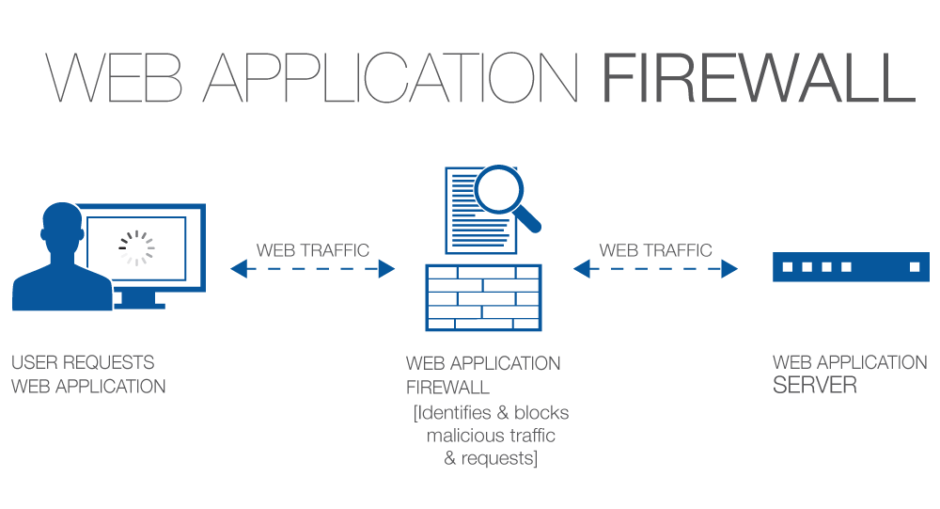 0xinfection/awesome-waf
Everything about Web Application Firewalls (WAFs) from Security Standpoint! 🔥
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 paragonie/awesome-appsec
A curated list of resources for learning about application security
 six2dez/wahh_extras
The Web Application Hacker's Handbook - Extra Content
 cy-clon3/awesome-ios-security
A curated list of awesome iOS application security resources.
 owasp/asvs
Application Security Verification Standard
 xalgord/massive-web-application-penetration-testing-bug-bounty-notes
A comprehensive guide for web application penetration testing and bug bounty hunting, covering methodologies, tools, and resources for identifying…
 chrislockard/api_wordlist
A wordlist of API names for web application assessments
 cisagov/decider
A web application that assists network defenders, analysts, and researchers in the process of mapping adversary behaviors to the MITRE ATT&CK®…
 waf-bypass-maker/waf-community-bypasses
Curated CSV collection of community-sourced Web Application Firewall bypass payloads for testing and validating WAF protections.
 numencyber/vulnerability_poc
Collection of proof-of-concept exploits and technical analyses for high-impact CVEs, covering browser memory corruption, TCP/IP RCE, and web…
 net-hunter121/api-wordlist
Curated wordlists of API function names, verbs, and nouns for fuzzing web application endpoints with Burp Suite Intruder.