Metabase_CVE-2021-41277
 vulnmachines/metabase_cve-2021-41277
Exploit for Metabase CVE-2021-41277, a local file inclusion vulnerability in custom GeoJSON map support, allowing unauthorized file access.
ctfcurated-resourceseducation+3
4
vulnmachines/metabase_cve-2021-41277Exploit for Metabase CVE-2021-41277, a local file inclusion vulnerability in custom GeoJSON map support, allowing unauthorized file access.
 chaitanyagarware/cve-2026-50181
Curated landing page for CVE-2026-50181, documenting a Langroid path traversal vulnerability (CWE-22/23) with links to GHSA, NVD, and public database…
 paparojonathan/cve-2026-9335-keras-hdf5-externallink
CVE-2026-9335: KerasFileEditor and load_weights follow h5py ExternalLinks, disclosing arbitrary local HDF5 file contents in keras ≤ 3.14.0. Advisory…
 haluka92/cve-2025-47423
Detailed disclosure of CVE-2025-47423: Local File Inclusion in Personal Weather Station Dashboard 12_lts. Includes PoC, vulnerable code analysis, and…
 harekrishnarai/xz-utils-vuln-checker
Checker for CVE-2024-3094 where malicious code was discovered in the upstream tarballs of xz, starting with version 5.6.0. Through a series of…
 saykino/cve-2025-56218
Advisory detailing CVE-2025-56218, an unrestricted file upload vulnerability in Ascertia SigningHub allowing malicious Excel files with phishing…
 doerrdan/it-sec-toolshell
Marp slide deck detailing CVE-2025-53770, a SharePoint zero-day vulnerability, with modular slides, custom themes, and build scripts for HTML, PDF,…
 k0nnect/cve-2026-21440-writeup-poc
poc and writeup for cve-2026-21440: a critical path traversal vulnerability in @adonisjs/bodyparser allowing arbitrary file writing
 redyank/cve-2026-35492
Demonstrates CVE-2026-35492, a path traversal vulnerability in kedro-datasets PartitionedDataset allowing arbitrary file write, with impact analysis…
 recorded-texteditor120/cve-2026-31802
Demonstrate and analyze the CVE-2026-31802 path traversal vulnerability in npm tar, enabling arbitrary file overwrite via symlink extraction.
 mr-xn/blackhat_usa2022
BLACKHAT USA2022 PDF Public
 ruattd/cve-2026-31431
GitHub Actions workflow to test if the runner is vulnerable to CVE-2026-31431, confirming root privileges in a controlled environment.
 bx33661/cve-2026-30039
Security advisory and bilingual write-up detailing CVE-2026-30039, a symlink traversal vulnerability in rarfile affecting versions up to 4.2, leading…
 gylq/cve-2022-3464
A vulnerability classified as problematic has been found in puppyCMS up to 5.1. This affects an unknown part of the file /admin/settings.php. The…
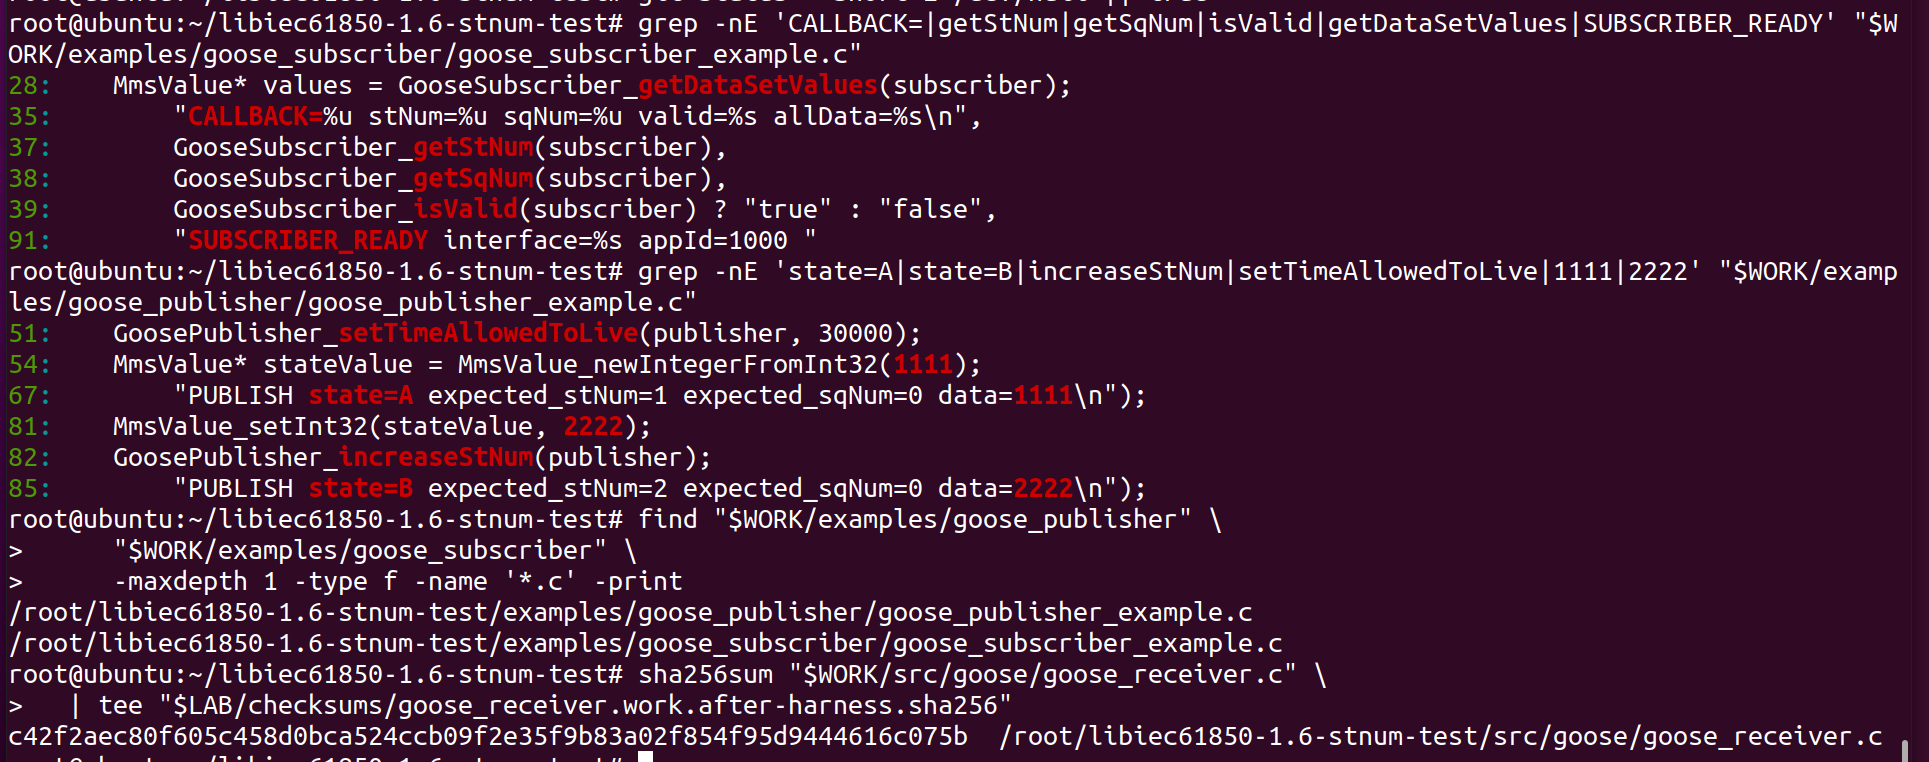 if-forget/cve-2026-52134-libiec61850
Public technical advisory and reproduction evidence for CVE-2026-52134 affecting GOOSE replay handling in libiec61850 v1.6.
 kagancapar/cve-2026-54984
CVE-2026-54984 / ZDI-26-543: Windows ICC file parsing out-of-bounds write (CWE-122, CVSS 7.8)
 chaitanyagarware/cve-2026-54520
Public advisory landing page documenting CVE-2026-54520, a high-severity path traversal vulnerability in ai-agent-automation's workflow executor,…