

third-thoughts
 lightless-labs/third-thoughts
Research toolkit for analyzing AI agent behavioral patterns through multi-disciplinary corpus analysis. Parses session logs, runs 23 analytical…
ai-securityanomaly-detectioncurated-resources+5
3
lightless-labs/third-thoughtsResearch toolkit for analyzing AI agent behavioral patterns through multi-disciplinary corpus analysis. Parses session logs, runs 23 analytical…
 geeksikhsecurity/ai-tool-poisoning-guard
Free security-baseline rule for Claude Code, Codex, and Cursor: treats MCP tool descriptions as untrusted input (OWASP MCP Top 10 MCP03,…
 jacobideji/aiiroverlay
AI IR Overlay™ — practical incident response framework for AI agents in production. Built on NIST SP 800-61 r3, mapped to NIST AI RMF, NIST CSF 2.0,…
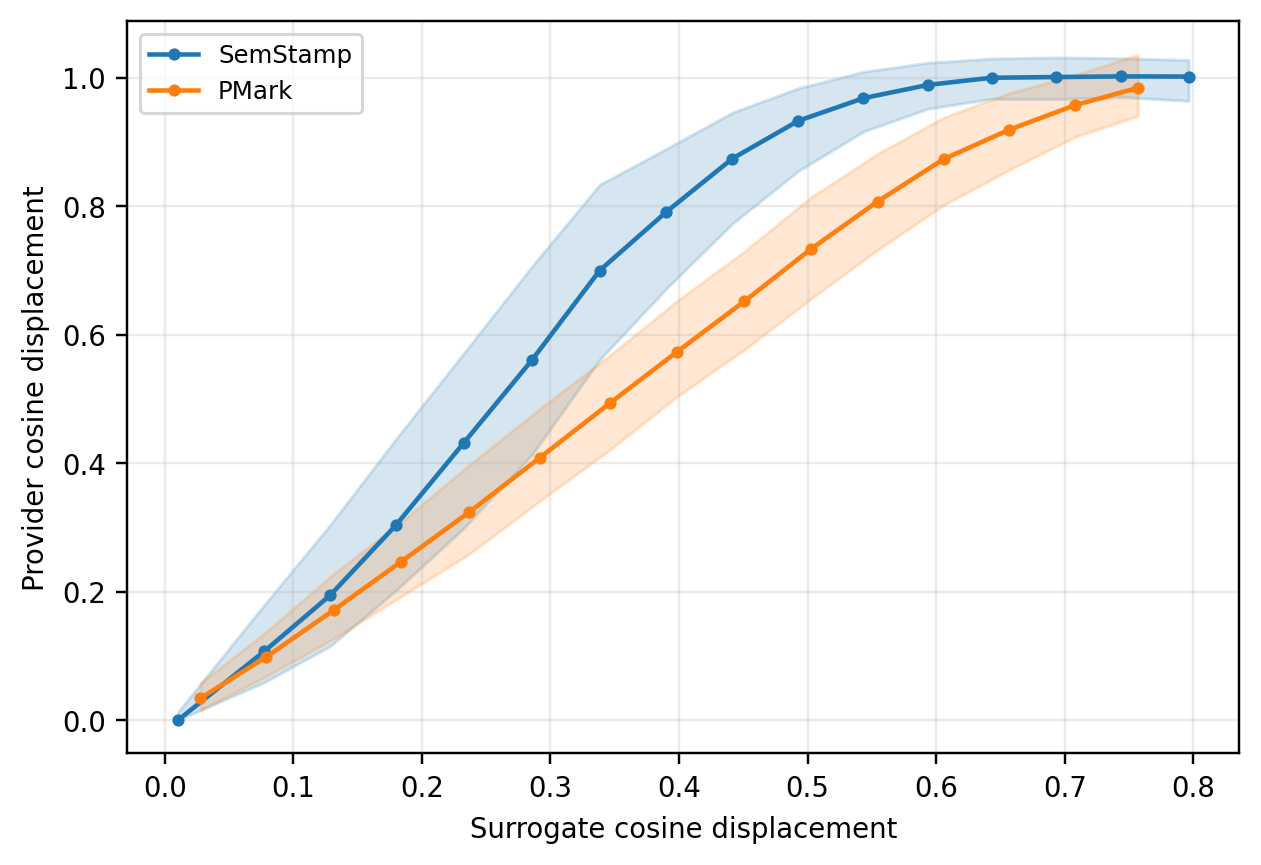 d-diaa/swordstamp
Semantic Watermarking with Order-Robust Detection over Sub-sentence Units
 owasp/owasp-top-10-ai-infrastructure-security-risks
A practical framework identifying and prioritizing the top security risks in AI datacenter infrastructure, covering hardware, networking, management…
 pathakabhi24/llm-mcp-security-field-guide
The most comprehensive LLM + MCP security guide i.e. OWASP aligned, real CVEs, actionable checklists
 appsec-forge/appsec-forge
Structured security knowledge base with production-inspired cases: vulnerability analysis, exploit explanation, remediation, and DevSecOps for…
 pduggusa/dugganusa-ietf
DugganUSA threat-intelligence contributions to the IETF Hackathon — real-world agentic-attack benchmark vectors, CVE-2026-33697 attestation analysis,…
 owasp/owasp-model-card-security-standard
Open standard for documenting security-relevant metadata of AI models, including training data provenance, PII risk, known vulnerabilities, and…
 horkimhab/llm-prompt-injection-resources
A curated collection of resources for learning and researching LLM prompt injection attacks, defenses, and security.
 nanashibx2/bx2-writeups
Cybersecurity writeups, walkthroughs, and technical notes by Nanashi Bx2.
 nightfullstar/openclaw-defender
Multi-layer security framework for AI agent ecosystems. Provides pre-installation skill auditing, file integrity monitoring, runtime protection, and…
 owasp/agent-skills-security-standard
Security standard for agent skills, providing guidelines and best practices to secure AI-driven autonomous agents in cloud and API environments.
 chaitanyagarware/cve-2026-54519
Public advisory landing page for CVE-2026-54519: missing ownership checks in ai-agent-automation memory APIs enabling cross-user memory read and…
 zeltoc/threat-intel-brief-cve-2026-42208-litellm
Threat intelligence brief on CVE-2026-42208, a critical pre-auth SQL injection in BerriAI LiteLLM exploited within 36 hours of disclosure. Covers…
 nexaiceo/nexus-os
The Governed Agentic AI Operating System — Rust + Tauri 2.0 | 65 crates, 658 commands, 84 pages, 5,029 tests, 10/10 OWASP
 roninforge/roninforge-angularjs-migration
AngularJS 1.x -> Angular 18 migration guidance for GitHub Copilot. Source-of-truth repo for…
 openexecution-coder/demo-cve-2026-4821
Demonstrates AI agent-driven CVE remediation with cryptographic provenance tracking, showcasing detection, analysis, human approval, and verification…