
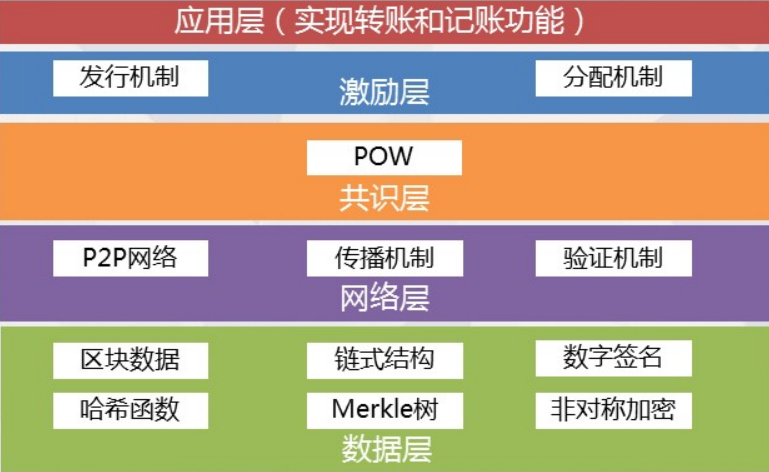
BlockChainConstruction
 al1ex/blockchainconstruction
BlockChain Security Construction
code-analysiscryptographycurated-resources+3
3
al1ex/blockchainconstructionBlockChain Security Construction
 pvharmo2/gha-lab-6ab39df295
Controlled security-research lab reproducing CVE-2024-45798 (GHSA-h52q-xhg2-6jw8) in espressif/arduino-esp32 — poisoned-artifact pwn request via…
 suominen/cve-2026-9256
Tracking the nginx CVE-2026-9256 rewrite-module heap overflow
 suominen/ipv6_frag_escape
Tracking IPV6_FRAG_ESCAPE (CVE-2026-53362, CVE-2026-53366), the IPv6 fragmentation container escape
 suominen/ghostlock
Tracking GhostLock (CVE-2026-43499), the rtmutex/futex stack use-after-free
 suominen/ovswrap
Tracking OVSwrap (CVE-2026-64531), the Open vSwitch datapath netlink overflow
 suominen/cve-2026-31431
Tracking Copy Fail (CVE-2026-31431), the Linux algif_aead privilege escalation
 suominen/pintheft
Tracking PinTheft (CVE-2026-43494, CVE-2026-43502), the RDS zerocopy double-free privilege escalation
 suominen/cifswitch
Tracking CIFSwitch (CVE-2026-46243), the CIFS cifs.spnego key-origin privilege escalation
 m8seven/cve-2026-22874-gitea-ssrf-allowlist
CVE-2026-22874 writeup: incomplete SSRF allow-list in Gitea webhook/migration (IPv6 transition and cloud metadata). Fixed in Gitea 1.26.3.
 kaleth4/cve-2026-7482
Technical analysis and educational documentation of CVE-2026-7482, a critical heap buffer over-read in Ollama's GGUF loader, including exploitation…
 pvharmo2/gha-lab-2f775f277c
Authorized lab reproduction of CVE-2025-47928 (spotipy-dev/spotipy pull_request_target secrets exfiltration) — snapshot at vulnerable commit 4f5759d
 sims718718/unifiedthreathunting
Documents a structured, repeatable threat hunting methodology covering triggers, SMART hypotheses, feasibility gates, scoping, hunt plans, and…