
tirith
 sheeki03/tirith
Terminal security for developers and AI agents. Intercepts homograph URLs, pipe-to-shell, ANSI injection, obfuscated payloads, data exfiltration, and…
curated-resourcesdata-exfiltrationdevsecops+8
sheeki03/tirithTerminal security for developers and AI agents. Intercepts homograph URLs, pipe-to-shell, ANSI injection, obfuscated payloads, data exfiltration, and…
 toborrm9/malicious_extension_sentry
Malicious Extension Database
 magicsword-io/loldrivers
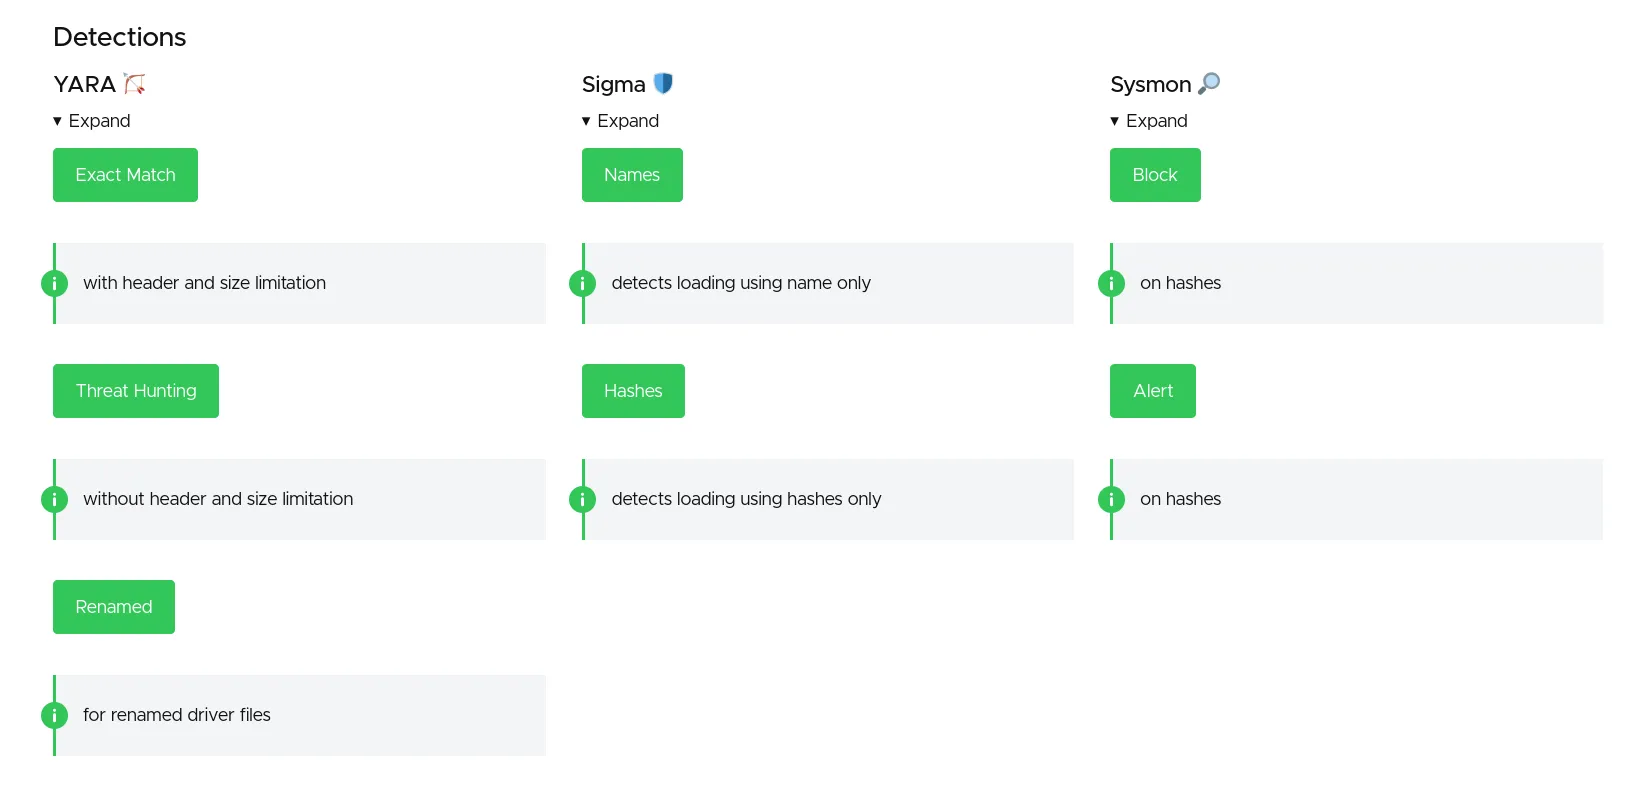
Curated database of vulnerable and malicious Windows drivers with YARA, Sigma, ClamAV, and Sysmon detection rules for proactive threat hunting and…
 blackorbird/apt_report
Interesting APT Report Collection And Some Special IOCs
 gherardofiori/maliciousbrowserextensions
This Repository is created after my own research into malicious browser extensions, by brining the work of many others and news articles into one…
 owasp/owasp-hunting
Curated collection of payloads for ethical security testing and bug bounty hunting, covering common web vulnerabilities and attack vectors.
 mr-r3b00t/cyber_rss
a list of useful feeds
 randomaccess3/detections
Curated repository of detection information and validation guidance for identifying malicious activity in enterprise environments.
 andreassudo/cve-2026-21510-cvss-8.8-important-windows-shell-security-feature-bypass
Detailed analysis of CVE-2026-21510, a Windows Shell security feature bypass allowing silent code execution via malicious links or shortcuts.…
 saykino/cve-2025-56218
Advisory detailing CVE-2025-56218, an unrestricted file upload vulnerability in Ascertia SigningHub allowing malicious Excel files with phishing…
 sevenolu7/malicious-url-detection-open-source
We collected existing open source code for malicious URL detection
 gi7w0rm/malwareconfiglists
Just some lists of Malware Configs

 harekrishnarai/xz-utils-vuln-checker
Checker for CVE-2024-3094 where malicious code was discovered in the upstream tarballs of xz, starting with version 5.6.0. Through a series of…
 inquest/malware-samples
A collection of malware samples and relevant dissection information, most probably referenced from http://blog.inquest.net
 jstrosch/malware-samples
Malware samples, analysis exercises and other interesting resources.
 m4now4r/vn_daily_samples
Daily collection of malicious samples originating from Vietnam for malware analysis, threat intelligence, and detection engineering research.
 mbadanoiu/xxe-payloads
Quick access to XXE Payloads