
Vulns
 strik3r0x1/vulns
Collection of public proof-of-concept exploits for multiple CVEs, providing vulnerability demonstration code and references for security research and…
curated-resourcesexploitationpapers-research+2
5
strik3r0x1/vulnsCollection of public proof-of-concept exploits for multiple CVEs, providing vulnerability demonstration code and references for security research and…
 rknf404/chromium-hardening-guide
Harden chromium (somewhat) for privacy and security (and performance)
 google/bughunters
Reference resources for Google's vulnerability reward programs, including domain tiers, OSS repository tier lists, and rewarded patch examples for…
 arpsyndicate/vedas-signatures
VEDAS-Driven Autonomous Generation + Community Contributions of Suricata & Nuclei Rules for over 12000 CVEs
 portswigger/xss-cheatsheet-data
Community-contributed JSON dataset of XSS payload vectors powering the PortSwigger XSS cheat sheet, with browser support and interaction metadata.
 pvharmo2/gha-lab-51c6b6d0a0
Lab reproducing CVE-2025-67727 (parse-community/parse-server ci-performance.yml pull_request_target RCE at e78e58d) — authorized security research
 viralmaniar/vulnvault
Developer-focused knowledge base of application security vulnerabilities with insecure vs secure code examples, prevention guidance, and OWASP/CWE…
 carlosalbertotuma/advisory
Public security advisories and PoCs for vulnerabilities discovered in open-source web software, with root-cause analysis, CVE references,…
 cylock11/cve-list
A collection of CVE exploits, including Python PoCs and README files with instructions for reproducing and exploiting each vulnerability.
 ut-dacs/anycast-census
Longitudinal anycast census system that probes IPv4/IPv6 prefixes via ICMP, TCP, and DNS to detect anycast deployments and geolocate PoPs, publishing…
 mitsu-bis/security-portfolio
Security portfolio of original responsible-disclosure findings, CTF and lab write-ups, methodology notes, and purpose-built pentest tooling covering…
 leox48/cve-2026-1769-writeup
Public write-up and disclosure timeline for CVE-2026-1769 (Stored XSS in Xerox CentreWare Web)
 blackarch/blackarch
An ArchLinux based distribution for penetration testers and security researchers.
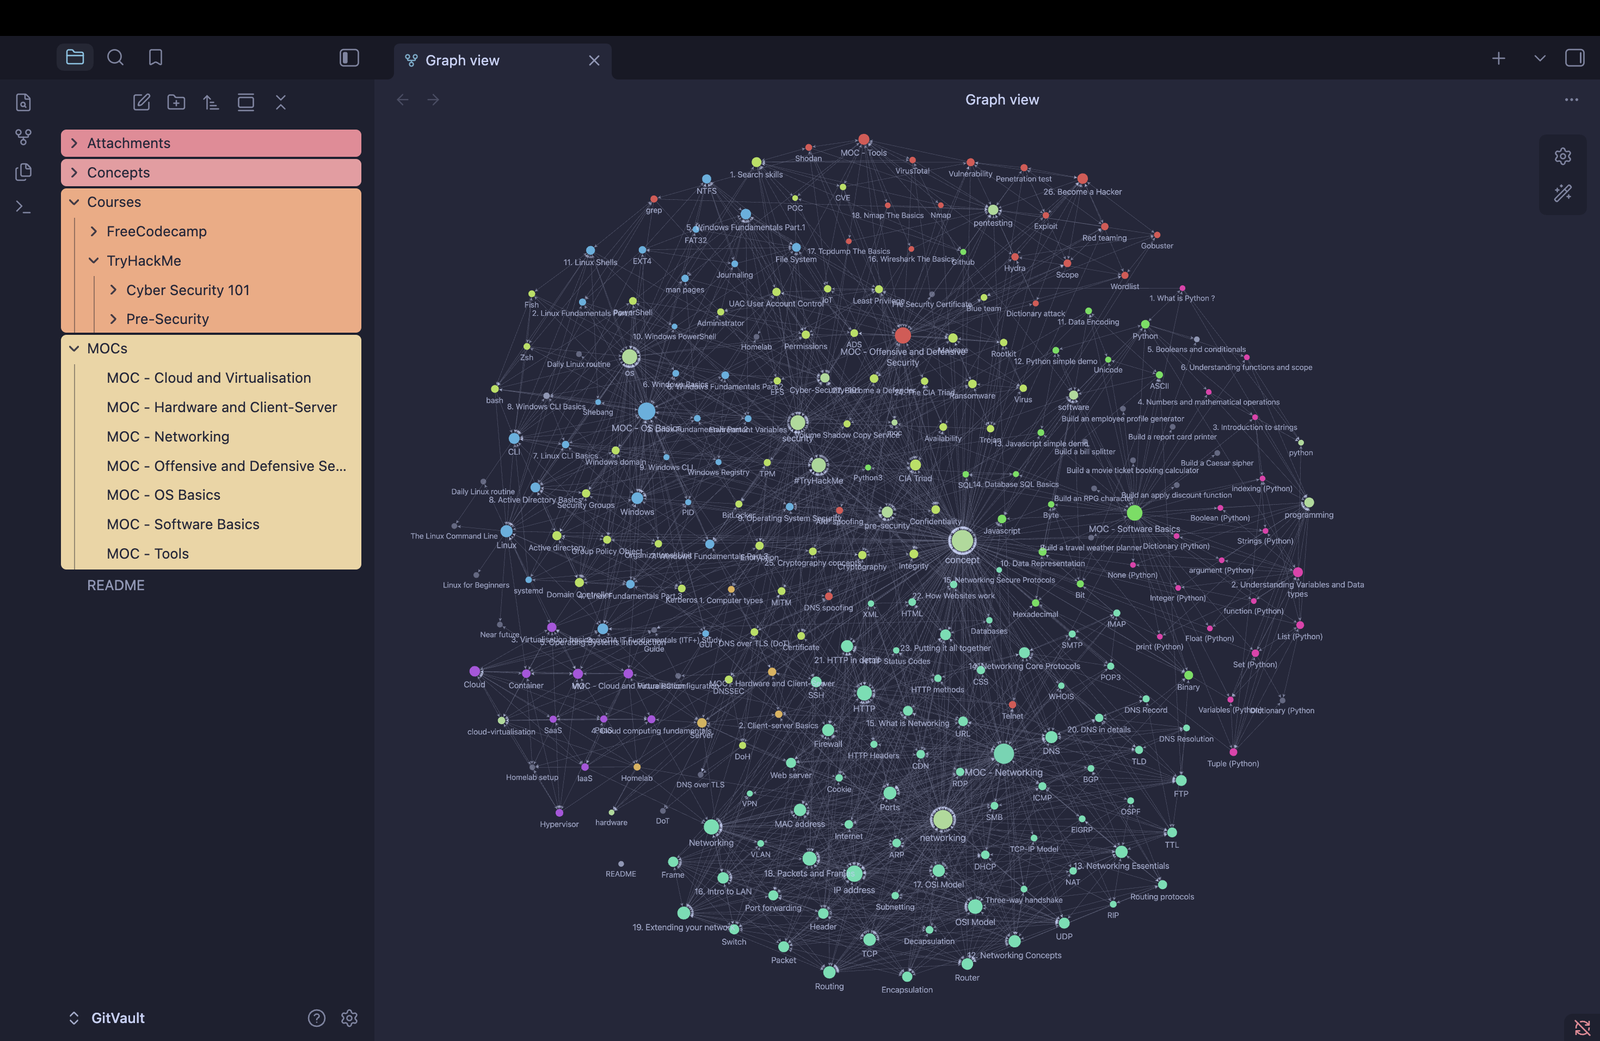 gitowl58/gitvault
A beginner Obsidian Vault structure for Cybersecurity, Linux, Homelabbing / Self-hosting, all about sharing knowledge.
 prince325/cve-2026-93659-writeup
Stored XSS in Concrete CMS Community Store leads to admin dashboard takeover
 ghoxtbyte/cve-2026-16265
Technical advisory and research notes for CVE-2026-16265, a Subscriber+ denial-of-service flaw in the WP Maps WordPress plugin fixed in version 4.9.7.
 ghoxtbyte/cve-2026-18464
Security advisory and technical research notes for CVE-2026-18464, an unauthenticated denial-of-service flaw in the WP Maps Pro WordPress plugin…
 ekitji/siem
Curated SIEM queries and techniques for offensive discovery of Windows privilege escalation, misconfigured ACLs, services, scheduled tasks, and…