
lab
 chakshugupta13/lab
Code artifacts from research paper implementations
cryptographycurated-resourceseducation+2
chakshugupta13/labCode artifacts from research paper implementations
 domssilva/vulnsearch
A deep look at some recon methodologies and web-application vulnerabilities of my interest where I will merge all my notes gathered from books,…
 github/advisory-database
Security vulnerability database inclusive of CVEs and GitHub originated security advisories from the world of open source software.
 doctorwebltd/malware-iocs
Curated Indicators of Compromise (IOCs) from Doctor Web malware investigations, published for threat intelligence, detection engineering, and…
 inquest/yara-rules
Collection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.
 tencent-hunyuan/diagsafe
Diagnostic LLM safety benchmark with 3,489 bilingual prompts, an 84-label taxonomy, and prompt-level rubric judging for explainable, fine-grained…
 emrekybs/veiled-eye
OSINT identity investigation tool. Pivot from an e-mail, username, phone or wallet across 46 sources into one profile and relationship graph.
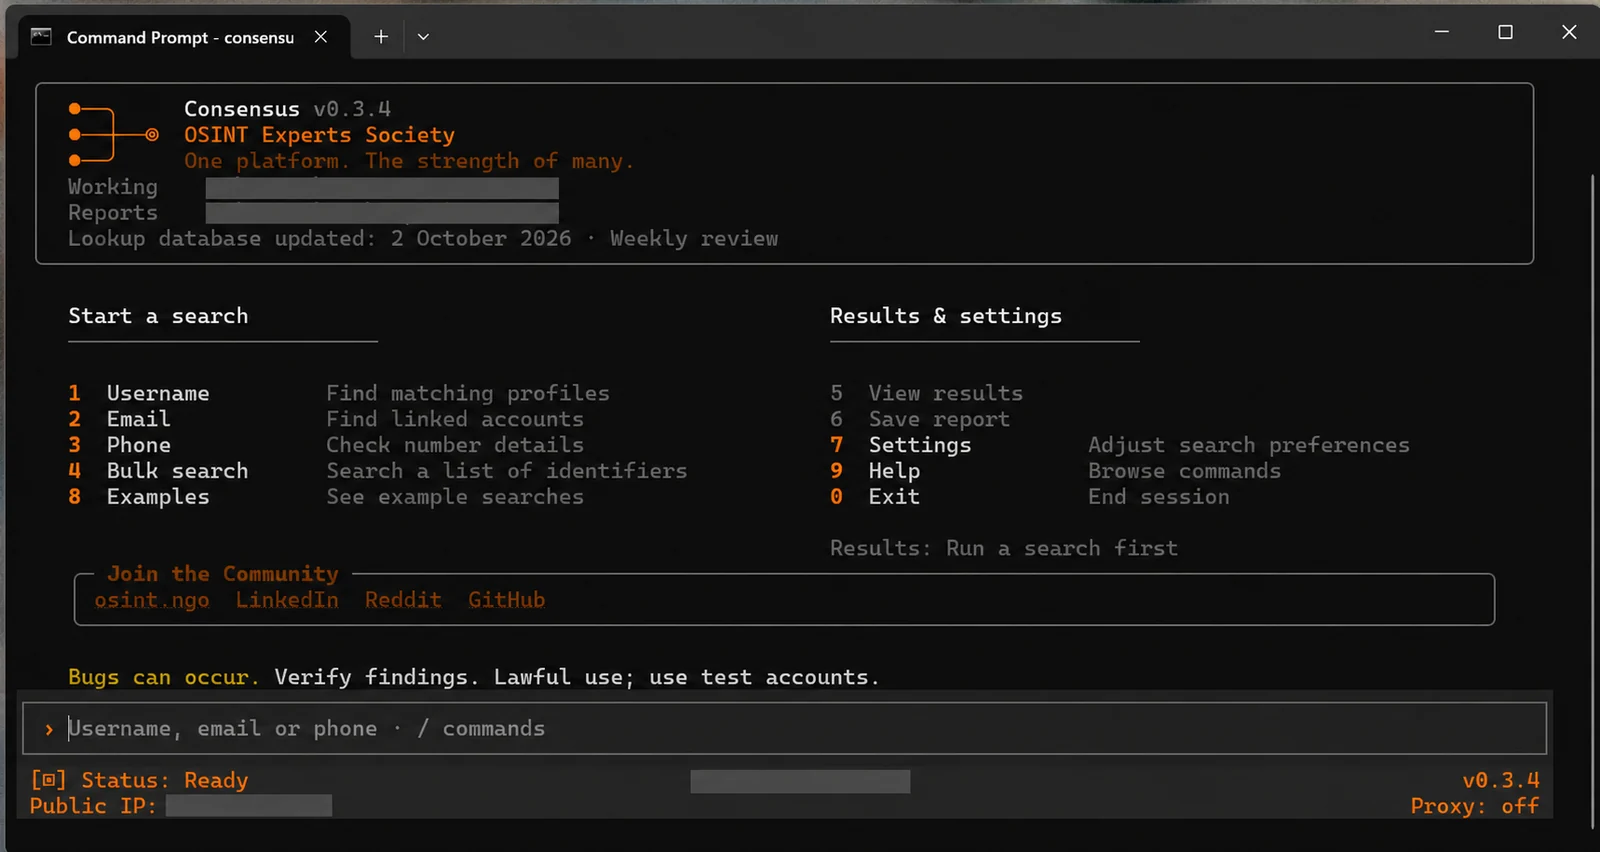 osint-experts-society/consensus-osint
🔎 Username, email & phone OSINT — 9,700+ lookup checks from 19 projects, with profile enrichment, bulk searches, evidence graphs and expert-reviewed…
 kypvas/ad_attack_architecture
Active Directory Attack Architecture Map Comprehensive Pentest Reference — From Recon to Domain Dominance
 kypvas/red-team-map
Red Team Operations Architecture Map Comprehensive Operator Reference — From Infrastructure to Impact
 cisagov/vulnrichment
A repo to conduct vulnerability enrichment.
 cyber-courses/cyber-library
Community-maintained Markdown knowledge base covering cybersecurity foundations, offensive and defensive practice, governance, threat intelligence,…
 rknf404/chromium-hardening-guide
Harden chromium (somewhat) for privacy and security (and performance)
 linnemanlabs/advisories
Curated Linux security advisories with CVE write-ups and reproducible proof-of-concept exploits covering local privilege escalation and authorization…
 kiteworks/security-advisories
Publishes Kiteworks security advisories and CVE disclosures, including vulnerability details, disclosure policy, and bug bounty information for…
 securewithumer/exploit-index
Zero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
 sims718718/unifiedthreathunting
Documents a structured, repeatable threat hunting methodology covering triggers, SMART hypotheses, feasibility gates, scoping, hunt plans, and…
 jeeberrr/honeypot-stuff
Stuff like malware analysis reports on things I captured from my honeypot