Information-Security-Tasks

Curated infosec knowledge base of practitioner notes, methodologies, and daily-updated CVE, news, and tool digests organized by offensive, defensive,…

Curated infosec knowledge base of practitioner notes, methodologies, and daily-updated CVE, news, and tool digests organized by offensive, defensive,…

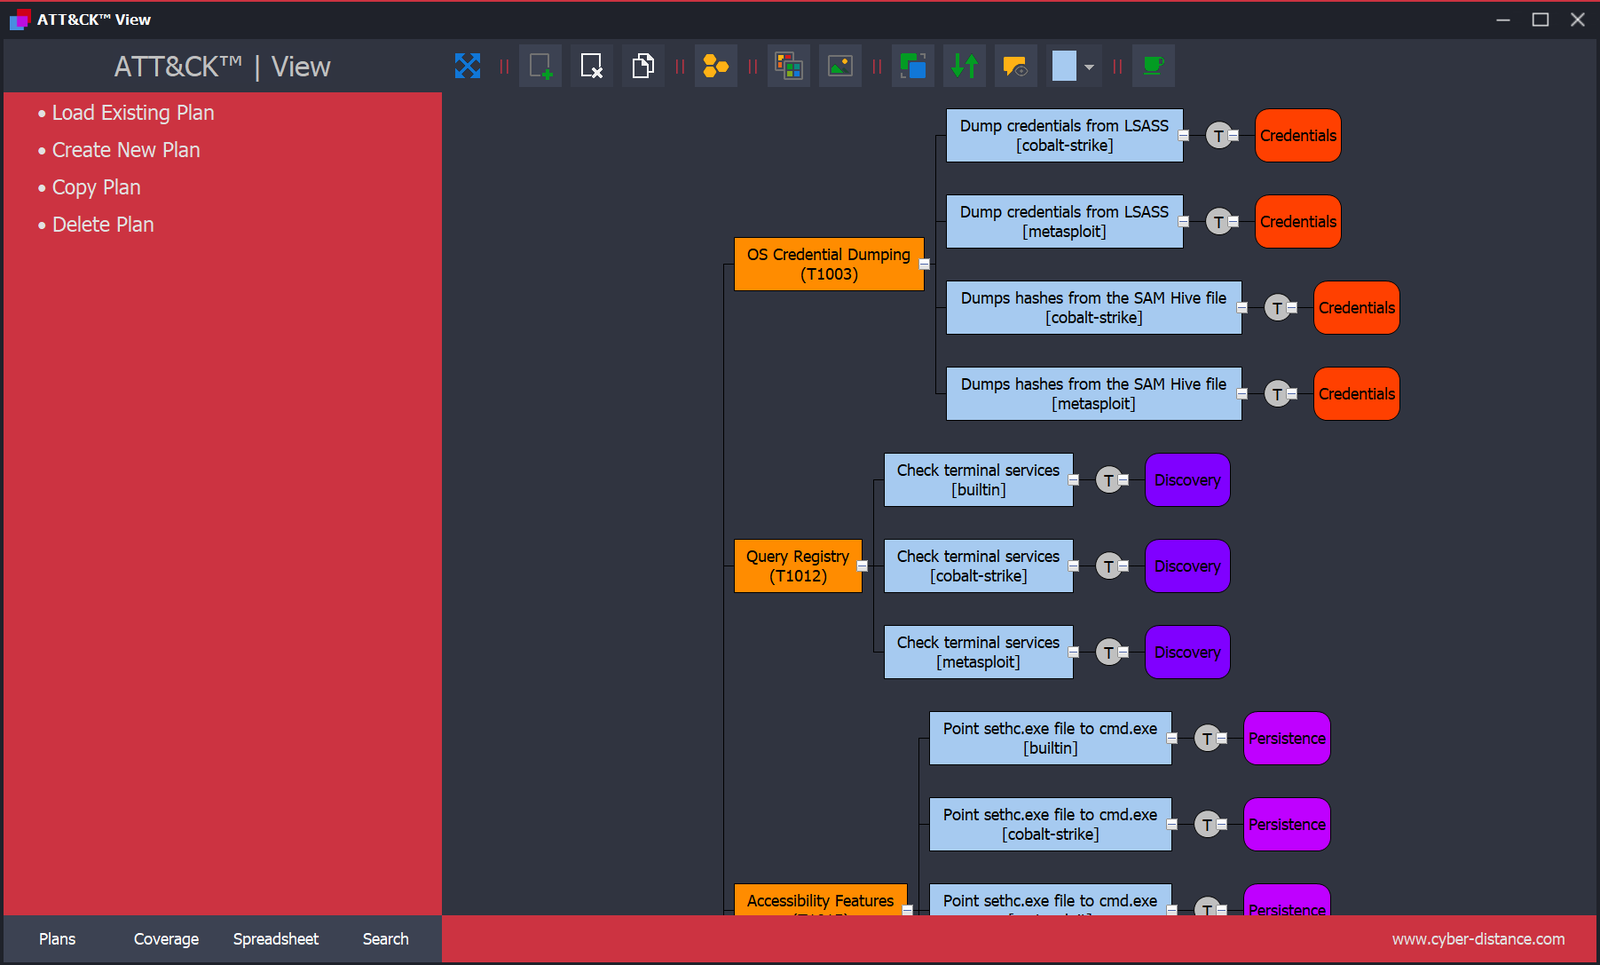
SQLite relational data model for MITRE ATT&CK plus an adversary emulation planning tool, enriched with Red Canary ATOMIC tests and APT3 emulation…

Curated collection of web and API vulnerability checklists covering XSS, SQLi, CSRF, IDOR, authentication bypass, file upload, and bug bounty testing…

Jekyll-based pentesting knowledge base with methodology guides, cheatsheets, tool indexes, certification roadmaps, and curated practice lab and CTF…

OWASP reference project for agentic AI security evidence: correlates agent execution, identity, tool calls, and authorization decisions into…

Monorepo of OWASP Bug Logging Tool projects: crowd-sourced vulnerability reporting, bug bounty workflows, CVE namespace, autopatching, and security…

OSINT identity investigation tool. Pivot from an e-mail, username, phone or wallet across 46 sources into one profile and relationship graph.

🔎 Username, email & phone OSINT — 9,700+ lookup checks from 19 projects, with profile enrichment, bulk searches, evidence graphs and expert-reviewed…

An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.

Curated SIEM queries and techniques for offensive discovery of Windows privilege escalation, misconfigured ACLs, services, scheduled tasks, and…

Sell bookable services and appointments through WooCommerce -- closes CVE-2026-2931 by construction.

Free security-baseline rule for Claude Code, Codex, and Cursor: treats MCP tool descriptions as untrusted input (OWASP MCP Top 10 MCP03,…

AI-driven OSINT and security research agent that builds a live knowledge graph from public data, with bundled recon tools and offensive-security…

CVE intelligence pipeline that compares public CVEs against Nuclei templates to identify missing vulnerability coverage, classify types, and rank…

Weak-RNG stream-sweep research (CVE-2026-71851 class): PRNG schemes x seeds -> BIP39 -> victim set membership

Documentation of CVE-2026-26418, a missing authentication and authorization vulnerability in TCS Cognix Recon Client v3.0 Web API, including affected…

Java安全相关的漏洞和技术demo,原生Java、Fastjson、Jackson、Hessian2、XML反序列化漏洞利用和Spring、Dubbo、Shiro、CAS、Tomcat、RMI、Nexus等框架\中间件\功能的exploits以及Java Security…

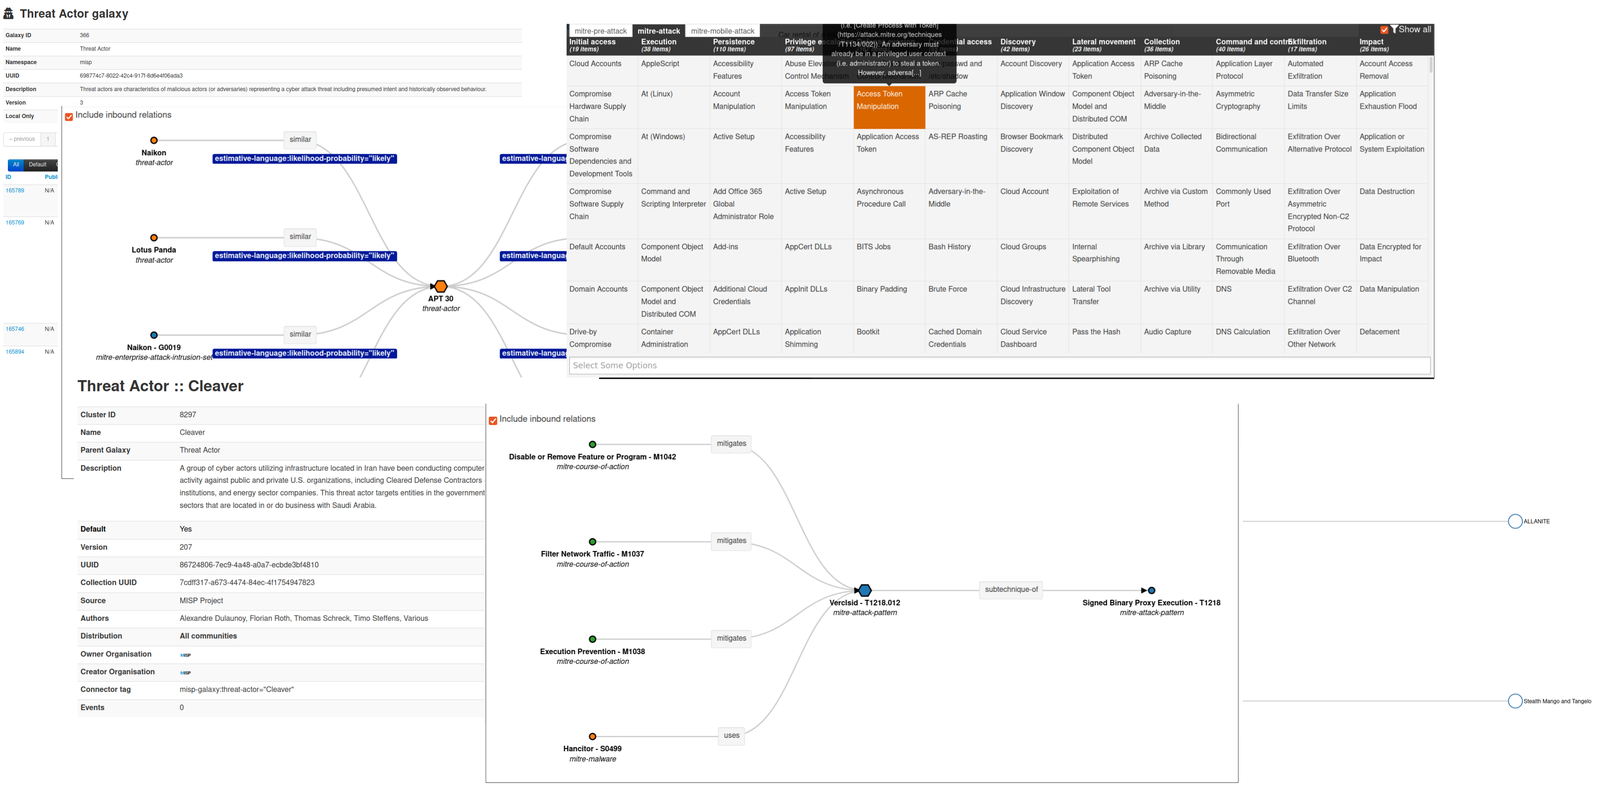
Clusters and elements to attach to MISP events or attributes (like threat actors)