
awesome-android-security
 saeidshirazi/awesome-android-security
A curated list of Android Security materials and resources For Pentesters and Bug Hunters
android-securitycurated-resourceseducation+6
2.0k
saeidshirazi/awesome-android-securityA curated list of Android Security materials and resources For Pentesters and Bug Hunters
 webbreacher/obsidian-osint-templates
These templates are suggestions of how the Obsidian notetaking tool can be used during an OSINT investigation. The example data in those files should…
 mindcrypt/covertchannels-steganography
A list of covert channels and steganography/steganalysis resources (books, papers & tools)
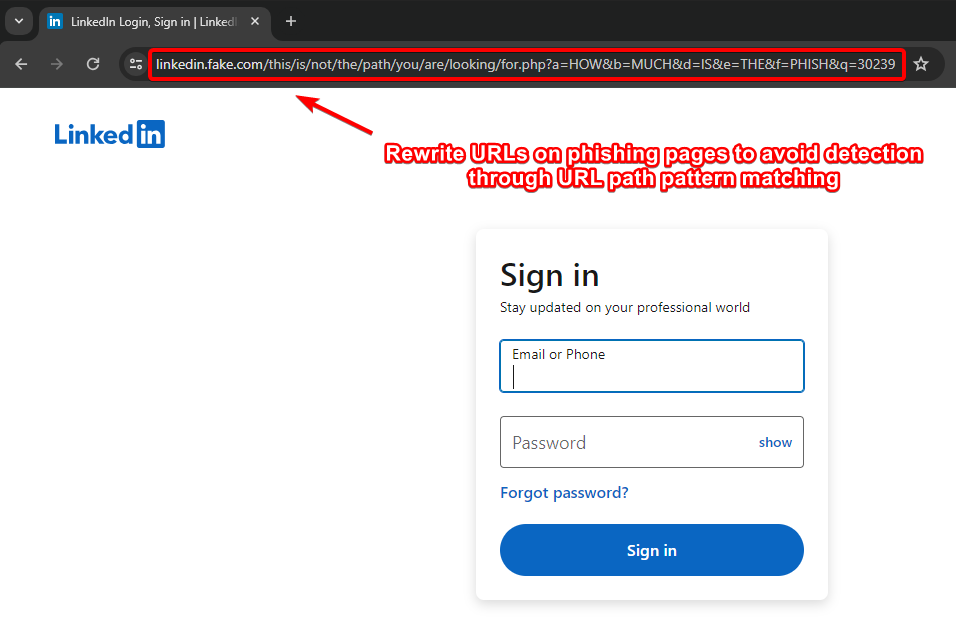 an0nud4y/evilginx-phishing-infra-setup
Evilginx Phishing Infrastructure Setup Guide - Securing Evilginx and Gophish Infrastructure, Removing IOCs, Phishing TTPs
 edoverflow/can-i-take-over-xyz
"Can I take over XYZ?" — a list of services and how to claim (sub)domains with dangling DNS records.
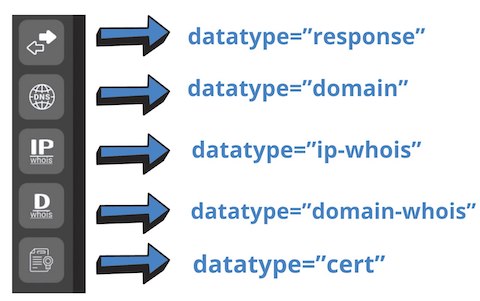 netlas-io/netlas-cookbook
The goal of this guide is very simple - to teach anyone interested in cyber security, regardless of their knowledge level, how to make the most of…
 demining/digital-signature-forgery-attack
How CVE-2025-29774 Vulnerabilities and the SIGHASH_SINGLE Bug Threaten Multi-Signature Wallet Operational Methods with Fake RawTX
 enovella/tee-reversing
A curated list of public TEE resources for learning how to reverse-engineer and achieve trusted code execution on ARM devices
 ansvar-systems/eu_compliance_mcp
EU focused compliance MCP server
 0x4d31/awesome-oscp
A curated list of awesome OSCP resources
 jigerjain/interview_tips
Summary of Cyber Security interview questions I have been through, hope this helps
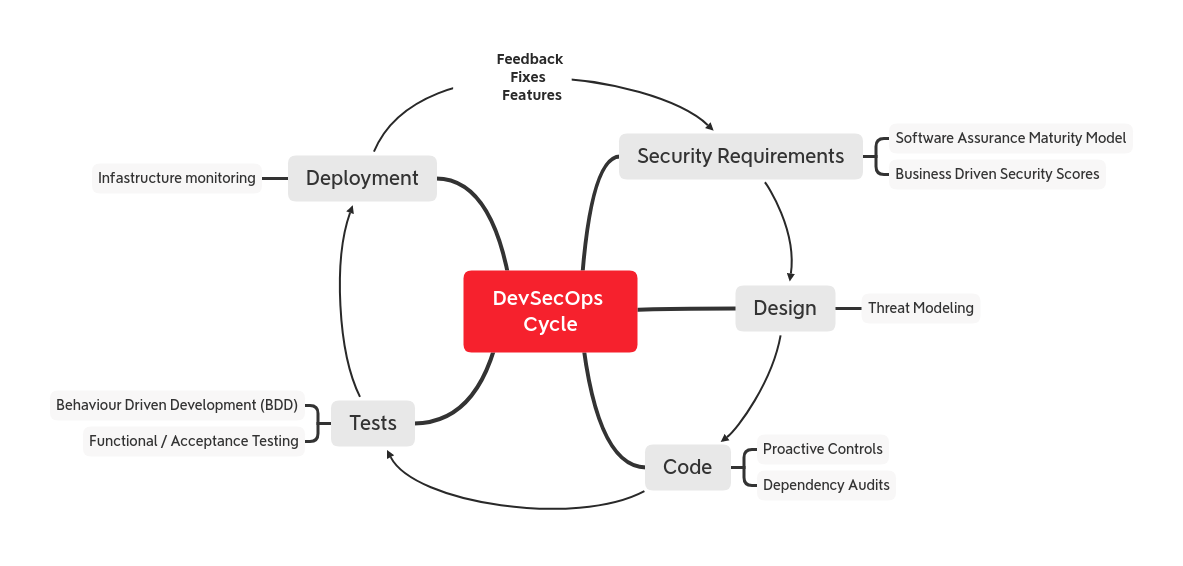 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 tjnull/tj-osint-notebook
This OSINT Notebook provides an overview of the tools, techniques, and resources that I use for a variety of situations when it comes to performing…
 rizemon/exploit-writing-for-oswe
Tips on how to write exploit scripts (faster!)
 fofainfo/awesome-fofa
The FOFA Library collects usage tips, common scenarios, F&Q, and more for FOFA.
 gmh5225/eac
Compiles EAC and EOC anti-cheat SDKs, reversing research, and code resources to study how game anti-cheat systems integrate and operate.
 dariusiakabos/log4j
Curated OSINT compilation on Log4Shell (CVE-2021-44228) covering detection methods, attack surface, mitigation steps, and indicators of compromise…
 hakluke/bug-bounty-standards
A list of edge cases that occur in bug bounty programs, conversations on how they should be handled. The goal is to standardise the way that specific…