

mutillidae
 webpwnized/mutillidae
OWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…
ctfeducationlabs-practice+3
1.5k
webpwnized/mutillidaeOWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…
 hackmelocal/cve-2025-31486-simulation
Containerized lab environment to simulate and exploit CVE-2025-31486, a path traversal vulnerability in Vite's development server, with step-by-step…
 het-kalariya/cve-2026-20253
Self-contained security training lab reproducing CVE-2026-20253 (Splunk Enterprise unauthenticated RCE). Provides a Docker-based environment to…
 goultarde/cve-2025-55182-react2shell-lab
CTF lab environment exploiting CVE-2025-55182 (RCE in React Server Components) with vulnerable Next.js blog, detection scripts, and manual exploit…
 takito1812/web-hacking-playground
Web application with vulnerabilities found in real cases, both in pentests and in Bug Bounty programs.
 androidteacher/cve-2025-64424-coolify-
Containerized CTF lab for learning and exploiting CVE-2025-64424, a command injection RCE in Coolify. Includes vulnerable environment, walkthrough,…

 mbrandner-group/juiceshopgl
Intentionally vulnerable web application for security training, CTF competitions, and testing security tools. Covers OWASP Top Ten vulnerabilities…
 owasp/securityshepherd
Web and mobile application security training platform
 syn-4ck/wvctf
WVCTF or WebVulnCTF is a gamified web platform which promotes training in pentesting and web application development security in an entertaining way.…
 juice-shop/juice-shop
Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…
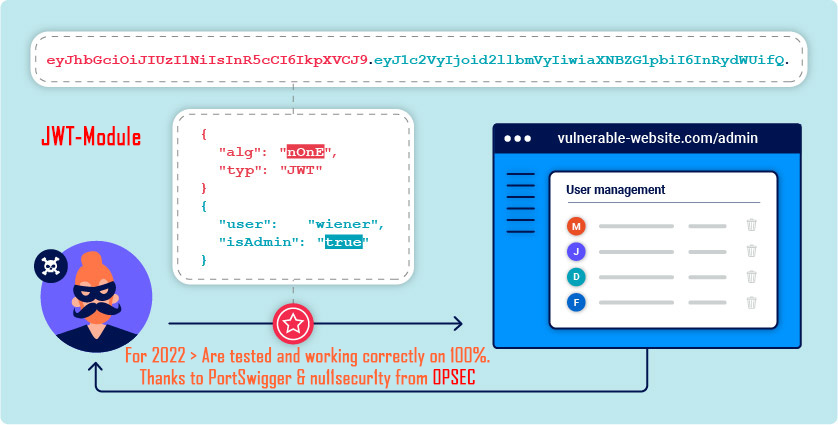 nu11secur1ty/portswigger-web-security-academy
Curated solutions and walkthroughs for PortSwigger Web Security Academy labs, covering web vulnerabilities, JWT attacks, and exploitation techniques…
 deepankarkumar1/cve-2025-55182_vulnerable-application
Intentionally vulnerable React Server Components lab for studying CVE-2025-55182. Provides a safe environment for security researchers, developers,…
 aperikube/compose-aperisite
Docker Compose wrapper to deploy AperiSite, a curated platform hosting CTF writeups, security challenges, and educational resources covering web,…
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 koadt/oss-oopssec-store
Security training for the apps you actually ship. Open your browser and start hacking.
 cliffe/breakescape
Mountable Rails engine providing 24+ cybersecurity escape room scenarios with randomized passwords, JIT-compiled NPC dialogue, and RESTful API for…
 infosecantara/cve-2025-14765-and-cve-2025-14766
Interactive browser-based lab simulating Chrome memory corruption vulnerabilities (CVE-2025-14765/14766) for safe security training, featuring…
 flojboj/cve-2024-32002
Educational exploit script for CVE-2024-32002 (Git RCE) with automated setup, designed for CTF environments and security training.