

Pegasus-Pentest-Arsenal
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
api-security-testingctfeducation+9
57
sobri3195/pegasus-pentest-arsenalA comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
 dontpanico/jwtxploiter
Automated JWT security testing tool that exploits known CVEs, tampers with payloads, performs JKU/X5U injection, key confusion attacks, and verifies…
 ticarpi/jwt_tool
:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
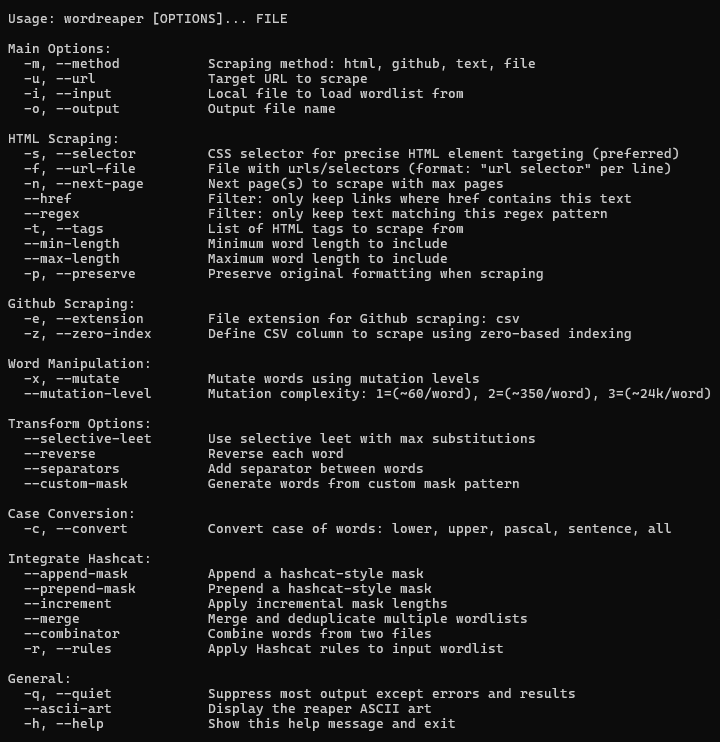 nemorous/wordreaper
📜 Scrape targeted wordlists for password cracking using CSS selectors
 ez4rd1x1/cve-2026-8181
Proof-of-concept exploit for CVE-2026-8181, an authentication bypass in the Burst Statistics WordPress plugin. Demonstrates remote, unauthenticated…
 franklincg/secdim-assurance-drift-challenge
SecDim Challenge Builder repro inspired by CVE-2026-88861: AAL1 MFA bypass at privileged credential boundary
 bishopfox/otto-support
An implementation of a vulnerable MCP server using mcp-go
 ixzodiak/cve-2025-8110
Gogs service Exploit and get the root user
 hassan-hamadi/cve-2025-8110-silentium-htb
CVE-2025-8110 Specifically for the Silentium box on HTB.
 paradoxis/flask-unsign
Command line tool to fetch, decode, brute-force and craft session cookies of a Flask application by guessing secret keys.
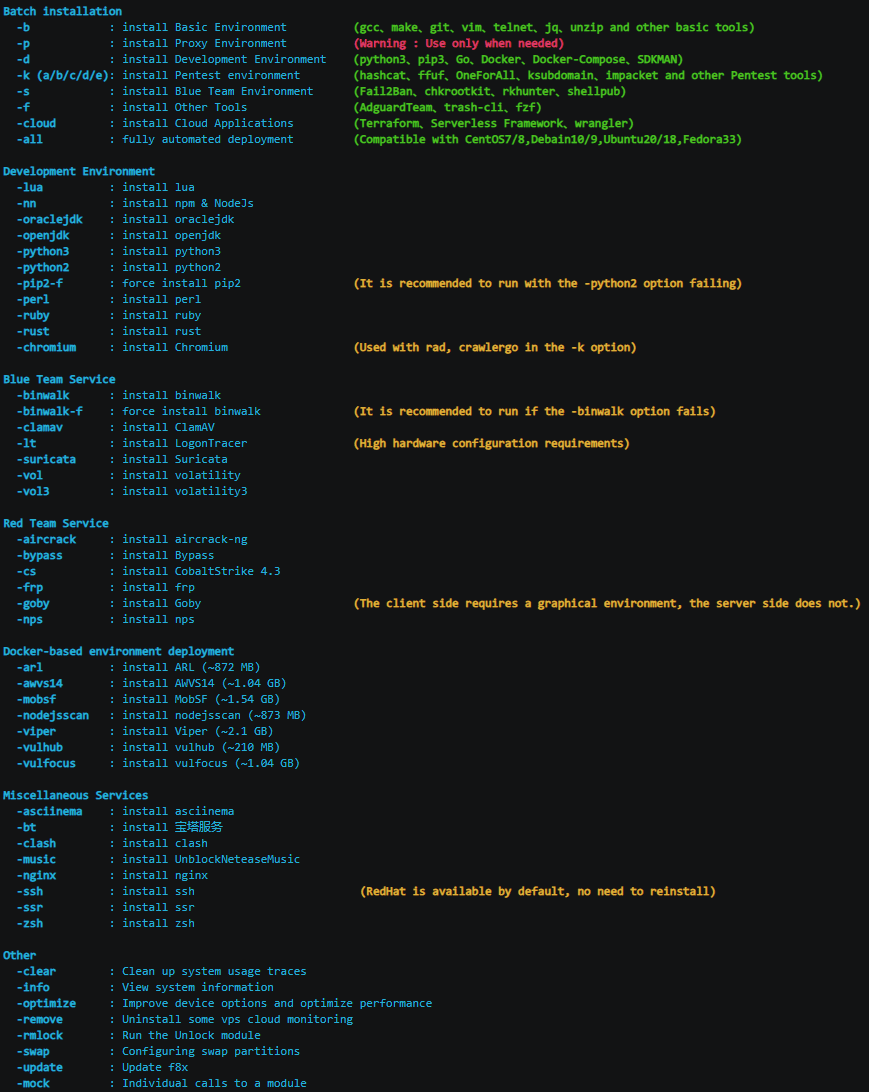 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool