
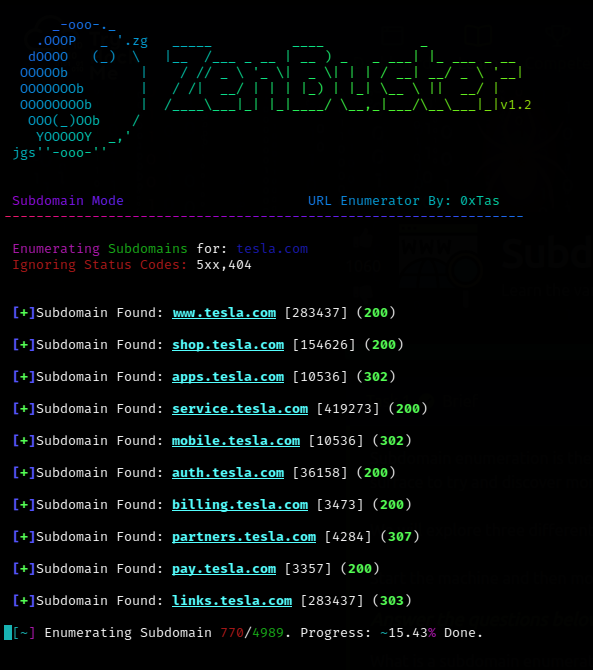
zenbuster
 0xtas/zenbuster
Multi-threaded URL enumeration/content-discovery tool in Python.
ctfinformation-gatheringpenetration-testing+2
0xtas/zenbusterMulti-threaded URL enumeration/content-discovery tool in Python.
 moxitpanchal/evershop-lab-cve-2026-25993
Docker-based lab for exploiting CVE-2026-25993, a second-order SQL injection in EverShop. Deploy, enumerate, and dump the database via crafted…
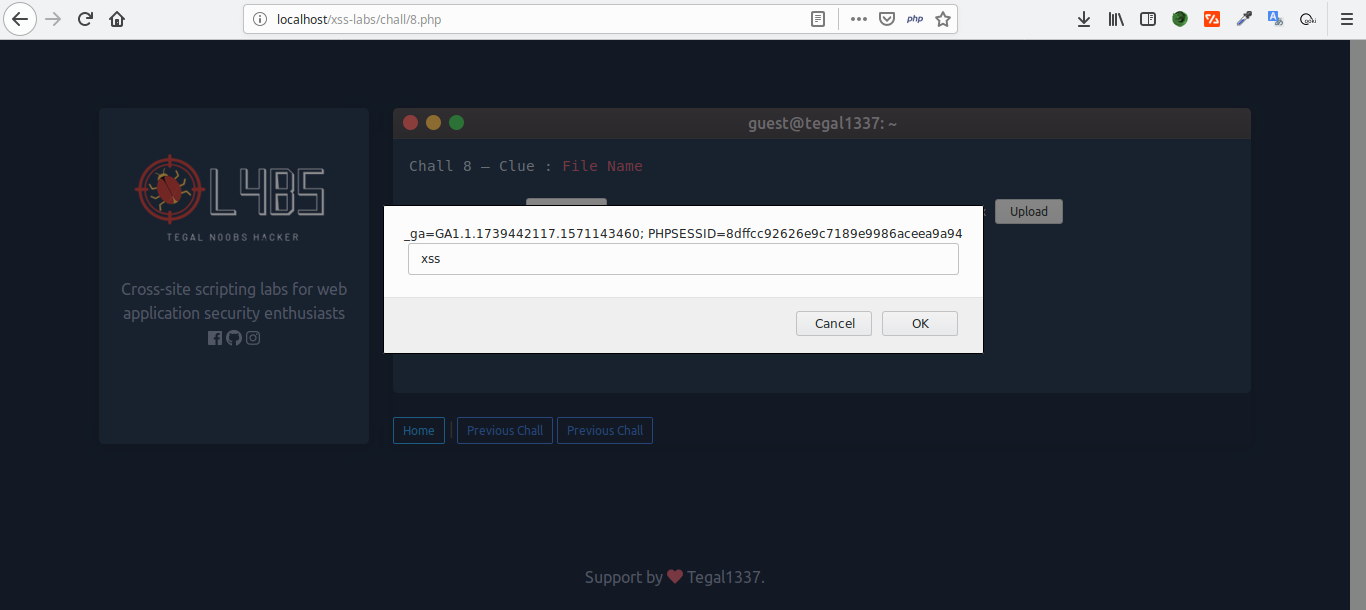 tegal1337/0l4bs
Cross-site scripting labs for web application security enthusiasts
 jithinodattu/cve-2023-24329-lab
Self-contained Docker lab demonstrating CVE-2023-24329, a Python urllib parser differential that bypasses URL scheme and host filters, with…
 owasp/igoat-swift
OWASP iGoat (Swift) - A Damn Vulnerable Swift Application for iOS
 1h3ll/cve-2025-50365_csrf_delete_category-phpgurukul-cve
PoC for CVE-2025-50365: a CSRF flaw in PHPGurukul Maid Hiring Management System allowing deletion of hiring categories via a crafted admin request.
 seanpesce/cve-2024-22243
Example exploitable scenarios for CVE-2024-22243 affecting the Spring framework (open redirect & SSRF).

 speatx/chamilolms-cve-2023-4220
CVE-2023-4220 — Unauthenticated file upload RCE in Chamilo LMS ≤ 1.11.24. OSCP-style and auto exploit.
 flame-11/cve-2016-15041-mainwp-dashboard
Vuln lab: MainWP Dashboard <= 3.1.2 Unauthenticated Stored XSS