
PoC-CVE-2024-44349
 andreaf17/poc-cve-2024-44349
Proof-of-concept exploit for CVE-2024-44349, an SQL injection in Anteeo WMS v4.7.x, enabling database dumping and arbitrary SQL query execution.
ctfdatabase-securityeducation+4
1
andreaf17/poc-cve-2024-44349Proof-of-concept exploit for CVE-2024-44349, an SQL injection in Anteeo WMS v4.7.x, enabling database dumping and arbitrary SQL query execution.
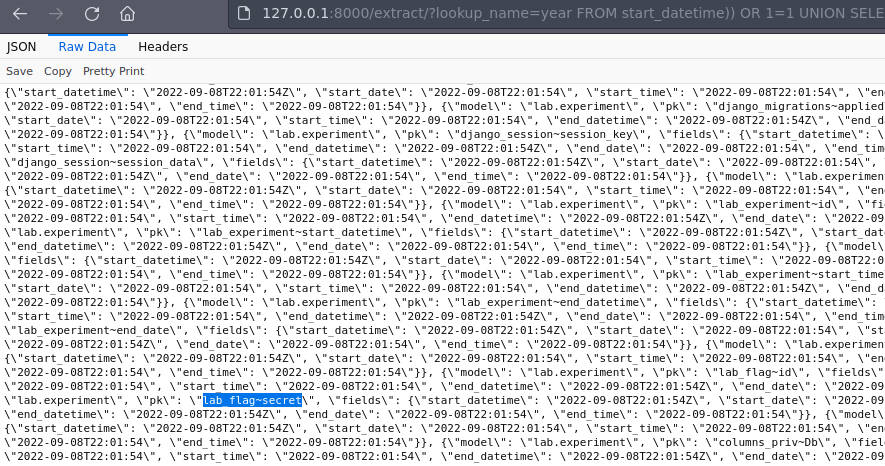 lnwza0x0a/ctf_django_cve-2022-34265
Docker-based CTF challenge demonstrating SQL injection in Django's Trunc() and Extract() database functions (CVE-2022-34265) with UNION-based payload…
 tempuss/ctf_cve-2020-7471
CTF challenge exploiting CVE-2020-7471, a Django SQL injection vulnerability in PostgreSQL StringAgg, with Docker setup and exploit scripts.
 warxim/vucsa
Deliberately vulnerable client-server application for learning penetration testing of non-HTTP thick clients. Includes challenges for SQL injection,…
 hackerking24/cve-2026-29782-openstamanager-rce
Proof-of-concept exploit for CVE-2026-29782, chaining SQL injection and PHP object injection to achieve remote code execution in OpenSTAManager.…
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
 ayham-megdadi/zero-day-legacy
A vulnerable Boot-to-Root CTF lab machine simulating a hospital environment. Features a realistic 17-step attack chain including SQL Injection, XSS,…
 giangdurian/cve-2026-63030-cve-2026-60137
Pre-auth RCE exploit for WordPress (CVE-2026-63030 + CVE-2026-60137) chaining route confusion and SQL injection into full shell access. Includes…
 joaovicdev/exploit-cve-2026-63030
Docker-based vulnerable WordPress lab with Python exploit demonstrating pre-auth route confusion and SQL injection chain (CVE-2026-63030 +…
 baptistecontreras/cve-2017-8917-joomla
CVE-2017-8917 SQL injection Vulnerability in Joomla! 3.7.0 exploit
 moxitpanchal/evershop-lab-cve-2026-25993
Docker-based lab for exploiting CVE-2026-25993, a second-order SQL injection in EverShop. Deploy, enumerate, and dump the database via crafted…
 drackyjr/cve-2025-8018
Python PoC exploit for CVE-2025-8018, a critical unauthenticated SQL injection in Food Ordering Review System v1.0. Supports time-based blind and…
 ztrxwzy/joomla.3.7.0exploit
Proof of Concept exploit for the Joomla 3.7.0 com_fields SQL injection vulnerability (CVE-2017-8917), demonstrating detection, enumeration, and data…
 dinosn/cve-2026-6379
Docker-based lab kit for CVE-2026-6379, an unauthenticated SQL injection in WP Photo Album Plus. Includes time-based blind PoC, root-cause analysis,…
 sup3rdav3/cve-2025-4396
CVE-2025-4396 - WordPress Relevanssi Time-Based Blind SQL Injection
 rgkue/mysqli
Time-Based Blind SQL Injection tool for MySQL - CVE-2019-9053
 ydking0911/cve-2026-4060-poc
Proof-of-concept for CVE-2026-4060: unauthenticated time-based blind SQL injection in Geo Mashup WordPress plugin via ORDER BY clause. Includes…
 haerin-l/poc_cve-2026-42208
Reproduction lab for CVE-2026-42208, a critical pre-authentication SQL injection in LiteLLM. Includes Docker-based vulnerable/patched environments,…