
-CVE-2025-59528-PoC
 maradonam18/-cve-2025-59528-poc
A simple python script to exploit CVE-2025-59528, this an Authenticated RCE vulnerability in Flowise application, a popular AI tool. That is also…
ctfeducationexploitation+3
1
maradonam18/-cve-2025-59528-pocA simple python script to exploit CVE-2025-59528, this an Authenticated RCE vulnerability in Flowise application, a popular AI tool. That is also…
 prapul1/vulnhub-dc1-writeup
VulnHub DC-1 boot-to-root — exploiting CVE-2018-7600 (Drupalgeddon2) for RCE, extracting DB credentials from settings.php, forging admin password…
 pallangyo98/trickster-htb
This report details exploiting Trickster via an XSS in PrestaShop (CVE-2024-34716) to gain www-data access, extracting database credentials for SSH…
 wytchwulf/cve-2015-1397-magento-shoplift
Exploit scripts for CVE-2015-1397 in Magento CMS, including a pre-auth exploit to gain admin credentials and a post-auth RCE module for reverse shell…
 americooo/pentest-writeups
Kioptrix Level 1 writeup - CVE-2003-0201 Samba trans2open
 niteeshpujari/cve-2025-32433-poc
Proof-of-concept exploit for CVE-2025-32433, enabling unauthenticated remote code execution in Erlang/OTP SSH. Includes Docker setup and reverse…
 karimelsheikh1/htb-facts-writeup
HackTheBox Facts machine writeup — CVE-2025-2304, MinIO S3 enumeration, SSH key cracking, and facter privilege escalation.
 rippsec/cve-2025-24893-xwiki-ssti-rce
CVE-2025-24893 – XWiki SSTI unauthenticated RCE exploit (HackTheBox CTF)
 rippsec/cve-2025-27591-meta-below-lpe
CVE-2025-27591 – Meta below symlink following local privilege escalation (HackTheBox CTF)
 rippsec/cve-2025-49113-roundcube-rce
CVE-2025-49113 – Roundcube ≤1.6.10 post-auth RCE via PHP object deserialization (HackTheBox CTF)
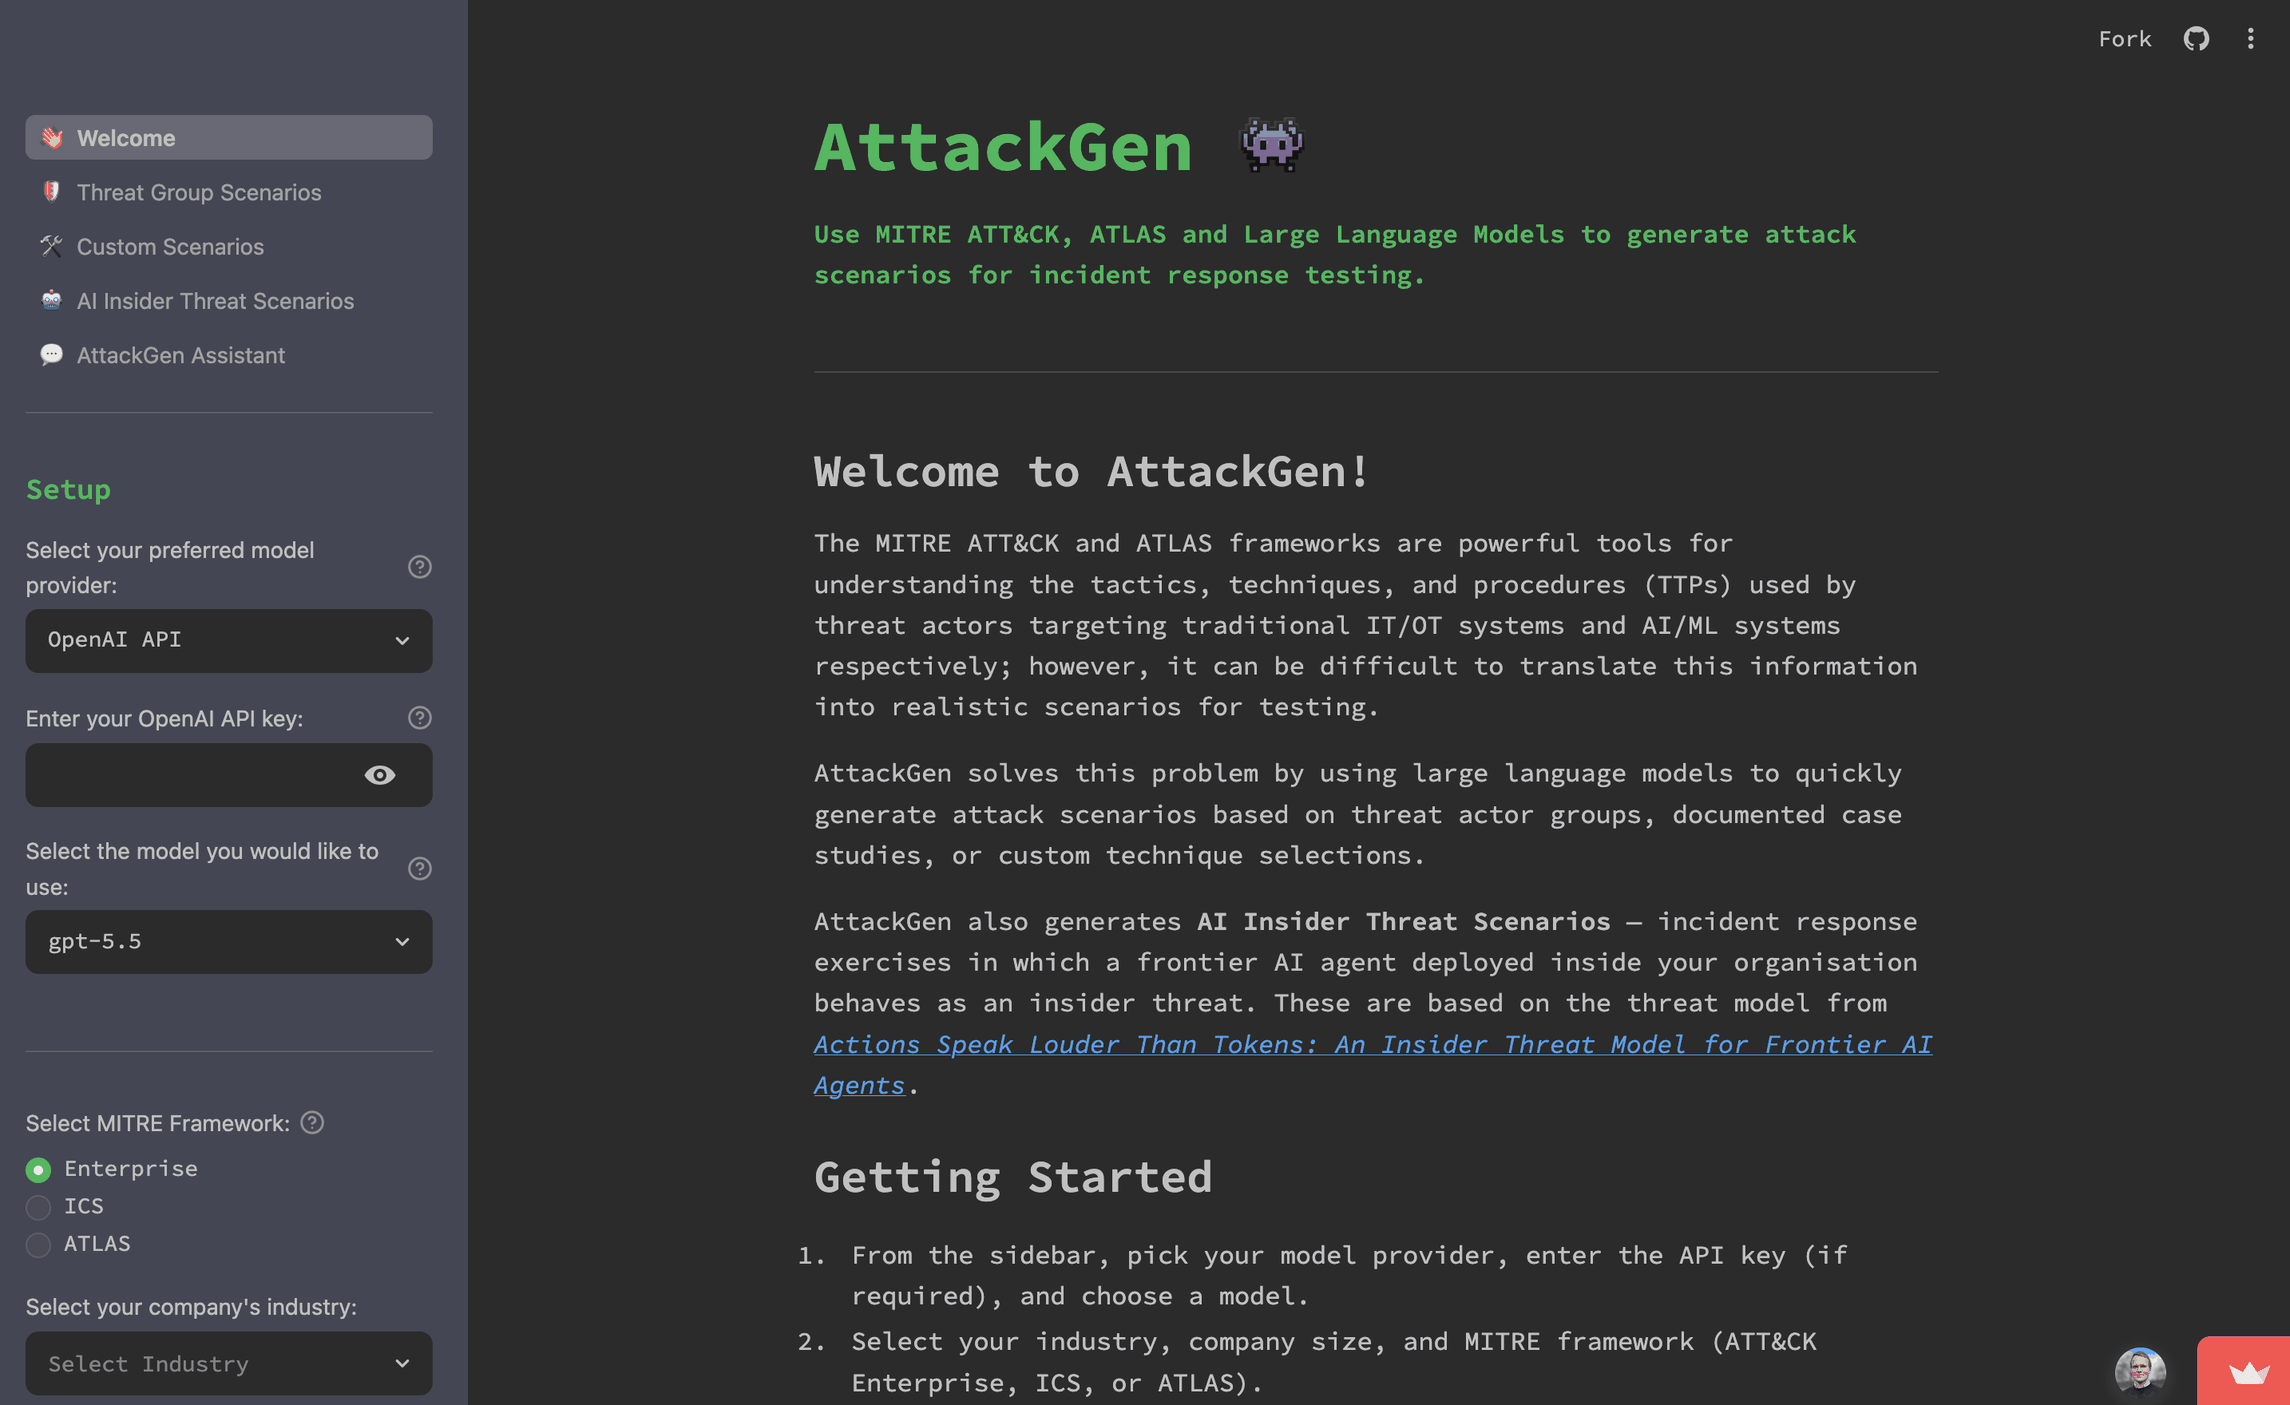 mrwadams/attackgen
AttackGen is a cybersecurity incident response testing tool that leverages the power of large language models and the comprehensive MITRE ATT&CK…
 bishopfox/cloudfoxable
Create your own vulnerable by design AWS penetration testing playground

 thepwnrip/lehack-analysis-of-cve-2018-8453
Conference talk analyzing CVE-2018-8453, a Windows kernel UAF and double-free vulnerability. Covers binary diffing, exploit reproduction, heap spray,…
 xmyronn/cve-2026-11518-xss
Proof-of-concept for unauthenticated stored XSS in SourceCodester Inventory System, demonstrating admin session hijacking via crafted registration…
 j3r1ch0123/cve-2025-32462
Exploit for CVE-2025-32462 enabling privilege escalation by bypassing sudo host restrictions on Linux systems with affected sudo versions and…
 haerin-l/poc_cve-2026-46716
Reproducible lab environment for CVE-2026-46716, a critical cross-tenant RCE in Nezha Monitoring via cron API authorization bypass. Includes Nuclei…
 karimelsheikh1/htb-twomillion-writeup
HackTheBox TwoMillion machine writeup — API abuse, command injection & CVE-2023-0386