

linux-smart-enumeration
 diego-treitos/linux-smart-enumeration
Linux enumeration tool for pentesting and CTFs with verbosity levels
ctfinformation-gatheringpenetration-testing+2
4.0k
diego-treitos/linux-smart-enumerationLinux enumeration tool for pentesting and CTFs with verbosity levels
 acceis/crypto_identifier
Crypto tool for pentest and ctf : try to uncipher data using multiple algorithms and block chaining modes. Usefull for a quick check on unknown…
 ethicalpap/cve-2025-29775
Educational lab environment demonstrating SAMLStorm (CVE-2025-29775) vulnerability in xml-crypto library. Includes vulnerable SAML service provider,…
 carlosaruy/cve-2025-55182
a critical Remote Code Execution (RCE) vulnerability in React Server Components (RSC). It also includes a realistic "Lab Environment" to safely test…
 lkimuk/reark
An intelligent reverse engineering and AI-assisted analysis tool for HarmonyOS NEXT (HAP/APP/ABC), Android (APK/AAB), iOS (IPA), and native…
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 atithkhawas/autoblue
AutoBlue - Automated EternalBlue (CVE-2017-0144 / MS17-010) exploitation tool leveraging Nmap and Metasploit for ethical hacking, penetration…
 vutiendat323/int14107_cve-2021-35042
Django-based CTF blog platform with integrated CVE-2021-35042 exploit tool for learning web application security and vulnerability exploitation.
 dontpanico/jwtxploiter
Automated JWT security testing tool that exploits known CVEs, tampers with payloads, performs JKU/X5U injection, key confusion attacks, and verifies…

 io12/pwninit
Automates setup of binary exploitation challenges by patching ELF binaries, fetching matching linkers, unstripping libc, and generating pwntools…
 ixzodiak/cve-2025-8110
Gogs service Exploit and get the root user
 noraj/ctf-party
:triangular_flag_on_post: A CLI tool & library to enhance and speed up script/exploit writing with string conversion/manipulation.
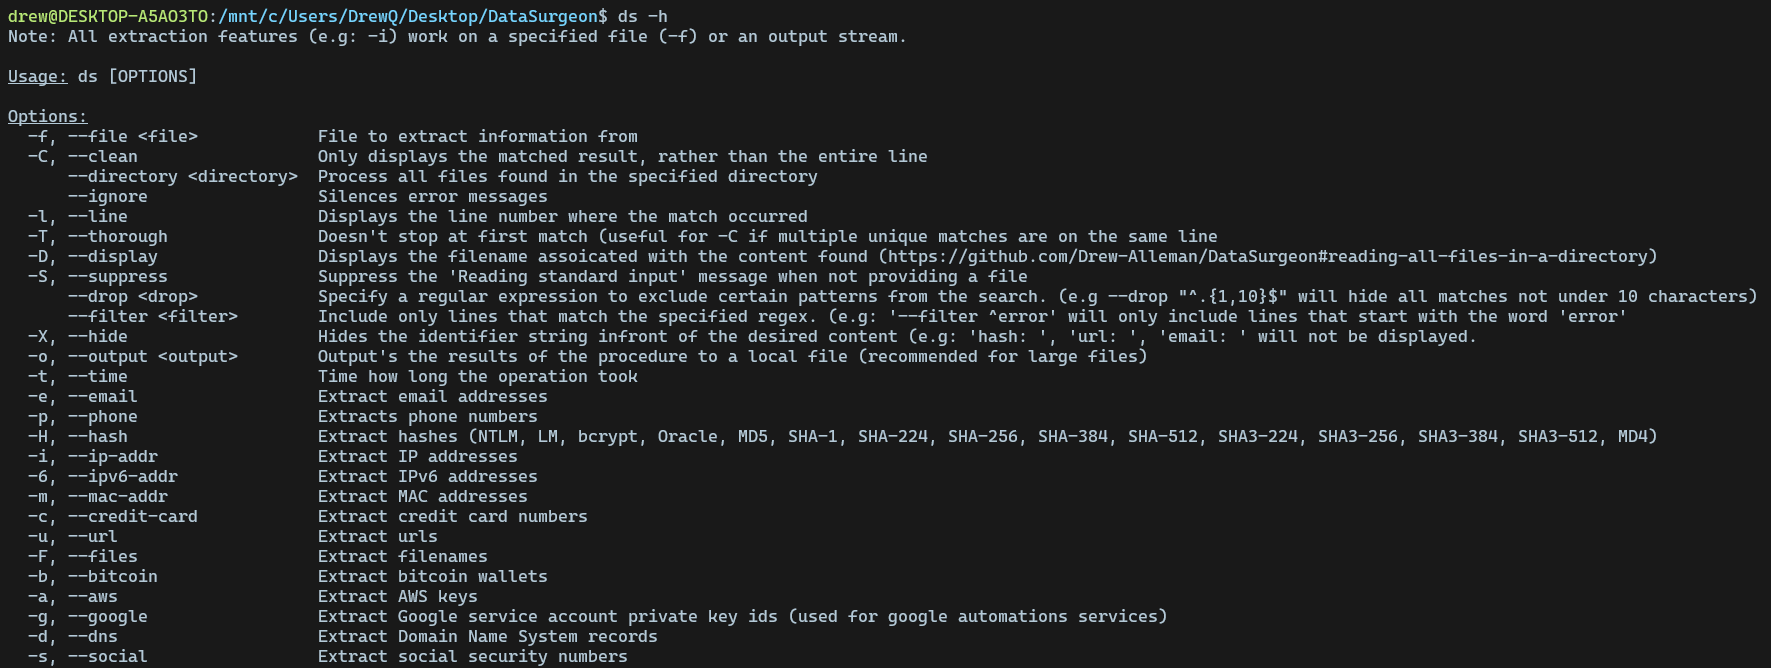 drew-alleman/datasurgeon
Quickly Extracts IP's, Email Addresses, Hashes, Files, Credit Cards, Social Security Numbers and a lot More From Text
 webpwnized/mutillidae
OWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…
 ticarpi/jwt_tool
:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
 tenable/cnappgoat
CNAPPgoat is an open source project designed to modularly provision vulnerable-by-design components in cloud environments.
 autorecon/autorecon
Multi-threaded network reconnaissance tool that automates service enumeration, port scanning, and information gathering for penetration testing and…