

PcapXray
 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
ctfdns-analysiseducation+7
1.9k5 months ago
srixivas/pcapxray❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
 t3l3machus/pentest-pivoting
A compact guide to network pivoting for penetration testings / CTF challenges.
 farhanashrafdev/90daysofcybersecurity
Structured 90-day cybersecurity study plan with daily tasks covering Network+, Security+, Linux, Python, traffic analysis, cloud security, and…
 bikini/exploitarium
Curated archive of public proof-of-concept exploits and vulnerability research writeups covering web, binary, and network security, with a focus on…
 autorecon/autorecon
Multi-threaded network reconnaissance tool that automates service enumeration, port scanning, and information gathering for penetration testing and…
 rawfilejson/awesome-osint-arsenal
OSINT & recon toolkit // 100+ tools, one-command installer, SOCMINT, GEOINT, network recon, dark web, forensics & more.
 m14r41/pentestingeverything
Complete Solution for VAPT/AppSec and Pentesting Guide: Web | Mobile | API | Thick Client | Source Code Review | DevSecOps | Wireless | Network…
 dedsec1121fk/dedsec
Educational Android (Termux) toolkit for learning penetration testing, OSINT, social engineering, and network security through hands-on scripts,…
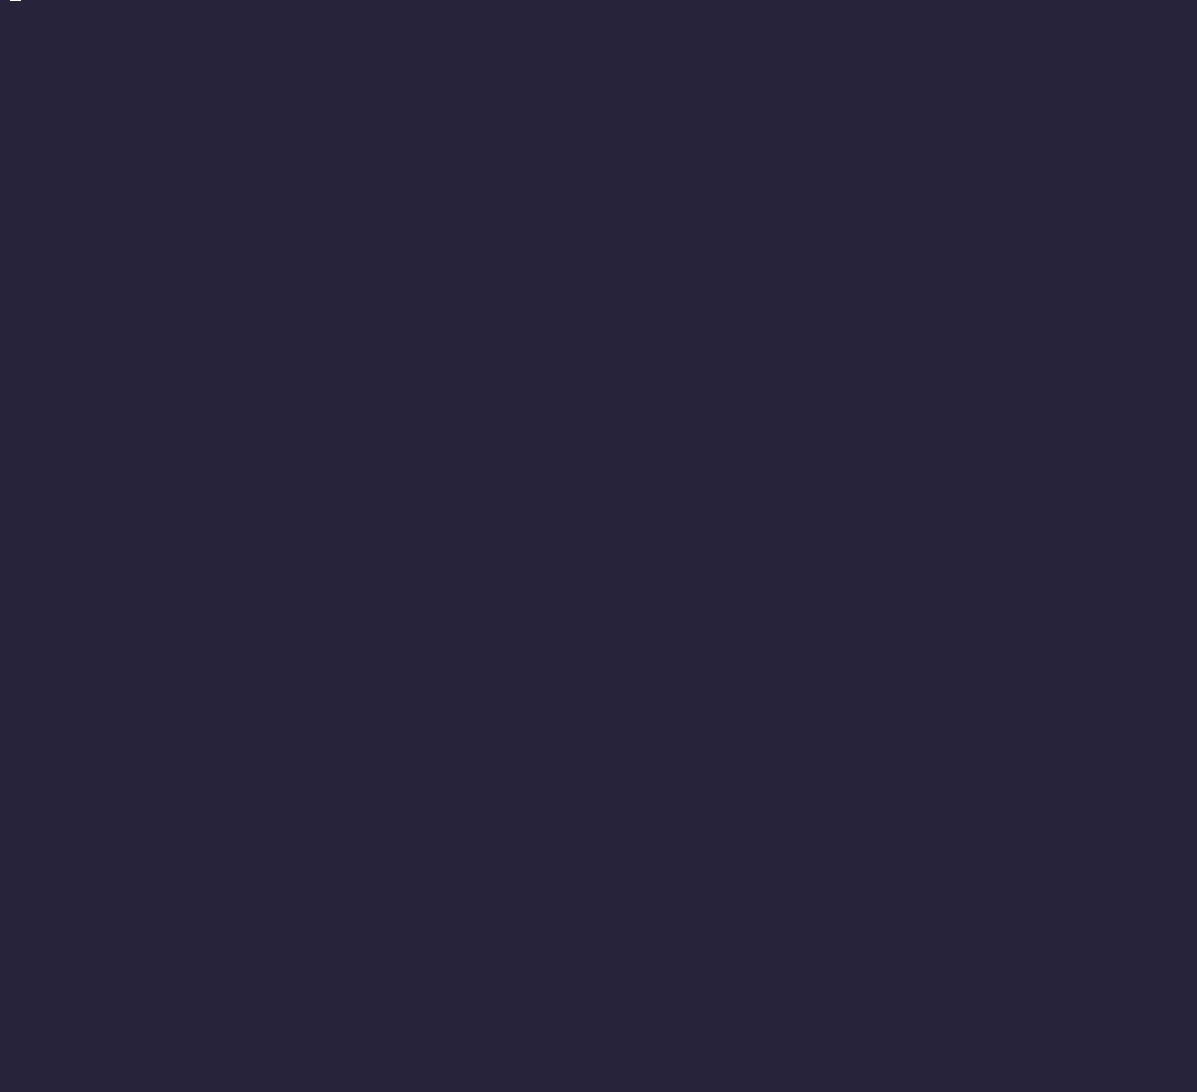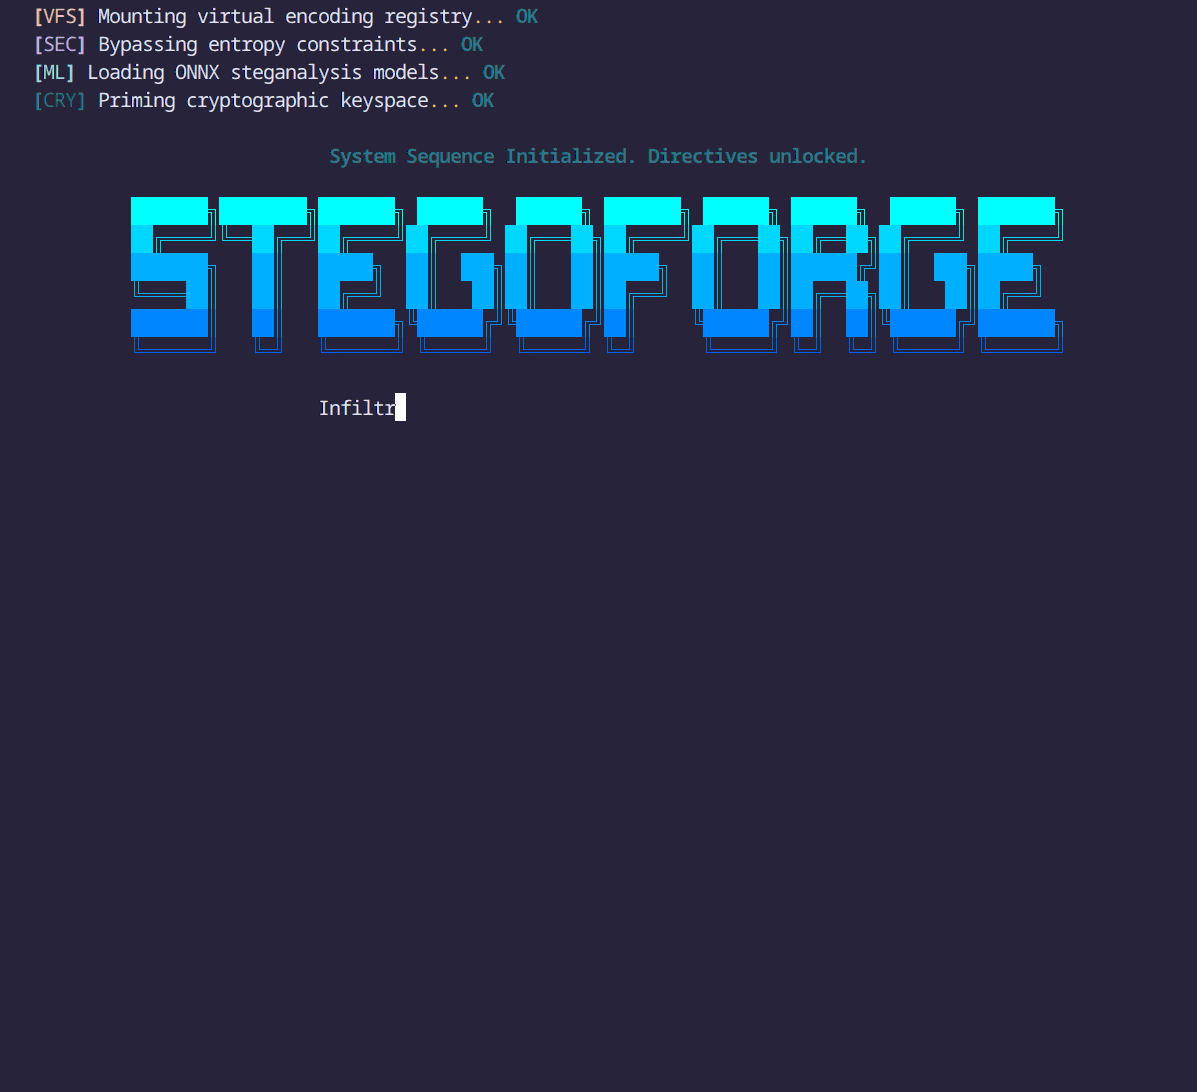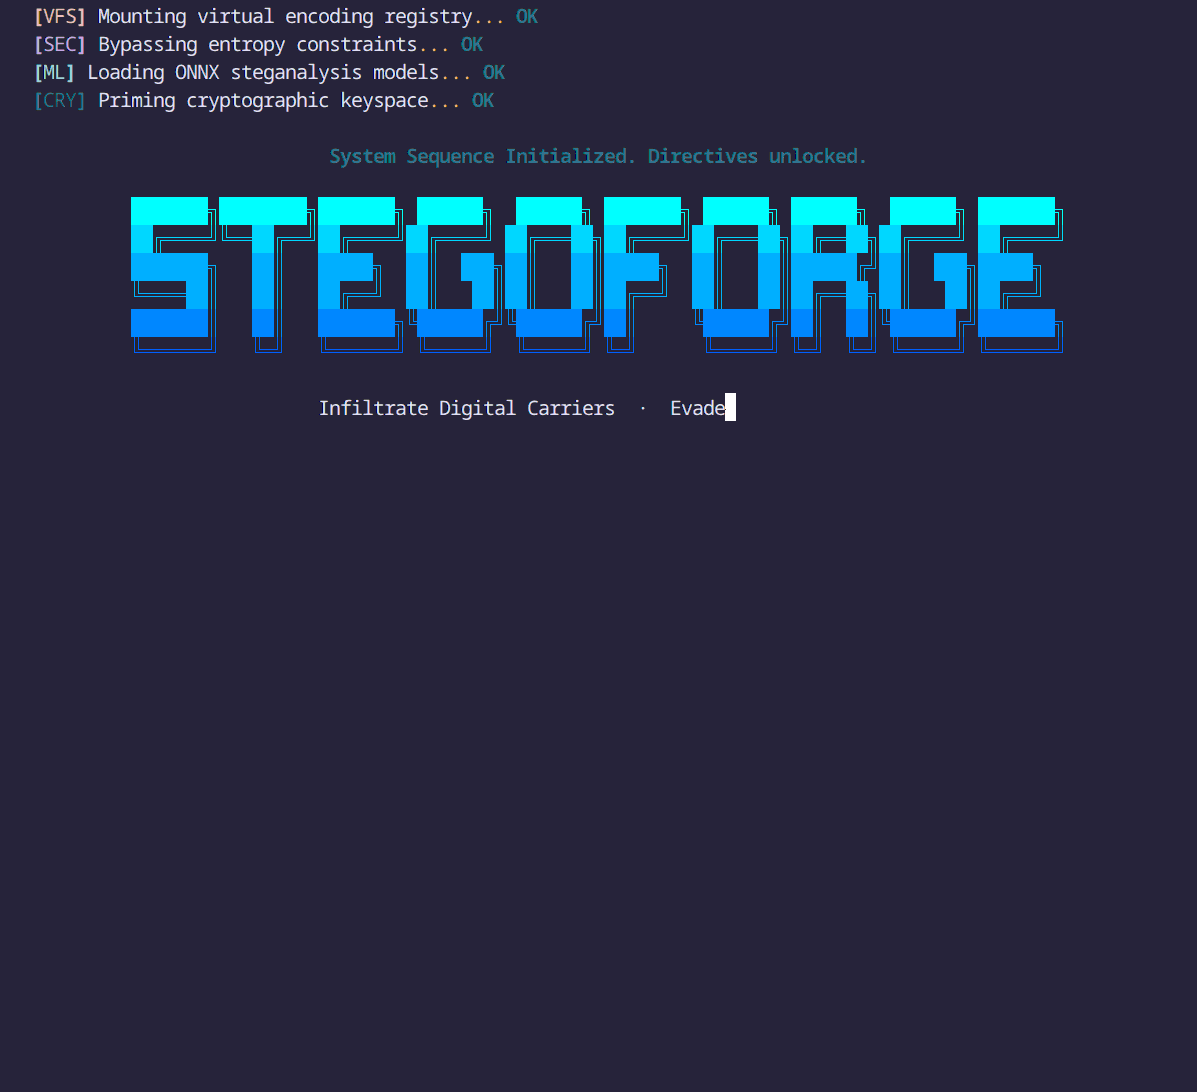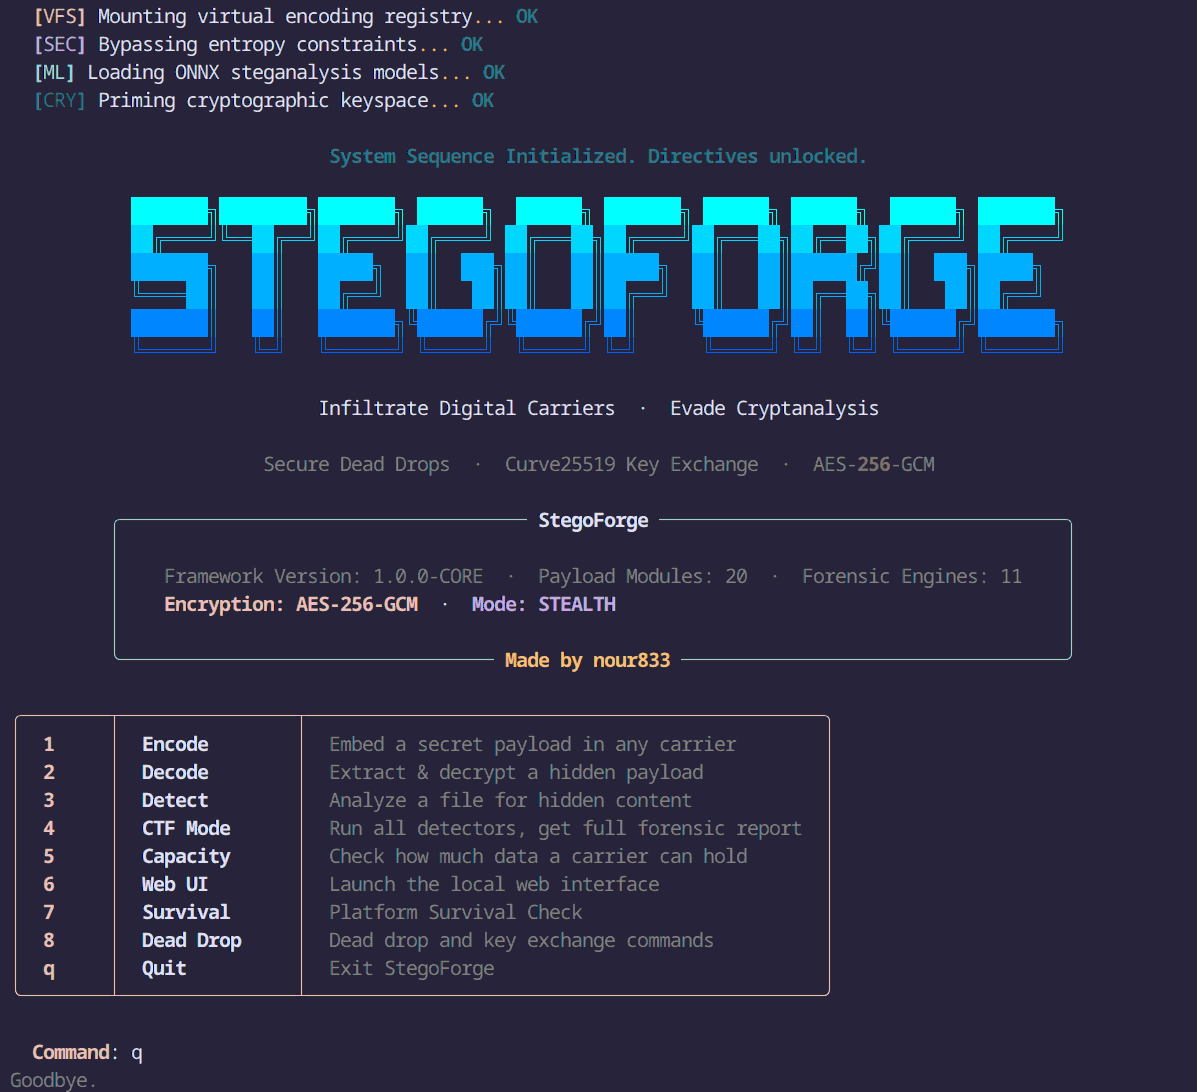 nour833/stegoforge
The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…
 eciavatta/caronte
A tool to analyze the network flow during attack/defence Capture the Flag competitions
 infobyte/spoilerwall
Spoilerwall introduces a brand new concept in the field of network hardening. Avoid being scanned by spoiling movies on all your ports!
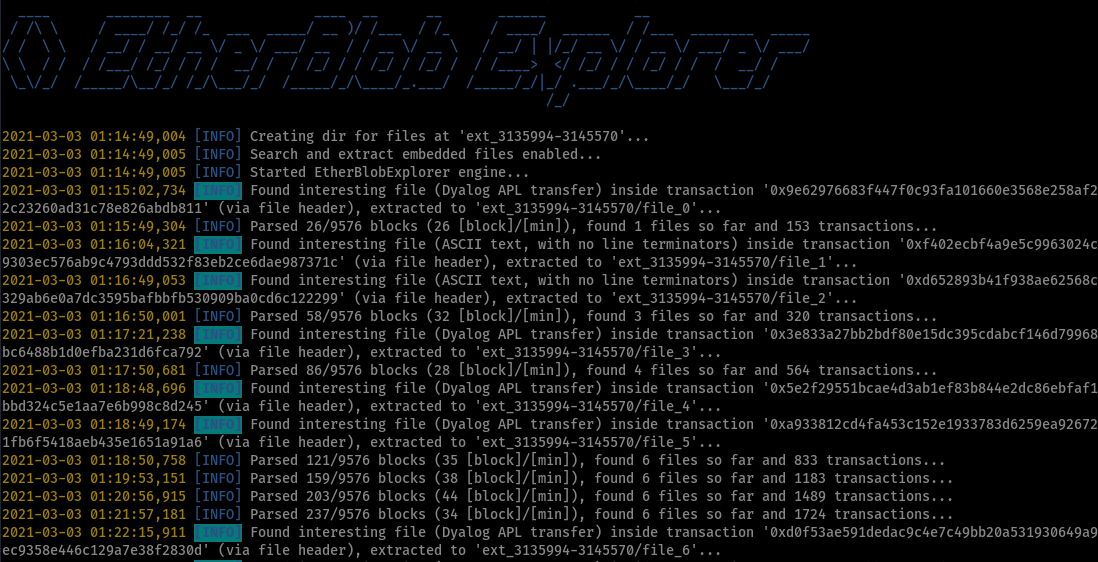 litneet64/etherblob-explorer
Search and extract blob files on the Ethereum Blockchain network
 alzeaty1/security-writeups
CTF writeups and teaching scripts for web security, bug bounty techniques, and network forensics, with blank-value versions for active practice.
 cves-labs/cve-2026-21877
Dockerized vulnerable lab environment with a Python-based network monitor and dedicated exploit script, enabling hands-on exploitation, privilege…
 pugazhendii22/keepass-exfil-forensics
Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…
 trerb/markdown-exfil-tester
Black-box test whether an LLM chatbot is vulnerable to markdown/HTML exfil (CVE-2025-32711 class). Spins up a sink, sends payloads, renders in…
 pixelotes/lab-cve-2023-4863
Docker-based lab to reproduce CVE-2023-4863 (heap buffer overflow in libwebp) with automated crash demonstration, patched vs vulnerable comparison,…
 paulameg/simplectf-thm-walkthrough
First CTF successfully completed! This repo documents my walkthrough of TryHackMe's Simple CTF. It covers network reconnaissance (Nmap), web…