

ictf-framework
 shellphish/ictf-framework
Open-source framework for hosting Attack/Defense CTF competitions with automated gamebot, script execution, VPN routing, and cloud-based…
cloud-securityctfeducation+1
331
shellphish/ictf-frameworkOpen-source framework for hosting Attack/Defense CTF competitions with automated gamebot, script execution, VPN routing, and cloud-based…
 gen0cide/laforge
Competition Infrastructure Management
 cliffe/breakescape
Mountable Rails engine providing 24+ cybersecurity escape room scenarios with randomized passwords, JIT-compiled NPC dialogue, and RESTful API for…
 9xeb/context-segmentation
Multi-agent automated context management for long horizon tasks in local AI Agents
 1h3ll/cve-2025-50365_csrf_delete_category-phpgurukul-cve
PoC for CVE-2025-50365: a CSRF flaw in PHPGurukul Maid Hiring Management System allowing deletion of hiring categories via a crafted admin request.
 owasp/igoat-swift
OWASP iGoat (Swift) - A Damn Vulnerable Swift Application for iOS
 cmpnn-romain/cve-2024-27198_lab
Lab for the CVE-2024-27198
 trivulzianus/tarantubench
The full repo of all the labs available as part of the benchmark
 vanhari/cve-2026-39987
Proof-of-concept exploit for an authentication bypass in marimo's terminal WebSocket endpoint, enabling unauthenticated command execution in versions…
 alardiians/gitea-cve-2026-28699
Lab + writeup for CVE-2026-28699: Gitea OAuth2 scope enforcement bypass via HTTP Basic auth
 hunt-benito/ash-authentication-oauth2-oidc-account-takeover-cve-2026-49757-email-based-user-matching
Proof-of-concept exploit for CVE-2026-49757 demonstrating OAuth2/OIDC account takeover via email-based user matching in AshAuthentication, with…
 ez4rd1x1/cve-2026-8181
Proof-of-concept exploit for CVE-2026-8181, an authentication bypass in the Burst Statistics WordPress plugin. Demonstrates remote, unauthenticated…
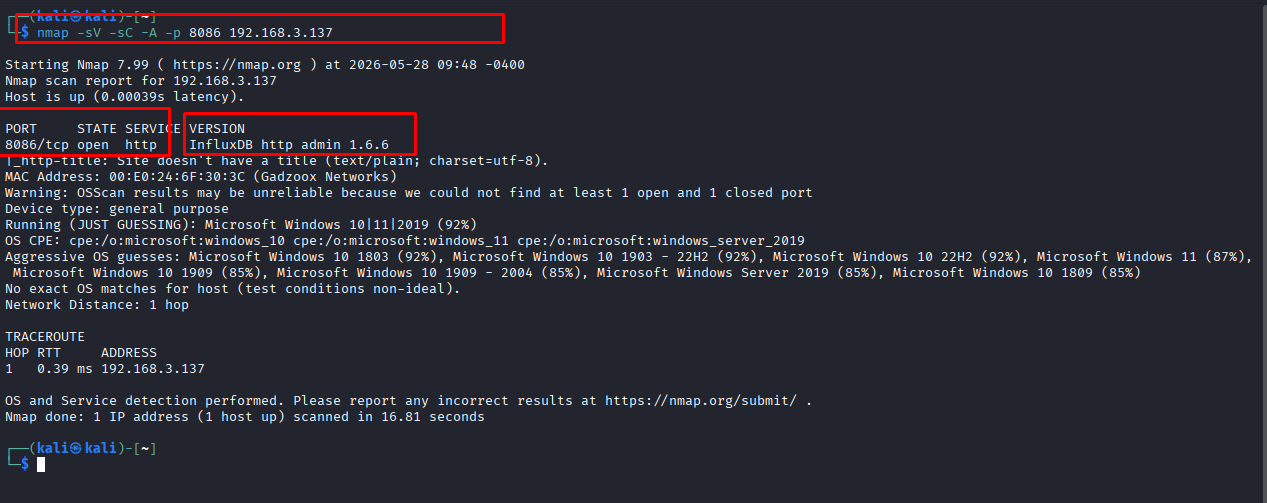 dungsocool/cve-2019-20933
Step-by-step lab writeup demonstrating CVE-2019-20933 InfluxDB authentication bypass via forged JWT tokens, including exploitation,…
 kaleth4/cve-2026-20896
Automated PoC exploit for CVE-2026-20896, a Gitea authentication bypass via directory traversal in the API authorization header, enabling…
 toddkk02/cve-2025-29927
Proof-of-concept exploit for CVE-2025-29927, demonstrating authentication bypass in Next.js middleware via the x-middleware-subrequest header, with…
 0xdtc/crushftp-auth-bypass-cve-2025-31161
Exploit for CrushFTP CVE-2025-31161 auth bypass: detects vulnerable targets, enumerates users, and creates unauthorized admin accounts through…
 yafiah-darwesh/cs50-cyber-paloalto-oauth
CS50 Cybersecurity final project — Palo Alto OAuth token breach (CVE-2024-3400)