

osx-password-dumper
 jeanpeyremesmots/osx-password-dumper
A tool to dump users's .plist on a Mac OS system and to convert them into a crackable hash
ctfpassword-crackingpenetration-testing+2
53
jeanpeyremesmots/osx-password-dumperA tool to dump users's .plist on a Mac OS system and to convert them into a crackable hash
 r4ygm/stegbrute
Fast Steganography bruteforce tool written in Rust useful for CTF's
 bee-san/name-that-hash
Identify 300+ hash types instantly via CLI or web app. Prioritizes popular hashes, provides summaries, and integrates with HashCat and John the…
 paradoxis/stegcracker
Steganography brute-force utility to uncover hidden data inside files
 tim-karov/cmsms-sqli
Python3 exploit for CVE-2019-9053 (CMS Made Simple <= 2.2.9 SQLi). No deps, time-based blind SQLi → admin creds dump. HTB Writeup owned.
 pczbuilds/monikerlink-cve-2024-21413-writeup
Writeup of TryHackMe's Moniker Link room, exploiting CVE-2024-21413 to bypass Outlook Protected View and capture NTLMv2 hashes via crafted Moniker…
 maikneysm/autopwn-titanic.htb
This is an automated exploitation script for the Hack The Box machine *Titanic*. It extracts Gitea user hashes via LFI, assists in cracking them, and…
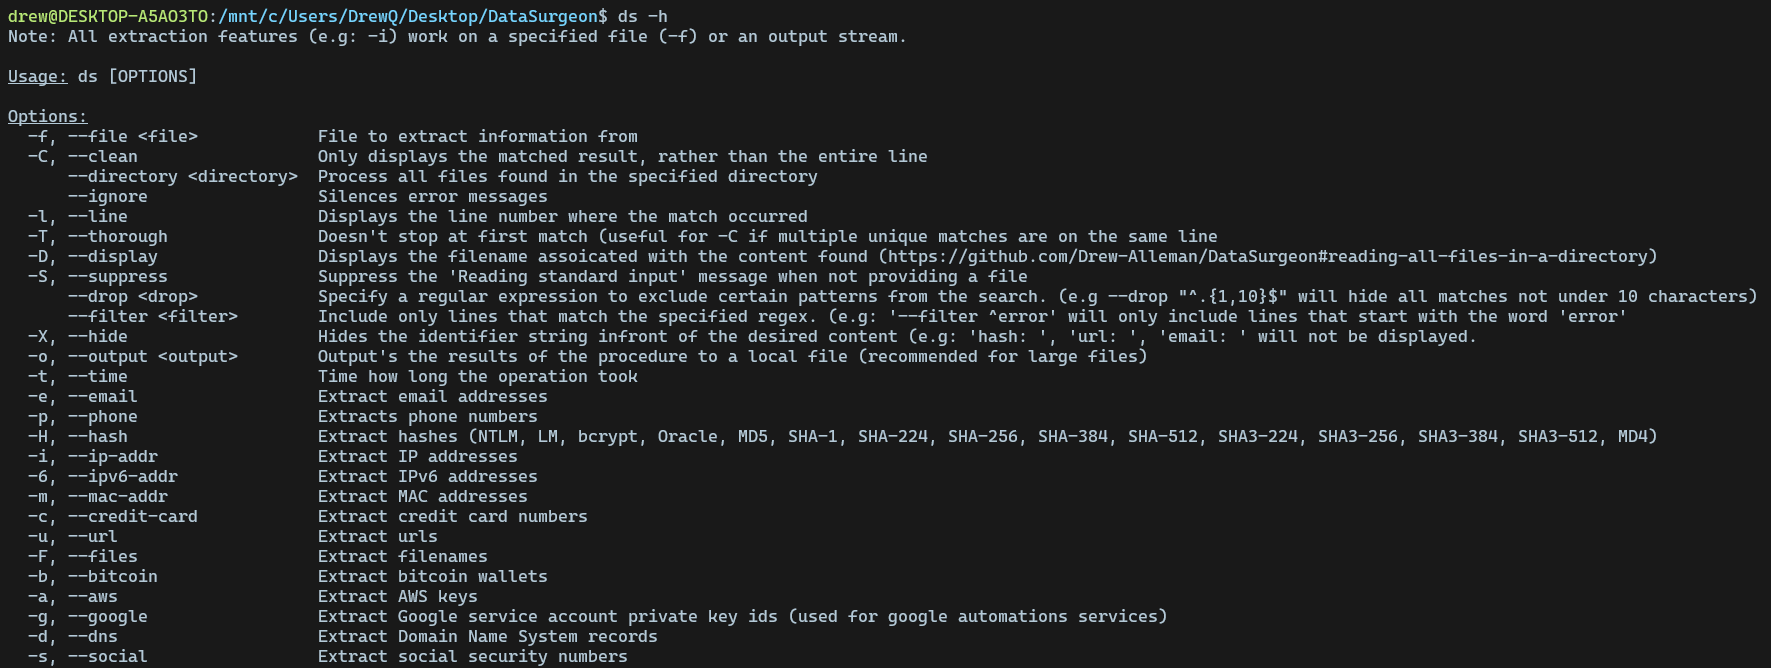 drew-alleman/datasurgeon
Quickly Extracts IP's, Email Addresses, Hashes, Files, Credit Cards, Social Security Numbers and a lot More From Text
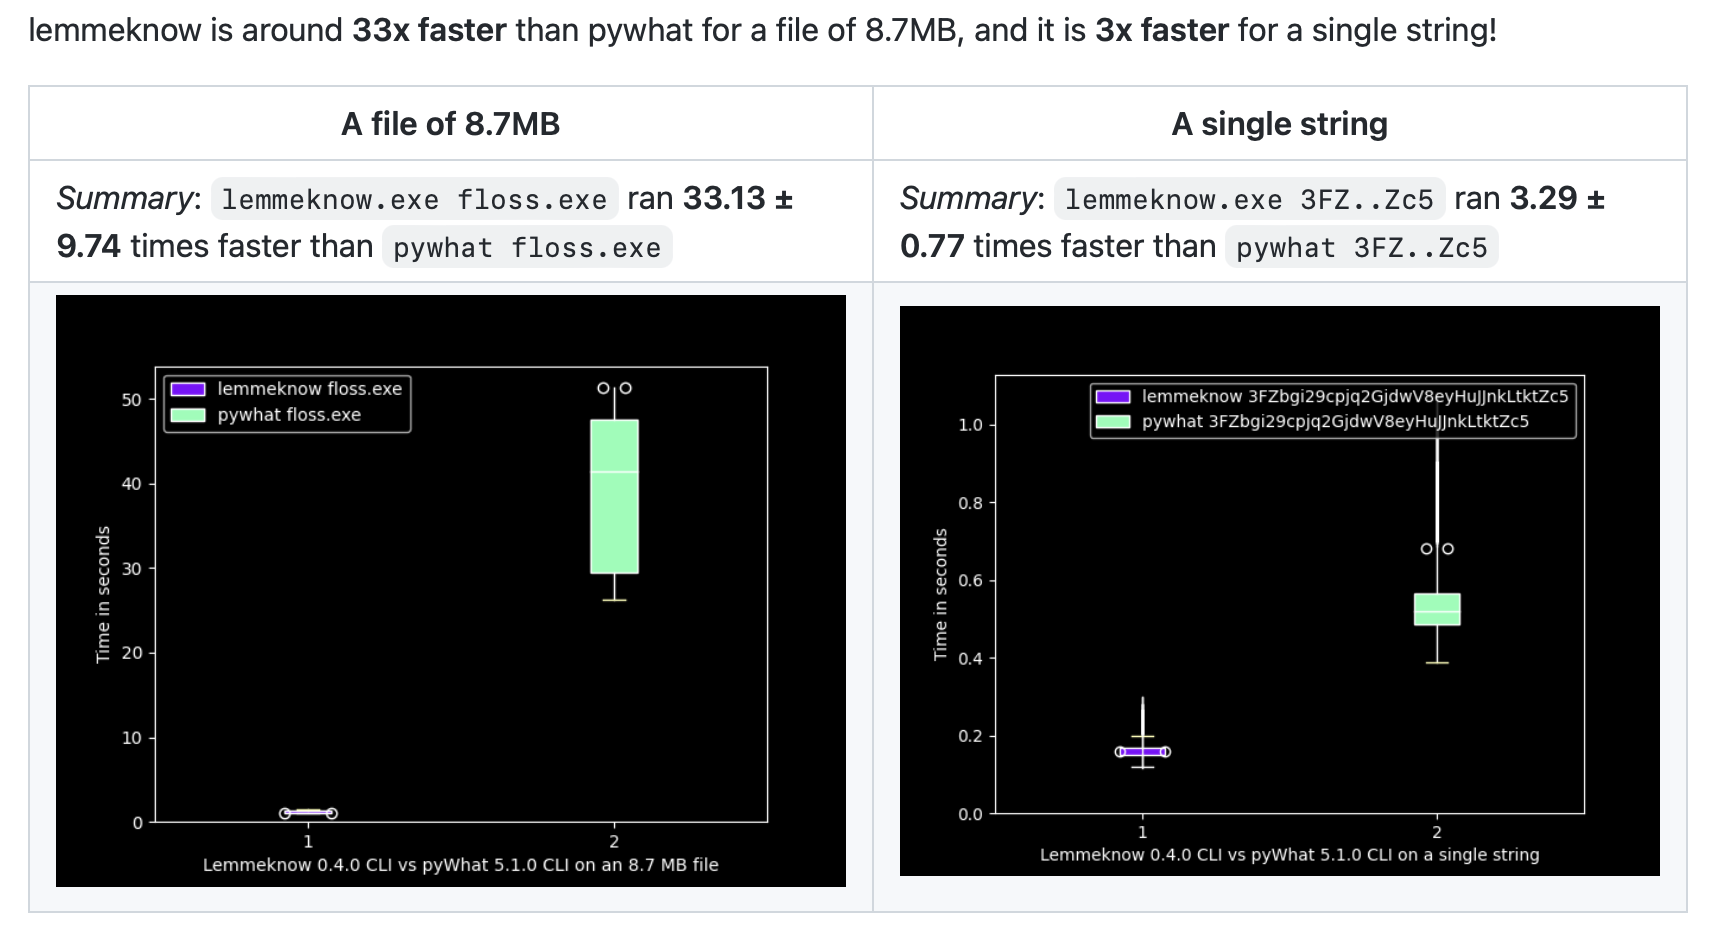 bee-san/ciphey
⚡ Automatically decrypt encryptions without knowing the key or cipher, decode encodings, and crack hashes ⚡
 perseus99999/cve-2019-9053-working-
CMS Made Simple < 2.2.10 - SQL Injection . Actual working version
 helich0pper/karkinos
Penetration Testing and Hacking CTF's Swiss Army Knife with: Reverse Shell Handling - Encoding/Decoding - Encryption/Decryption - Cracking Hashes /…
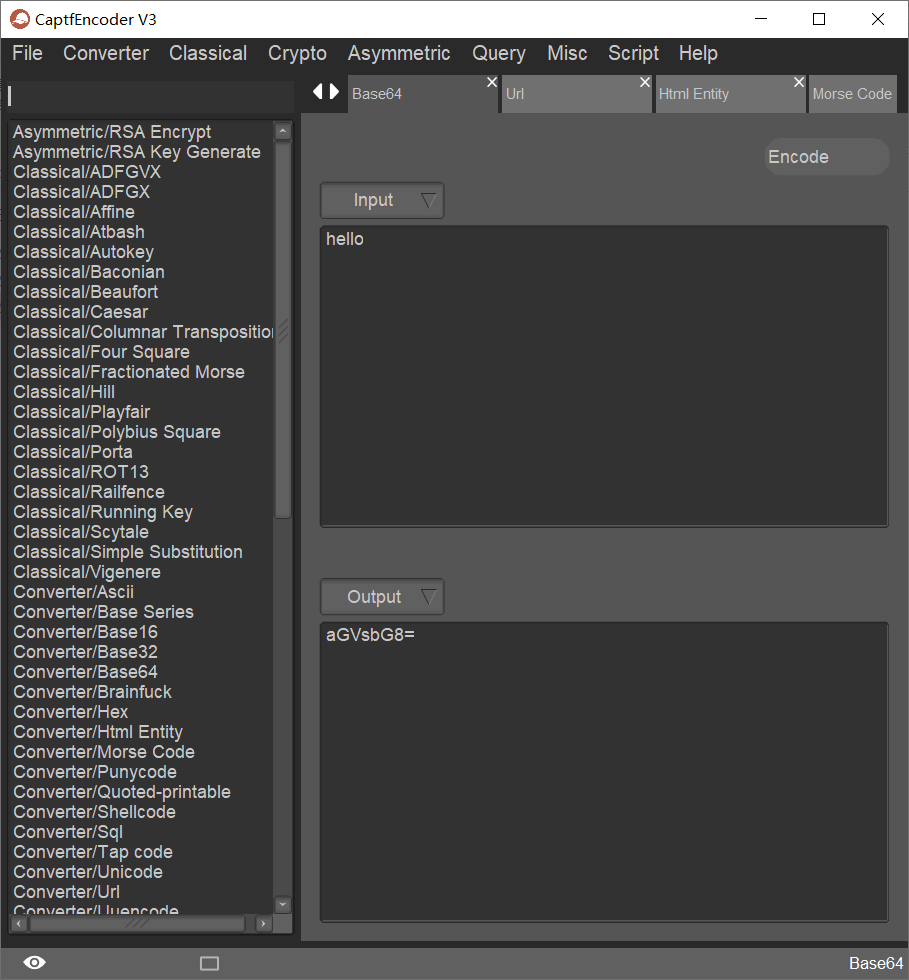 guyoung/captfencoder
Cross-platform security toolkit for encoding, classical and modern cryptography, hash computation, and online reconnaissance queries, designed for…

 k4m4/dcipher-cli
🔓Crack hashes using online rainbow & lookup table attack services, right from your terminal.
 k4m4/dcipher
Decipher hashes using online rainbow & lookup table attack services.
 dampedcoast/exploiting-a-vulnerability-using-reverse-shell
This project simulates a real-world attack-and-defend scenario across two virtual machines. You will exploit a critical pre-authentication RCE…
 p1rat3r00t/why-so-serious-sam
PoC malware that uses exploit CVE-2021-36934 (improper ACLs on shadow copies) using a fileless red team method on Windows 10/11 with LOLBins,…