

pspy
 dominicbreuker/pspy
Monitor linux processes without root permissions
ctfinformation-gatheringpenetration-testing+2
dominicbreuker/pspyMonitor linux processes without root permissions
 tenable/cnappgoat
CNAPPgoat is an open source project designed to modularly provision vulnerable-by-design components in cloud environments.
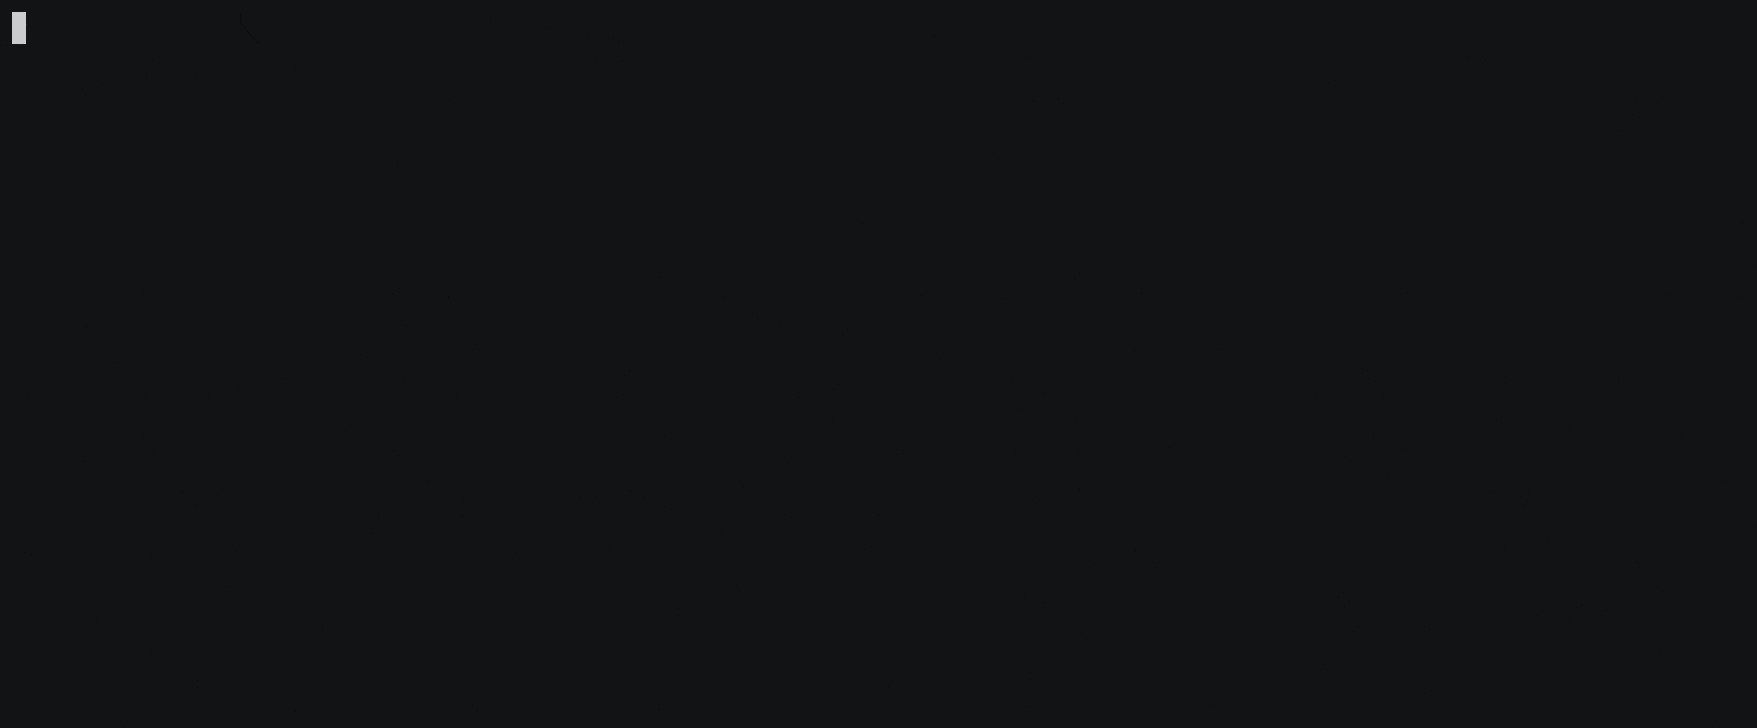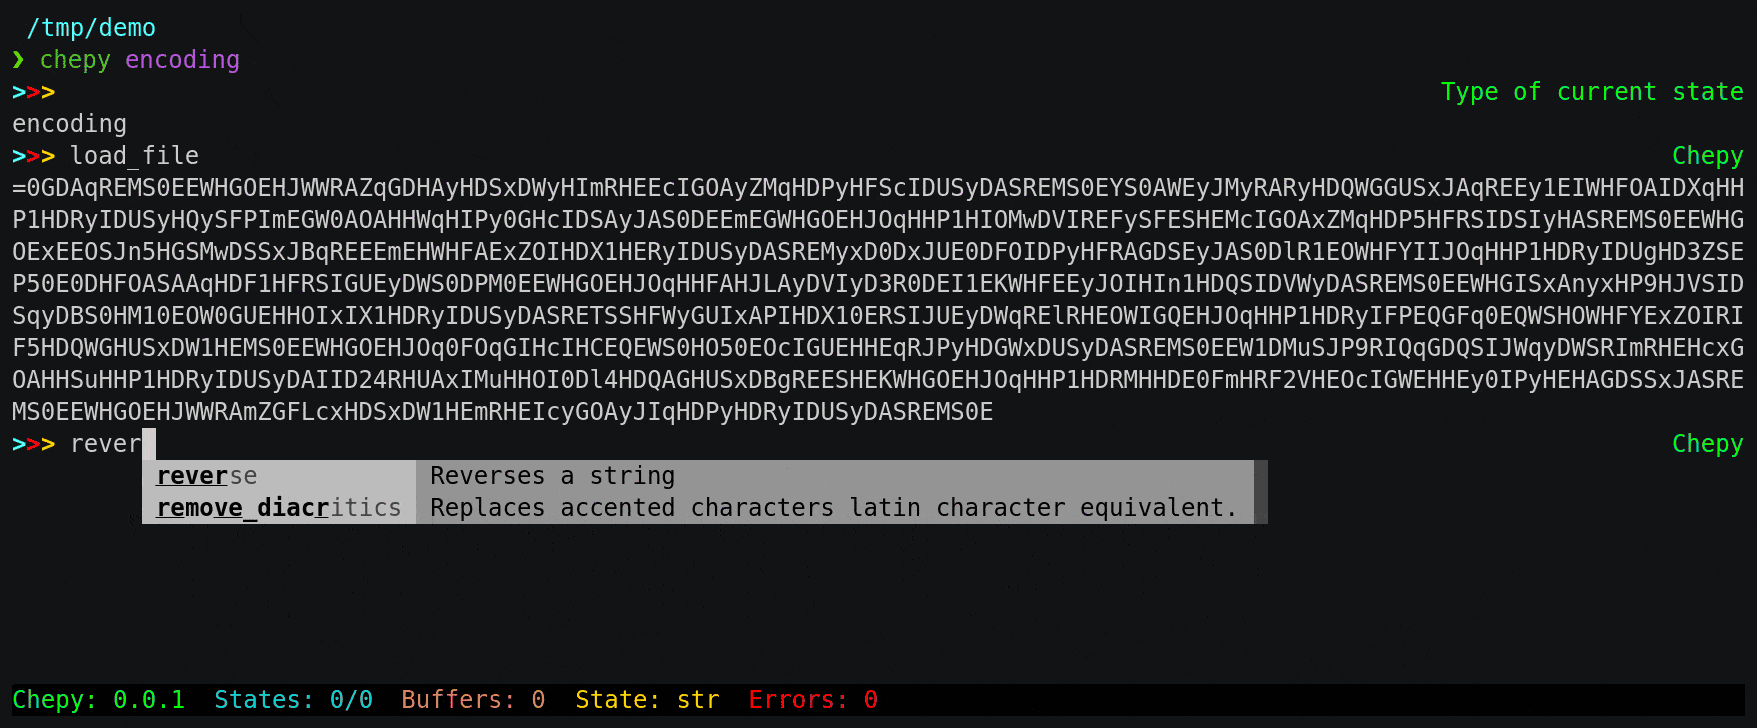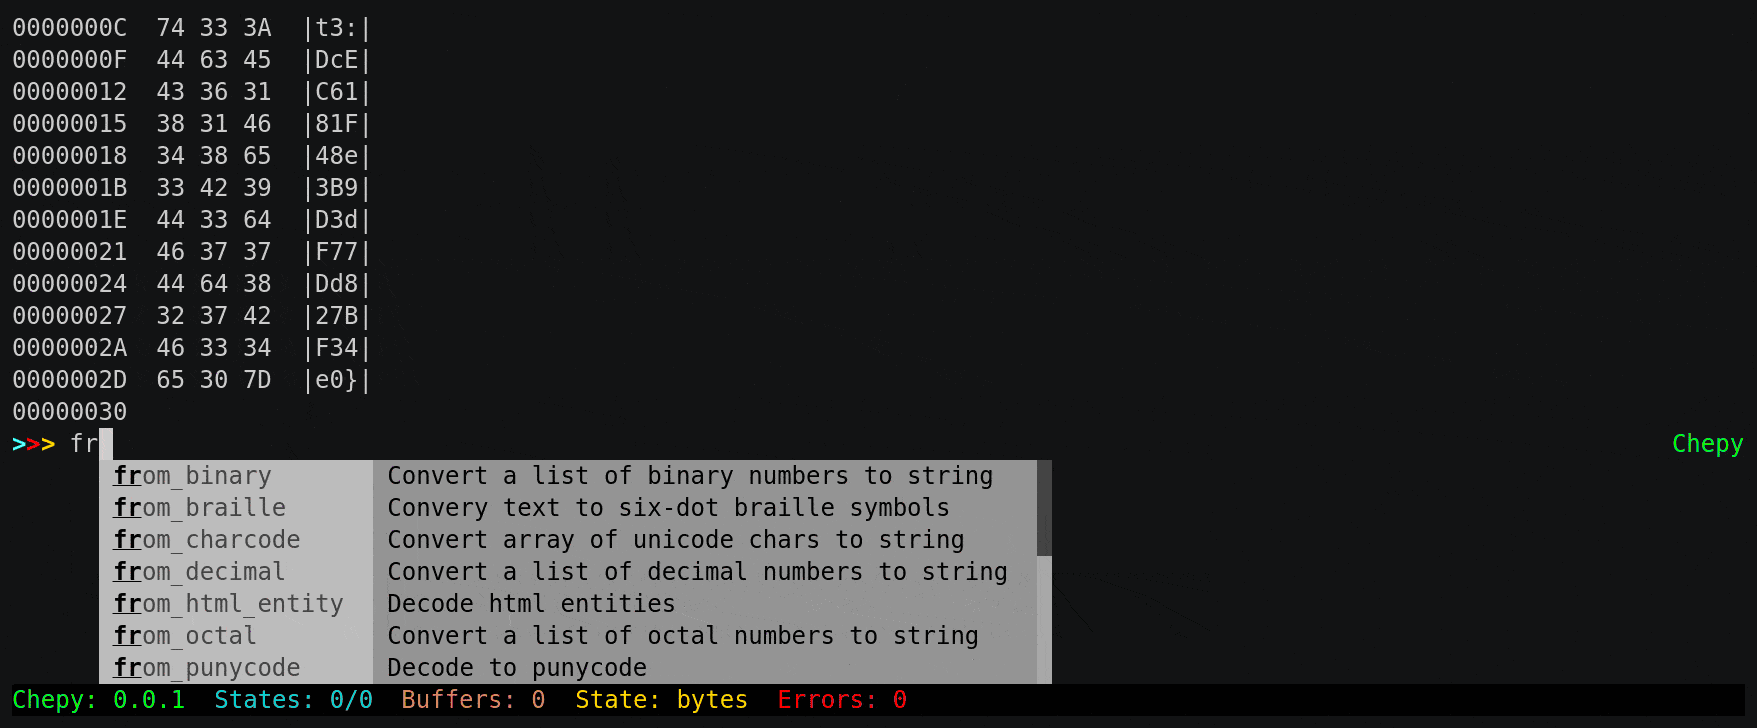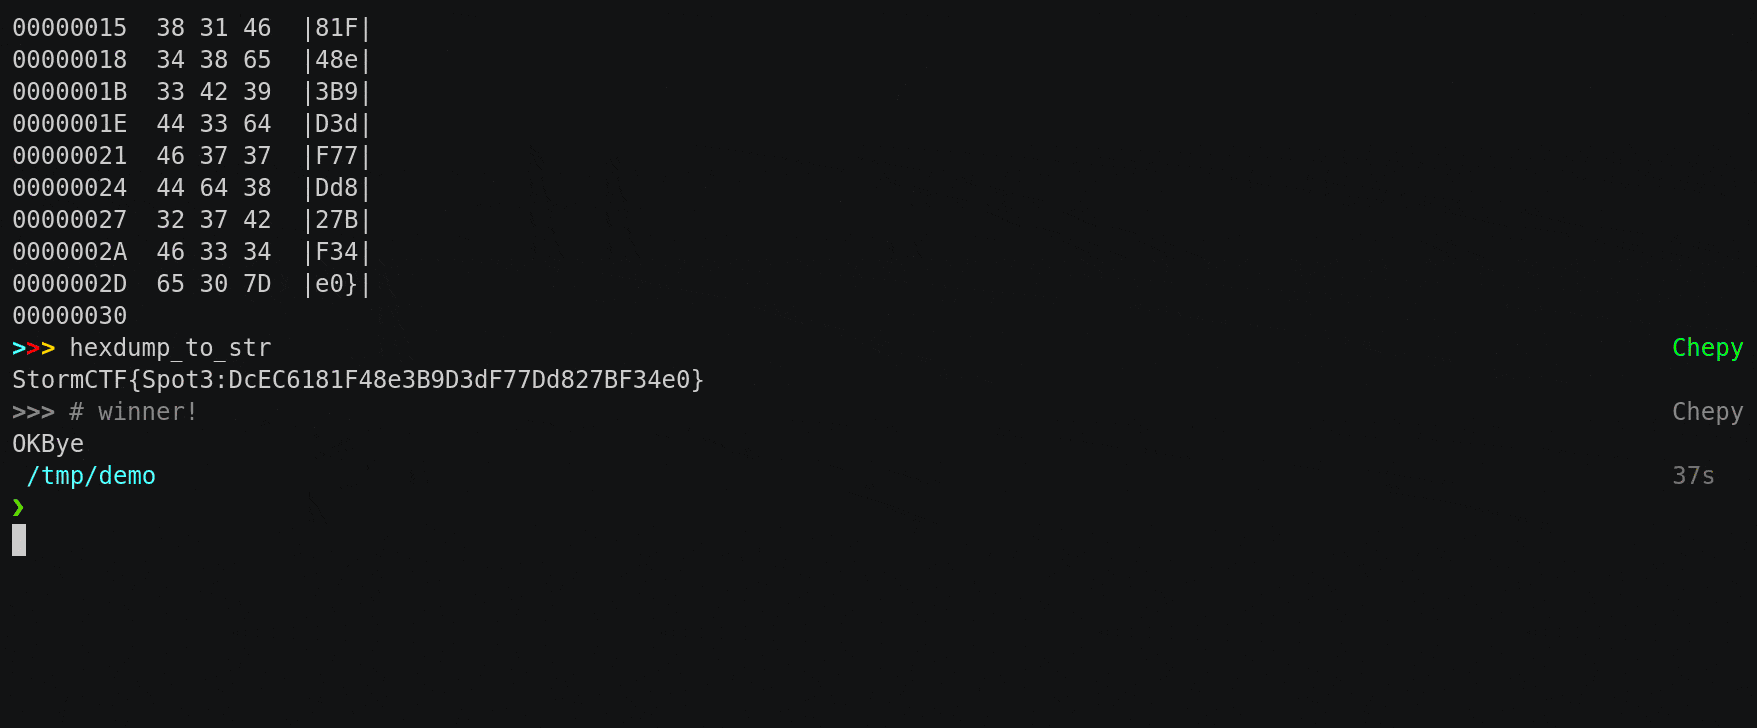 securisec/chepy
Chepy is a python lib/cli equivalent of the awesome CyberChef tool.
 alardiians/gitea-cve-2026-28699
Lab + writeup for CVE-2026-28699: Gitea OAuth2 scope enforcement bypass via HTTP Basic auth
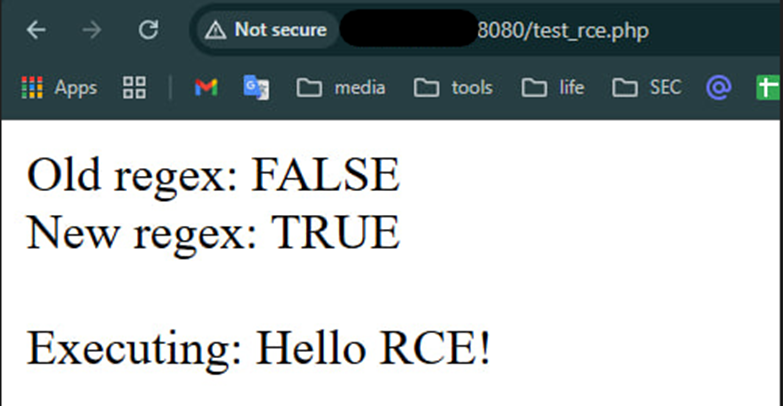 soltanali0/cve-2024-12877-exploit
Educational CVE-2024-12877 exploit demo for PHP Object Injection in GiveWP WordPress plugin. Includes root cause analysis, regex bypass techniques,…
 cure53/xsschallengewiki
Community-maintained wiki cataloging XSS challenges and solutions, providing curated hands-on exercises for learning cross-site scripting…
 fauzan-aldi/cve-2022-21661
A Python PoC for CVE-2022-21661, adapted from z92g's Go PoC, designed to demonstrate the vulnerability in a more accessible scripting environment.
 bishopfox/local-llm-ctf
A small go harness that uses Ollama to orchestrate LLMs in a restricted process flow
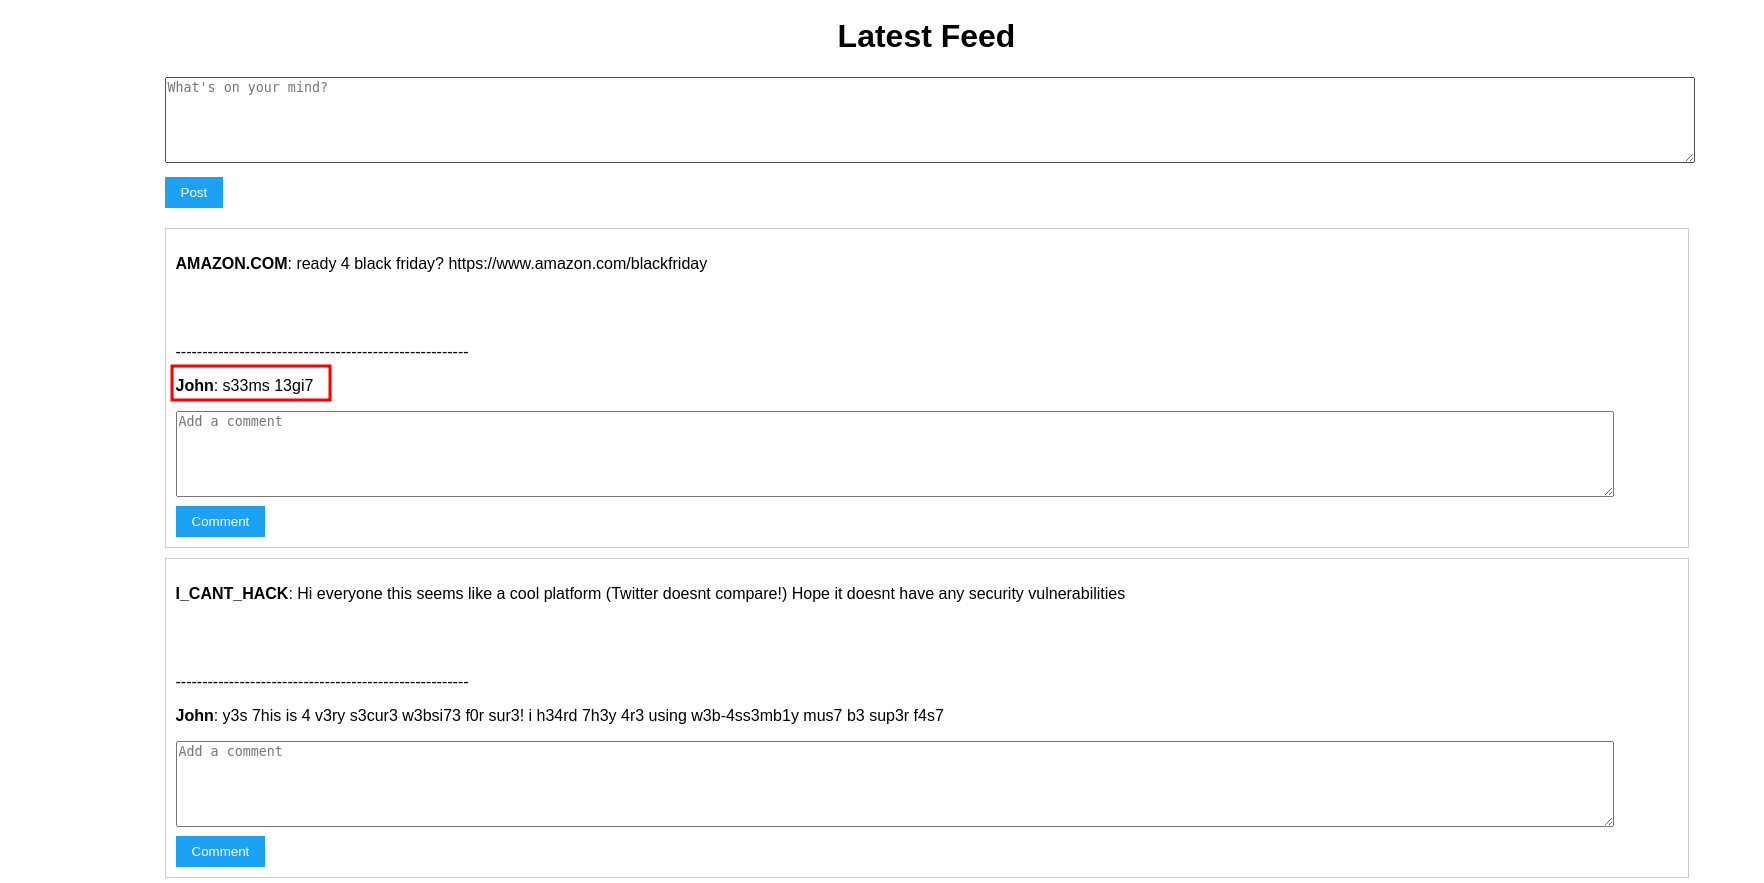 paras98/cve-2021-38297-go-wasm-replication
Educational proof-of-concept replicating CVE-2021-38297, a Go WASM buffer overflow leading to stored XSS. Includes vulnerable app setup, exploit…
 0ca/boxpwnr
A modular framework for benchmarking LLMs and agentic strategies on security challenges across HackTheBox, TryHackMe, PortSwigger Labs, Cybench,…
 microsoft/ai-red-teaming-playground-labs
AI Red Teaming playground labs to run AI Red Teaming trainings including infrastructure.
 gosecure/pyrdp
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
 adityabhatt3010/react2shell-cve-2025-55182
React2Shell CVE-2025-55182: unauthenticated unsafe deserialization in React Server Components leading to reliable remote code execution via the…
 3jee/copy-fail-go
Go port of the CVE-2026-31431 (copy-fail) Linux kernel privilege escalation PoC, with automatic SUID binary enumeration and interactive target…
 bitburner/ivre-wizard
An interactive wizard front end for IVRE to make creating scans to the database easier.
 echosecure/vuln-chain-lab
PoC Docker lab: chaining file upload bypass + stored XSS to create admin accounts. Educational resource for pen testers.
 ethicalpap/cve-2025-29775
Educational lab environment demonstrating SAMLStorm (CVE-2025-29775) vulnerability in xml-crypto library. Includes vulnerable SAML service provider,…
 0xdtc/crushftp-auth-bypass-cve-2025-31161
Exploit for CrushFTP CVE-2025-31161 auth bypass: detects vulnerable targets, enumerates users, and creates unauthorized admin accounts through…