
Flask-Unsign
 paradoxis/flask-unsign
Command line tool to fetch, decode, brute-force and craft session cookies of a Flask application by guessing secret keys.
ctfpassword-attackspenetration-testing+1
paradoxis/flask-unsignCommand line tool to fetch, decode, brute-force and craft session cookies of a Flask application by guessing secret keys.
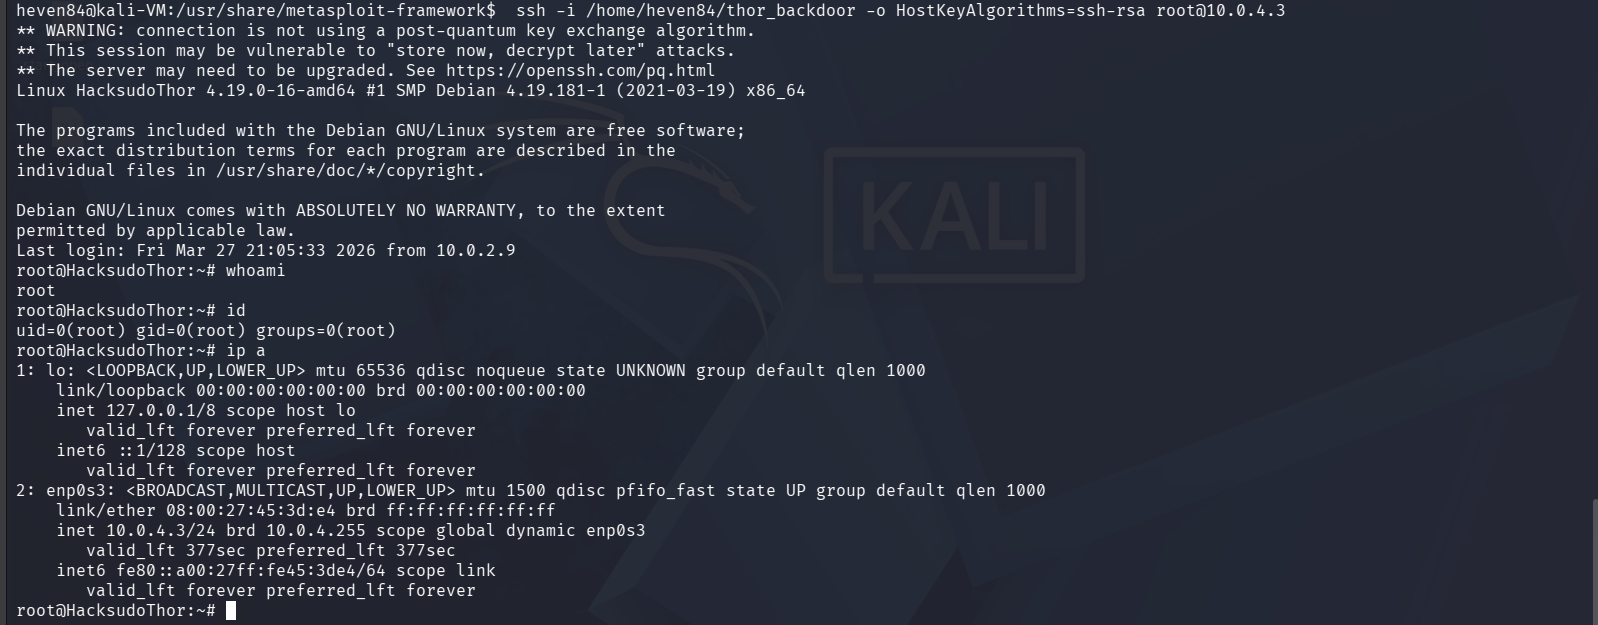 heventafese/penetration-testing-walkthrough-hacksudo-thor
Black-box penetration test against HackSudo Thor : CVE-2014-6271 Shellshock RCE through Apache mod_cgi, chained with sudo misconfiguration and bash…
 m0d0ri205/wargame-turkey_in_2
CTF wargame platform featuring Unicode bypass exploitation (CVE-2015-9238), flag file segmentation, brute force delay, and password hashing for…
 paradoxis/stegcracker
Steganography brute-force utility to uncover hidden data inside files
 jeanpeyremesmots/osx-password-dumper
A tool to dump users's .plist on a Mac OS system and to convert them into a crackable hash

 rickdejager/stegseek
:zap: Worlds fastest steghide cracker, chewing through millions of passwords per second :zap:
 r4ygm/stegbrute
Fast Steganography bruteforce tool written in Rust useful for CTF's
 perseus99999/cve-2019-9053-working-
CMS Made Simple < 2.2.10 - SQL Injection . Actual working version
 adityabhatt3010/room-walkthrough-billing
A detailed walkthrough of Billing room exploiting CVE-2023-30258 and escalating via fail2ban misconfig
 hack-with-github/awesome-hacking
A collection of various awesome lists for hackers, pentesters and security researchers
 the-art-of-hacking/h4cker
Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
 trimstray/the-book-of-secret-knowledge
A collection of inspiring lists, manuals, cheatsheets, blogs, hacks, one-liners, cli/web tools and more.
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
 enaqx/awesome-pentest
A collection of awesome penetration testing resources, tools and other shiny things
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 gchq/cyberchef
The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis