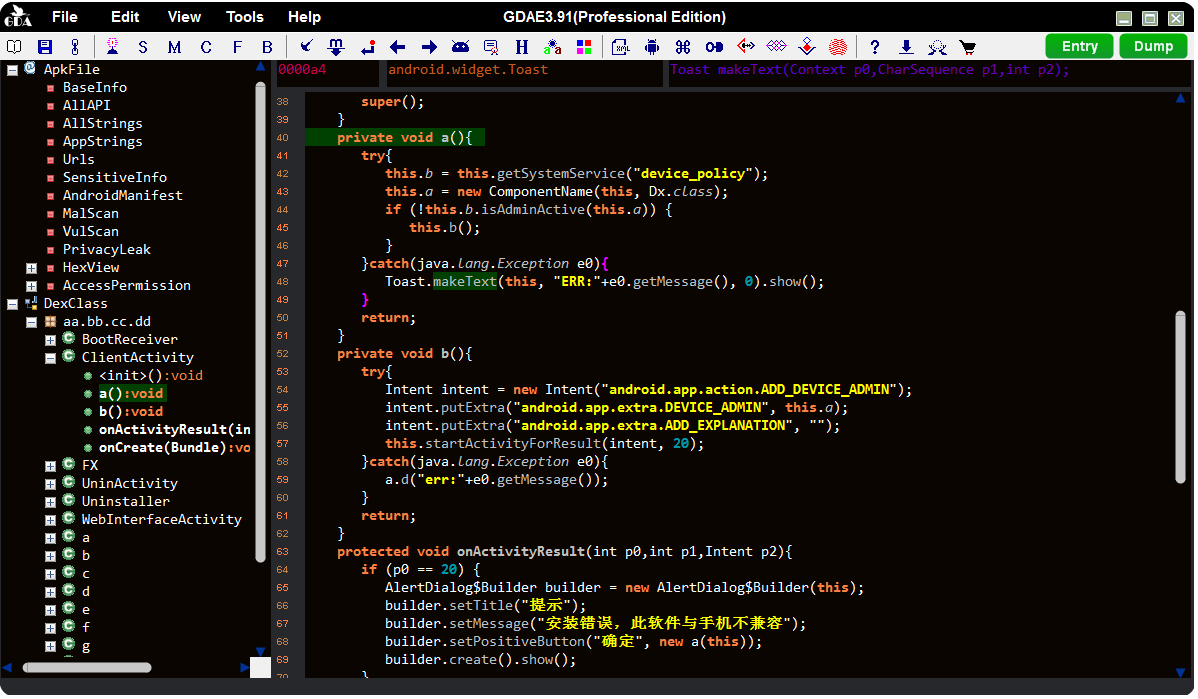
GDA-android-reversing-Tool

the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…

the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…

Display information about files in different file formats and find gadgets to build rop chains for different architectures (x86/x86_64, ARM/ARM64,…

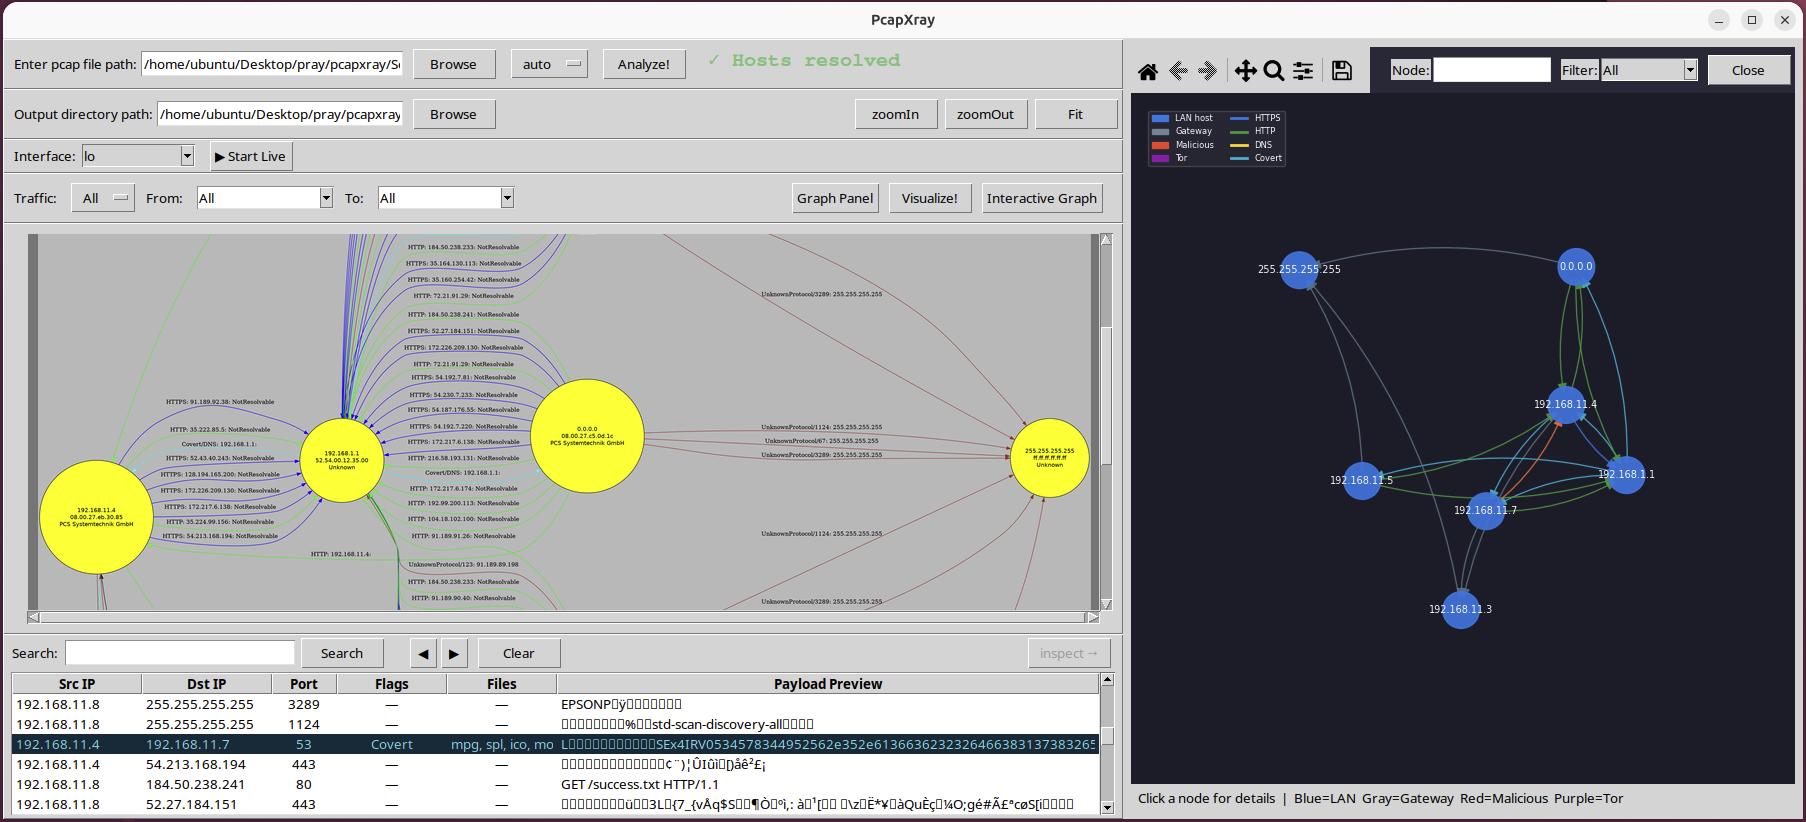
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…

Feature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP…

Annual small file competition repository with binary golf challenges across themes like polyglots, crashes, self-replication, and downloads,…

Exploit for CVE-2026-46215, a Linux kernel DRM GEM use-after-free local privilege escalation. Uses racing, slab spraying, and Dirty Pipe-style file…

Proof-of-concept exploit for ImageMagick arbitrary file read vulnerability (CVE-2022-44268) via crafted PNG textual chunks, enabling extraction of…

Code Roulette is a terminal interface based (TUI), online multiplayer, Russian Roulette game where the loser executes the winner's Python payload…

Exploit for Metabase CVE-2021-41277, a local file inclusion vulnerability in custom GeoJSON map support, allowing unauthorized file access.

This repository contains a Crystallographic Information File (CIF) intended for use on the "Chemistry" machine on Hack The Box (HTB).

Proof-of-concept exploit for CVE-2026-48908, an unauthenticated RCE in Joomla SP Page Builder via arbitrary file upload, with adaptive payload…

CVE-2025-4138 - Python Arbitrary file write outside extraction directory

This program Prompts you for the Local File Inclusion information and will automatically search the /etc/passwd and using the users names found will…

This is a exploit for the known Remote Code Execution (RCE) vulnerability in the `pymatgen` (CVE-2024-23346) Python library by uploading a malicious…

Proof-of-concept exploit for CVE-2024-32258, a path traversal vulnerability in FCEUX NetPlay 2.7.0 enabling unauthenticated remote arbitrary file…

Proof-of-concept exploit for CVE-2025-49132, abusing a file inclusion vulnerability in Pterodactyl to achieve remote code execution via pearcmd.php.

Arbitrary file read controller based on CVE-2021-29447

PoC scripts to exploit LFR (Local File Read) via PHP filters chain oracle (php://filter), especially for CTF purposes or the exploit of…