
HTB-NanoCorp-CVE-2024-0670
 taktak0x/htb-nanocorp-cve-2024-0670
PowerShell exploit for CVE-2024-0670 that abuses CheckMK Agent MSI repair to escalate privileges to SYSTEM on the NanoCorp Hack The Box machine.
ctfeducationexploitation+4
taktak0x/htb-nanocorp-cve-2024-0670PowerShell exploit for CVE-2024-0670 that abuses CheckMK Agent MSI repair to escalate privileges to SYSTEM on the NanoCorp Hack The Box machine.

 sleventyeleven/linuxprivchecker
Local Linux enumeration script that identifies privilege escalation vectors including misconfigurations, world-writable files, clear-text passwords,…
 shellphish/ictf-framework
Open-source framework for hosting Attack/Defense CTF competitions with automated gamebot, script execution, VPN routing, and cloud-based…
 gr1mmie/autoenum
Automatic Service Enumeration Script
 evyatarmeged/stegextract
Bash script that extracts trailing data, embedded files, and hidden strings from PNG, JPG, and GIF images using magic numbers and hexdump analysis.
 koadt/poc-cve-2025-29927
This repository contains a proof of concept (POC) and an exploit script for CVE-2025-29927, a critical vulnerability in Next.js that allows attackers…
 0xcomposure/fftstegpic
A python script for digital image steganography using Fast Fourier Transform.
 elit3pwner/cve-2015-1328-goldeneye
Automated local privilege escalation exploit for CVE-2015-1328 targeting Ubuntu overlayfs, designed for CTF environments with a simple bash…
 azureadtrent/cve-2025-4517-poc
Privilege Escalation script for CVE-2025-4517
 l41kaa/cve-2023-33733-exploit-poc
Python exploit script for CVE-2023-33733 targeting web applications. Automates authentication, session extraction, and reverse shell delivery for…
 ritinify/cve-2025-29927-poc
Proof-of-concept exploit for CVE-2025-29927, a Next.js middleware authorization bypass. Includes a vulnerable target lab and Python script to verify…
 jroo1053/grafanadirinclusion
Script to demonstrate the Grafana directory traversal exploit (CVE-2021-43798).
 r4y-br/cve-2022-22963
Python automation script that reproduces CVE-2022-22963, a critical SpEL injection in Spring Cloud Function, enabling reverse shell in authorized lab…
 d1se0/cve-2024-10924-bypass-mfa-wordpress-lab
Lab environment and exploit script for CVE-2024-10924, demonstrating MFA bypass in WordPress via the Really Simple SSL plugin's skip_onboarding…
 cves-labs/cve-2026-21877
Dockerized vulnerable lab environment with a Python-based network monitor and dedicated exploit script, enabling hands-on exploitation, privilege…
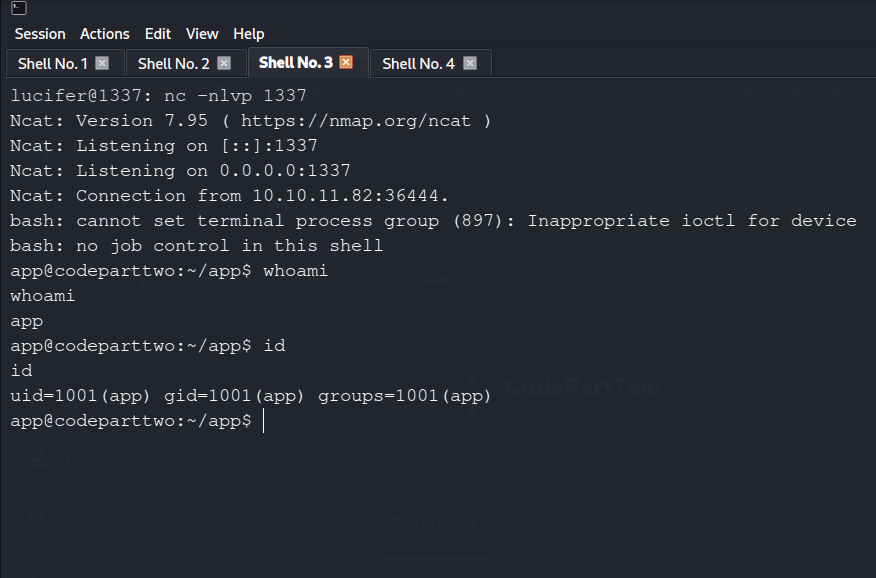 l1337xi/cve-2024-28397-exploit-automation
A Python automation script for exploiting the **js2py Sandbox Escape** vulnerability (CVE-2024-28397). This tool automates the payload generation and…
 liquid-sec/variatype.htb-cve-2025-66034
Python exploit script for CVE-2025-66034 in the HackTheBox Variatype machine, delivering command execution and reverse shell payloads for initial…