

 benedictejepu/cve-2024-24945-nginx-rift---tryhackme-lab-walkthrough
This lab demonstrates the exploitation of CVE-2024-24945, a heap corruption vulnerability affecting NGINX. The objective was to understand how memory…
 eyodav/cve-2025-34157
A stored XSS in the project delete flow allows execution of attacker-controlled JavaScript in an administrator’s browser when the admin attempts to…
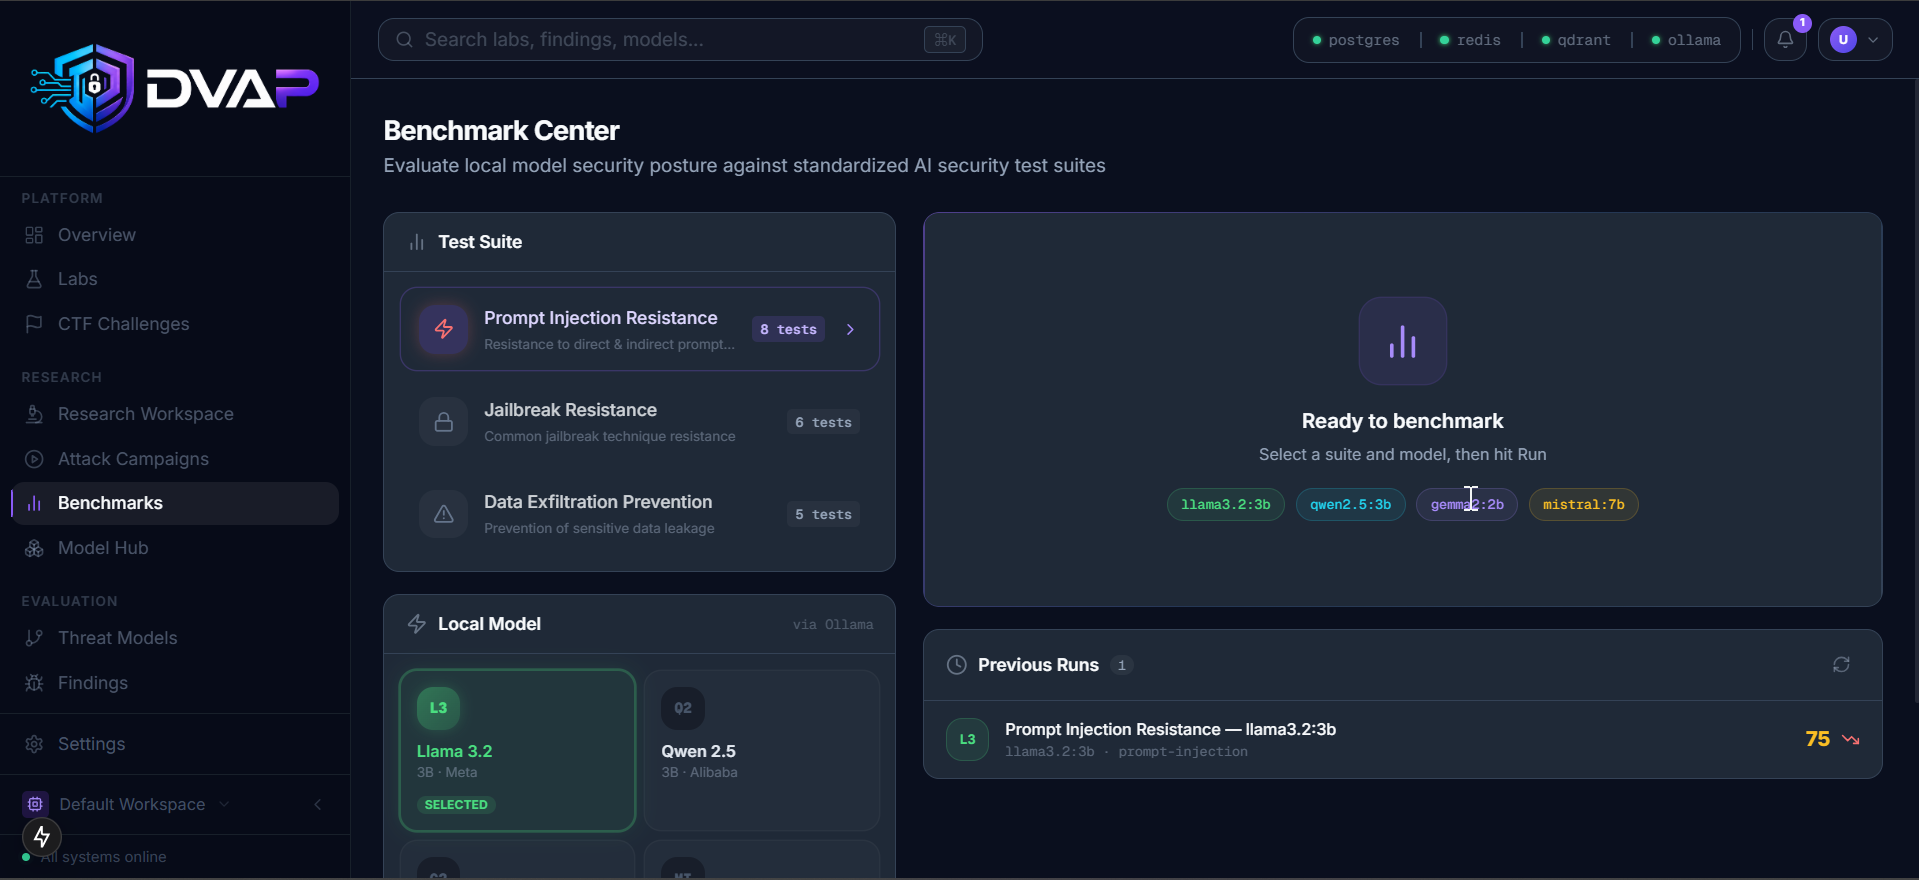 sonuoffsec/dvap
An OWASP-aligned intentionally vulnerable platform for learning and testing AI, LLM, RAG, MCP, and Agentic AI security.
 shen771/blackash-cve-2025-55182
CVE-2025-55182