Linux-Kernel-Dirty-Pipe-Exploitation-Logic-Bug-
 bluedragonsecurity/linux-kernel-dirty-pipe-exploitation-logic-bug-
Exploiting CVE-2022-0847 - written by : Antonius (w1sdom)
binary-exploitationcode-analysisctf+5
bluedragonsecurity/linux-kernel-dirty-pipe-exploitation-logic-bug-Exploiting CVE-2022-0847 - written by : Antonius (w1sdom)
 l41kaa/cve-2023-33733-exploit-poc
Python exploit script for CVE-2023-33733 targeting web applications. Automates authentication, session extraction, and reverse shell delivery for…
 thefizzyfish/cve-2025-4138_tarfile_filter_bypass
CVE-2025-4138 - Python Arbitrary file write outside extraction directory
 josh-blythe/bordair-detector
Two-stage prompt-injection and jailbreak detector: regex gates plus a quantised DeBERTa-v3 ONNX classifier, with image, document, and audio support.…
 itsc1sco/freepbx-sqli-exploit-privilege-escalation
This walkthrough documents the complete compromise of the HTB machine Connected.
 aalex954/jwt-key-confusion-poc
JWT Key Confusion PoC (CVE-2015-9235) Written for the Hack the Box challenge - Under Construction
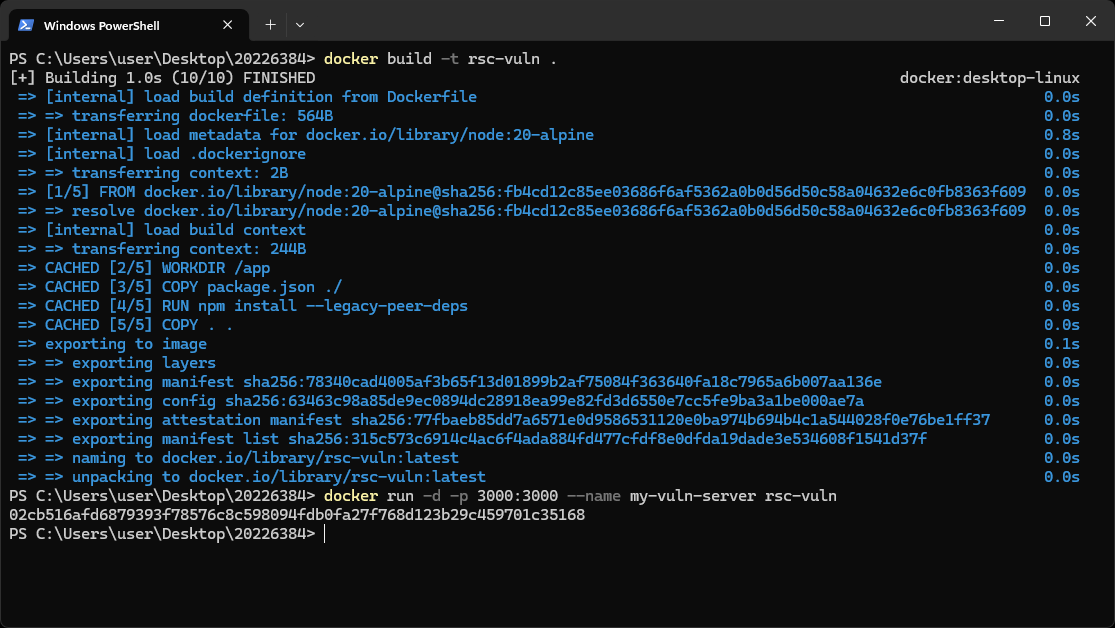
 sparshbiswas-ai/cve-2025-11844-smolagents
Educational sandbox and dynamic proof-of-concept scanner for CVE-2025-11844 XPath injection in Hugging Face smolagents library, enabling local data…
 zenithgenius/wordpress-batch-rce-lab
CVE-2026-63030: WordPress REST batch-endpoint array desync. Mechanism, detection, mitigation, and a safe reproduction lab.
 rippsec/cve-2025-24893-xwiki-ssti-rce
CVE-2025-24893 – XWiki SSTI unauthenticated RCE exploit (HackTheBox CTF)
 rippsec/cve-2025-49113-roundcube-rce
CVE-2025-49113 – Roundcube ≤1.6.10 post-auth RCE via PHP object deserialization (HackTheBox CTF)
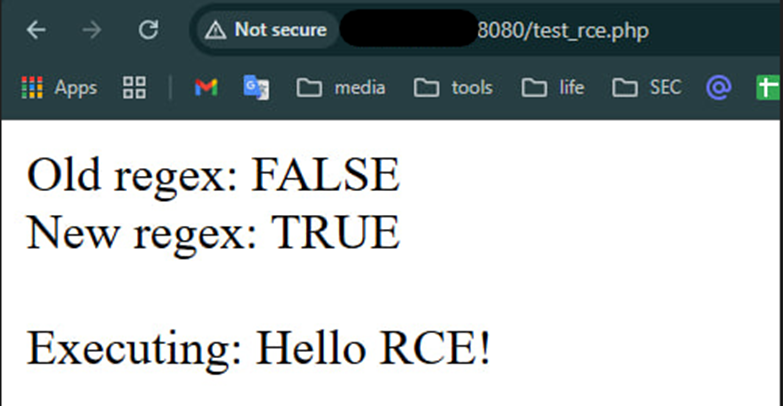 soltanali0/cve-2024-12877-exploit
Educational CVE-2024-12877 exploit demo for PHP Object Injection in GiveWP WordPress plugin. Includes root cause analysis, regex bypass techniques,…
 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…
 ankitpandey383/roundcube-cve-2025-49113-lab
Hands-on exploitation lab for Roundcube Webmail CVE-2025-49113 (authenticated PHP object deserialization → RCE) to read /secret.txt.
 ldb33/cve-2023-24249-poc
Proof-of-concept exploit for CVE-2023-24249, an arbitrary file upload vulnerability in laravel-admin, enabling web shell deployment for penetration…
 useru1k/php-8.1.0-dev-exploit
Exploit for the PHP 8.1.0-dev backdoor vulnerability (CVE-2021-21707)
 nou-man/cve-2022-46169
Proof of concept / CTF script for exploiting CVE-2022-46169 in Cacti, versions >=1.2.22