CVE-2022-30190-Analysis-With-LetsDefends-Lab
 abdibimantara/cve-2022-30190-analysis-with-letsdefends-lab
this is my simple article about CVE 2022-30190 (Follina) analysis. I use the lab from Letsdefend.
ctfeducationexploitation+3
abdibimantara/cve-2022-30190-analysis-with-letsdefends-labthis is my simple article about CVE 2022-30190 (Follina) analysis. I use the lab from Letsdefend.
 rishabh-kumar-cyber-sec/cve-2023-27163-ssrf-to-port-scanning
It is a simple script to automate internal port scanning dueto SSRF in requests-baskets v 1.2.1. this script can also assisst in solving 'SAU'…
 9xeb/context-segmentation
Multi-agent automated context management for long horizon tasks in local AI Agents
 iapetus12/hackcar-writeup
Writeup: Hackcar - DockerLabs (Node.js Inspector RCE + CVE-2025-55182 React2Shell)
 shivammittal2403/cve-2026-59827-metabase-cyber-range
Educational cyber range for CVE-2026-59827 (Metabase H2 unsafe deserialization / CWE-502). Isolated Docker lab — training only, not for attacking…
 taktak0x/htb-nanocorp-cve-2024-0670
PowerShell exploit for CVE-2024-0670 that abuses CheckMK Agent MSI repair to escalate privileges to SYSTEM on the NanoCorp Hack The Box machine.
 m4rc0s-s3c/cve-2025-5548-freefloat-ftp-lab
Laboratorio académico de análisis y explotación de CVE-2025-5548 en FreeFloat FTP Server 1.0.
 iapetus12/cohort-htb
HTB Cohort - SSRF, Marimo pre-auth RCE (CVE-2026-39987) y PackageKit privesc (CVE-2026-41651)
 shivammittal2403/cve-2025-57819-freepbx-range
Isolated educational FreePBX-compatible cyber range for CVE-2025-57819 (CWE-89/CWE-288). Docker lab — not official Sangoma FreePBX.
 athack-ctf/chall2026-telneted
[AtHack 2026] Pwn challenge about telnetd CVE-2026-24061
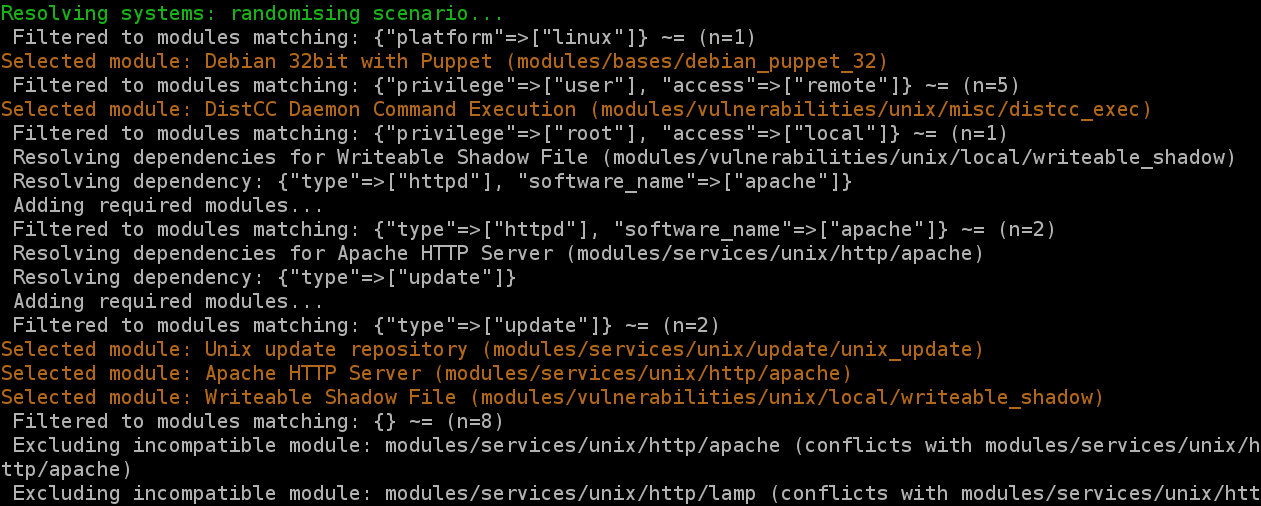 secgen/secgen
Generate vulnerable virtual machines on the fly (current team development is taking place in the cliffe/SecGen fork)
 octetsplicer/lazypariah
A tool for generating reverse shell payloads on the fly.
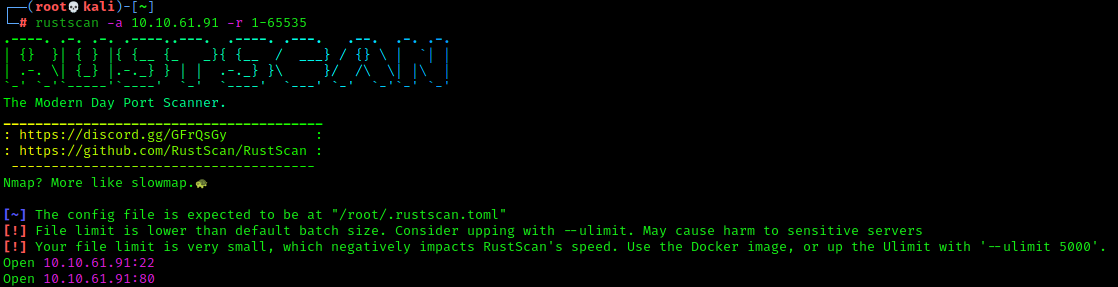 wizardy0ga/thm-vulnerability_capstone-cve-2018-16763
A write up on the THM room Vulnerability Capstone & Exploit script for CVE-2018-16763.
 wizardy0ga/thm-source-cve-2019-15231
A write up on the TryHackMe room Source & a python script to exploit the vulnerability