
CVE-2022-26134
 acfirthh/cve-2022-26134
A PoC for CVE-2022-26134 for Educational Purposes and Security Research
ctfeducationexploitation+3
acfirthh/cve-2022-26134A PoC for CVE-2022-26134 for Educational Purposes and Security Research
 carlosaruy/cve-2025-55182
a critical Remote Code Execution (RCE) vulnerability in React Server Components (RSC). It also includes a realistic "Lab Environment" to safely test…


 katseyres2/cve-2022-44268-pilgrimage
Automated proof-of-concept exploit for CVE-2022-44268 (ImageMagick arbitrary file read) with PNG payload generation, designed for CTF challenges and…
 bishopfox/otto-support
An implementation of a vulnerable MCP server using mcp-go
 franklincg/secdim-assurance-drift-challenge
SecDim Challenge Builder repro inspired by CVE-2026-88861: AAL1 MFA bypass at privileged credential boundary
 trivulzianus/tarantubench
The full repo of all the labs available as part of the benchmark
 vanhari/cve-2026-39987
Proof-of-concept exploit for an authentication bypass in marimo's terminal WebSocket endpoint, enabling unauthenticated command execution in versions…
 alardiians/gitea-cve-2026-28699
Lab + writeup for CVE-2026-28699: Gitea OAuth2 scope enforcement bypass via HTTP Basic auth
 hunt-benito/ash-authentication-oauth2-oidc-account-takeover-cve-2026-49757-email-based-user-matching
Proof-of-concept exploit for CVE-2026-49757 demonstrating OAuth2/OIDC account takeover via email-based user matching in AshAuthentication, with…
 ez4rd1x1/cve-2026-8181
Proof-of-concept exploit for CVE-2026-8181, an authentication bypass in the Burst Statistics WordPress plugin. Demonstrates remote, unauthenticated…
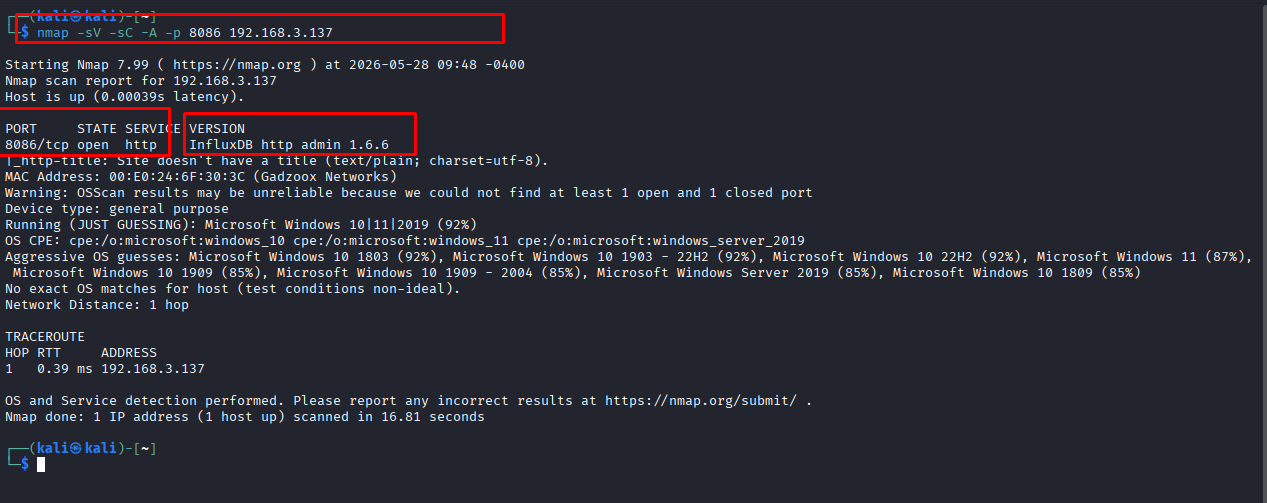 dungsocool/cve-2019-20933
Step-by-step lab writeup demonstrating CVE-2019-20933 InfluxDB authentication bypass via forged JWT tokens, including exploitation,…
 kaleth4/cve-2026-20896
Automated PoC exploit for CVE-2026-20896, a Gitea authentication bypass via directory traversal in the API authorization header, enabling…
 toddkk02/cve-2025-29927
Proof-of-concept exploit for CVE-2025-29927, demonstrating authentication bypass in Next.js middleware via the x-middleware-subrequest header, with…