
security-portfolio
 mitsu-bis/security-portfolio
Security portfolio of original responsible-disclosure findings, CTF and lab write-ups, methodology notes, and purpose-built pentest tooling covering…
ctfcurated-resourceseducation+6
mitsu-bis/security-portfolioSecurity portfolio of original responsible-disclosure findings, CTF and lab write-ups, methodology notes, and purpose-built pentest tooling covering…
 volksrat71/react2shellexploitvisualized
Interactive visualization of the React2Shell (CVE-2025-55182) RCE vulnerability with narrated animations for three audiences: Expert, Practitioner,…
 quincyomoruyi6-lang/blue-writeup-cve-2017-0144
Conducted a complete security assessment of an unpatched Windows 7 target ("Blue") to demonstrate the impact of legacy service vulnerabilities in an…
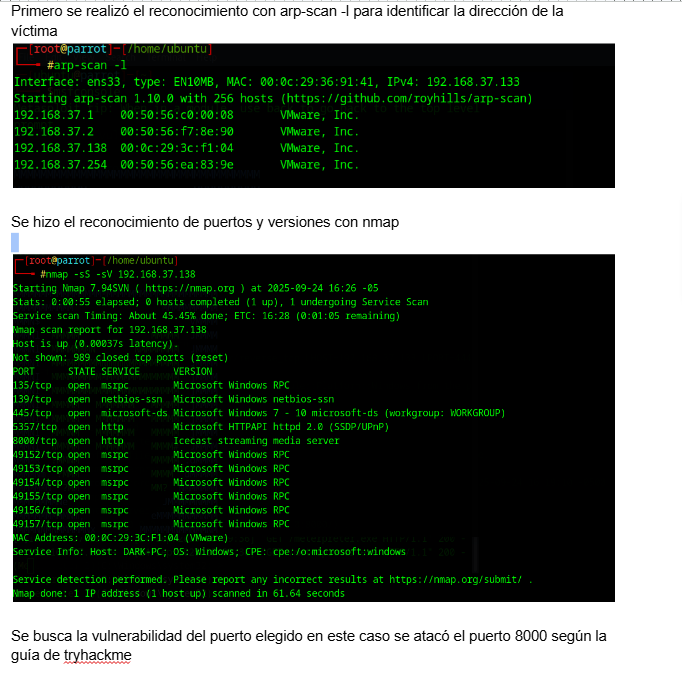 monseigneurpatas/thm-ice-icecast-rce-privesc
Full compromise of TryHackMe's Ice machine — Icecast 2.0.1 RCE (CVE-2004-1561) via buffer overflow, followed by Windows privilege escalation through…
 felisha-elmer/sandbox-challenge-spring4shell-cve-2022-22965-
Step-by-step walkthrough of exploiting CVE-2022-22965 (Spring4Shell) with Metasploit, deploying a C2 listener, and mitigating the vulnerability by…
 chathura123git/ethical-hacking-cve-2011-2523
Ethical Hacking Assessment | Practical vulnerability testing of vsftpd 2.3.4 backdoor (CVE-2011-2523) on Metasploitable2 using Kali Linux & Metasploit
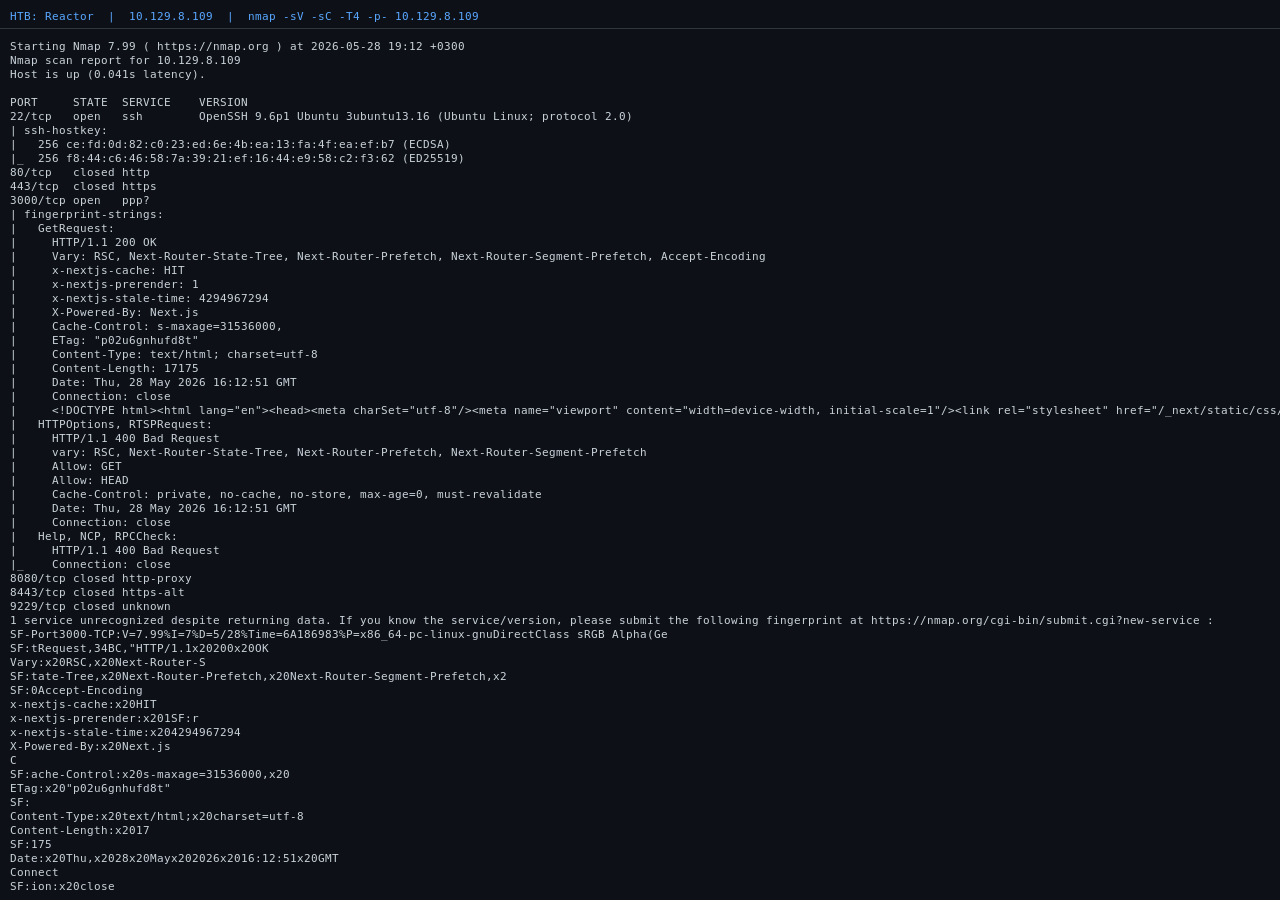 sonnycroco/htb-reactor-linux-machine-walkthrough
Full walkthrough of HTB's Reactor machine — exploit CVE-2025-55182 to gain a shell, then get root via an exposed Node.js debugger. Step-by-step with…
 benedictejepu/cve-2024-24945-nginx-rift---tryhackme-lab-walkthrough
This lab demonstrates the exploitation of CVE-2024-24945, a heap corruption vulnerability affecting NGINX. The objective was to understand how memory…
 razureink/cve-2025-53779-kerberos_bypass_reproduction
Reproduction of cve-2025-53779-kerberos_bypass_reproduction
 arnavps/ctf-web-exploitation
A comprehensive collection of 12 containerized web exploitation challenges covering CVE-2023-25690, WebAuthn bypasses, HTTP/3 smuggling, and advanced…
 trax69/cve-2025-55182-poc
Proof of Concept for CVE-2025-55182 ("React2Shell"). A fully dockerized environment demonstrating Remote Code Execution (RCE) via insecure…
 themursalin/htb-mailing-a-complete-walkthrough
If you've been grinding through HackTheBox machines, Mailing is one of those boxes that genuinely teaches you something. It's rated Easy, runs on…
 qduarte-42/rainfall
Introduction to the exploitation of ELF binaries.
 cyberone-teamares/jquery-cve-2022-31160
jquery XSS Proof of Concept (PoC)
 vatsalgupta67/all-in-one-cybersecurity-resources
List of CyberSecurity Resources and some different Sub-Domains of CyberSecurity
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 elder-plinius/t3mp3st
autonomous red teaming platform; multi-agent offensive-security meta-harness
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux