POC_react2shell_CVE-2025-55182

Exploit for CVE-2025-55182 targeting Next.js React Server Components via prototype pollution, enabling remote code execution with command execution…

Exploit for CVE-2025-55182 targeting Next.js React Server Components via prototype pollution, enabling remote code execution with command execution…

Gogs service Exploit and get the root user

A PoC for CVE-2022-26134 for Educational Purposes and Security Research

a critical Remote Code Execution (RCE) vulnerability in React Server Components (RSC). It also includes a realistic "Lab Environment" to safely test…


An implementation of a vulnerable MCP server using mcp-go

The full repo of all the labs available as part of the benchmark

Proof-of-concept exploit for an authentication bypass in marimo's terminal WebSocket endpoint, enabling unauthenticated command execution in versions…

Lab + writeup for CVE-2026-28699: Gitea OAuth2 scope enforcement bypass via HTTP Basic auth

SecDim Challenge Builder repro inspired by CVE-2026-88861: AAL1 MFA bypass at privileged credential boundary

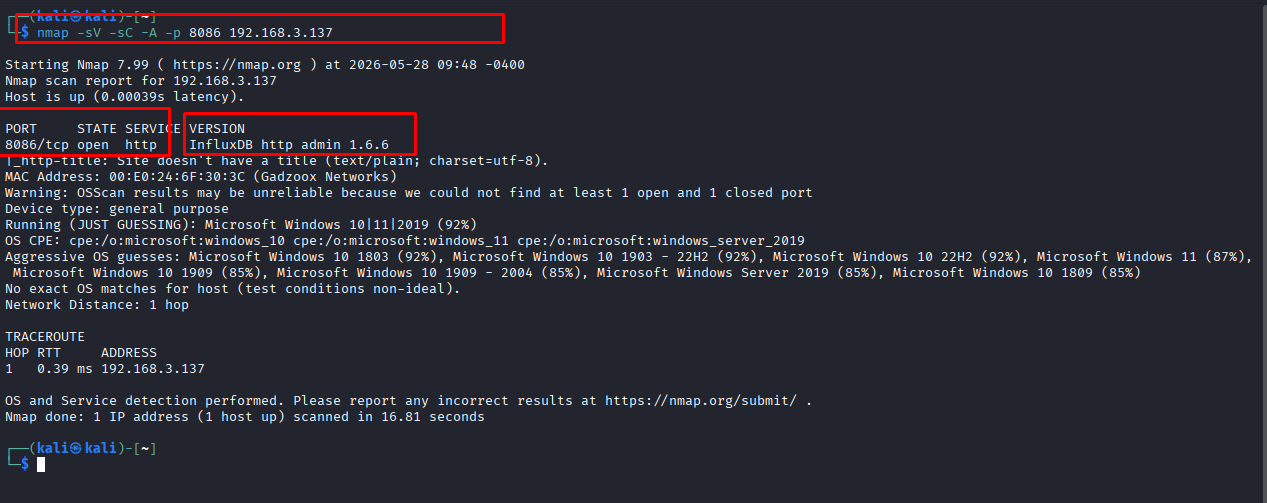
Step-by-step lab writeup demonstrating CVE-2019-20933 InfluxDB authentication bypass via forged JWT tokens, including exploitation,…

Proof-of-concept exploit for CVE-2026-8181, an authentication bypass in the Burst Statistics WordPress plugin. Demonstrates remote, unauthenticated…

Proof-of-concept exploit for CVE-2025-29927, demonstrating authentication bypass in Next.js middleware via the x-middleware-subrequest header, with…

Exploit for CrushFTP CVE-2025-31161 auth bypass: detects vulnerable targets, enumerates users, and creates unauthorized admin accounts through…