


 hasherezade/flareon2024
Solutions and write-ups for Flare-On 11 CTF challenges, showcasing reverse engineering, binary analysis, and malware analysis techniques with…
 tianstcht/cve-2023-4427
Exploit for CVE-2023-4427 targeting Chrome 117 V8, using many cross-origin iframes to brute-force ASLR and achieve code execution. Provides…
 hasherezade/flareon2023
Source-code solutions to Flare-On 10 reverse engineering challenges, demonstrating binary and malware analysis techniques for CTF-style reversing…
 nyu-llm-ctf/ctftiny
Official repository for CTFTiny
 pduggusa/dugganusa-ietf
DugganUSA threat-intelligence contributions to the IETF Hackathon: real-world agentic-attack benchmark vectors, CVE-2026-33697 attestation analysis,…
 alzeaty1/security-writeups
CTF writeups and teaching scripts for web security, bug bounty techniques, and network forensics, with blank-value versions for active practice.
 pczbuilds/monikerlink-cve-2024-21413-writeup
Writeup of TryHackMe's Moniker Link room, exploiting CVE-2024-21413 to bypass Outlook Protected View and capture NTLMv2 hashes via crafted Moniker…
 khwajasaad267-coder/cve-2024-4577-lab
Docker-based CTF lab demonstrating CVE-2024-4577 PHP-CGI argument injection leading to RCE. Includes vulnerable PHP 5.4.1 CGI, exploit scripts, and…

 taktak0x/htb-nanocorp-cve-2024-0670
PowerShell exploit for CVE-2024-0670 that abuses CheckMK Agent MSI repair to escalate privileges to SYSTEM on the NanoCorp Hack The Box machine.
 saqibnet/blackbox-pentesting-infsecos
Full black-box penetration test against SecOS:1 (VulnHub) — CSRF exploitation, privilege escalation via CVE-2015-1328 (OverlayFS), post-exploitation


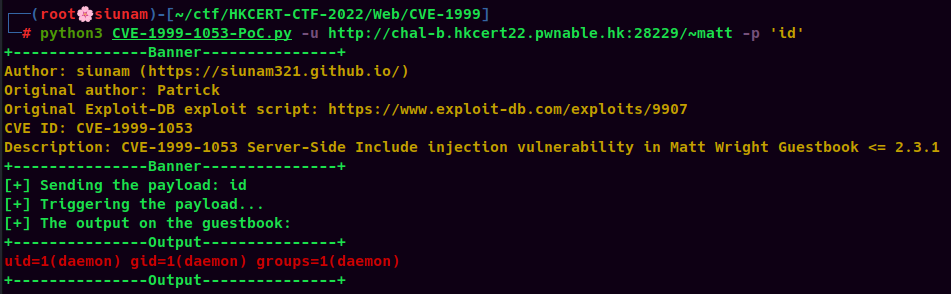 siunam321/cve-1999-1053-poc
CVE-1999-1053 Proof-of-Concept Exploit
 vanishedpeople/cve-2017-7269
Python proof-of-concept for CVE-2017-7269, a buffer overflow in IIS 6.0 WebDAV, enabling remote code execution on Windows Server 2003 R2.
 eurogig/jankybank
Simple Java Front and Back end with bad log4j version featuring CVE-2021-44228